

DockSec
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
ai-securitycode-analysiscontainer-security+5
owasp/docksecAI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 owasp/cornucopia
The source files and tools needed to build the OWASP Cornucopia decks in various languages
 owasp/asst
OWASP ASST (Automated Software Security Toolkit) | A Novel Open Source Web Security Scanner.
 owasp/cwe-tool
A command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 owasp/owasp-vwad
⚠️ This repo is no longer in use. Please refer to https://github.com/OWASP/www-project-vulnerable-web-applications-directory
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
 owasp/wstg
The Web Security Testing Guide is a comprehensive Open Source guide to testing the security of web applications and web services.
 microsoft/agent-governance-toolkit
Policy enforcement, zero-trust identity, execution sandboxing, and audit logging for autonomous AI agents. Covers 10/10 OWASP Agentic Top 10 with…
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 roottusk/vapi
vAPI is Vulnerable Adversely Programmed Interface which is Self-Hostable API that mimics OWASP API Top 10 scenarios through Exercises.
 owasp/securecodingdojo
The Secure Coding Dojo is a platform for delivering secure coding knowledge.
 owasp/software-component-verification-standard
Software Component Verification Standard (SCVS)
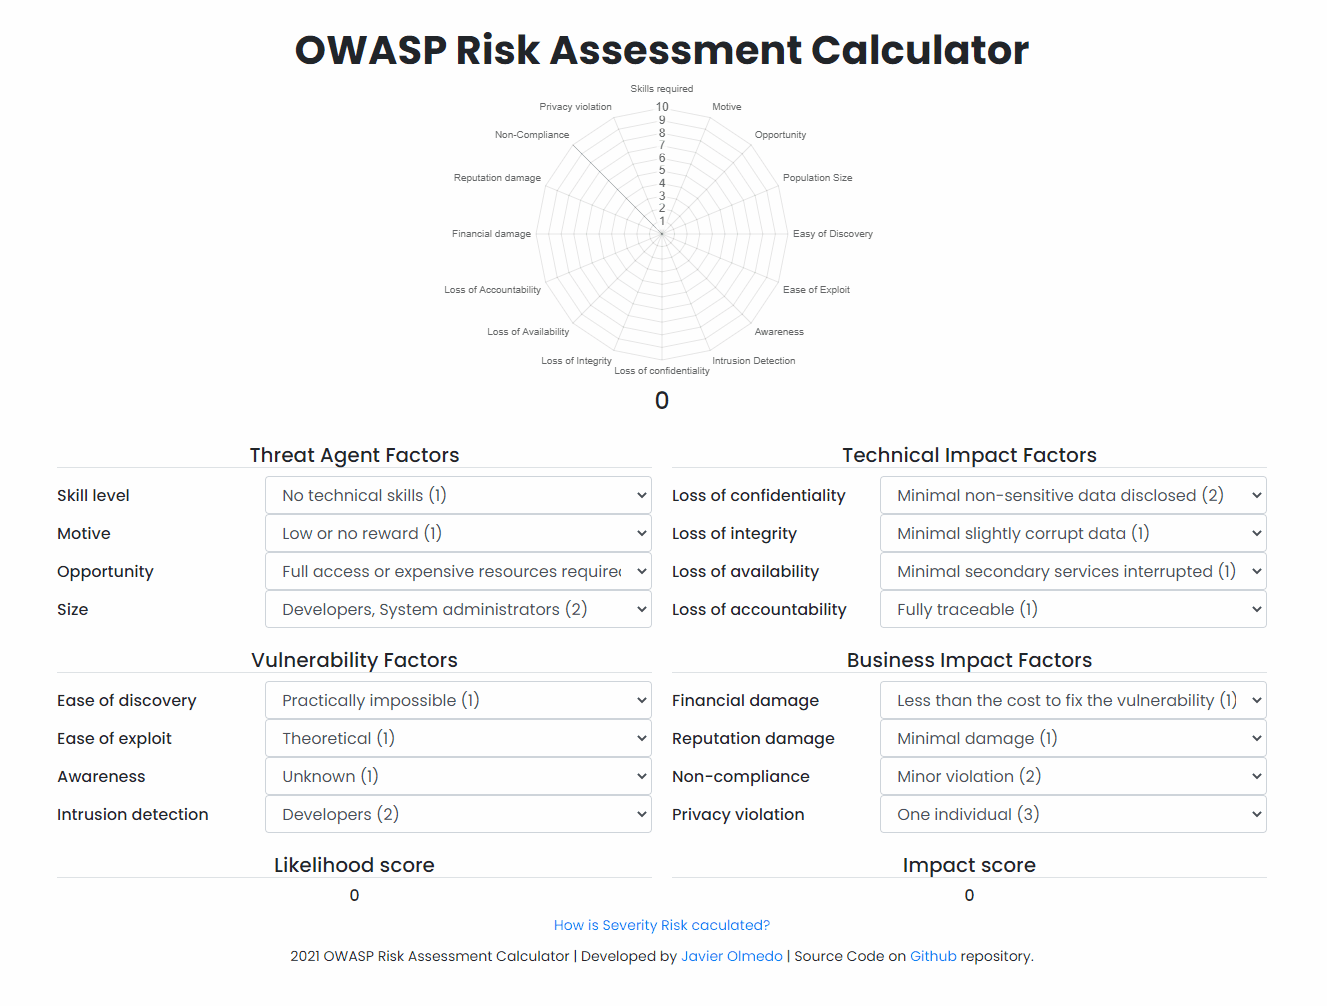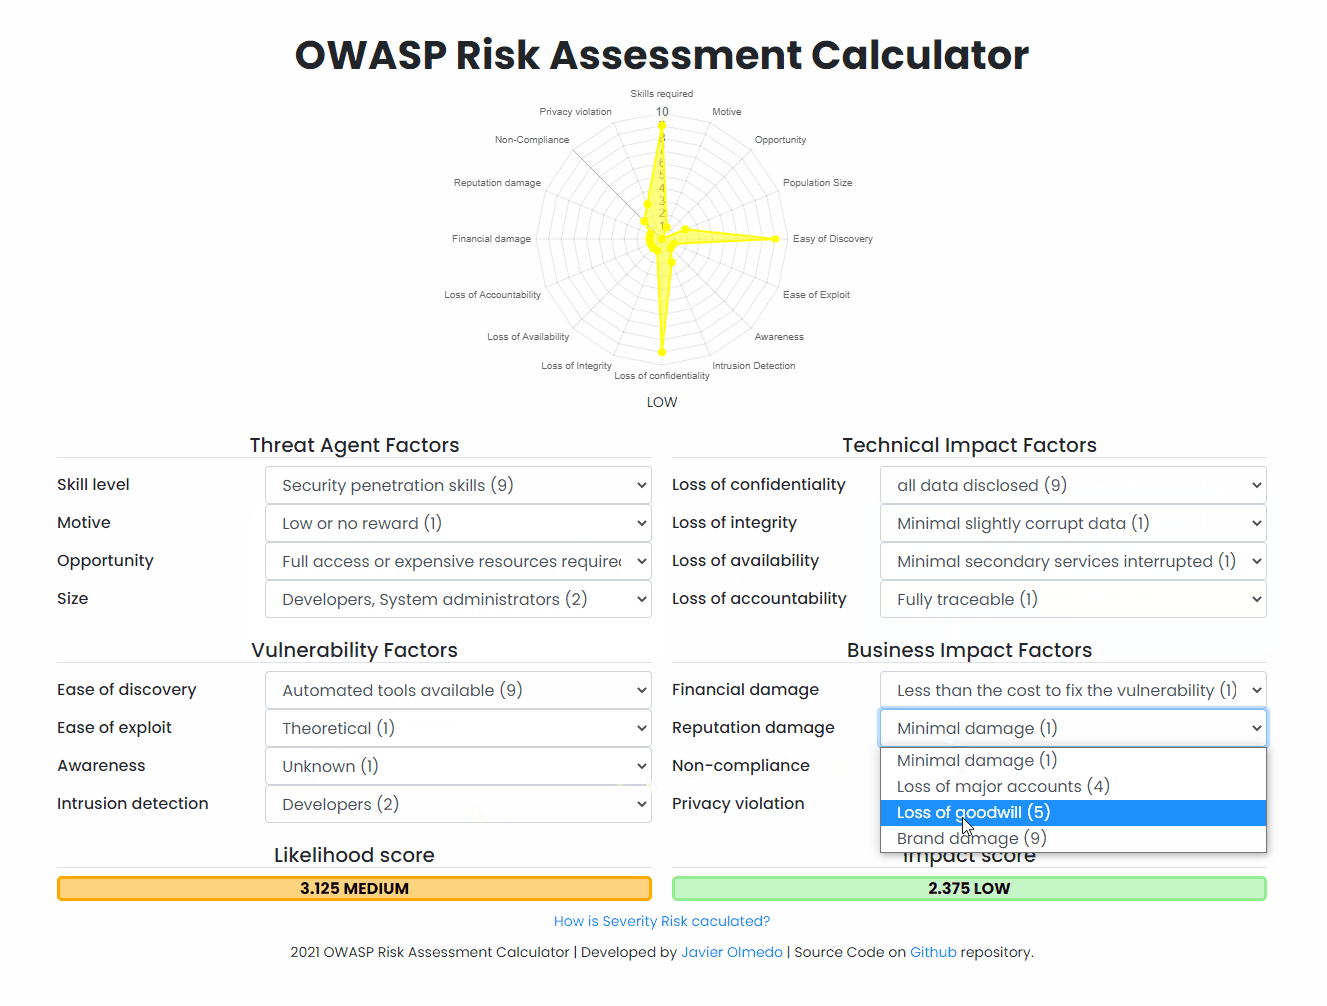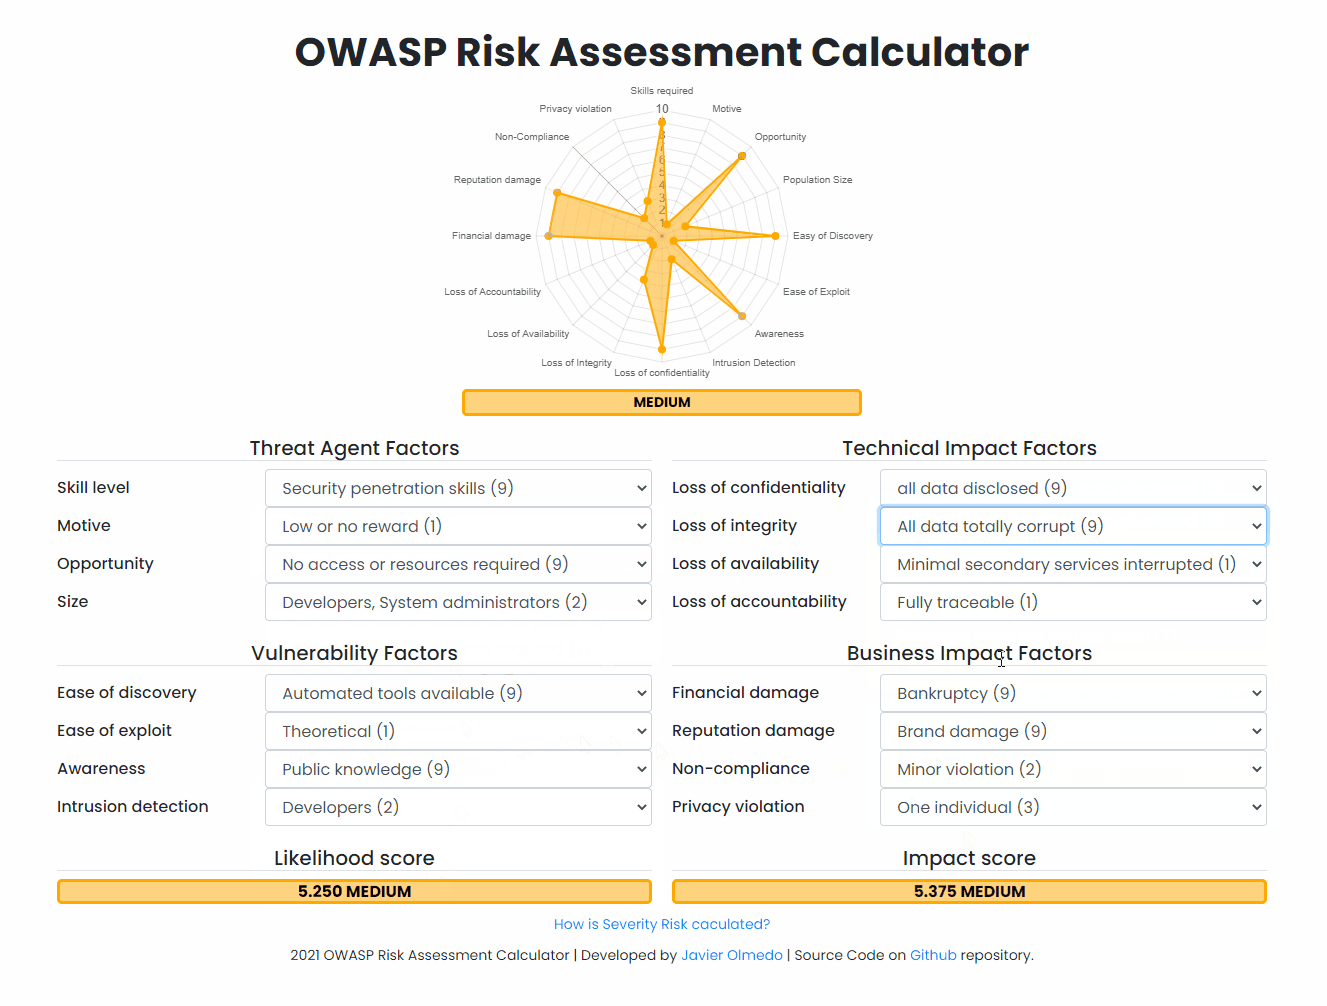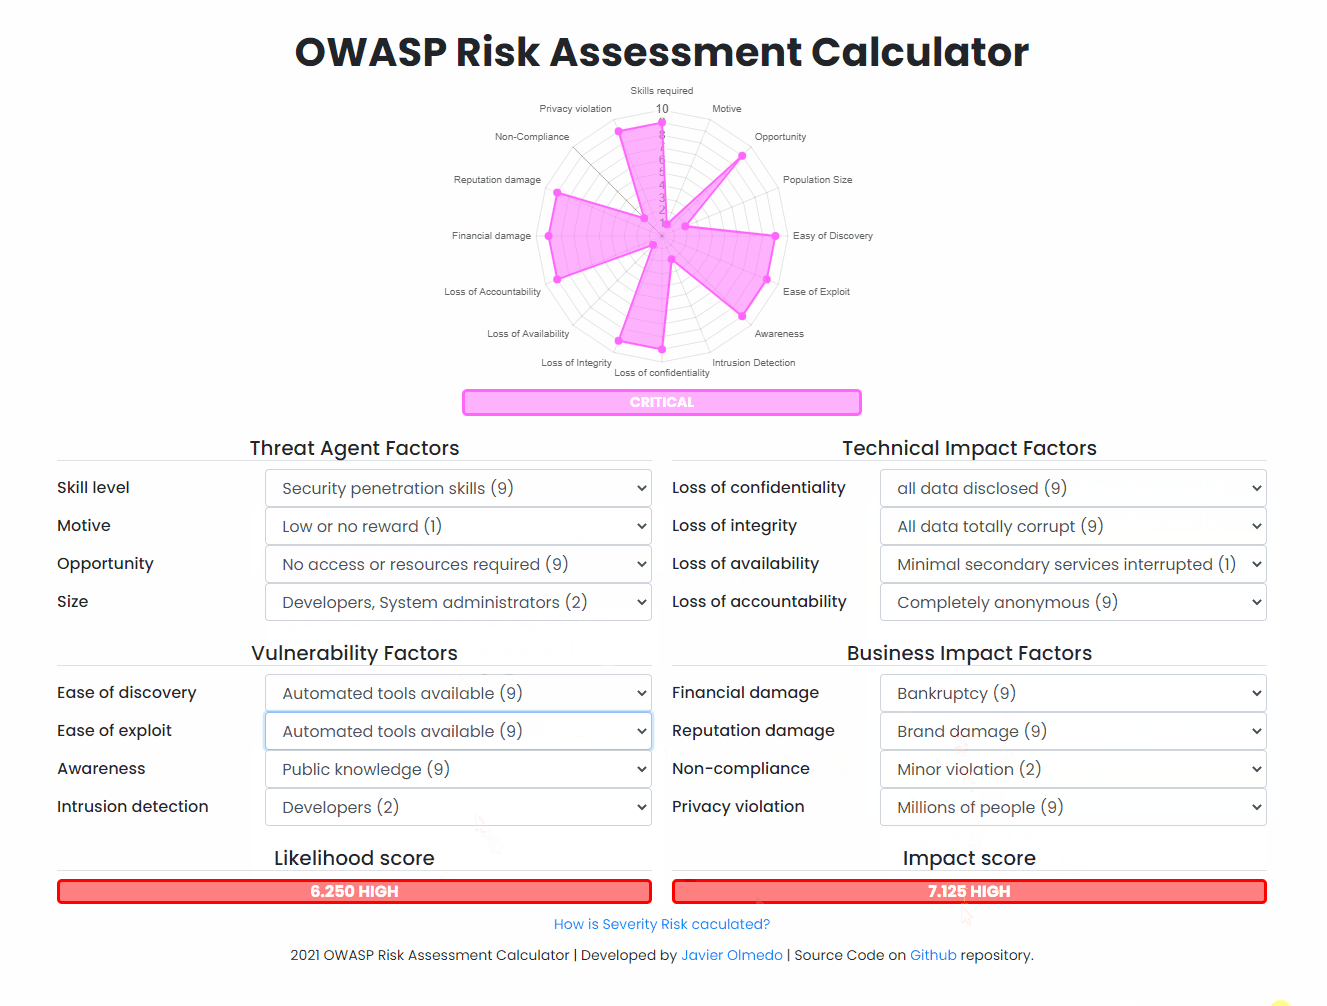 javierolmedo/owasp-calculator
🧮 An online calculator to assess the risk of web vulnerabilities based on OWASP Risk Assessment
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.