
cve-2023-45612_exploit
 clemfavre/cve-2023-45612_exploit
Reproduction of a high severty security problem that allows XXE (XML eXternal Entity) attacks on Ktor's XML serialization.
api-security-testingcode-analysiseducation+3
clemfavre/cve-2023-45612_exploitReproduction of a high severty security problem that allows XXE (XML eXternal Entity) attacks on Ktor's XML serialization.
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 skysliently/cve-2022-22947-pb-ai
一个由AI生成的漏洞验证应用
 ashiqrehan-21/mcp-inspector-cve-2025-49596
MCP-Inspector-vulncheck is a Python script that checks if an MCP Inspector server is vulnerable to CVE-2025-49596. It tests whether the /sse endpoint…
 nxploited/cve-2024-9707-poc
he Hunk Companion Plugin for WordPress: Vulnerable to Unauthorized Plugin Installation/Activation (Versions Up to and Including 1.8.4)
 aureum01/cve-2023-23752
A bash automation that exploits the vulnerable endpoints for the Joomla! API 4.0 - 4.2.7
 shoucheng3/perwendel__spark_cve-2018-9159_2-7-1
Lightweight Java 8 web framework with routing, filters, and static file serving. Includes security advisory for older versions and CRUD API examples.
 shoucheng3/perwendel__spark_cve-2018-9159_2_7_2_fixed
Lightweight Java 8 web framework for building REST APIs and web applications, with built-in routing, static file serving, and template engine support.
 palmtreeforest/codepath_week_7-8
CodePath Assignment for Weeks 7 & 8: CVE-2017-14719, CVE-2019-9787 & Unauthenticated Page/Post Content Modification via REST API
 themalwareguardian/brokeclaudia
CVE-2025-41090 (brokeCLAUDIA): Broken access control in microCLAUDIA, the anti-ransomware platform by CCN-CERT.
 rapid7/hackazon
A modern vulnerable web app
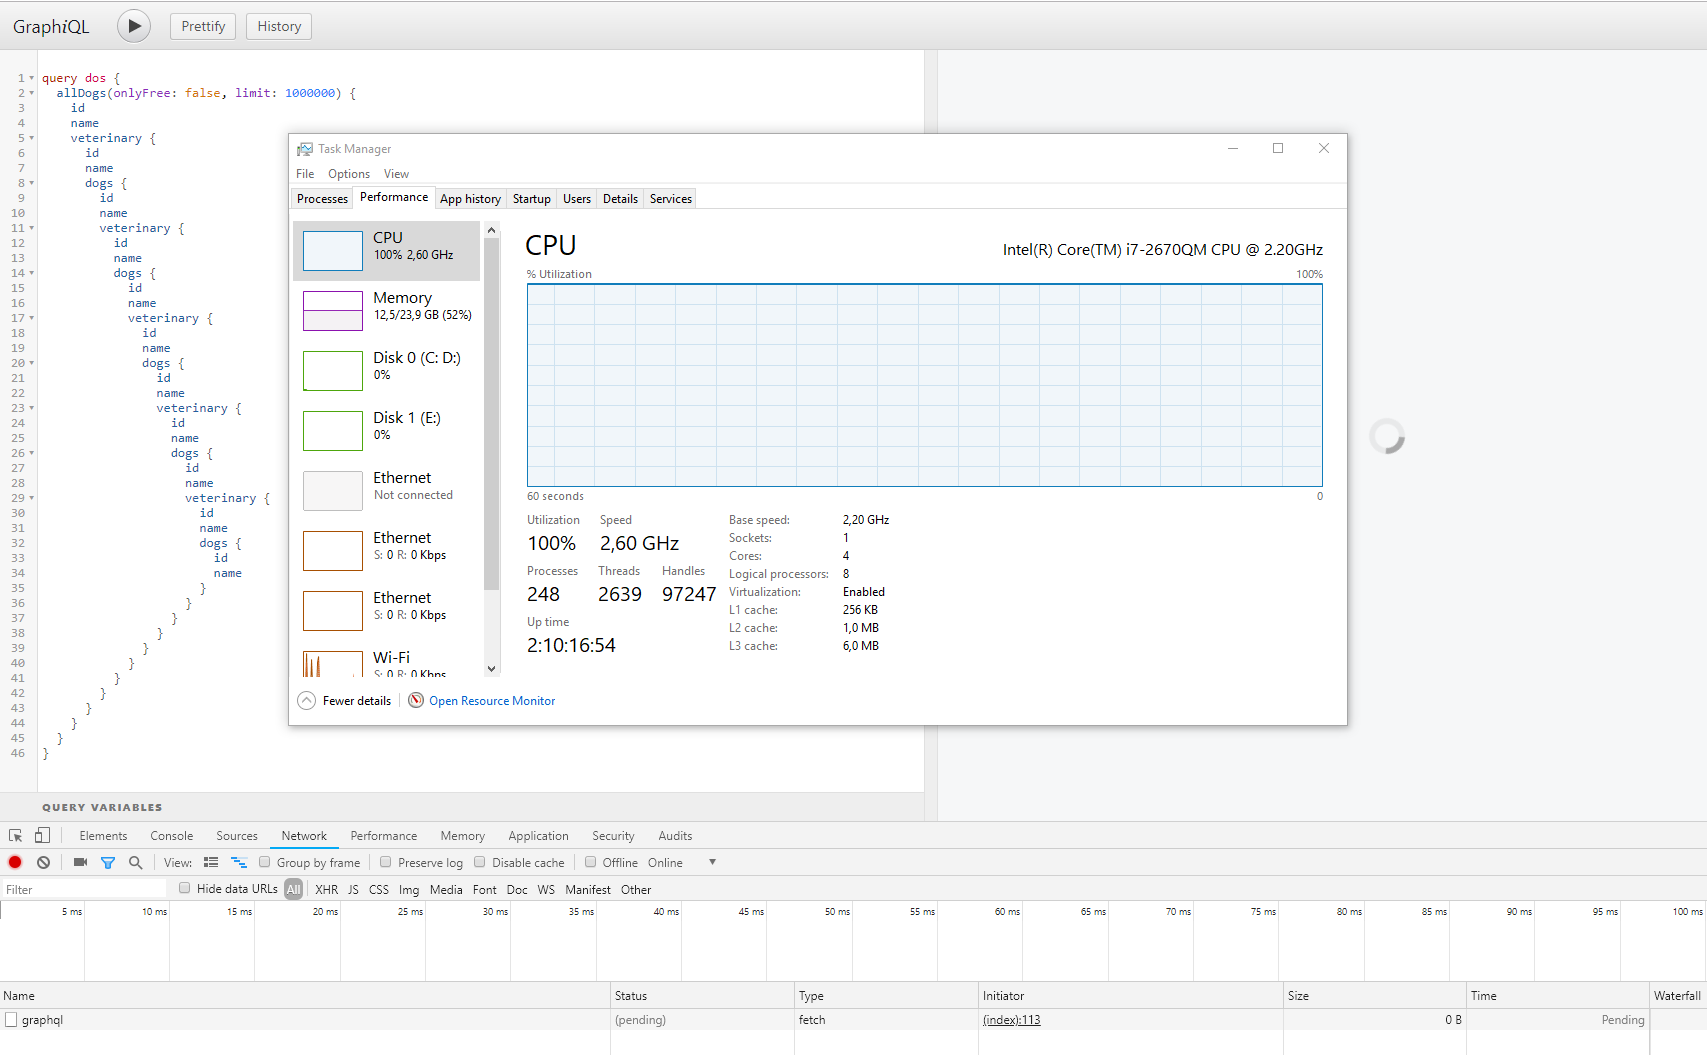 righettod/poc-graphql
Research on GraphQL from an AppSec point of view.