
Copy_Grail
 cleozi/copy_grail
Elegant C++ exploit for CVE-2026-31431 (Copy Fail) using AF_ALG authenticated encryption + splice(2) to overwrite setuid binary memory
binary-exploitationeducationexploitation+3
cleozi/copy_grailElegant C++ exploit for CVE-2026-31431 (Copy Fail) using AF_ALG authenticated encryption + splice(2) to overwrite setuid binary memory
 stigtsp/cve-2019-6690-python-gnupg-vulnerability
Proof-of-concept exploit for CVE-2019-6690, demonstrating input validation bypass in python-gnupg symmetric encryption via newline injection in…
 spiralbl0ck/one-time-ecb-oracle-attack-aes
Implementation of the byte-at-a-time ECB oracle attack against AES-ECB encryption. Decrypts ciphertexts by feeding chosen plaintexts to a block…
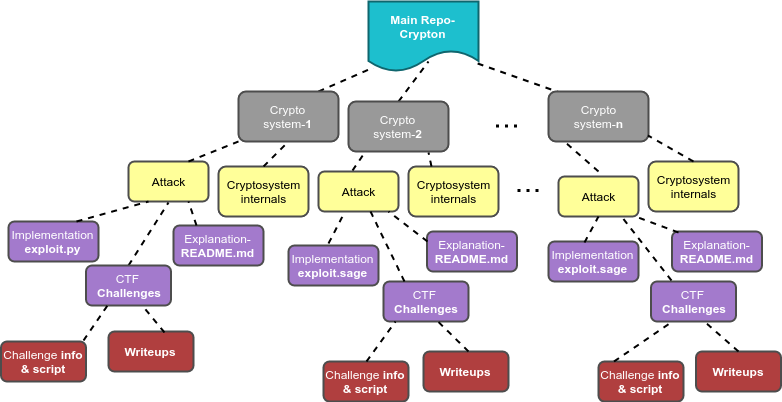 ashutosh1206/crypton
Library consisting of explanation and implementation of all the existing attacks on various Encryption Systems, Digital Signatures, Key Exchange,…
 lycis/cawdog
CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…
 c2sp/wycheproof
Project Wycheproof tests crypto libraries against known attacks.
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
 thegaminggallifreyan/liberationplay-cve-2025-24132-airbourne-poc
POC for CVE-2025-24132 (AirBourne). Currently just triggers the overflow and causes a crash
 razureink/cve-2026-34486-tomcat_encrypt_bypass_reproduction
CVE Reproduction: cve-2026-34486-tomcat_encrypt_bypass_reproduction
 george0papasotiriou/cve-2026-11110-aes-gcm-nonce-reuse-leading-to-key-recovery
Demonstrates AES-GCM nonce-reuse exploitation by collecting same-nonce ciphertexts, leading to GHASH key leakage, message forgery, and key recovery…
 user6400/cve-2026-39031-lansweeper-lsrunase2-lsencrypt2
CVE-2026-39031 — offline plaintext password recovery for Lansweeper lsrunase 2.0 / lsencrypt 2.0 via a hardcoded RC4 key. PoC + technical advisory.
 roxanne_ardary/real-estate
Specifications and open-source platforms for self-sovereign, encrypted real estate data management with blockchain-inspired verification, enabling…