
EXPLOIT-CVE-2026-87902
 joaovicdev/exploit-cve-2026-87902
Lab vulnerável (Docker) + PoC Python para a CVE-2026-87902 — path traversal não autenticado no WordPress Core (page-template -> LFI -> RCE…
container-securityeducationexploitation+6
joaovicdev/exploit-cve-2026-87902Lab vulnerável (Docker) + PoC Python para a CVE-2026-87902 — path traversal não autenticado no WordPress Core (page-template -> LFI -> RCE…
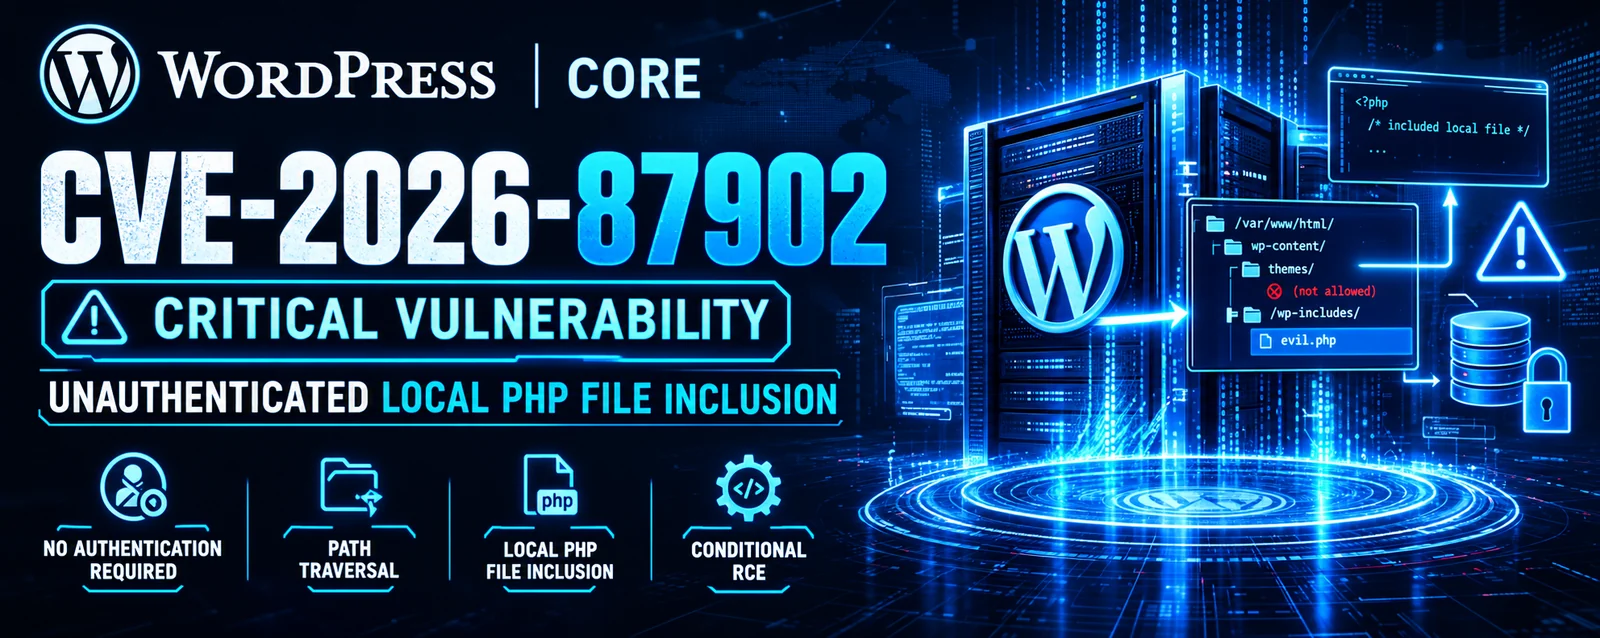 tc4dy/cve-2026-87902-toolkit
WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
 hassham1/cve-2026-87902
WordPress Core <= 7.1.1 unauthenticated LFI to RCE - validation lab, PoC, nuclei template (GHSA-7hp8-65ch-5whp)
 dinosn/cve-2026-87902-wordpress-lfi-lab
Reproduction lab + URL-list scanner + PoC for CVE-2026-87902 / GHSA-7hp8-65ch-5whp — WordPress get_page_template() unauthenticated LFI to conditional…
 sangsenimanwartefak/cve-2026-5118
Detection tooling for CVE-2026-5118, an unauthenticated privilege escalation in Divi Form Builder <= 5.1.2, identifying affected WordPress…
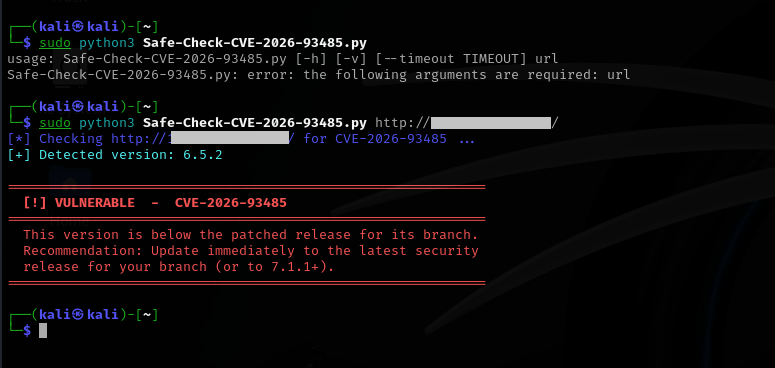 0xblackash/cve-2026-93485
Defensive research repository for CVE-2026-93485, a WordPress core stored XSS flaw, with version-check scanner, technical analysis, and patch…
 sangsenimanwartefak/cve-2026-80467
Python detection tool that fingerprints ACF Extended forms on WordPress and checks for publicly exposed role fields indicating CVE-2026-80467…
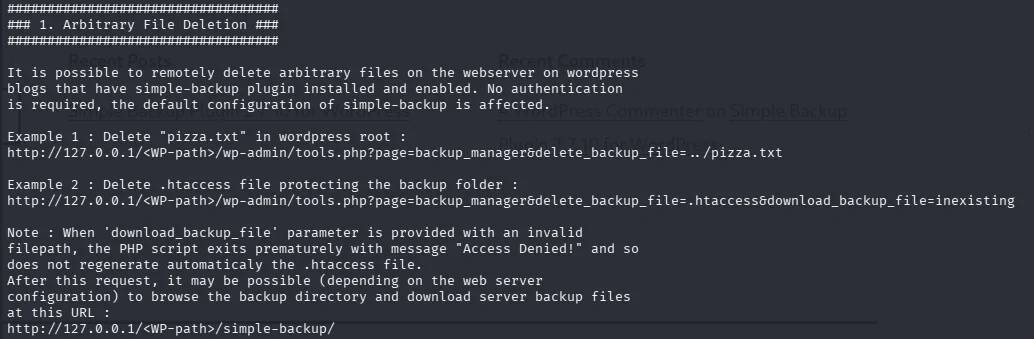 capivara-research/wordpress-path-traversal-cve-2019-11447
Detailed penetration test report demonstrating unauthenticated path traversal (CVE-2019-11447) in WordPress Simple Backup plugin, including…
 execution-py/cve-2026-9055
Defensive analysis of CVE-2026-9055, an unauthenticated privilege escalation in Amelia WordPress booking plugin. Provides root cause breakdown,…
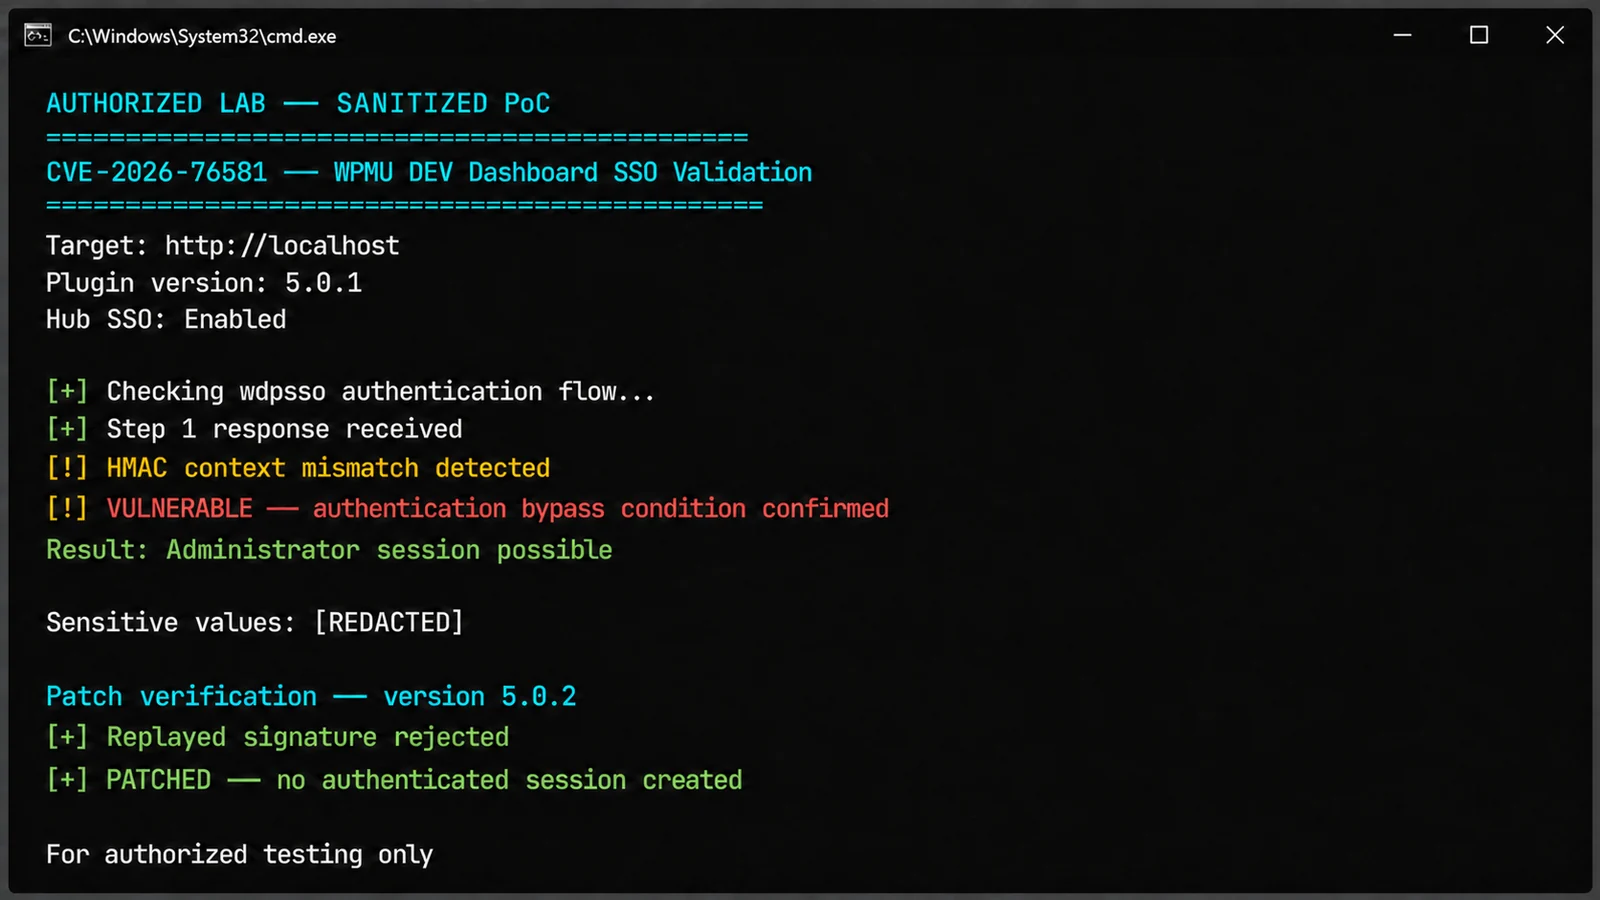 hackersroot/cve-2026-76581-detector
Safe passive detector for identifying WPMU DEV Dashboard versions affected by CVE-2026-76581.
 dinosn/givewp-cve-2026-82222-rce-lab
Authorized Docker lab and clean PoC for validating CVE-2026-82222 RCE in GiveWP 4.16.5.1 and the 4.16.7.2 fix.
 shawnng078-ops/cve-2024-28000-exploit-lab
Hands-on reproduction of CVE-2024-28000 in LiteSpeed Cache using an isolated WordPress lab. Includes reconnaissance, vulnerable hash recovery,…
 anggatechi/cve-2026-3844
CVE-2026-3844 — Unauthenticated Arbitrary File Upload to RCE in Breeze Cache (WordPress). CVSS 9.8 CRITICAL. Mass scanner + auto shell injector with…
 ghostpels/cve-2026-13001
Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…
 bhanunamikaze/wp2shell-cve-2026-63030-poc
PoC detector & safe validator for the WP2Shell WordPress vulnerability chain: CVE-2026-63030 (REST batch-route confusion) + CVE-2026-60137…
 ghostinexile/cve-2026-63030-wp2shell
WordPress REST API SQLi to RCE PoC (CVE-2026-63030 & CVE-2026-60137)
 squamity/cve-2026-8181-poc
Python PoC for CVE-2026-8181, a critical authentication bypass in Burst Statistics WordPress plugin. Includes exploit automation, bulk scanning, and…
 ch4120n/cve-2026-63030
CVE-2026-63030 - WordPress REST Batch Route-Confusion SQL Injection Proof of Concept