

Web-App-PenTesting
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
educationlabs-practicepenetration-testing+4
sarthak4126/web-app-pentestingWeb application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 abraxas/cve-2026-87796
Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…
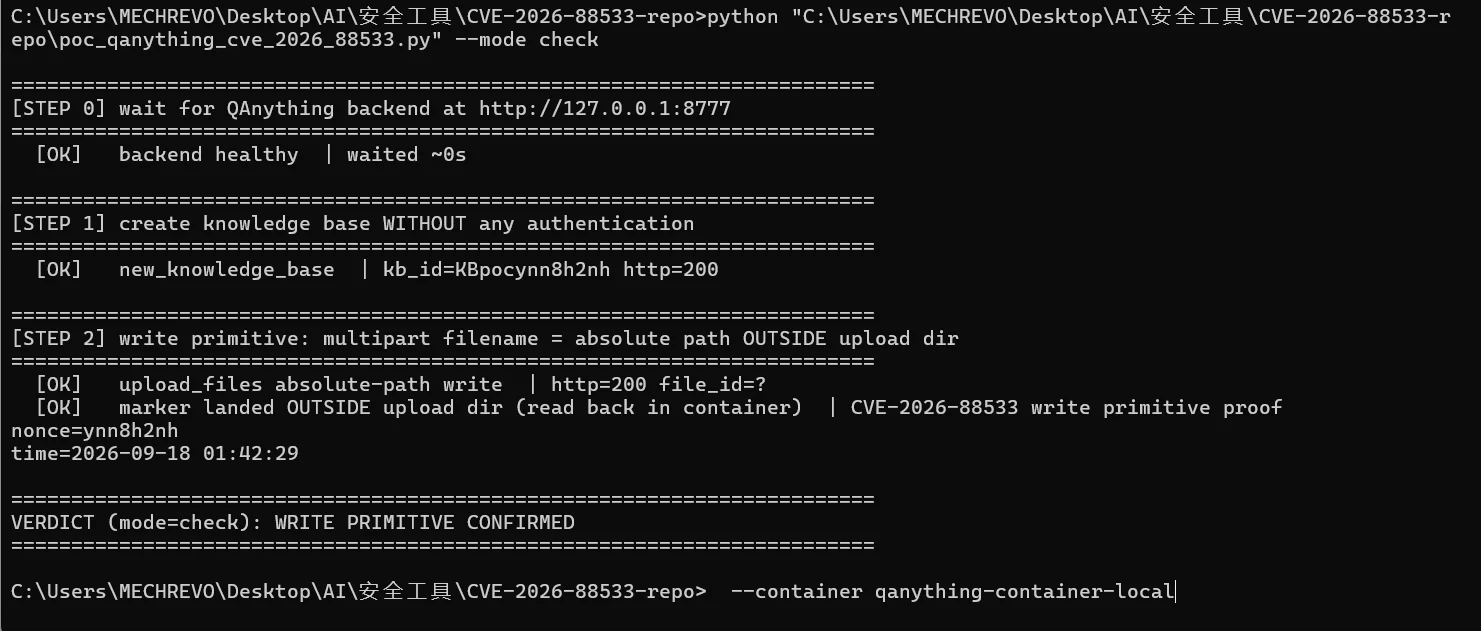 hemlock-lyk/cve-2026-88533
PoC and lab reproduction for CVE-2026-88533, an unauthenticated arbitrary file write leading to root RCE in QAnything via path traversal in the…
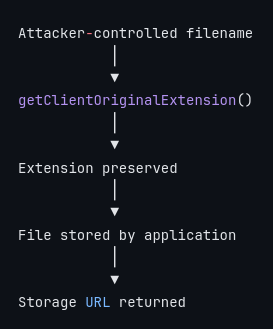 ish3ng0m4/cve-2026-38526-krayincrm
Authenticated Arbitrary File Upload leading to Remote Code Execution Technical analysis and controlled reproduction of CVE-2026-38526 in Webkul…
 hkenzokimura/cve-2025-31324
Proof-of-concept exploit for CVE-2025-31324, an unauthenticated file upload in SAP NetWeaver Visual Composer, with detection guidance, MITRE mapping,…
 ghostpels/cve-2026-75865
Unauthenticated arbitrary file upload -> RCE in WPLP Cookie Consent (gdpr-cookie-consent) <= 4.4.1 - technical write-up and PoC
 dinosn/cve-2026-32475-elementor-pro-lab
A/B Docker lab + PoC for CVE-2026-32475 (Elementor Pro Forms unauthenticated arbitrary file upload -> RCE via validation/move loop desync)
 symphony2colour/varlib-cve-2025-66034
Proof-of-concept exploit for CVE-2025-66034 in the fontTools variable font generation pipeline. A crafted .designspace file allows control of the…
 sahmsec/cve-2026-1357
Proof-of-concept exploit for CVE-2026-1357, an unauthenticated arbitrary file upload in WPvivid Backup & Migration leading to remote code execution.…
 sahmsec/cve-2026-32475
Proof-of-concept exploit for CVE-2026-32475, an unauthenticated arbitrary file upload in Elementor Pro leading to remote code execution. Includes…
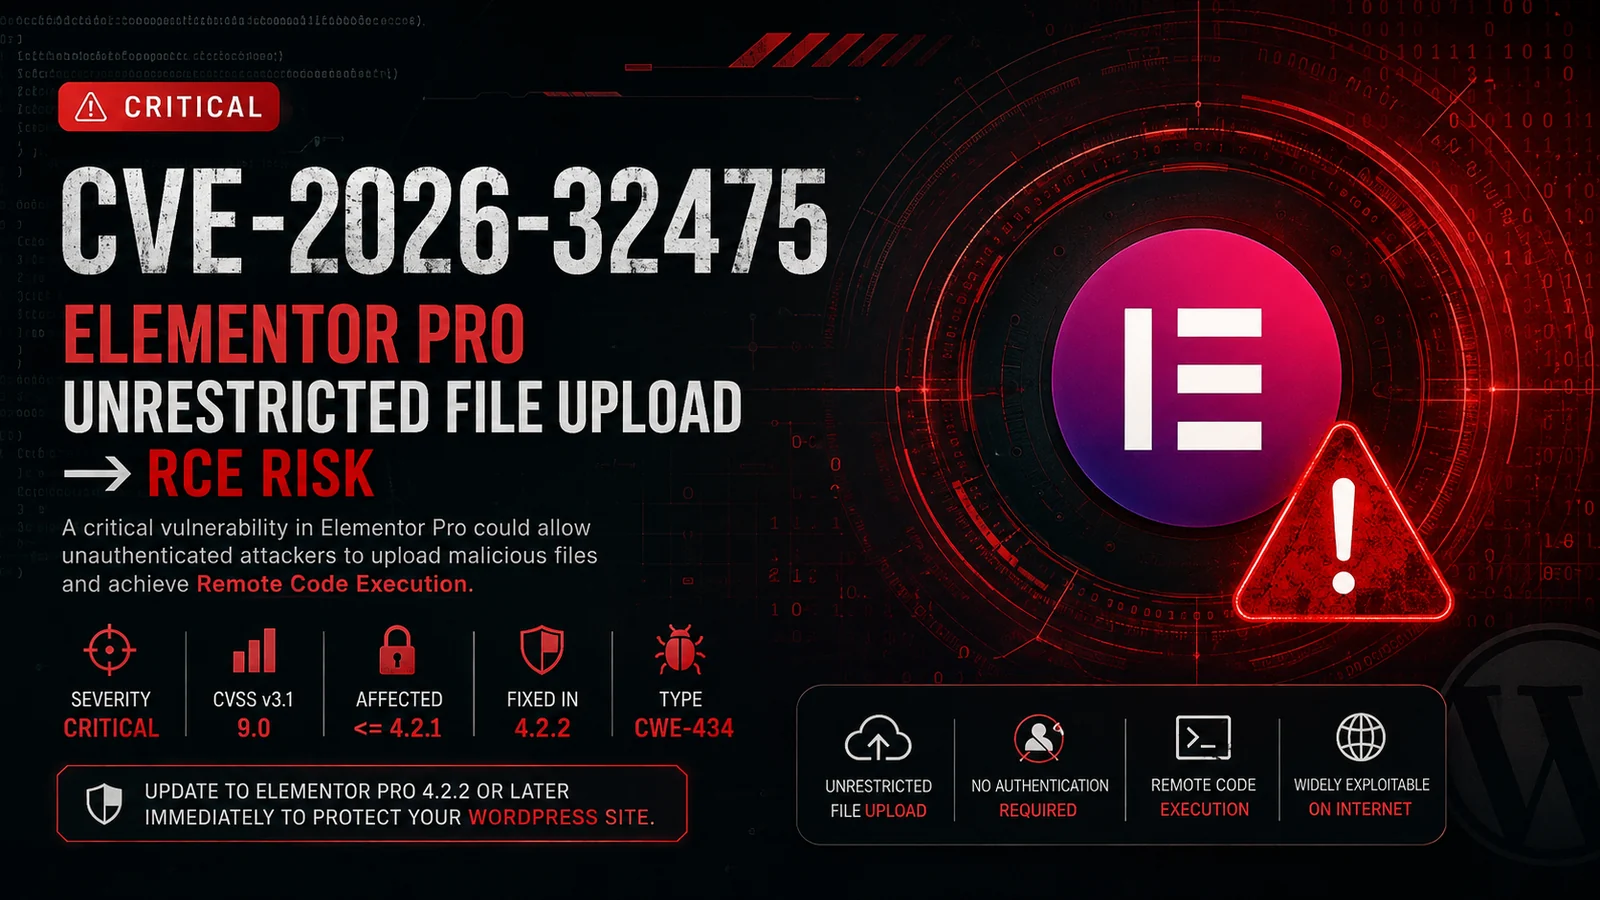 0xblackash/cve-2026-32475
Technical analysis and detection guidance for critical unrestricted file upload in Elementor Pro (CVE-2026-32475) leading to remote code execution.
 anggatechi/cve-2026-3844
CVE-2026-3844 — Unauthenticated Arbitrary File Upload to RCE in Breeze Cache (WordPress). CVSS 9.8 CRITICAL. Mass scanner + auto shell injector with…
 imbas007/cve-2026-63223-poc
CVE-2026-63223 PoC — CodeIgniter 4 is_image/mime_in File Upload RCE (CVSS 9.8). Unauthenticated remote code execution via unrestricted file upload…
 george0papasotiriou/cve-2026-4040-race-condition-in-file-upload-leading-to-rce
Reproduces CVE-2026-4040: Flask upload server with TOCTOU race condition and exploit script demonstrating arbitrary remote code execution.
 hurrrraaaa/cve-2021-21972
Isolated lab research writeup for VMware vCenter Server CVE-2021-21972, covering unauthenticated arbitrary file upload to RCE, Nmap-based detection,…
 jonas-fernandez-as/cve-2026-14856-tastyigniter
CVE-2026-14856 TastyIgniter v4.3.0
 imxur/cve-2026-48908-joomla-sp-page-builder-rce
Technical analysis and advisory for CVE-2026-48908: Unauthenticated Arbitrary File Upload to RCE in JoomShaper SP Page Builder.
 shinthink/cve-2026-3891
Pix for WooCommerce Unauthenticated File Upload via certificate_crt_path Parameter | CVSS 9.8