
osint-menace
 awesom3alex/osint-menace
Passive OSINT triage console for email, username, domain, IP, and crypto wallet reconnaissance. Features case management, curated resource links, and…
cryptographycurated-resourcesdns-analysis+5
10
awesom3alex/osint-menacePassive OSINT triage console for email, username, domain, IP, and crypto wallet reconnaissance. Features case management, curated resource links, and…
 obrige/http2-bomb
CVE-2026-49975 HTTP/2 Stream Amplification — Docker PoC with Web Console
 bhanunamikaze/cve-2026-2587-exploit-poc
CVE-2026-2587 PoC validator for Eclipse GlassFish EL Injection RCE in the admin console gadget.jsf handler. Safe authenticated vulnerability scanner…
 clayofgilgamesh/cve-2026-29000
CTF lab and exploit toolkit for CVE-2026-29000, a pac4j-jwt JWE authentication bypass. Includes vulnerable Flask target, token forging library,…
 fallen-angel-systems/fas-judgement-oss
Open-source prompt injection attack console. Test AI security by firing categorized attacks at any endpoint.
 sahiloj/cve-2023-31702
CVE-2023-31702 is an authenticated SQL Injection vulnerability discovered in MicroWorld Technologies eScan Management Console version 14.0.1400.2281.
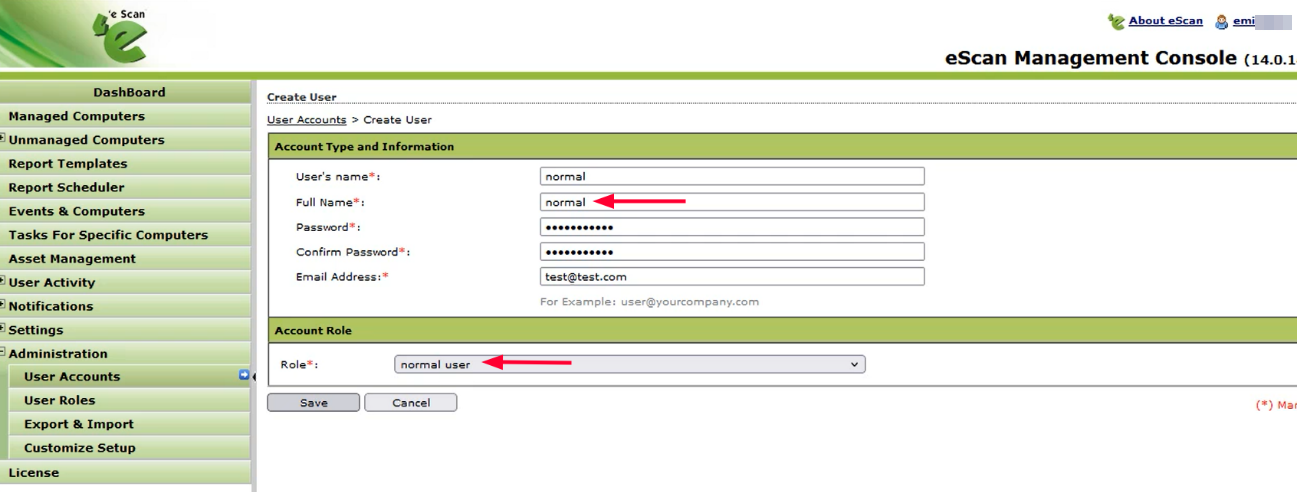 sahiloj/cve-2023-33730
eScan Management Console version 14.0.1400.2281 contains privilege escalation via `GetUserCurrentPwd` function lets attackers retrieve any user's…
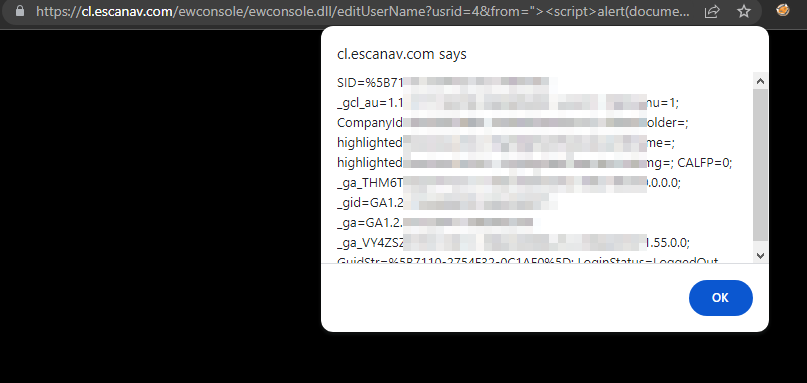 sahiloj/cve-2023-31703
A reflected Cross-Site Scripting (XSS) vulnerability exists in the Edit User functionality of the Microworld Technologies eScan Management Console…
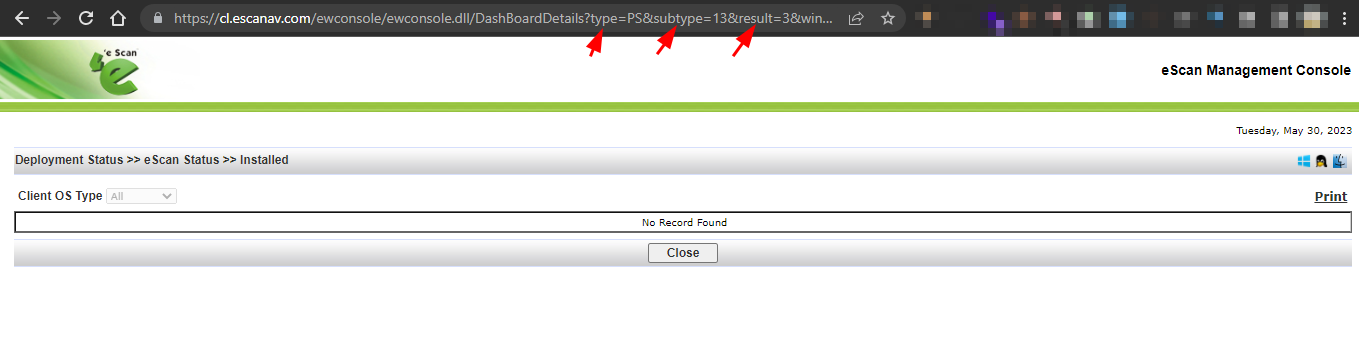 sahiloj/cve-2023-33731
A Reflected Cross-Site Scripting (XSS) vulnerability was discovered in the eScan Management Console (version 14.0.1400.2281) developed by Microworld…
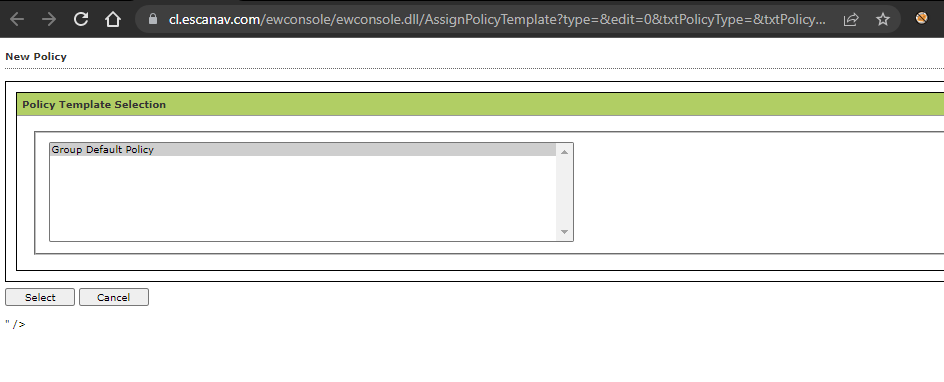 sahiloj/cve-2023-33732
CVE-2023-33732 is a Reflected Cross-Site Scripting (XSS) vulnerability discovered in the Microworld Technologies eScan Management Console, version…
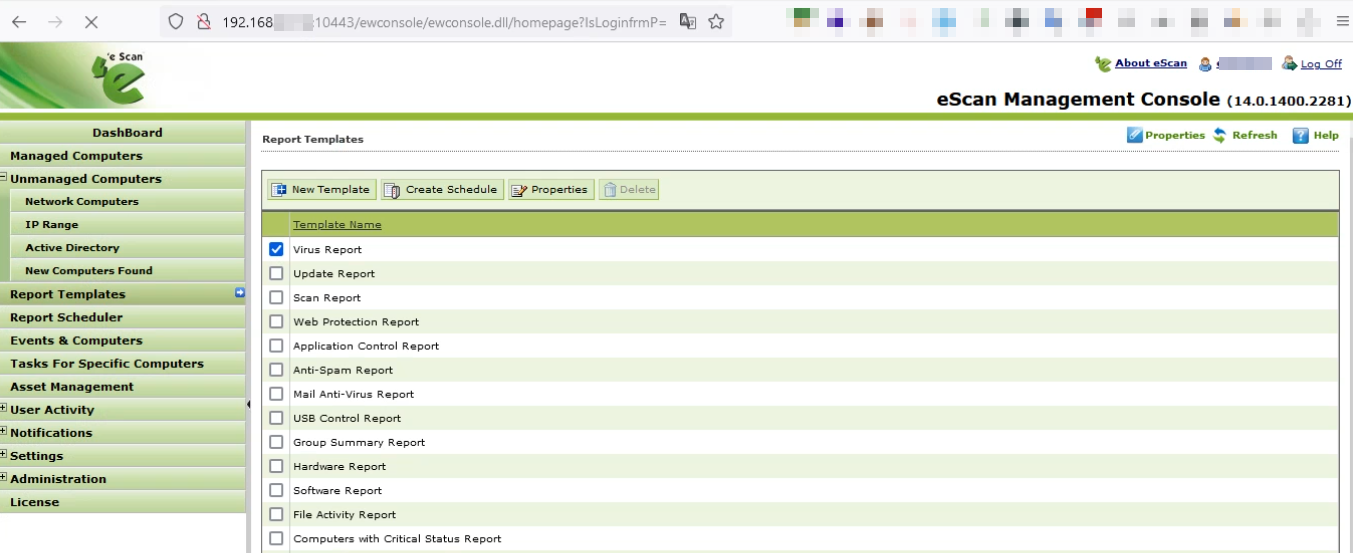 sahiloj/cve-2023-34835
A Reflected Cross-Site Scripting (XSS) vulnerability was discovered in the Microworld Technologies eScan Management Console, version 14.0.1400.2281.
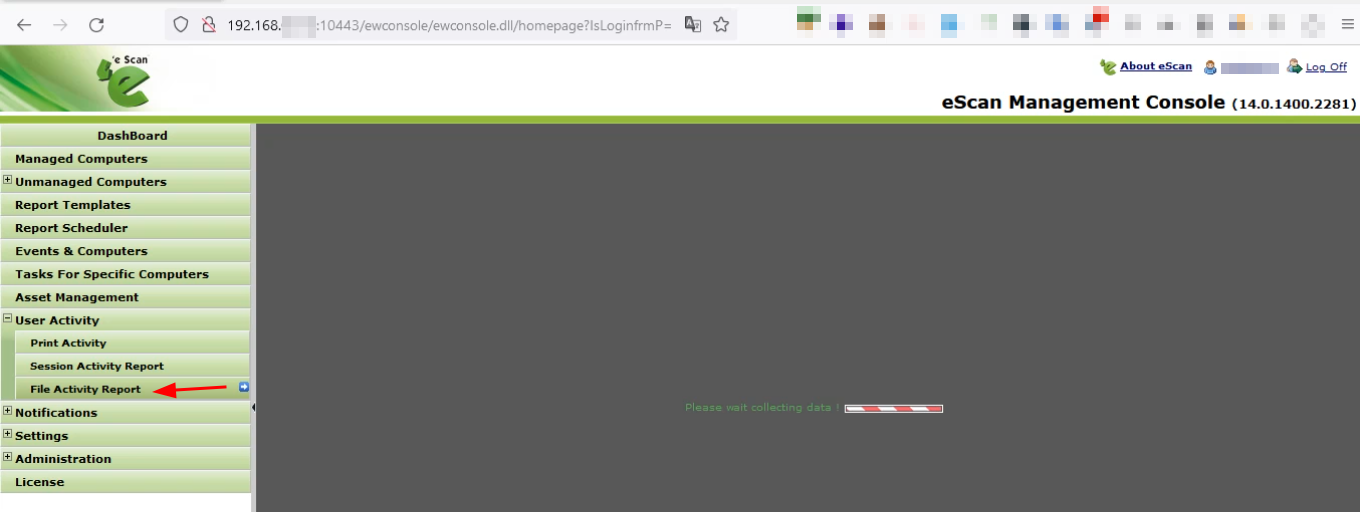 sahiloj/cve-2023-34836
A Reflected Cross-Site Scripting (XSS) vulnerability exists in Microworld Technologies eScan Management Console v14.0.1400.2281. The vulnerable…
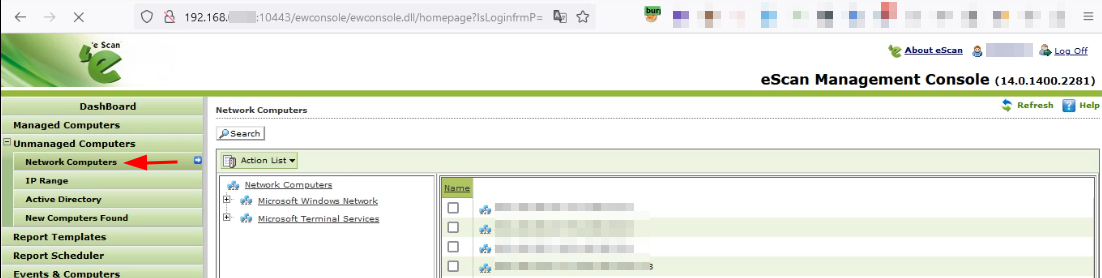 sahiloj/cve-2023-34837
CVE-2023-34837 is a Reflected Cross-Site Scripting (XSS) vulnerability discovered in the Microworld Technologies eScan Management Console version…
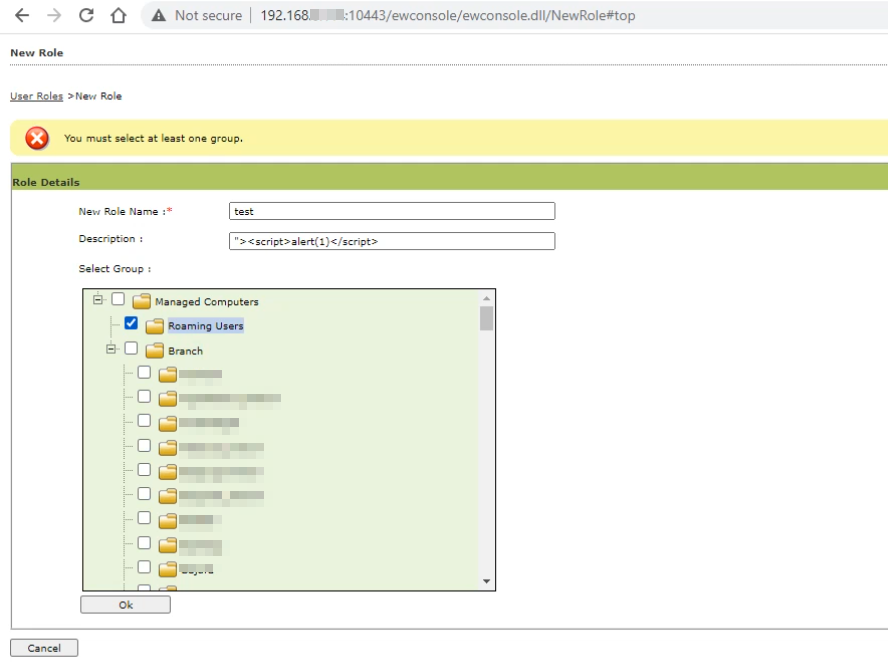 sahiloj/cve-2023-34838
Microworld Technologies eScan Management Console version 14.0.1400.2281 is vulnerable to a Stored Cross-Site Scripting (XSS) attack.
 ronin-rb/ronin
Ronin is a Free and Open Source Ruby Toolkit for Security Research and Development. Ronin also allows for the rapid development and distribution of…
 syrins/cve-2025-55182-react2shell-rce
A modern, user-friendly GUI application for detecting and exploiting the CVE-2025-55182 vulnerability in React Server Components. Built with Python…
 wrathfuldiety/cve-2025-52357
Proof of Concept and Security Advisory for XSS vulnerability in the FD602GW-DX-R410 fiber router’s admin console (firmware V2.2.14). Includes…