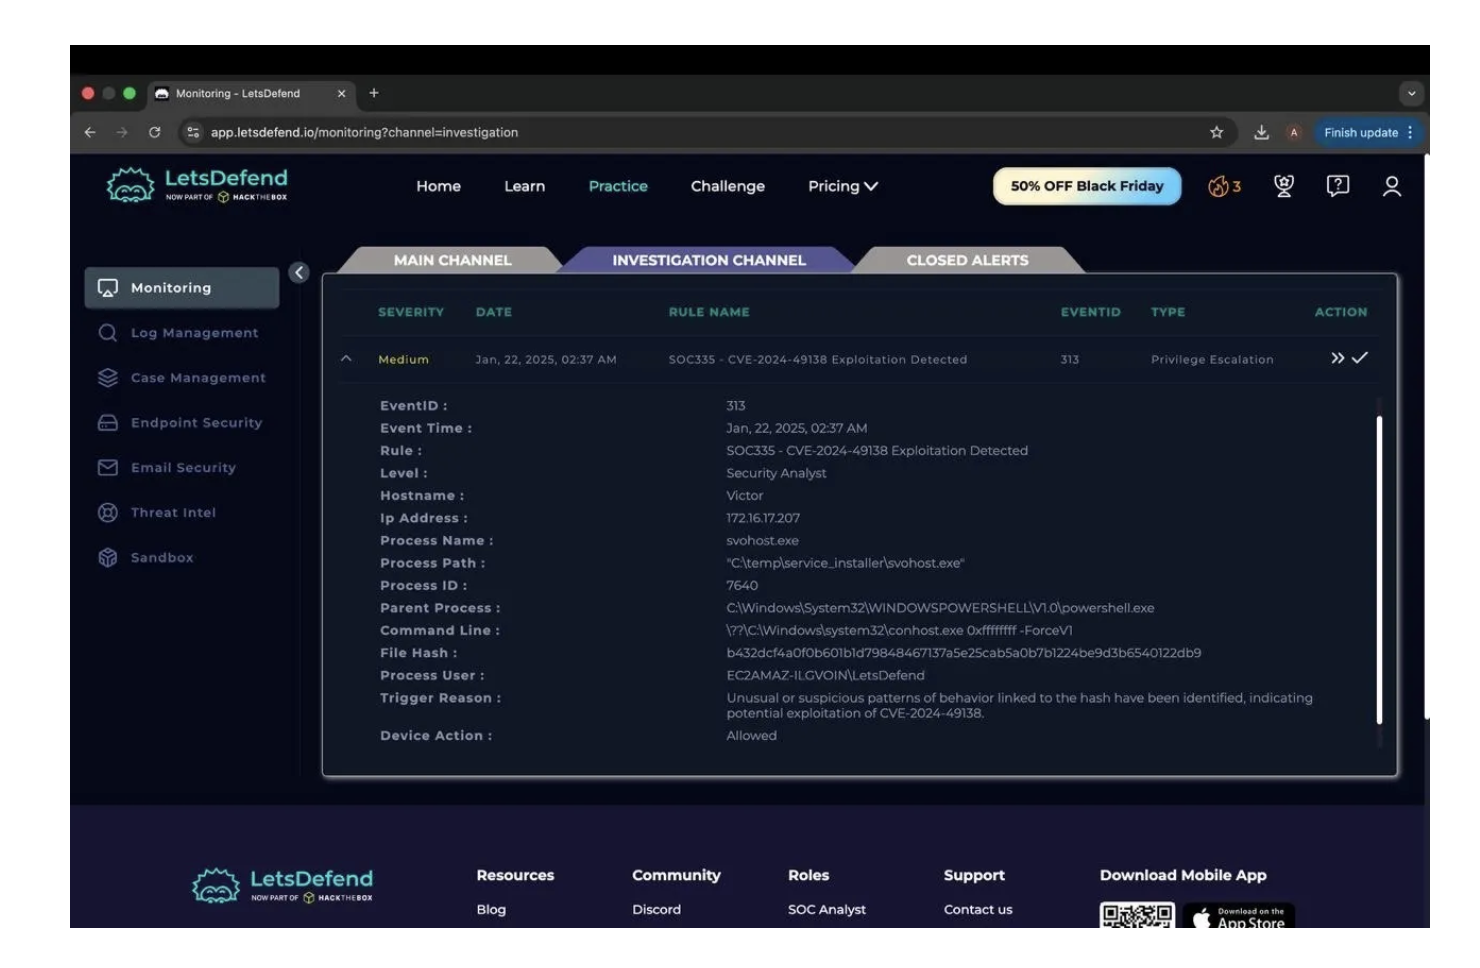
CVE-2024-49138-SOC-Investigation

SOC investigation of CVE-2024-49138 exploitation involving brute-force activity, PowerShell execution, malicious payload analysis, privilege…

SOC investigation of CVE-2024-49138 exploitation involving brute-force activity, PowerShell execution, malicious payload analysis, privilege…

Python simulation of the Bluetooth Classic KNOB attack, showing encryption key-size downgrade and brute-force decryption of intercepted Bluetooth…

Wazuh + Suricata SOC lab detecting real exploits (CVE-2011-2523) and brute-force attacks, with custom detection rules for gaps in default IDS…

Modular wordlist generation, editing, analysis, and discovery toolkit for password cracking, fuzzing, and ethical security testing. Supports…

Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…

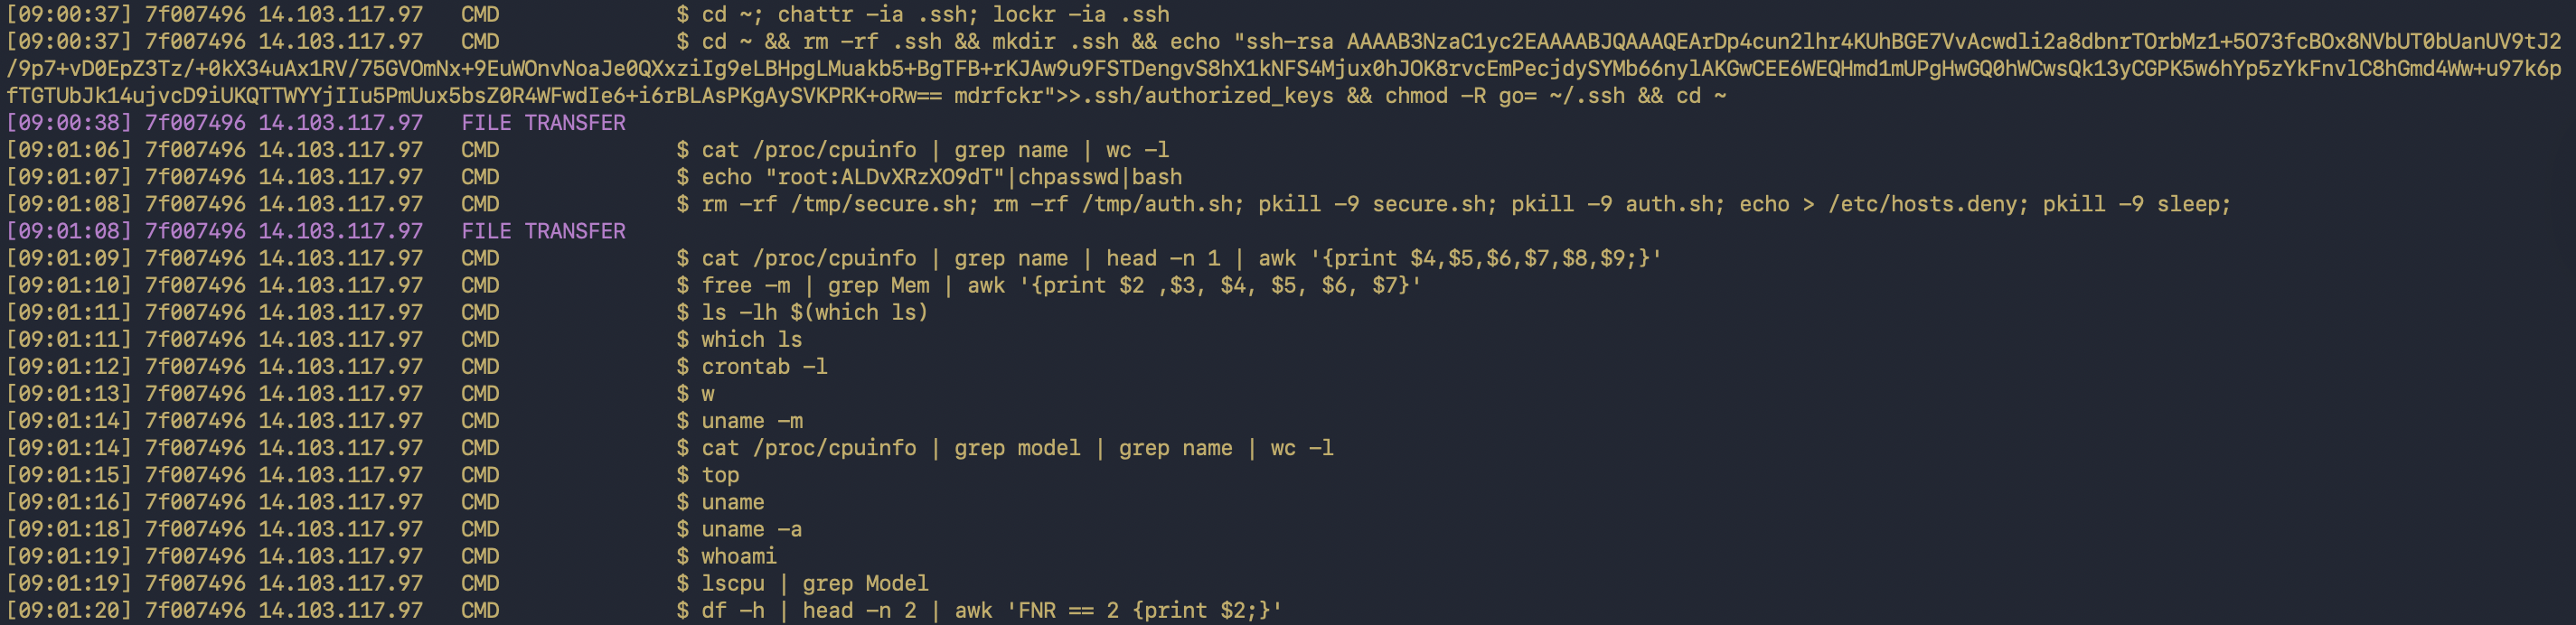
Medium-interaction SSH honeypot deployment capturing real-world brute-force traffic, malware drops, and attacker behavior. Includes TTY session…

An offline Wi-Fi Protected Setup brute-force utility

Performed a live cybersecurity assessment on a university Linux server. During analysis, active attack activity was identified, including brute-force…

Proof-of-concept for CVE-2026-31282: Totara LMS login page access control bypass enabling unauthenticated brute-force credential attacks. Includes…

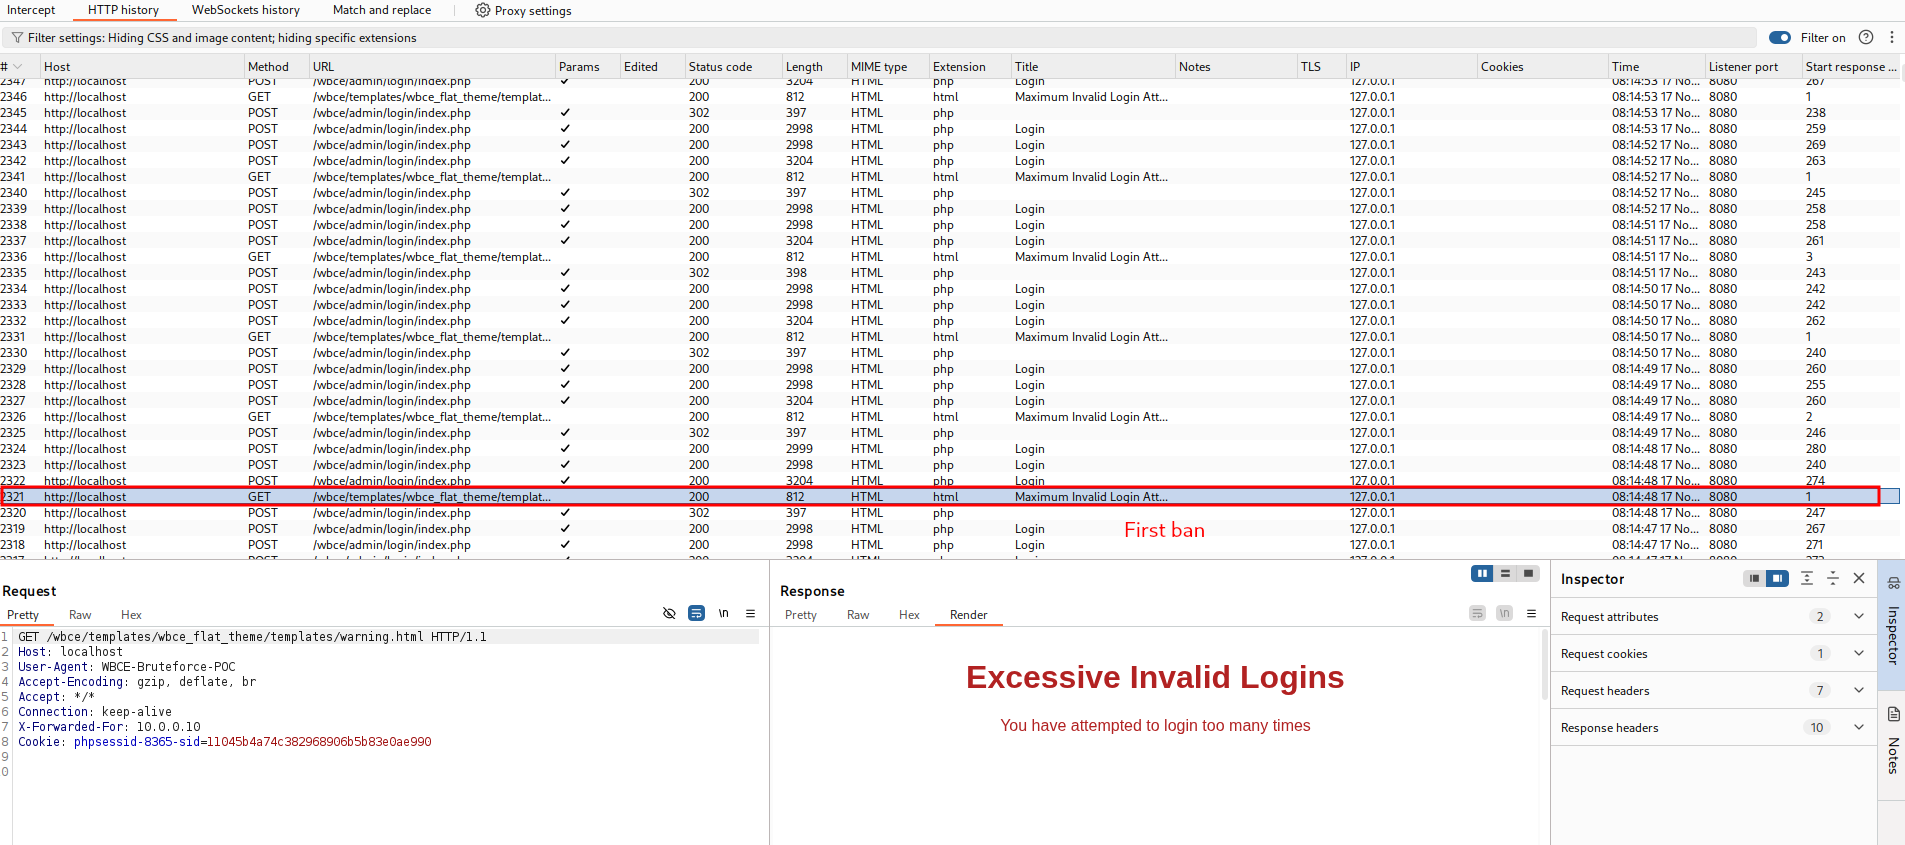
Proof-of-concept for CVE-2025-66204: brute-force protection bypass in WBCE CMS via spoofed X-Forwarded-For header, with automated Python exploit…

A 100% free standalone ZIP password recovery tool

Advisory detailing CVE-2025-56221, an authentication rate-limiting flaw in Ascertia SigningHub allowing brute-force attacks, with affected versions…

Advanced network penetration testing toolkit with SSH vulnerability assessment, CVE-2018-15473 exploitation, stealth brute force capabilities, and…

Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Ai2's playground chat, allowing attackers to brute-force predictable message…

Python-based exploit script for CVE-2023-37635, performing brute-force attacks against target URLs with optional proxy support for authorized…

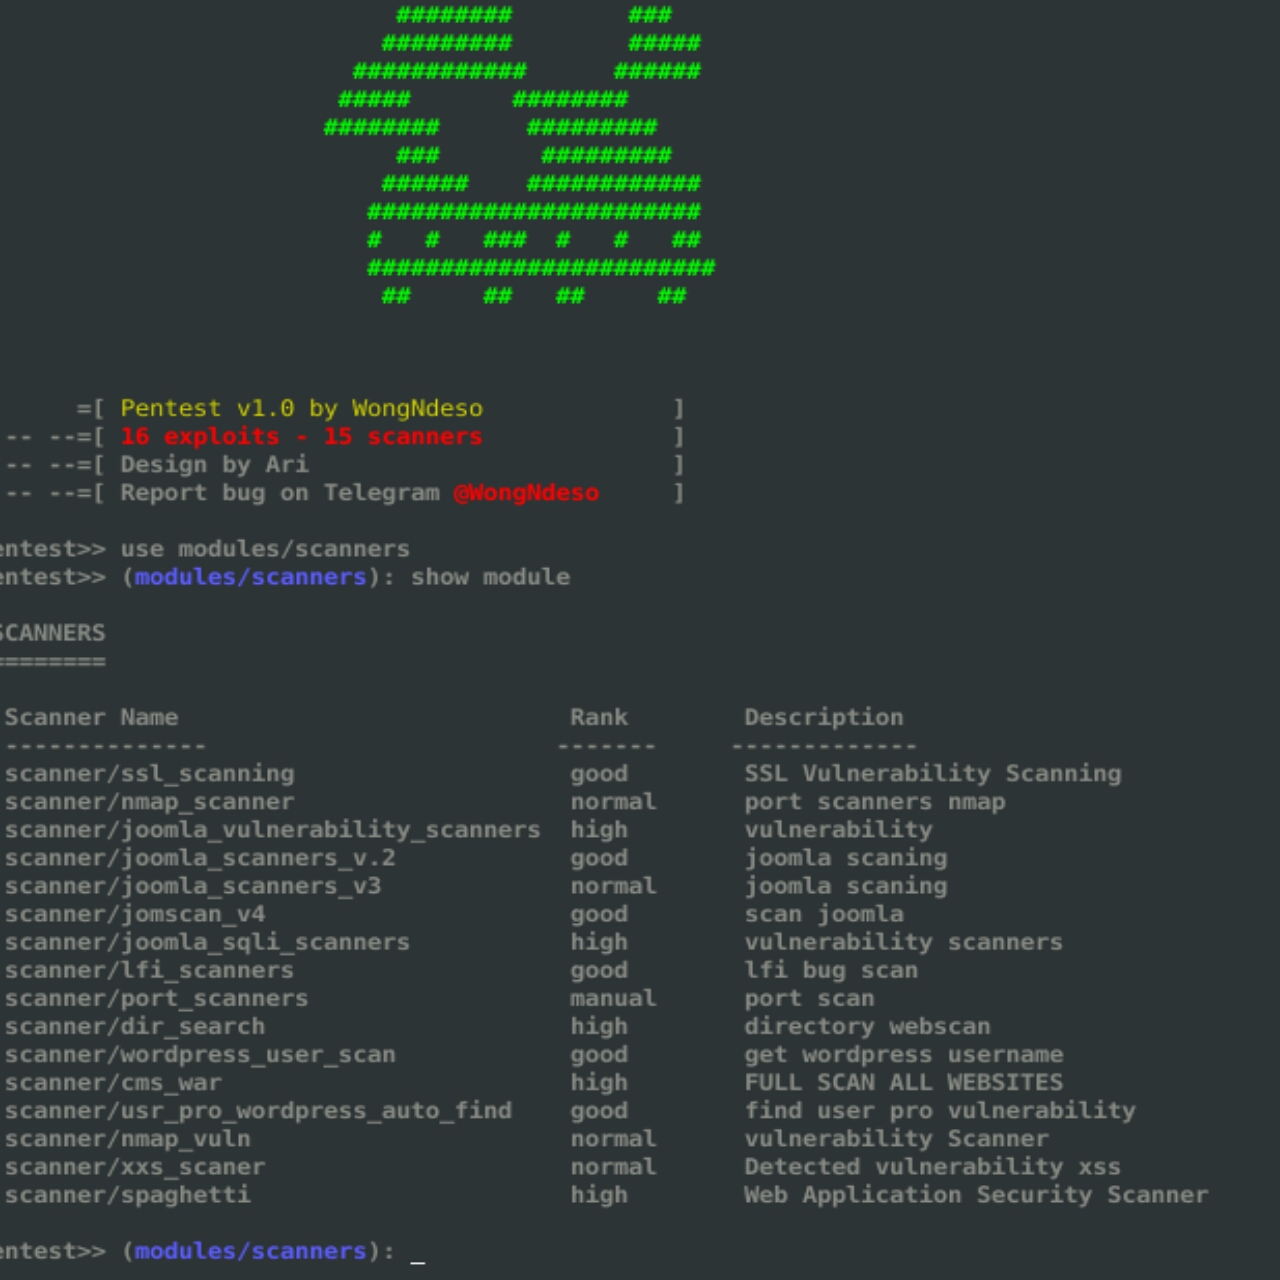
Pentest Tools Framework is a database of exploits, Scanners and tools for penetration testing. Pentest is a powerful framework includes a lot of…

Brute-force scraper for HackerOne disclosed reports via their public API, collecting report IDs, links, titles, and states for security research and…

Automated exploit for CVE-2024-24919 with API-based vulnerable IP discovery and LFI brute-force using custom wordlists. Designed for educational…