
CVE-2025-12163
 snailsploit/cve-2025-12163
CVE-2025-12163: Stored Cross-Site Scripting in Omnipress WordPress Plugin
educationpapers-researchvulnerability-analysis+2
snailsploit/cve-2025-12163CVE-2025-12163: Stored Cross-Site Scripting in Omnipress WordPress Plugin
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 john-jung/cve-2026-25604-poc
A PoC for demonstrating CVE-2026-25604
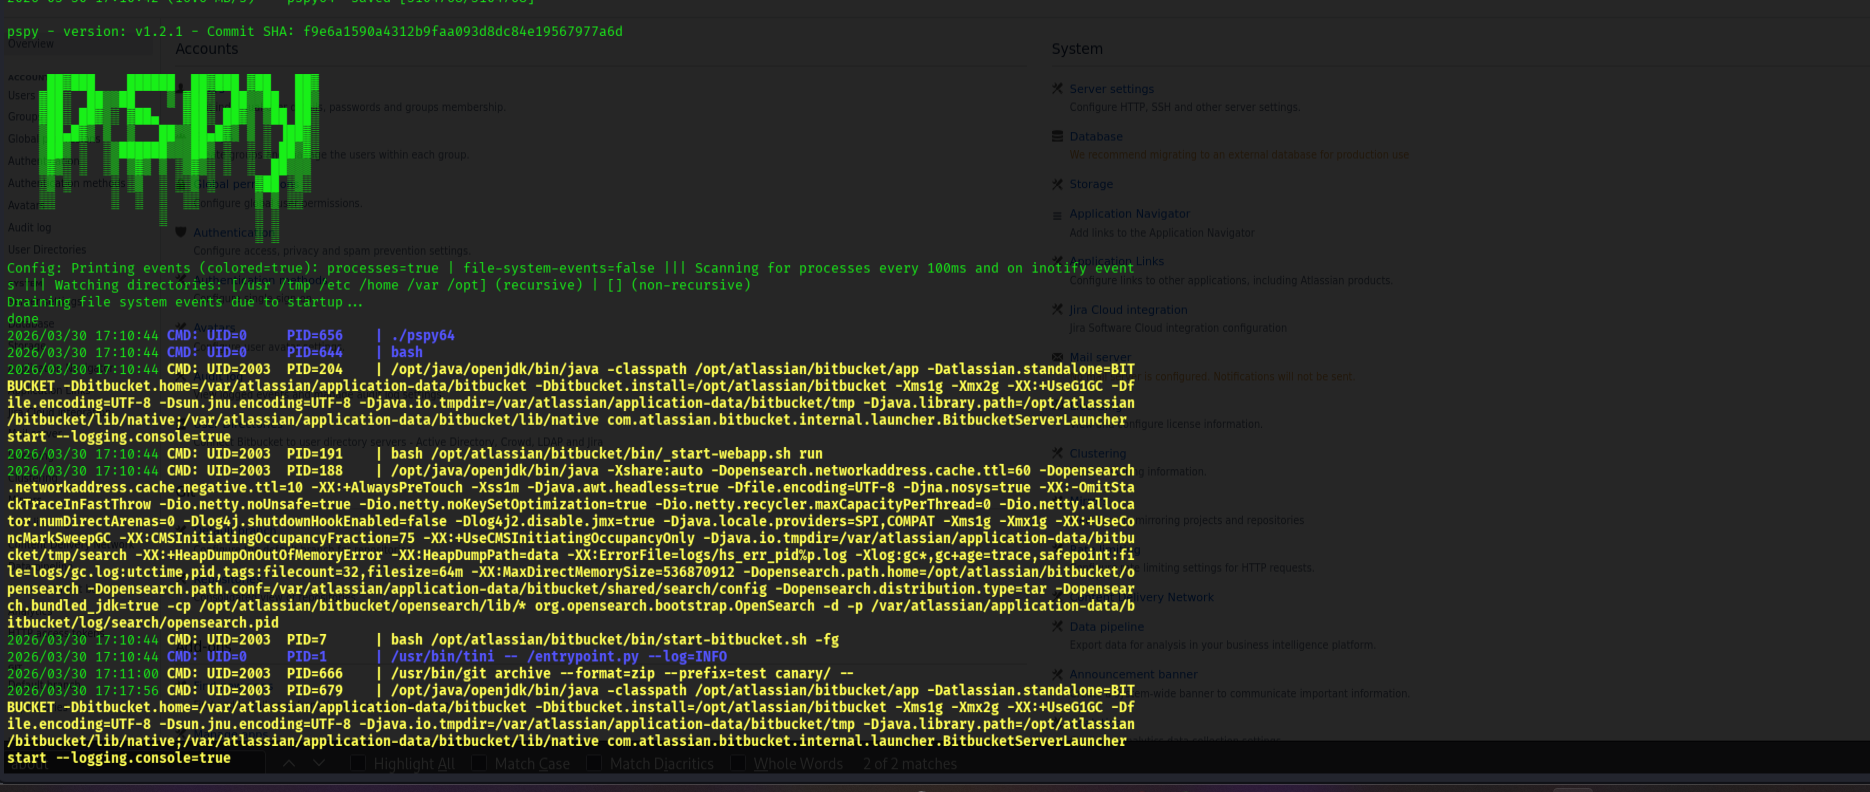 johangabrielson/bitbucket-test
Investigating CVE-2022-36804
 joshuavanderpoll/cve-2025-66398
CVE-2025-66398 — Signal K Server ≤ 2.18.0 RCE PoC
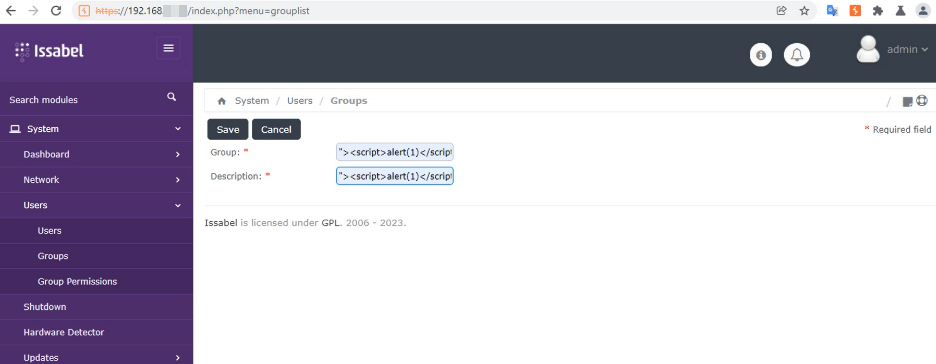 sahiloj/cve-2023-37191
A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel PBX version 4.0.0-6. This allows an authenticated attacker to inject arbitrary…
 mohnad-al-saif/gitea-git-hooks-rce-cve-2020-14144-
Gitea versions 1.1.0 → 1.12.5 allow authenticated users with "May create git hooks" permission to inject arbitrary shell commands into post-receive…
 dharan10/cve-2025-67730
A public disclourse of CVE-2025-67730 in Frape lms By dharan ragunathan
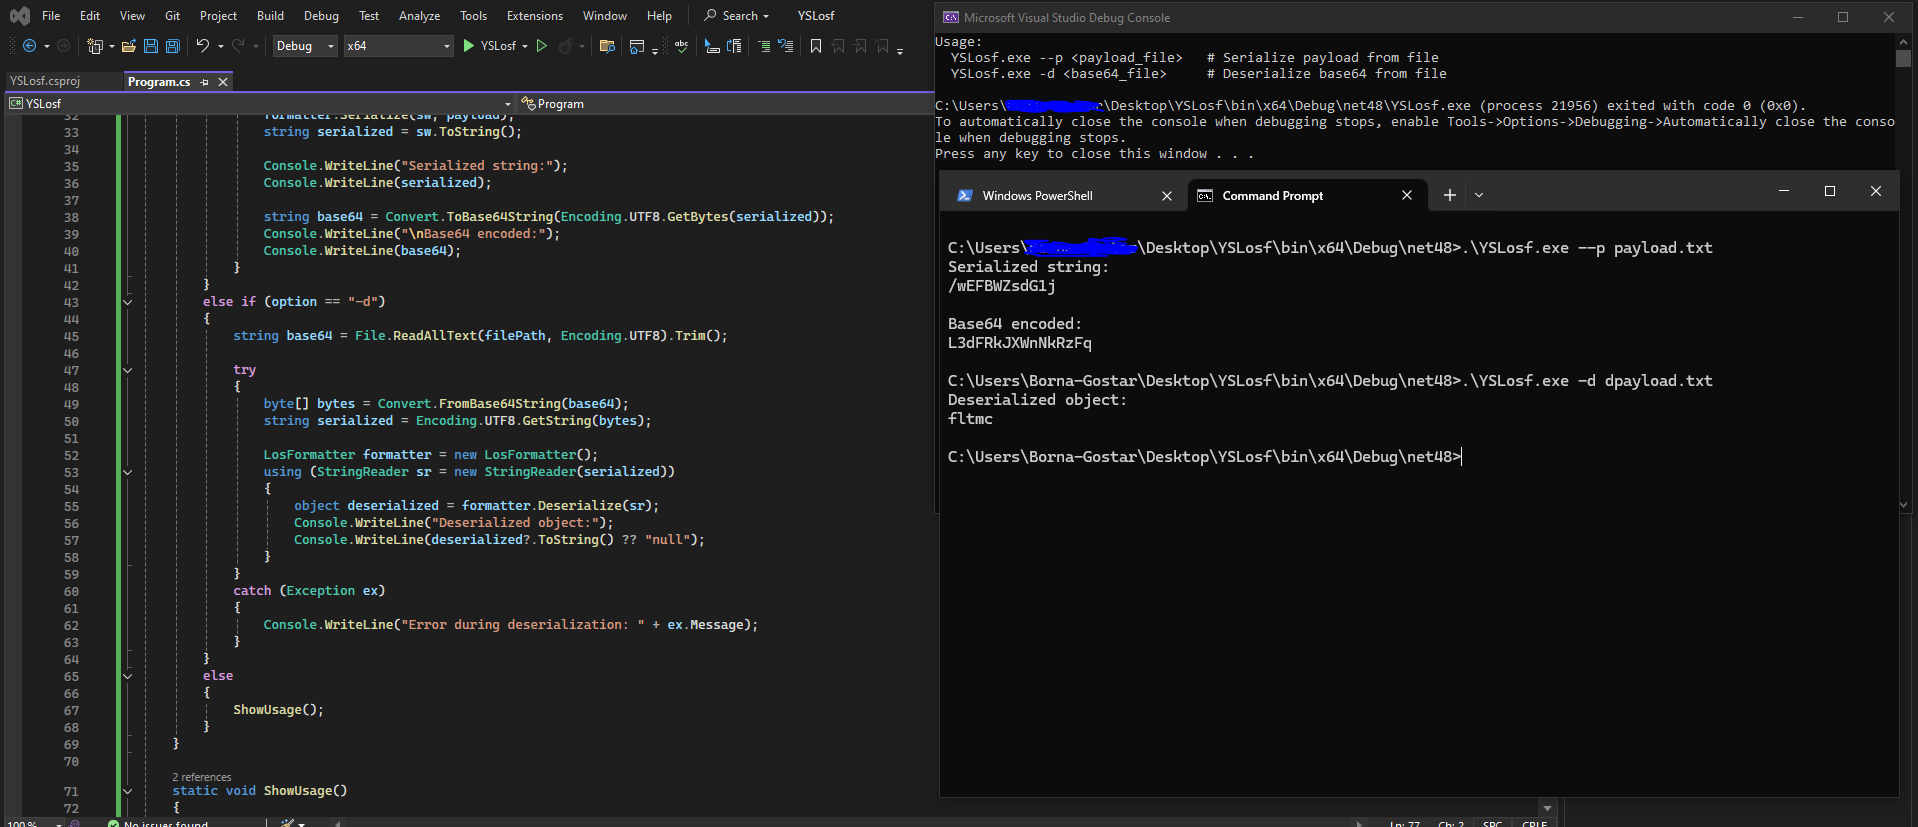 soltanali0/cve-2025-53770-exploit
SharePoint WebPart Injection Exploit Tool
 0xdtc/below-logger-symlink-attack_cve-2025-27591
A Bash-based privilege escalation exploit targeting the `below` system performance monitoring tool. This refurbished exploit leverages a symlink…
 theethat-thamwasin/cve-2025-63307
An authenticated Stored Cross-site Scripting (XSS) vulnerability in laravel-file-manager v3.3.1 and below allows attackers with access to the file…
 ajansha/cve-2025-60378
Proof of concept for stored HTML injection in RISE CRM, demonstrating how authenticated users can inject malicious HTML into invoices and messages,…
 mrk336/cve-2025-42957-sap-s-4hana-under-siege
CVE‑2025‑42957 exposes an RFC‑enabled SAP S/4HANA module that lets low‑privileged users inject ABAP code to create admin accounts and gain full…
 rrespxwnss/cve-2025-56771
During analysis of the ecodotempo.com.br website, a Stored Cross-Site Scripting (XSS) vulnerability was discovered. This vulnerability allows an…
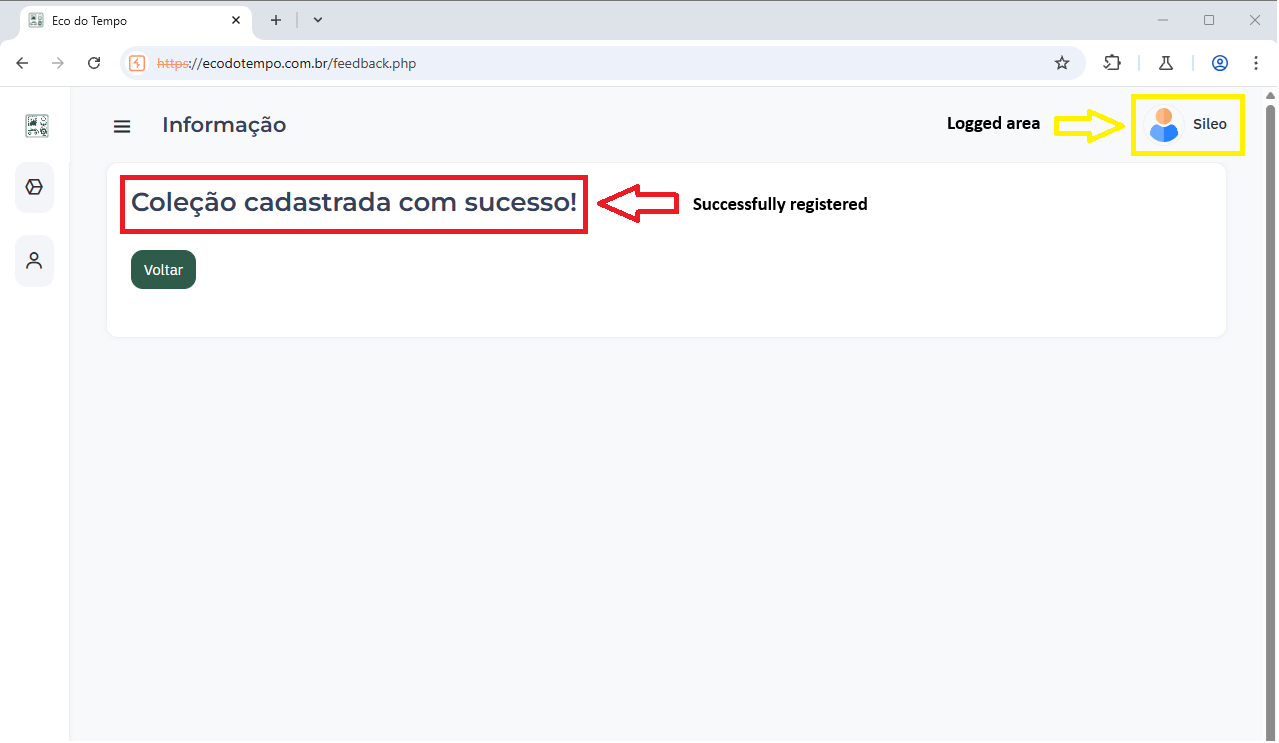 rrespxwnss/cve-2025-56772
During the analysis of the website ecodotempo.com.br, a Stored Cross-Site Scripting (XSS) vulnerability was discovered. This vulnerability allows an…
 thekin-ctrl/cve-2025-27591-below
Proof-of-concept exploit for CVE-2025-27591, a local privilege escalation in the 'below' system monitor. Demonstrates symlink attack on log file to…
 aninfosec/cve-2025-1094
It is an input sanitization flaw caused by an encoding mismatch, allowing crafted input to bypass filters. If a server is vulnerable, an attacker can…
 akhlak2511/cve-2024-50969
Proof-of-concept for a reflected XSS vulnerability in Code-projects Jonnys Liquor 1.0, demonstrating script injection via the search parameter in…