
macnoise
 0xv1n/macnoise
Extensible MacOS system telemetry generator.
defensive-toolseducationincident-response+4
0xv1n/macnoiseExtensible MacOS system telemetry generator.
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
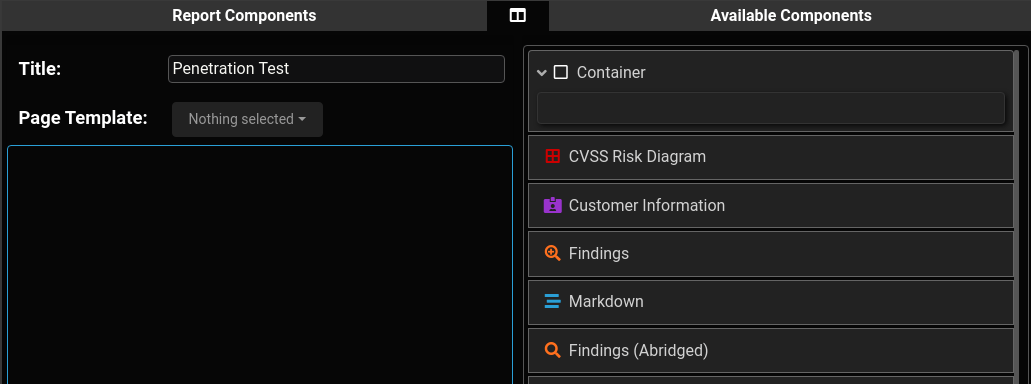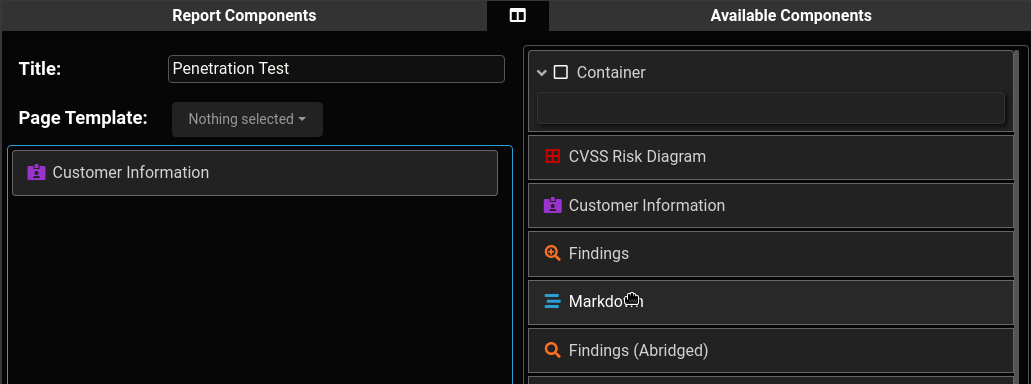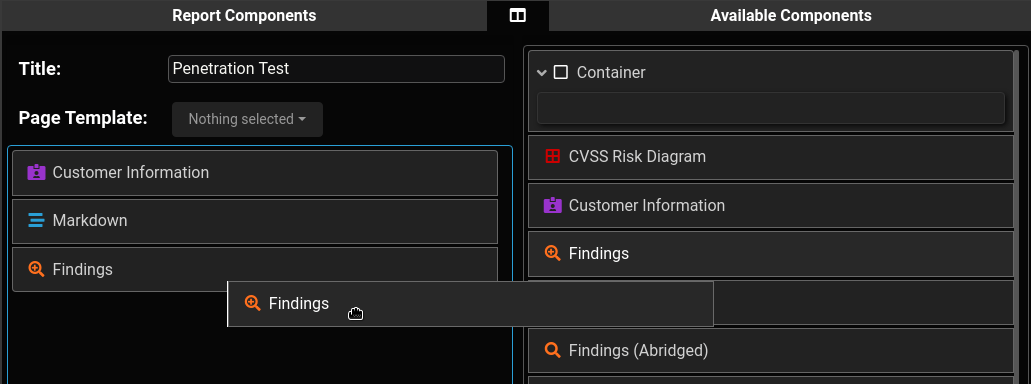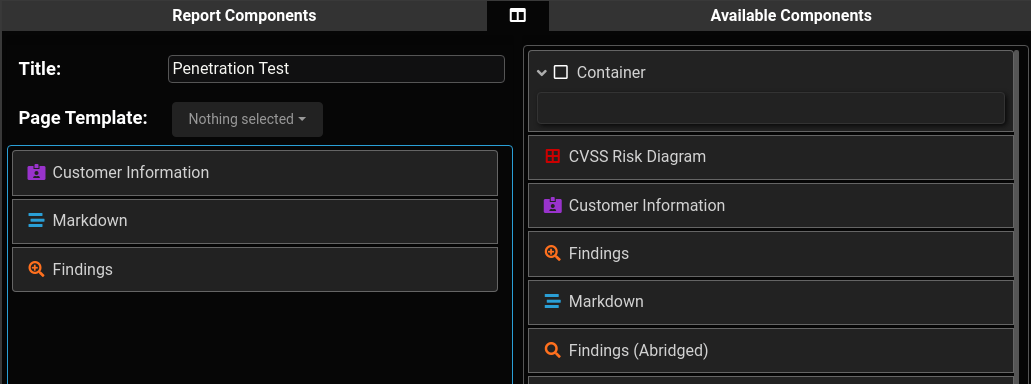 blacklanternsecurity/writehat
A pentest reporting tool written in Python. Free yourself from Microsoft Word.
 oscerd/cve-2026-91858
Runnable Spring Boot and Quarkus reproducer for CVE-2026-91858, an XXE in Apache Camel camel-fop via a third-party TransformerFactory, with affected…
 oscerd/cve-2026-85313
Runnable Spring Boot proof-of-concept reproducing CVE-2026-85313, where Apache Camel camel-jetty enableCORS reflects any origin with credentials,…
 oscerd/cve-2026-85250
Runnable XXE proof-of-concept for CVE-2026-85250 in Apache Camel camel-xpath (documentType=InputSource), with Spring Boot and Quarkus affected vs…
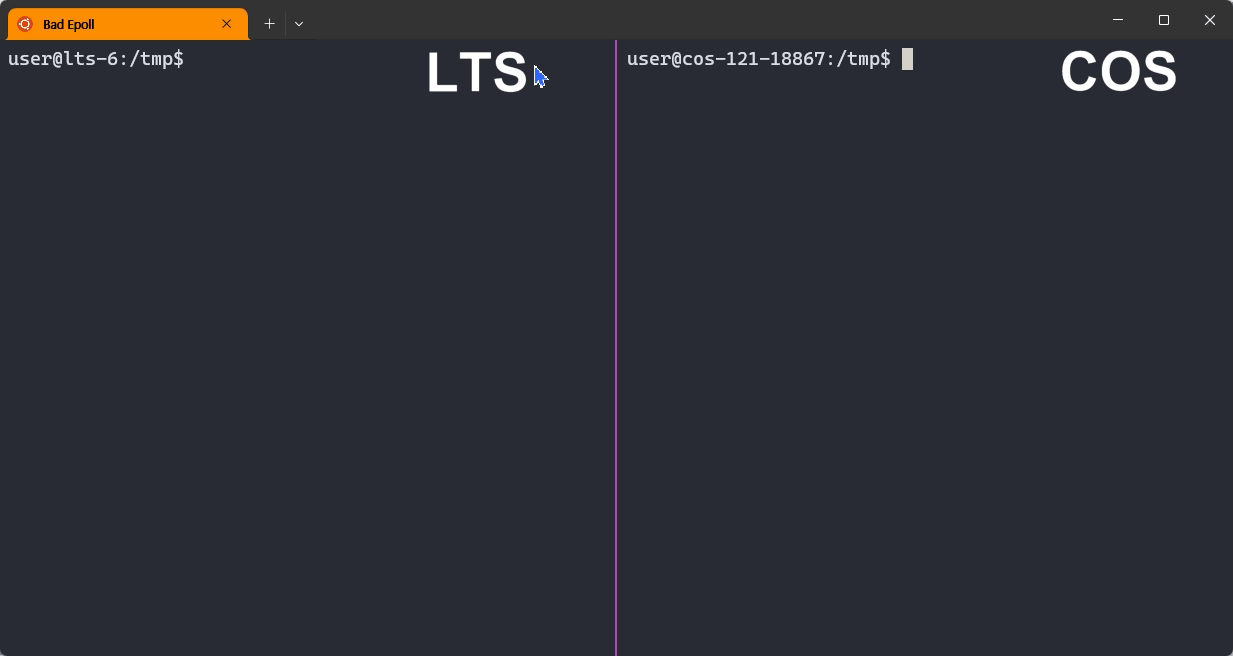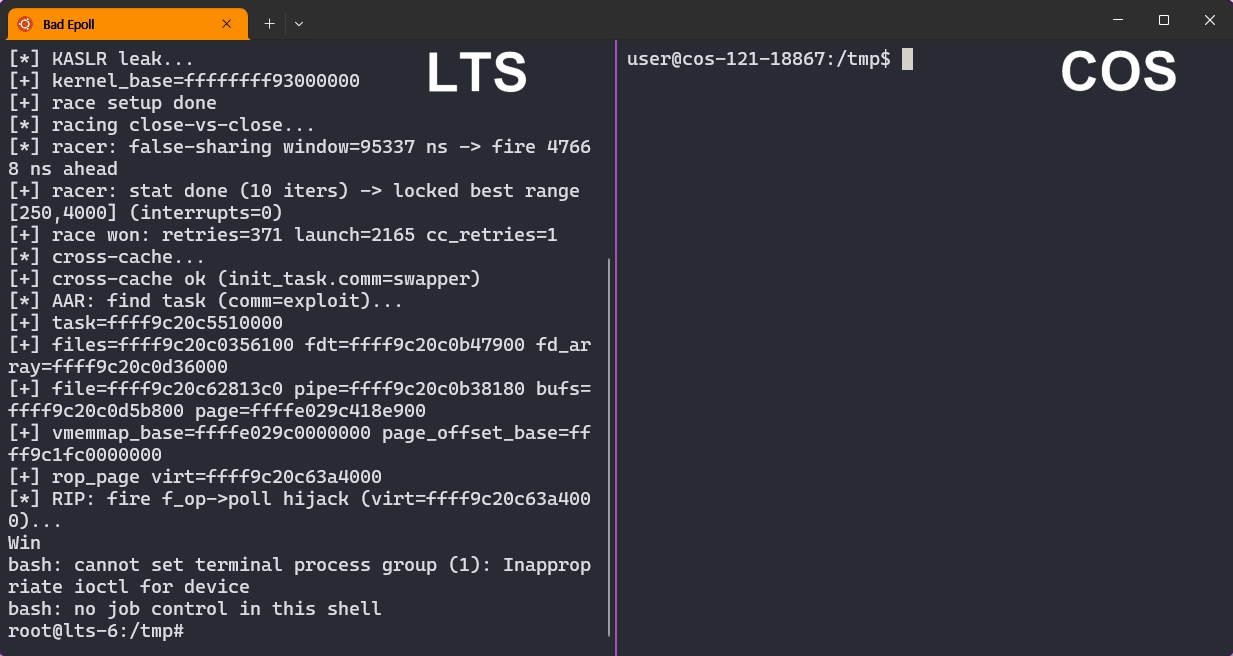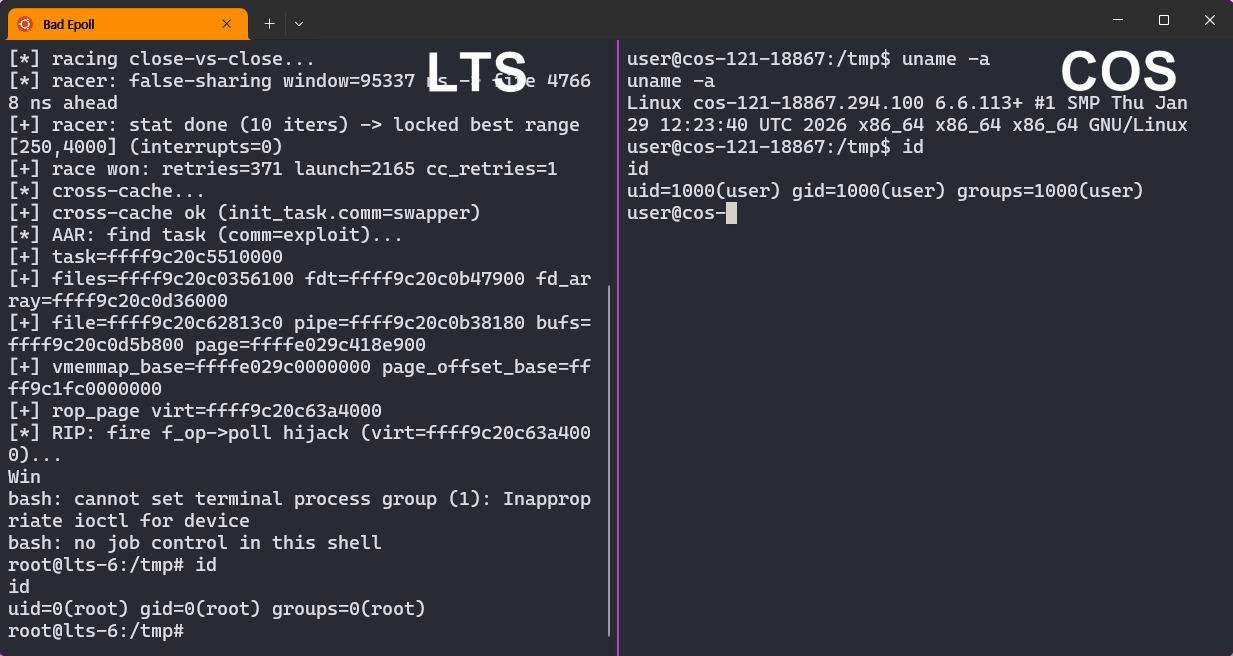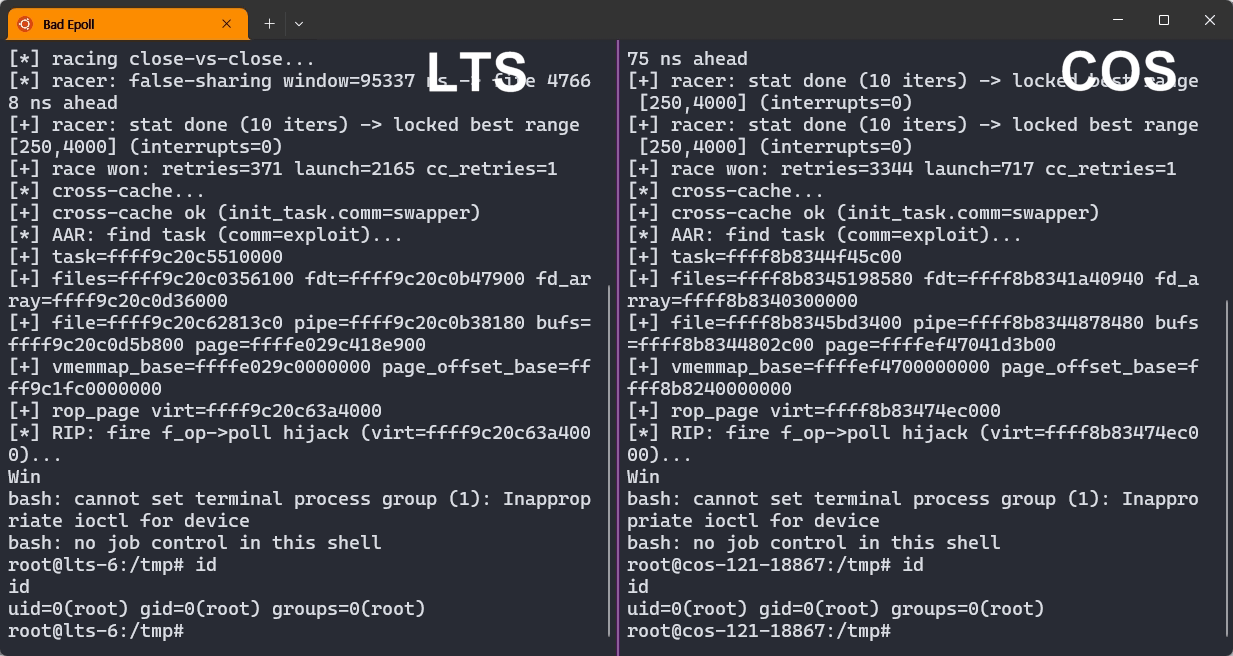 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…
 jeanextreme002/pymemoryeditor
A pure-Python library, app and MCP that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 owasp/pscf
OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…
 deathshotxd/0xkern3lcrush
Advanced PoC & Research for CVE-2026-0828 (Safetica) and CVE-2025-7771 (ThrottleStop). Analysis of BYOVD (Bring Your Own Vulnerable Driver) TTPs for…

 mevislobo2006/threatripper
Offline heuristic analyzer that scores suspicious SMS, chat messages and links for scam and phishing indicators, explaining each warning sign with…
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 mgiftson0/linux-env-vars-shellshock-lab
technical research & analysis on linux process execution, SUID privilege escalation, LD_PRELOAD hooking, and CVE-2014-6271 (shellshock).
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
 pwardle/not-a-mused
Proof-of-concept exploiting an undocumented Muse dictation endpoint setting, letting a local unprivileged process redirect dictation traffic to…
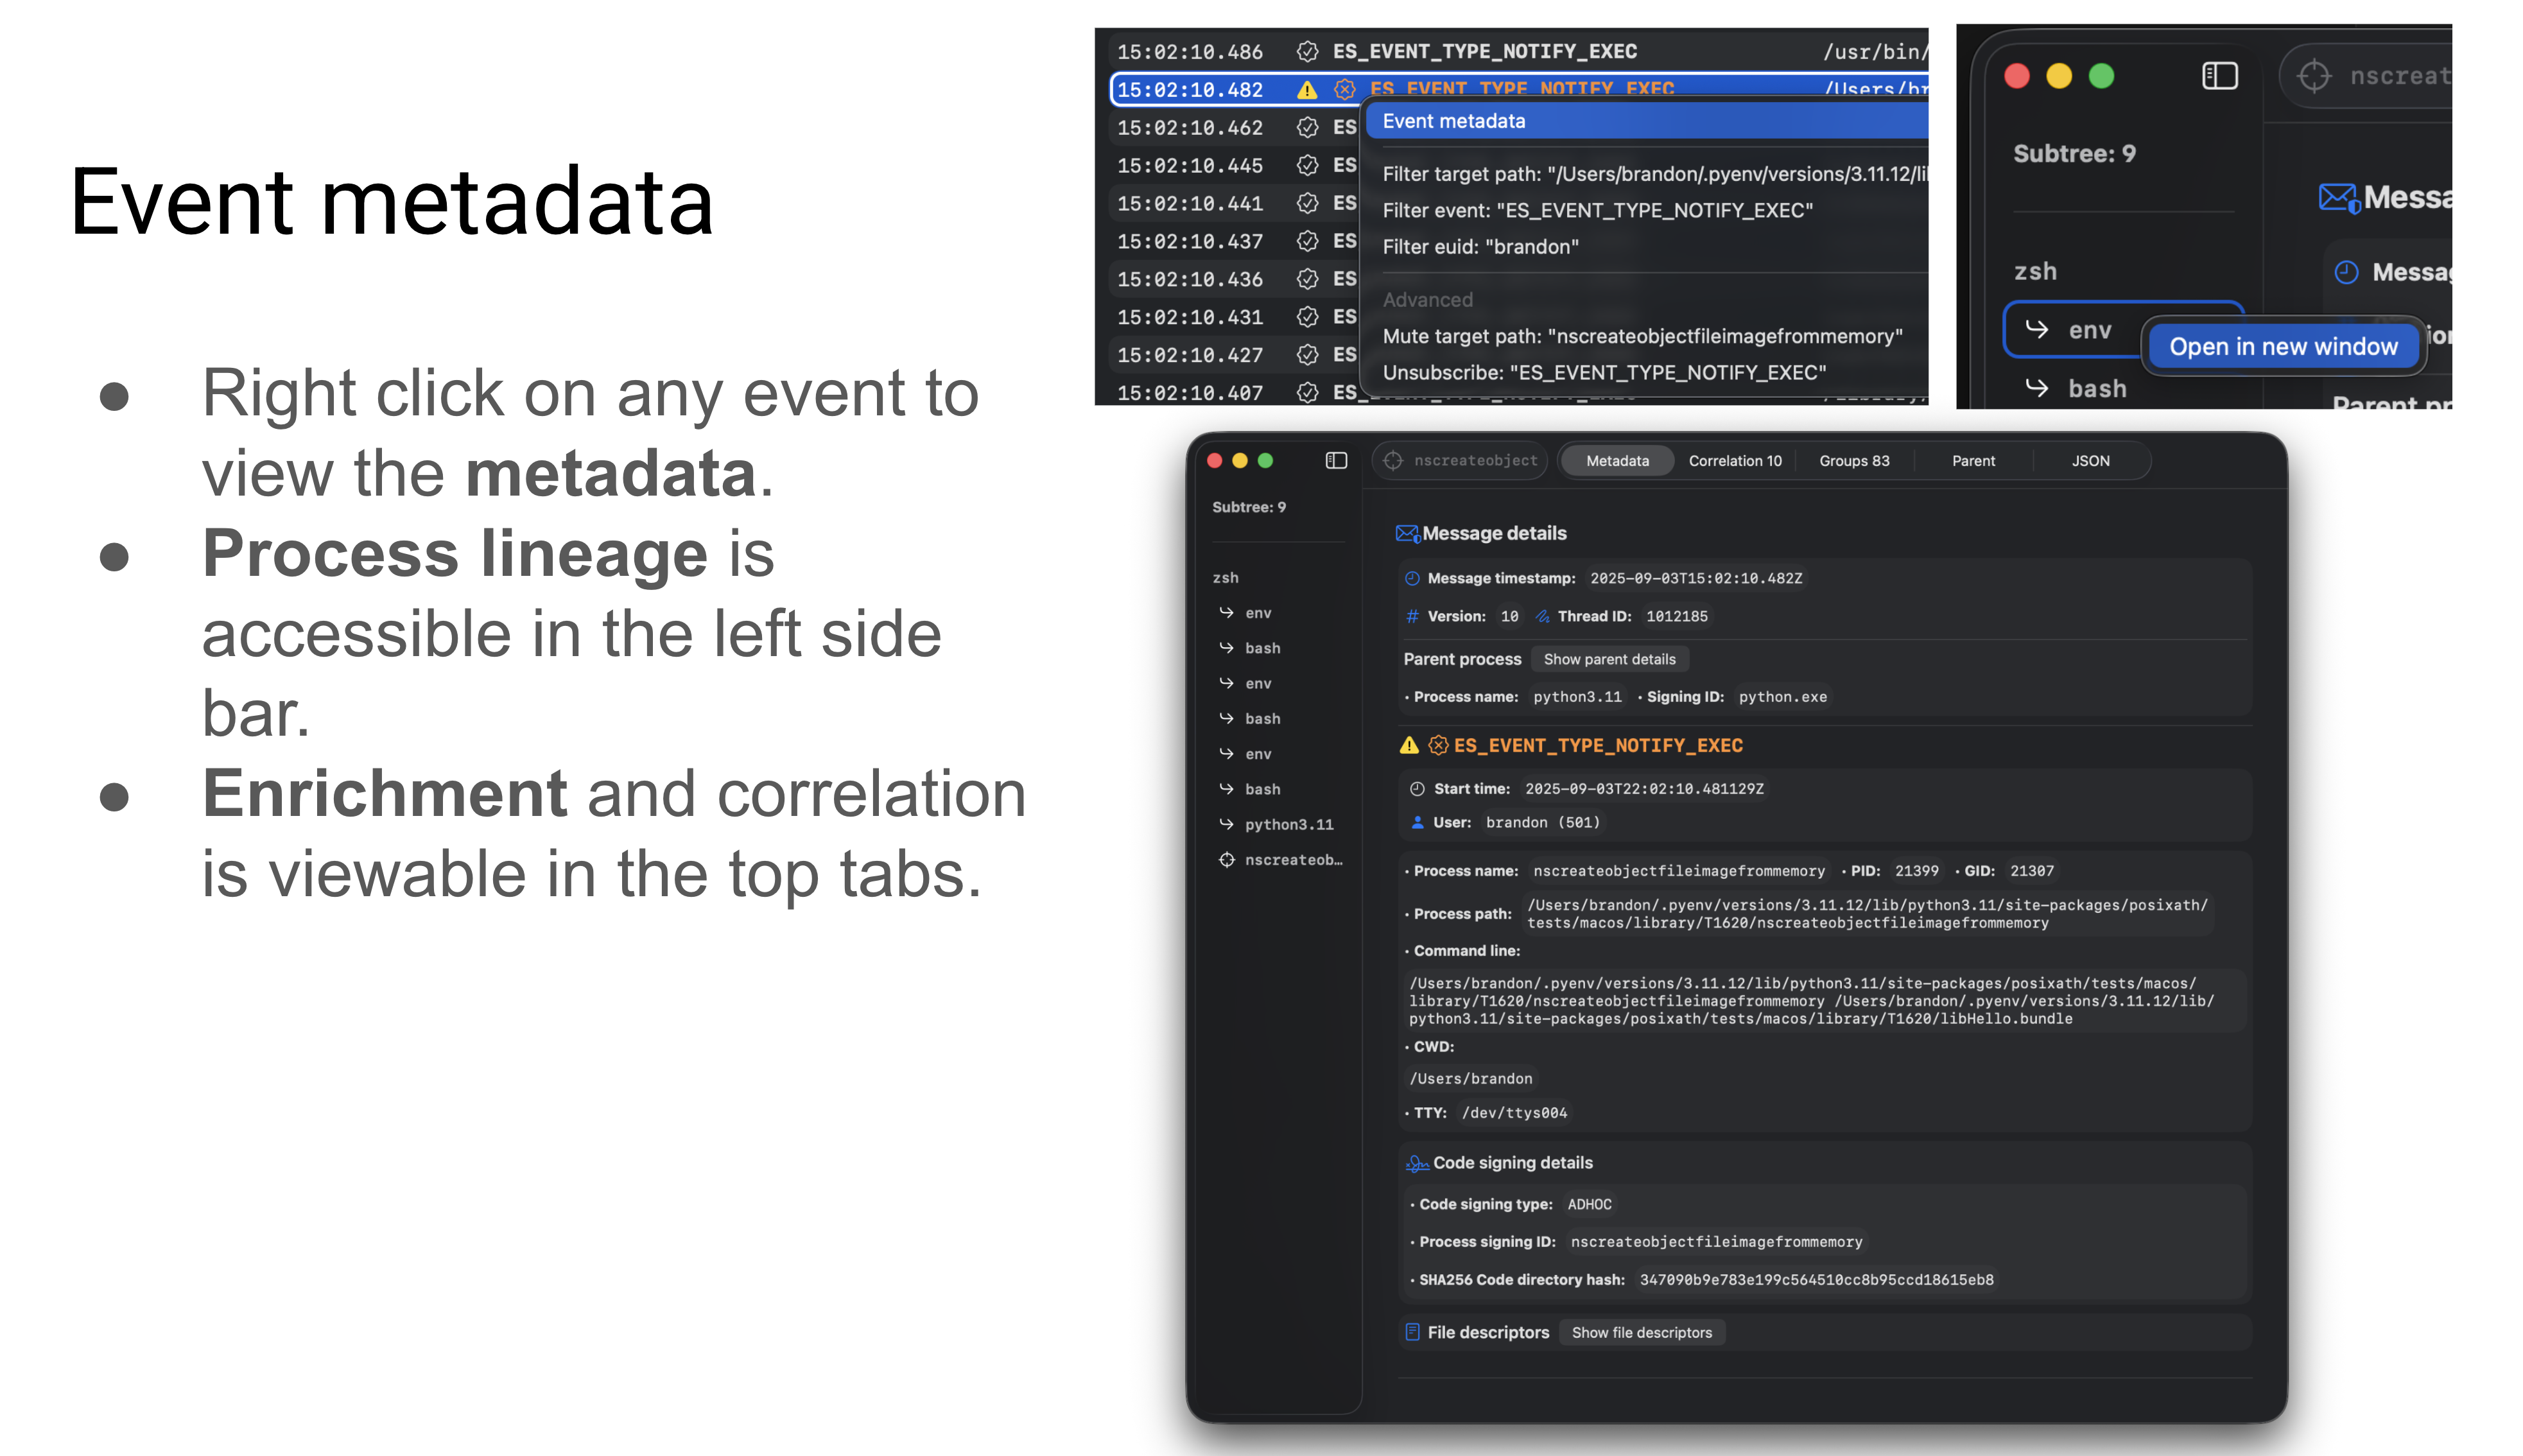 brandon7cc/mac-monitor
Advanced macOS system monitor leveraging Apple Endpoint Security to collect, enrich, and display process, file, memory, and XPC events for malware…
 tejasprasad2008-afk/tracetree
Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…
 fabianch20/soc335---cve-2024-49138-exploitation-detected
SOC335 incident response walkthrough for CVE-2024-49138 CLFS privilege escalation, covering alert triage, threat intel enrichment, process tree…