
open-sammy
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
cloud-securityconfiguration-auditingcontainer-security+3
29
owasp/open-sammyWeb-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 abraxas/php-stale-global-uaf
PHP 8.5.11 - Critical - Remote - UAF - CVE-2026-109619 PHP2Shell. Same-worker fatal backtrace then INI diagnostic on Apache mod_php. Lab vs 8.5.12.…
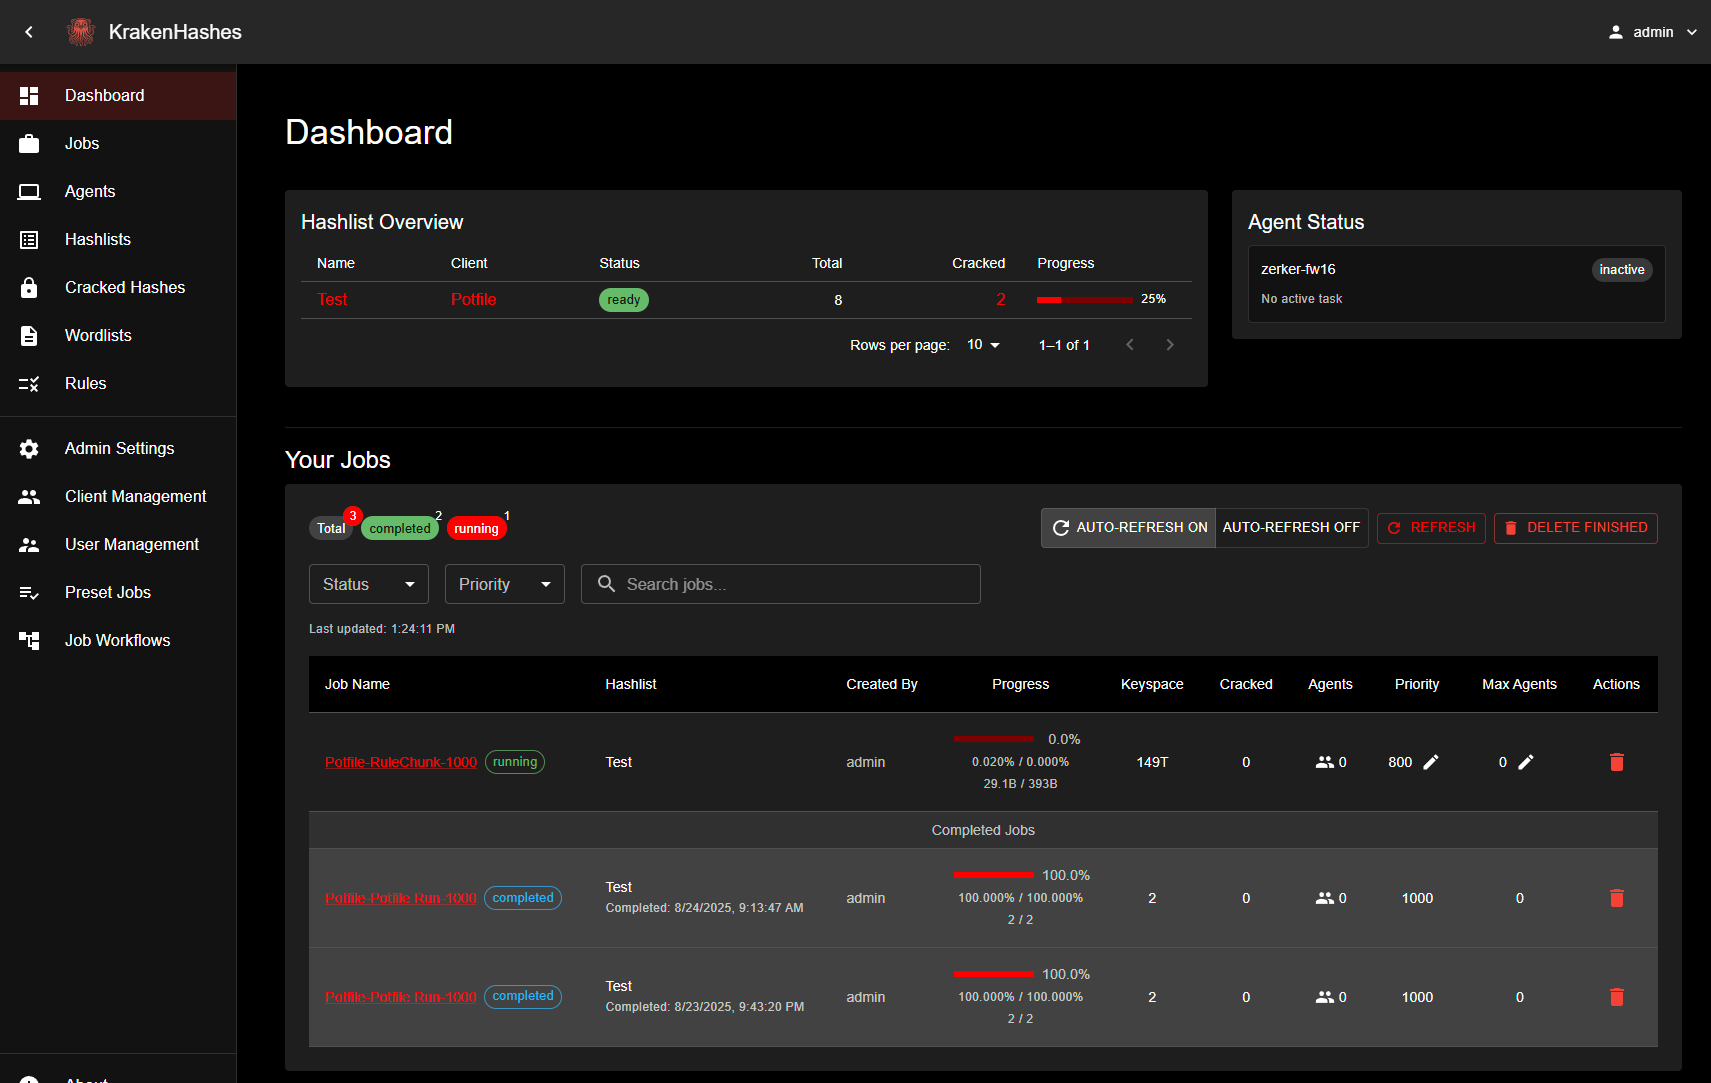 zerkereod/krakenhashes
Distributed password cracking platform coordinating GPU/CPU agents via Hashcat for high-speed hash recovery, with real-time job management,…
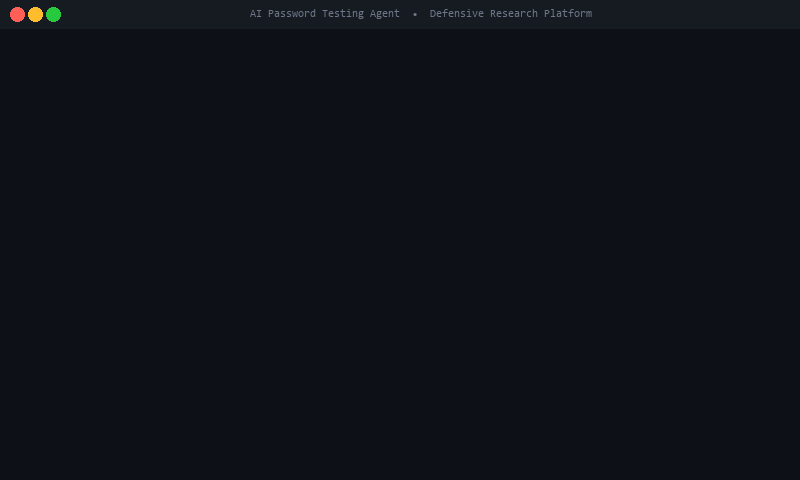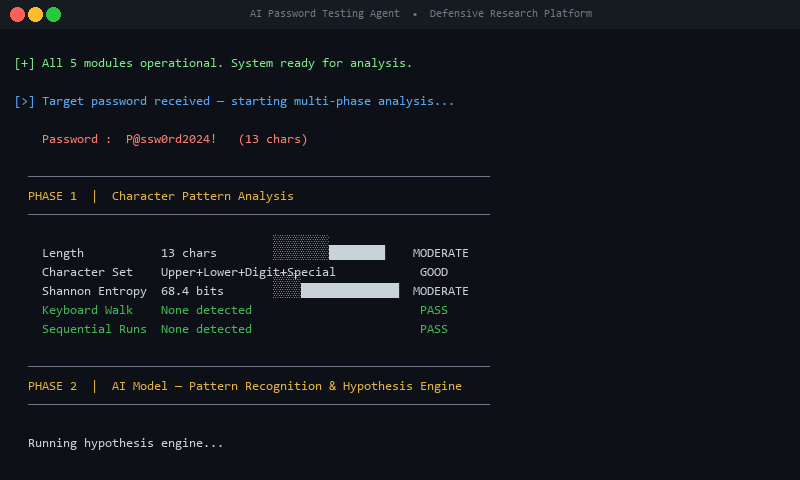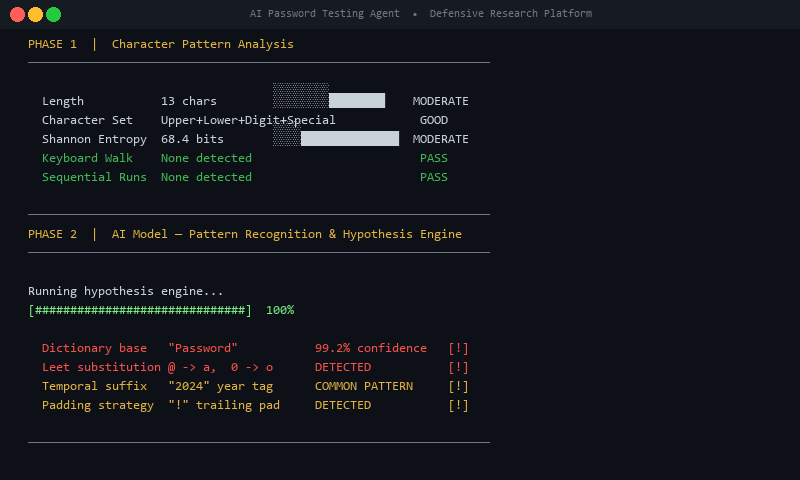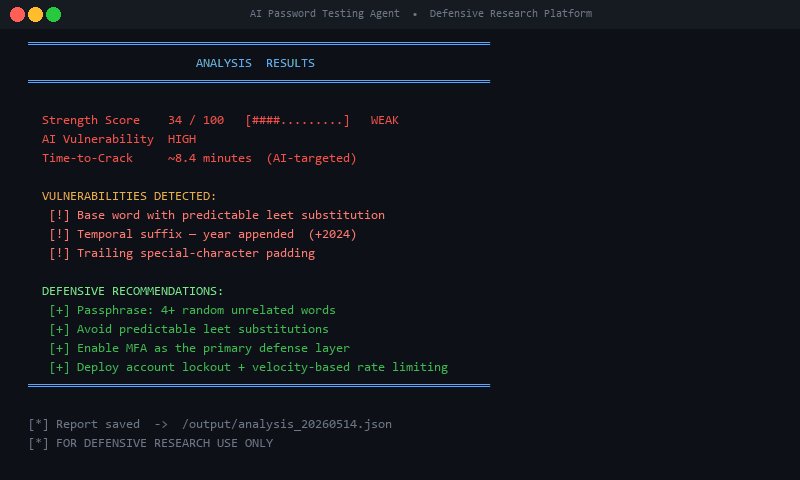 insider77circle/ai-password-testing-agent
An intelligent agent for testing password strength, identifying vulnerabilities, and exploring patterns in password creation.
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 bandrel/hashcatrosetta
Hashcat rule analyzer and interpreter - A Rosetta Stone for decoding hashcat rule syntax
 ihebski/defaultcreds-cheat-sheet
One place for all the default credentials to assist the Blue/Red teamers identifying devices with default password 🛡️
 pervinzahidli/cve-2026-77771
Advisory for CVE-2026-77771, a 2FA bypass in the miniOrange WordPress plugin via session-scoped OTP lockout, with impact analysis and remediation…
 het-p301204/afterlife
Revocation persistence detection lab: when the password reset succeeds but the attacker never leaves. Reproduces the Strapi CVE-2026-22706…
 n0kovo/awesome-password-cracking
A curated list of awesome tools, research, papers and other projects related to password cracking and password security.
 feartheploto/gitlab-cve-2023-7028
Mock vulnerable GitLab instance reproducing CVE-2023-7028 password reset hijack. Demonstrates array-based email parameter exploitation and account…
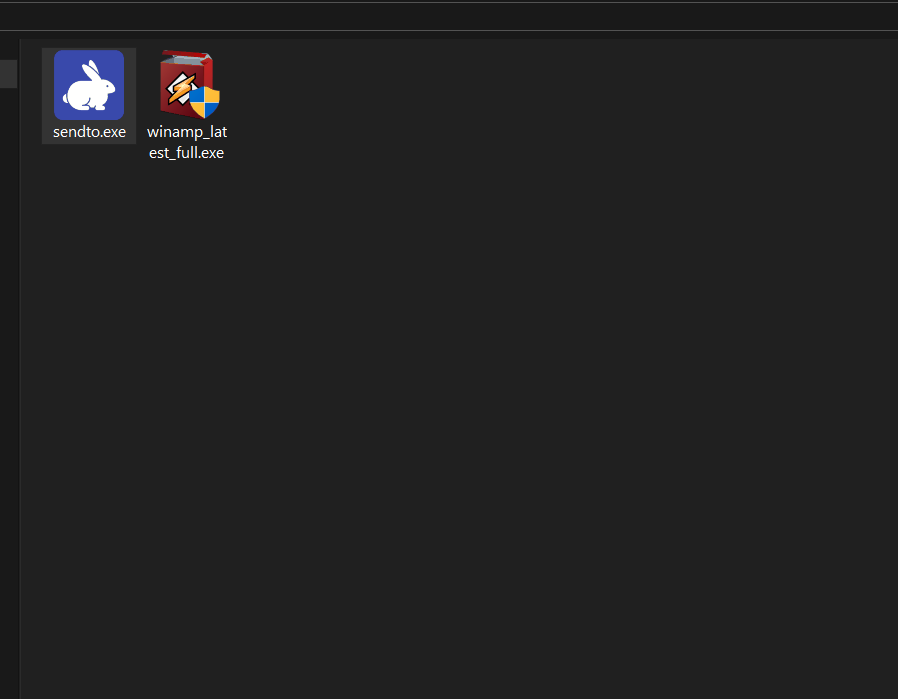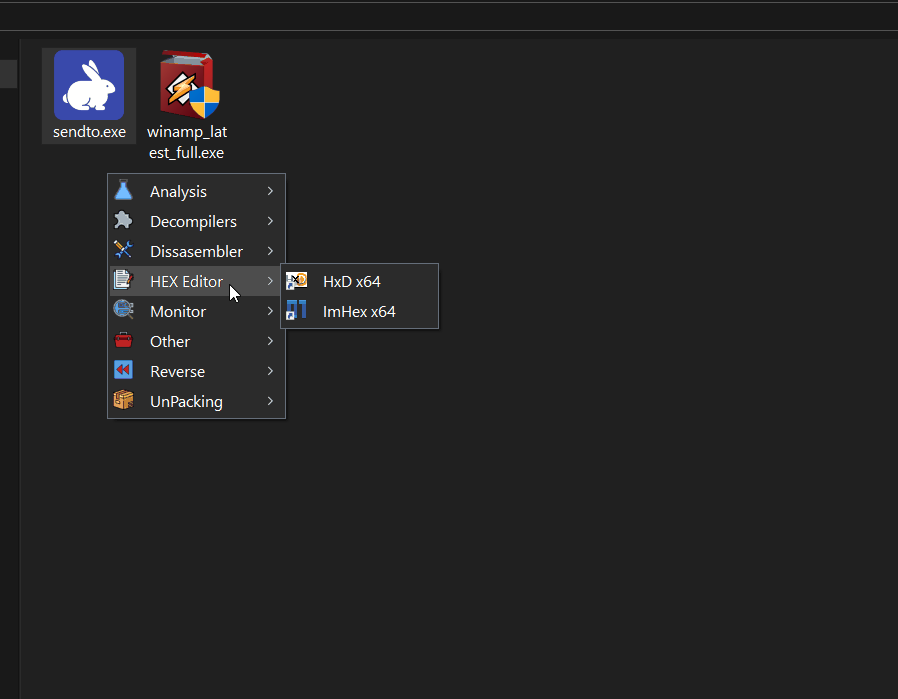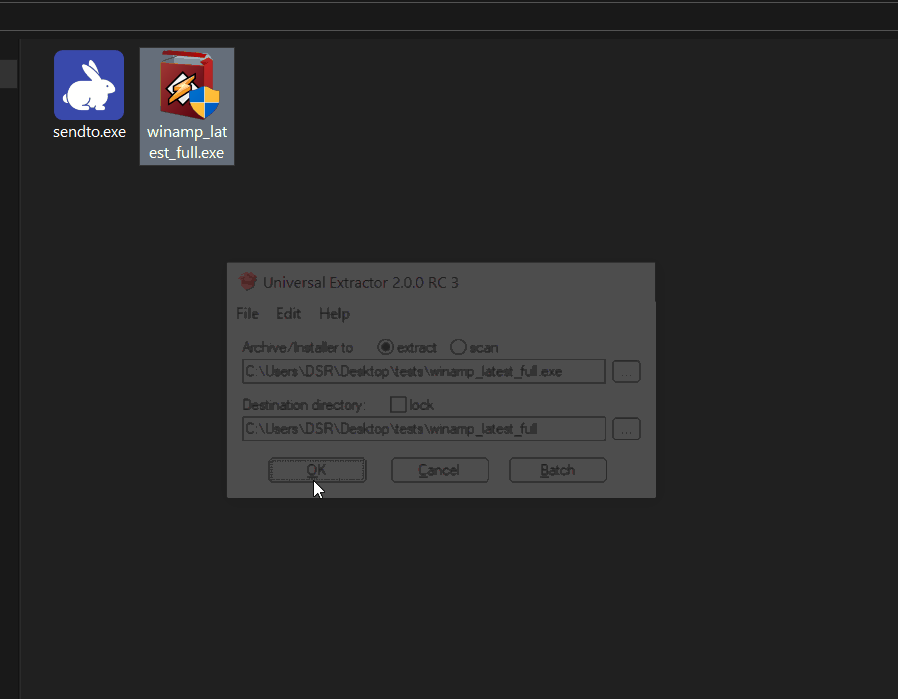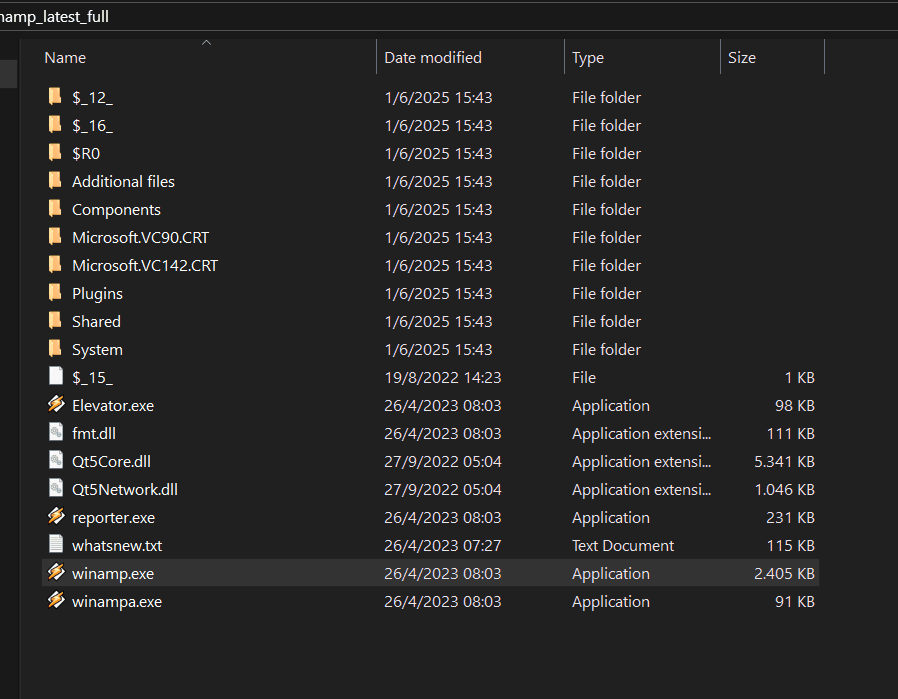 indetectables-net/toolkit
Curated Windows toolkit for reverse engineering, malware analysis, and password cracking. Includes 101 pre-configured tools with automatic updates…
 venablee/cve-2026-30252
The ZenShare Suite application is vulnerable by a Reflected Cross-Site Scripting (XSS) vulnerability, affecting web application login and recovery…
 camillegr/cve-2026-73292
Proof-of-concept exploit for CVE-2026-73292: CSRF attack on Semaphore UI password change endpoint, serving a malicious page that silently resets an…
 seemoo-lab/openwifipass
An open source implementation of Apple's Wi-Fi Password Sharing protocol in Python.
 ch4120n/cve-2026-55579
CVE-2026-55579 – Unauthenticated RCE in Pheditor via hardcoded default password "admin". Full Python exploit with file upload & terminal execution.…
 shinthink/cve-2025-32044
Moodle 4.5.0-4.5.2 Unauthenticated REST API User Data Exposure via Stack Trace Args Leak | CVSS 7.5
 mmoobbeeiidat-design/hack-the-box-enigma-findings-report
HTB_Enigma Security Assessment – Full pentest completed, chaining NFS disclosure, IMAPS password reuse, and OS Command Injection in OpenSTAManager…