


 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 nekr0ff/needrestart-sudo-escalate-cve-2024-4890
PoC exploit for CVE-2024-4890: Sudo privilege escalation via neecdrestart (>=3.8). Ethical lab-only. Scripts in Python and C.
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 wmal/linux-kodachi
Hardened Debian-based privacy OS with pre-integrated anonymity stack (Tor, VPN, DNSCrypt), anti-forensic tooling, SOC security center, and standalone…
 ph4l4nx/ctf-s-tools
Repository to index useful tools for CTF's
 hhhrrrttt222111/ethical-hacking-tools
Complete Listing and Usage of Tools used for Ethical Hacking
 bst04/cybersources
A curated list of cybersecurity tools and resources.
 crypto-unict/ghostfacempc
Reference implementation of privacy-preserving face recognition using replicated secret sharing in MP-SPDZ, with quantized GhostFaceNet inference,…
 ashardev002/cve-2025-32463_chwoot
🔍 Demonstrate the CVE-2025-32463 privilege-escalation flaw in sudo's chroot feature with this minimal, reproducible proof of concept environment.
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 aramosf/cve-2026-61500
Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.
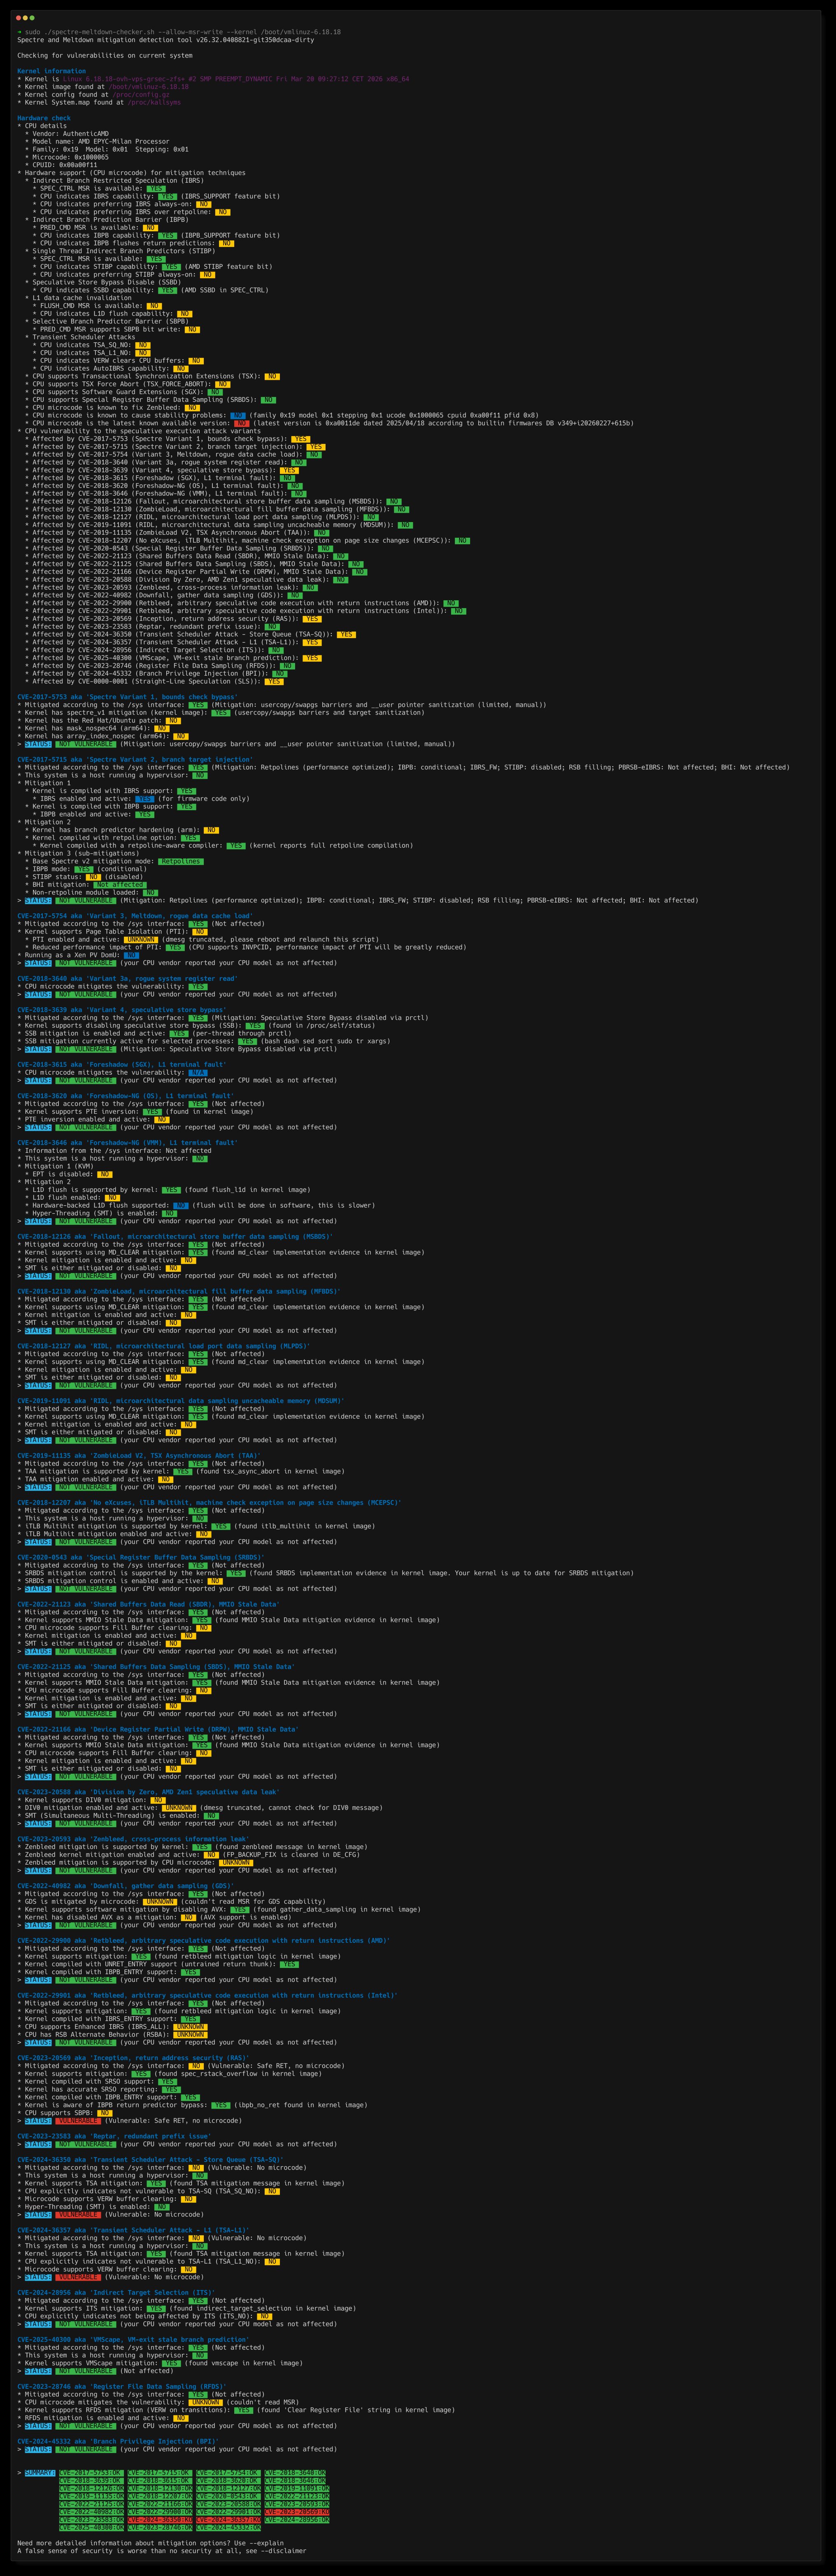 speed47/spectre-meltdown-checker
Reptar, Downfall, Zenbleed, ZombieLoad, RIDL, Fallout, Foreshadow, Spectre, Meltdown vulnerability/mitigation checker for Linux & BSD
 v1s1t0r1sh3r3/airgeddon
This is a multi-use bash script for Linux systems to audit wireless networks.
 priyanshu-rawa/cybersecurity-handbook
Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.
 kongqbin/cve-2016-5195
Educational implementation of the Dirty COW (CVE-2016-5195) privilege escalation exploit, including race condition payload and SUID-based root shell…
 haomin-yu/cve-2024-13176-timing-analysis
Instrumented analysis and reproducibility materials for ECDSA timing leakage in OpenSSL CVE-2024-13176