
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
20 results
HijackLibs preview

HijackLibs

GitHubwietze/hijacklibs

Project for tracking publicly disclosed DLL Hijacking opportunities.
curated-resourceseducationinformation-gathering+3
9275 days ago
malware-analysis-fake-hwmonitor preview

malware-analysis-fake-hwmonitor

GitHubdmitry-matvienko/malware-analysis-fake-hwmonitor

Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor

defensive-toolsdigital-forensicseducation+6
21 month ago
DLLHijackHunter preview

DLLHijackHunter

GitHubghostvectoracademy/dllhijackhunter

Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.

binary-analysisdynamic-code-analysiseducation+8
3961 month ago
EternalBlueC preview

EternalBlueC

GitHubbhassani/eternalbluec

EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
binary-exploitationeducationexploitation+7
6131 month ago
CVE-2026-50343-InstallService-EoP preview

CVE-2026-50343-InstallService-EoP

GitHubrat5ak/cve-2026-50343-installservice-eop

CVE-2026-50343 InstallService StaticPluginMap EoP - standard user to SYSTEM
binary-exploitationeducationexploitation+3
483 months ago
staged-DLL-Injection-SMB- preview

staged-DLL-Injection-SMB-

GitHubkasturixbm5/staged-dll-injection-smb-

Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
educationexploitationlabs-practice+5
425 months ago
CVE-2026-4255 preview

CVE-2026-4255

GitHubard33/cve-2026-4255

Proof-of-concept for CVE-2026-4255, a DLL side-loading privilege escalation in Thermalright TR-VISION HOME, demonstrating PATH-based planting of…
binary-exploitationeducationexploitation+4
15 months ago
cve-2026-25676 preview

cve-2026-25676

GitHubnexxus67/cve-2026-25676

Research and proof-of-concept for CVE-2026-25676, a DLL search path hijacking vulnerability in M-Track Duo HD installer, including root cause…
binary-analysisdefensive-toolseducation+3
18 months ago
CVE-2024-38077-MadLicense-exploit preview

CVE-2024-38077-MadLicense-exploit

GitHubermensonx/cve-2024-38077-madlicense-exploit

Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
binary-exploitationeducationexploitation+6
110 months ago
From-EternalBlue-to-CVE-2025-2776-The-Evolution-of-an-SMB-Attack preview

From-EternalBlue-to-CVE-2025-2776-The-Evolution-of-an-SMB-Attack

GitHubmrk336/from-eternalblue-to-cve-2025-2776-the-evolution-of-an-smb-attack

It shook the world in 2017 and has evolved into today’s CVE‑2025‑2776. Microsoft still relies on SMBv1, this article will explain how attackers have…
educationexploitationincident-response+4
1 year ago
Remote-DLL-Injection-with-Timer-based-Shellcode-Execution preview

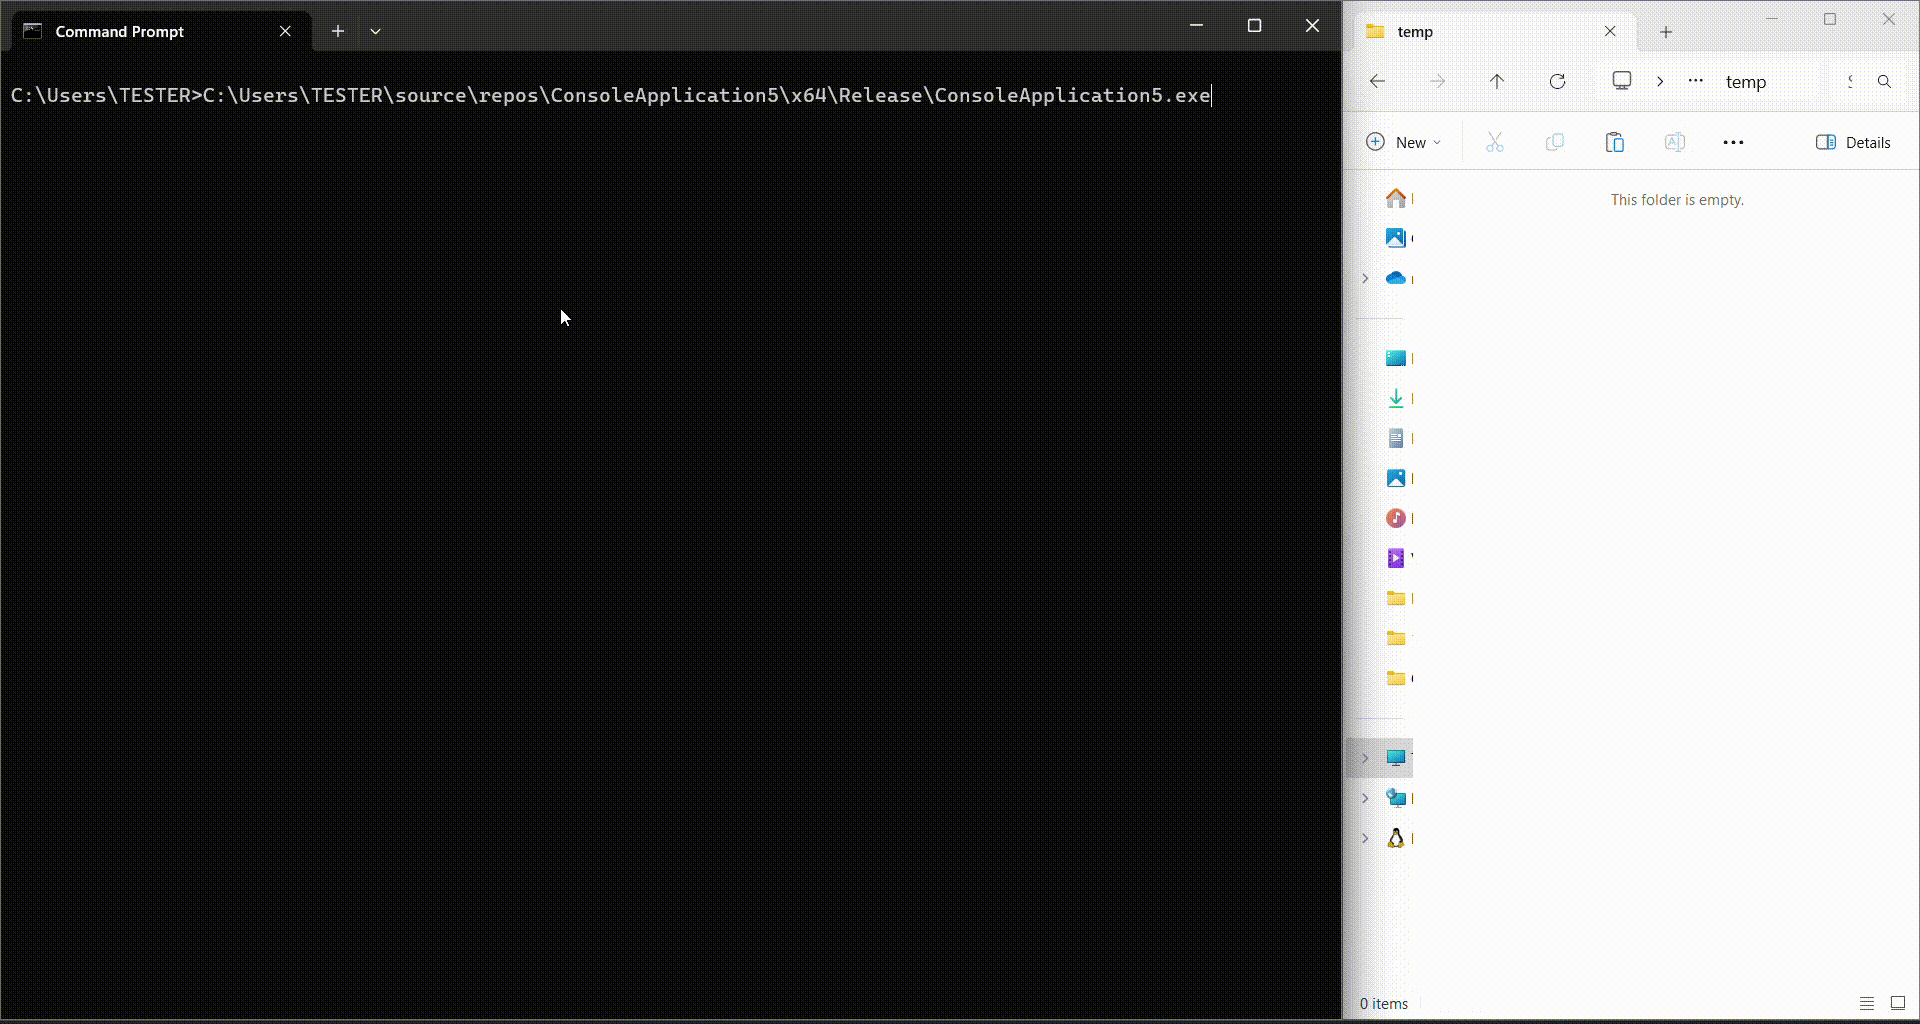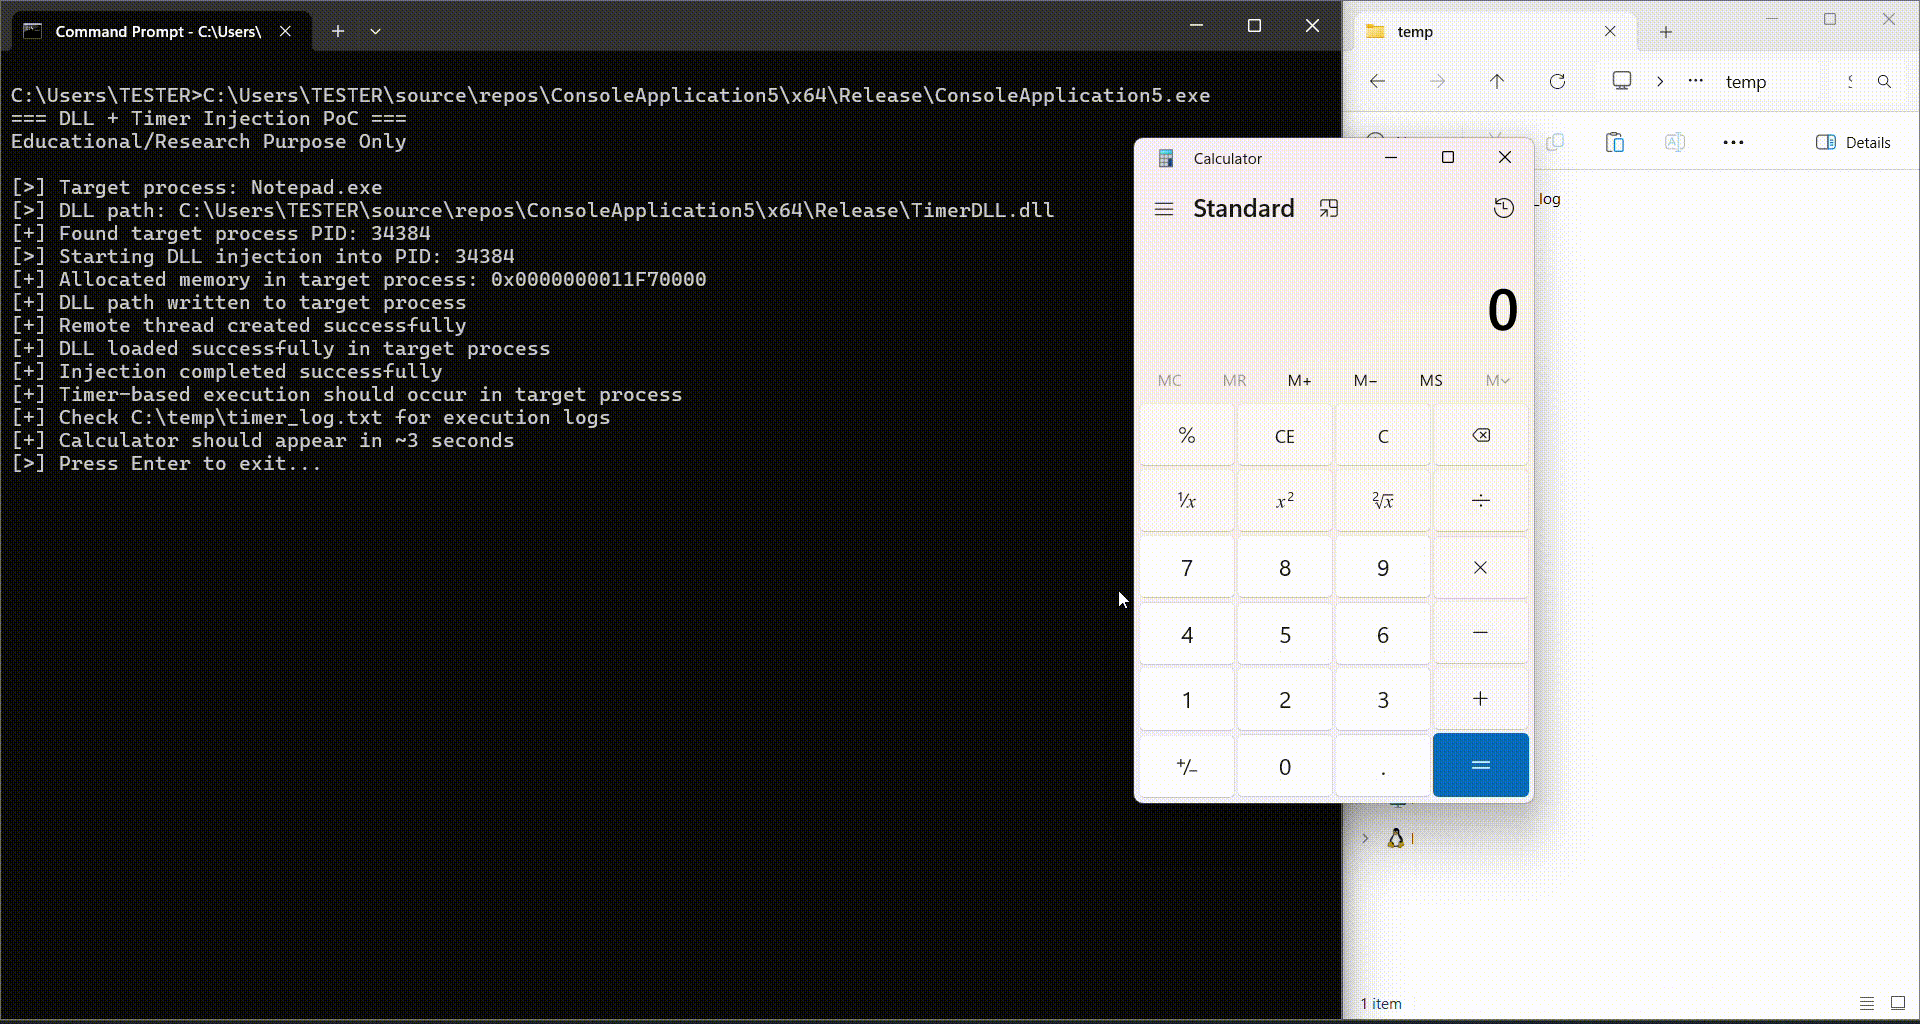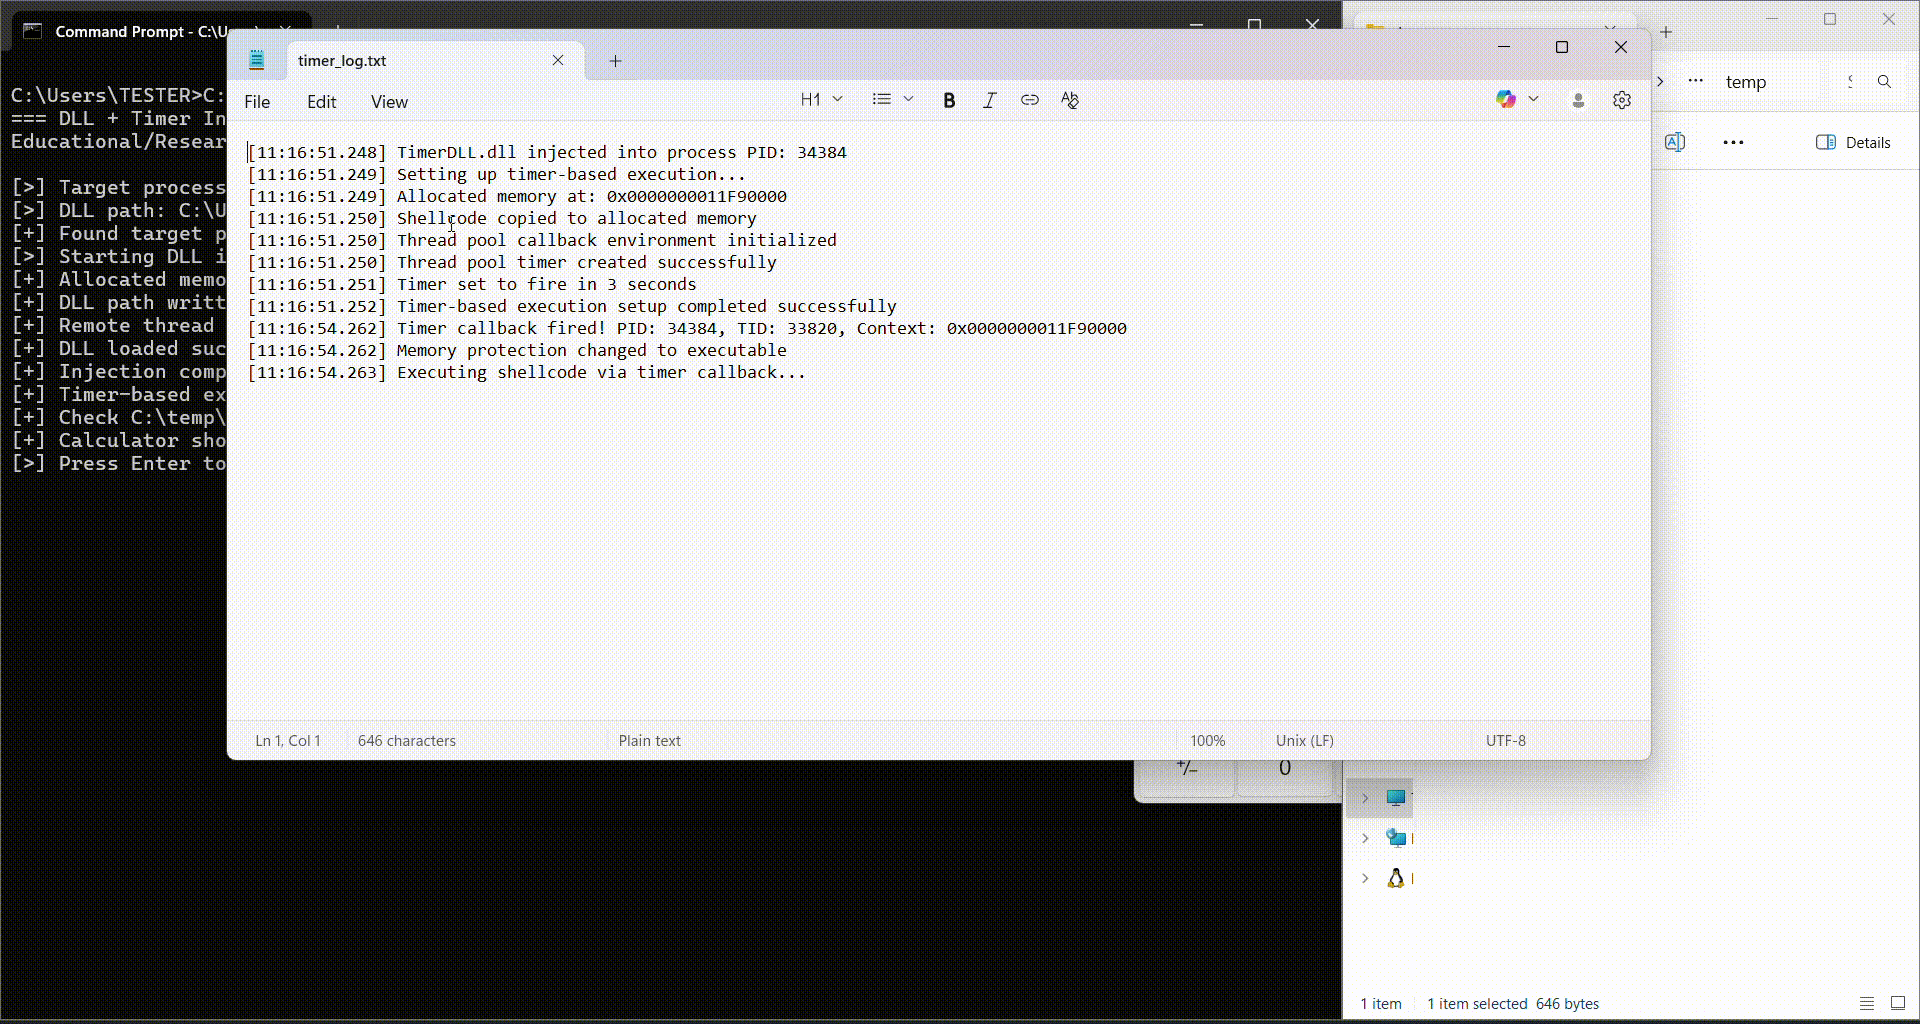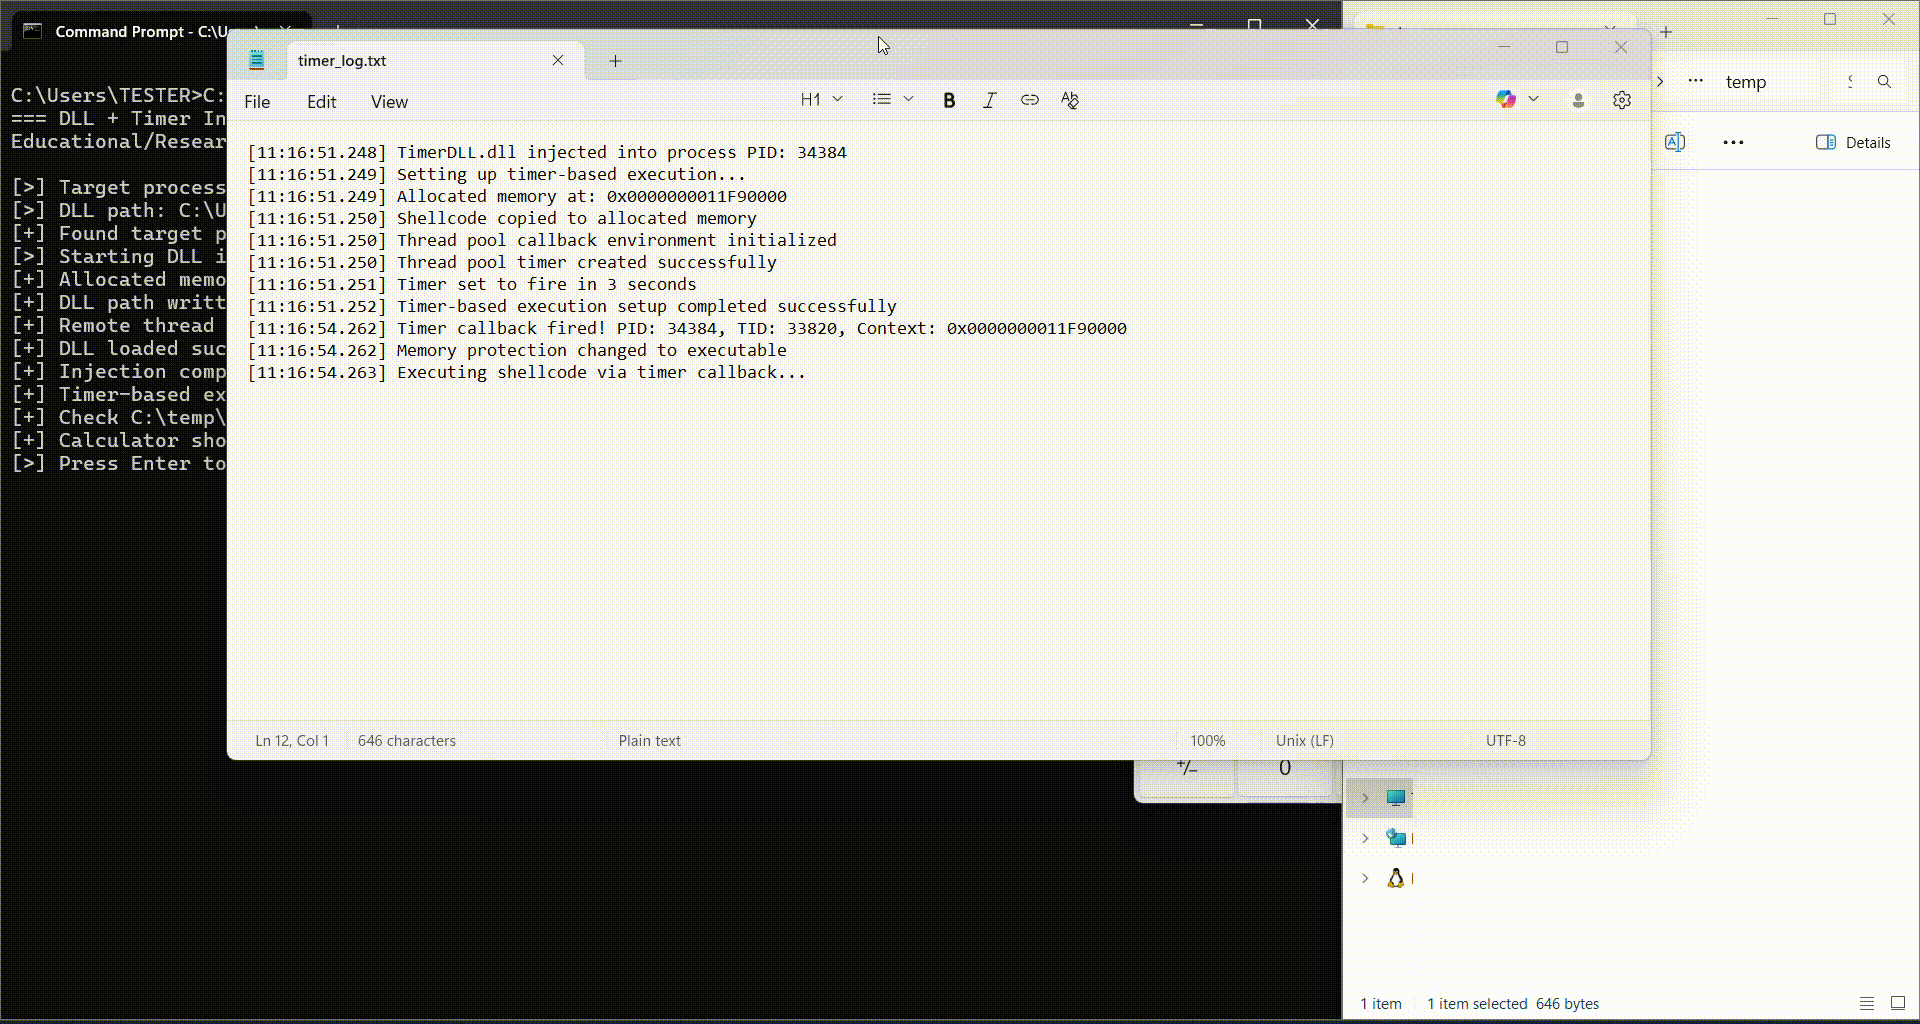
Remote-DLL-Injection-with-Timer-based-Shellcode-Execution

GitHubandreisss/remote-dll-injection-with-timer-based-shellcode-execution

Remote DLL Injection with Timer-based Shellcode Execution
educationexploitationpayload-development+3
2161 year ago
moonwalk preview

moonwalk

GitHubteach2breach/moonwalk

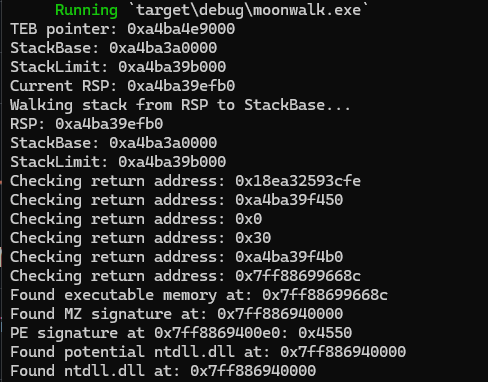
find dll base addresses without PEB WALK
binary-analysiseducationpayload-development+2
1701 year ago
CVE-2023-6401 preview

CVE-2023-6401

GitHubmekitoci/cve-2023-6401

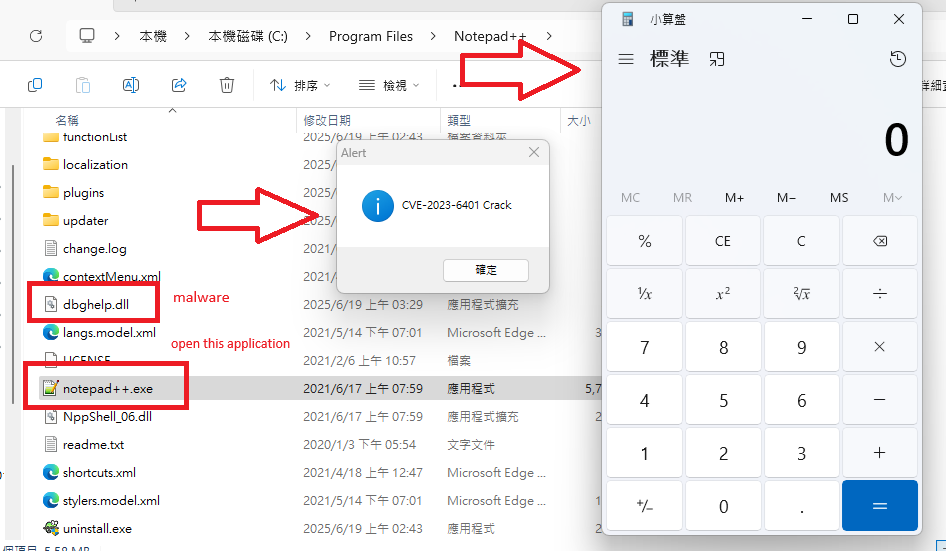
CVE-2023-6401 is a DLL hijacking vulnerability that allows attackers to execute arbitrary code by placing a malicious `dbghelp.dll` file in the…
binary-exploitationeducationexploitation+2
1 year ago
CVE-2025-24076 preview

CVE-2025-24076

GitHubmbanyamer/cve-2025-24076

Python exploit for CVE-2025-24076, a Windows Cross Device Service privilege escalation vulnerability. Replaces a DLL to achieve SYSTEM privileges via…
binary-exploitationeducationexploitation+3
181 year ago
PMD preview

PMD

GitHubrad9800/pmd

Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
binary-analysiseducationlabs-practice+6
1591 year ago
CVE-2024-6769 preview

CVE-2024-6769

GitHubfortra/cve-2024-6769

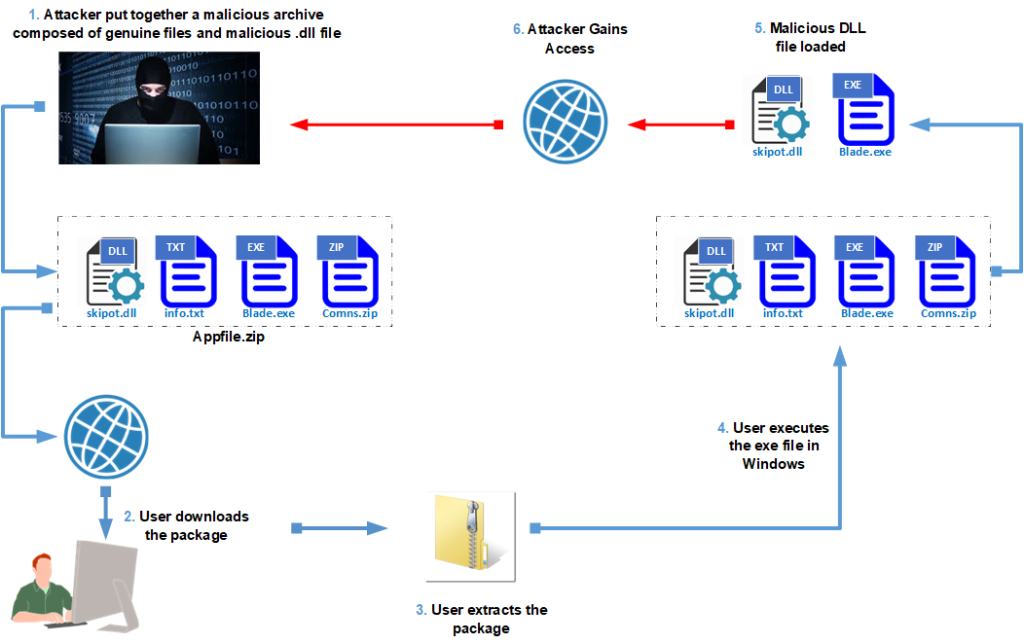
Technical writeup and PoC for CVE-2024-6769, chaining DLL hijacking with activation cache poisoning to escalate from medium to high integrity on…
binary-exploitationeducationexploitation+3
782 years ago
DLL_Injection_On_VLC preview

DLL_Injection_On_VLC

GitHubkobukovui/dll_injection_on_vlc

DLL Injection and CVE-2010-3124
binary-exploitationeducationexploitation+2
12 years ago
windows-api-function-cheatsheets preview

windows-api-function-cheatsheets

GitHubpaddycahil/windows-api-function-cheatsheets

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…

curated-resourceseducationmalware-analysis+3
1212 years ago
Previous12Next