

cve-lite-cli
 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
code-analysiscurated-resourcesdevsecops+5
756
owasp/cve-lite-cliFast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
 rahulreddykarne/cve-2026-65320-fastcore
Documents CVE-2026-65320, a tar-slip path traversal in fastcore's untar_dir(), with a harmless proof-of-concept demonstrating arbitrary file write…
 joaovicdev/exploit-cve-2026-33634
Deliberately vulnerable Docker lab reproducing CVE-2026-33634: LiteLLM gateway SSRF via api_base plus a trojanized dependency, with a multi-phase…
 michel-dv/xz-utils-backdoor-case-study
Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…
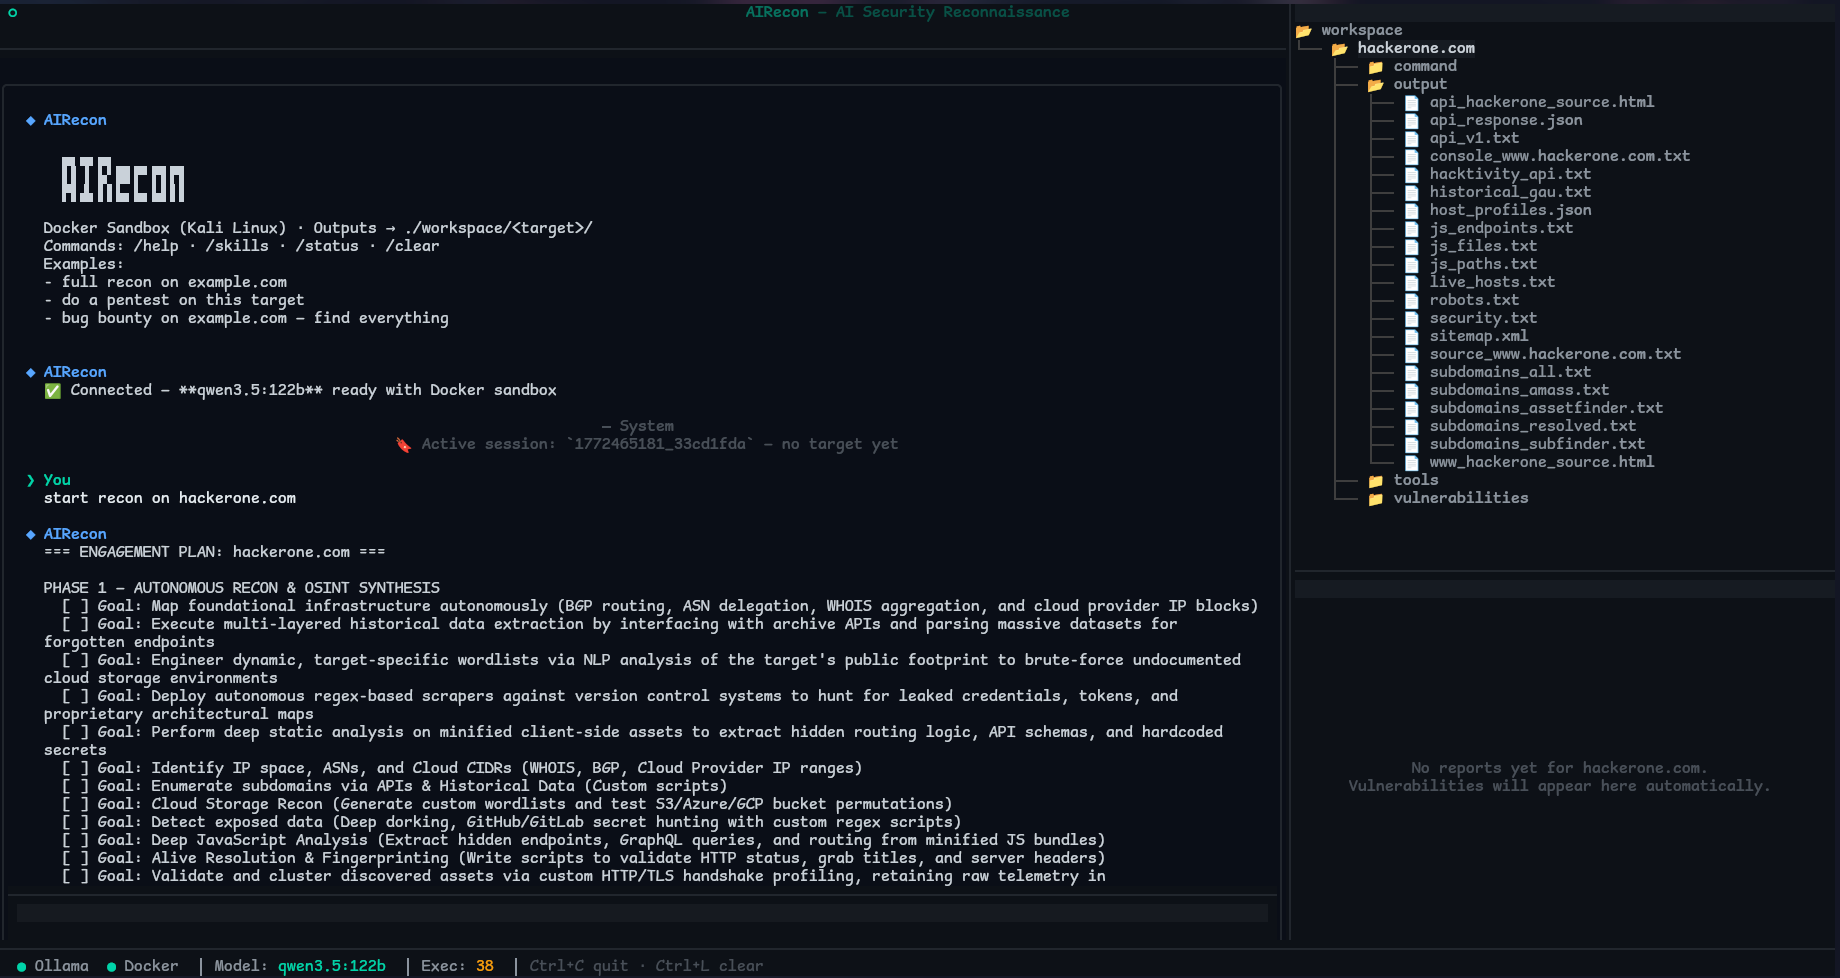 pikpikcu/airecon
AIRecon is an autonomous cybersecurity agent that combines a self-hosted Large Language Model (Ollama) with a Kali Linux Docker sandbox and a Textual…
 joshuaasmith/reproducer-okio-cve-2023-3635
Reproducer for CVE-2023-3635 in Okio 2.9.0, demonstrating how React Native's version catalog pins a vulnerable dependency, affecting Android apps.
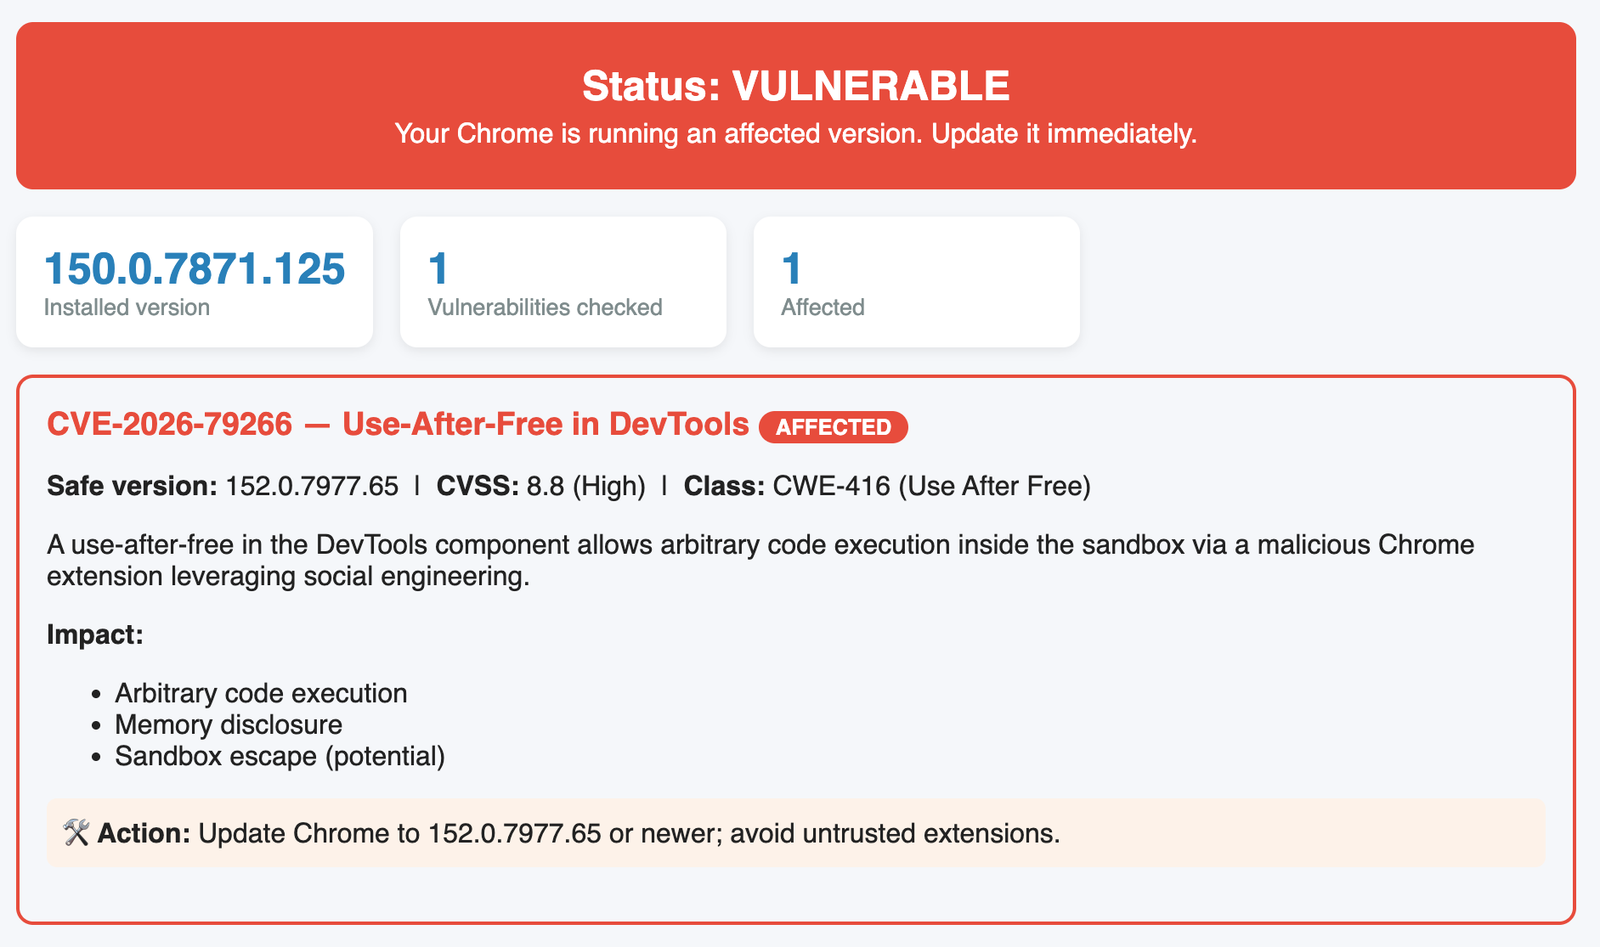 virologi-info/chrome-vuln-scanner
Check for CVE-2026-79266. A use-after-free in the DevTools component allows arbitrary code execution inside the sandbox via a malicious Chrome…
 d4ytox/cve-2021-22204
ExifTool RCE exploit (CVE-2021-22204) - improved version, no exiftool dependency
 eonraider/violent-python3
Source code for the book "Violent Python" by TJ O'Connor. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
 0xmrma/cve-2026-5061
Consul Template validated where a symlink pointed during template evaluation, but its later dependency fetch read the original path. Retargeting the…
 ananay/wp2shell-lab
Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain
 arpitgupta369/log4shell-scanner
Lightweight scanner that detects vulnerable Log4j versions and Log4Shell (CVE-2021-44228) indicators in a filesystem tree.
 cosignet/sdk
Thin TypeScript + zero-dep Python client and recipes to gate high-risk actions behind a payload-bound passkey approval.
 h4r335hr/vsftpd-234-backdoor
Dependency-free interactive Python exploit for the vsftpd 2.3.4 backdoor (CVE-2011-2523).
 renewablehacking/cve-2026-45321-tanstack
Educational lab simulating npm supply chain attacks, CI/CD abuse, and install-time code execution via CVE-2026-45321. Hands-on defensive security…
 samanzamani/copy-fail-checker
Read-only Bash checker for the Copy Fail Linux kernel vulnerability (CVE-2026-31431)
 dannyendortest/ollama
Synthetic demo target for Endor Labs EXPOSURE, tracking CVE-2024-12886 with a deliberately vulnerable dependency and a one-click PR-based fix…
 dannyendortest/node-prompt-here
Deliberately vulnerable Node.js demo target for CVE-2020-7602, used to showcase automated dependency vulnerability detection and one-click PR-based…