
log4shell-audit
 mcpmark-eval-liuhezi/log4shell-audit
Log4Shell (CVE-2021-44228) security review documentation and advisory triage
defensive-toolseducationincident-response+2
mcpmark-eval-liuhezi/log4shell-auditLog4Shell (CVE-2021-44228) security review documentation and advisory triage
 joapath/cve-2021-41773
Prueba de concepto de CVE-2021-41773
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 mohammadalimehri/cve-2021-44790-lab
Dockerized Apache mod_lua lab with a Python PoC reproducing the CVE-2021-44790 multipart boundary buffer overflow for local defensive testing and…
 woaphone/cve-2021-28664-poc
PoC skeleton for CVE-2021-28664, a Mali kbase GPU driver use-after-free, demonstrating a kernel arbitrary physical memory read/write primitive on…
 rubbxalc/cve-2021-32675
Functional DoS exploit for CVE-2021-32675 in Redis, leveraging oversized bulk string headers to trigger memory exhaustion. Includes usage…
 hkenzokimura/cve-2021-1675
Educational proof-of-concept for PrintNightmare (CVE-2021-1675/34527) with simulated non-functional payload, attack flow analysis, MITRE mapping,…
 14free/log4j2-vuln-lab
CVE-2021-44228 (Log4Shell) 漏洞复现靶场 | SpringBoot + Log4j2 2.14.1 | 3 个攻击向量 PoC 验证
 ericpardee/fire-hd-ownership
Owning a tablet Amazon kept shutting down — CVE-2022-38181 write-up, four AI models, and a blog
 shams-ul-mehmood/cve-2021-3156-project
Educational lab environment for CVE-2021-3156 (Baron Samedit) with a Dockerized vulnerable sudo target, exploit scaffold, canary test, root-cause…
 sanr01/cve-2021-41773-exploit-lab
CVE-2021-41773 Exploit Lab
 s-amnajafri/cve-2021-41773-apache-lab
Docker-based lab for reproducing CVE-2021-41773 (Apache HTTP Server 2.4.49) through controlled path traversal and file disclosure using a custom…
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 karitamw/printnightmare-detection-mitigation-lab
Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.
 sanasimran1403-jpg/log4shell
Log4Shell (CVE-2021-44228) research report — technical breakdown, root cause analysis, and end-to-end lab-reproduced exploit chain with evidence…
 zephrfish/cve-2021-28480_honeypoc3
DO NOT RUN THIS.
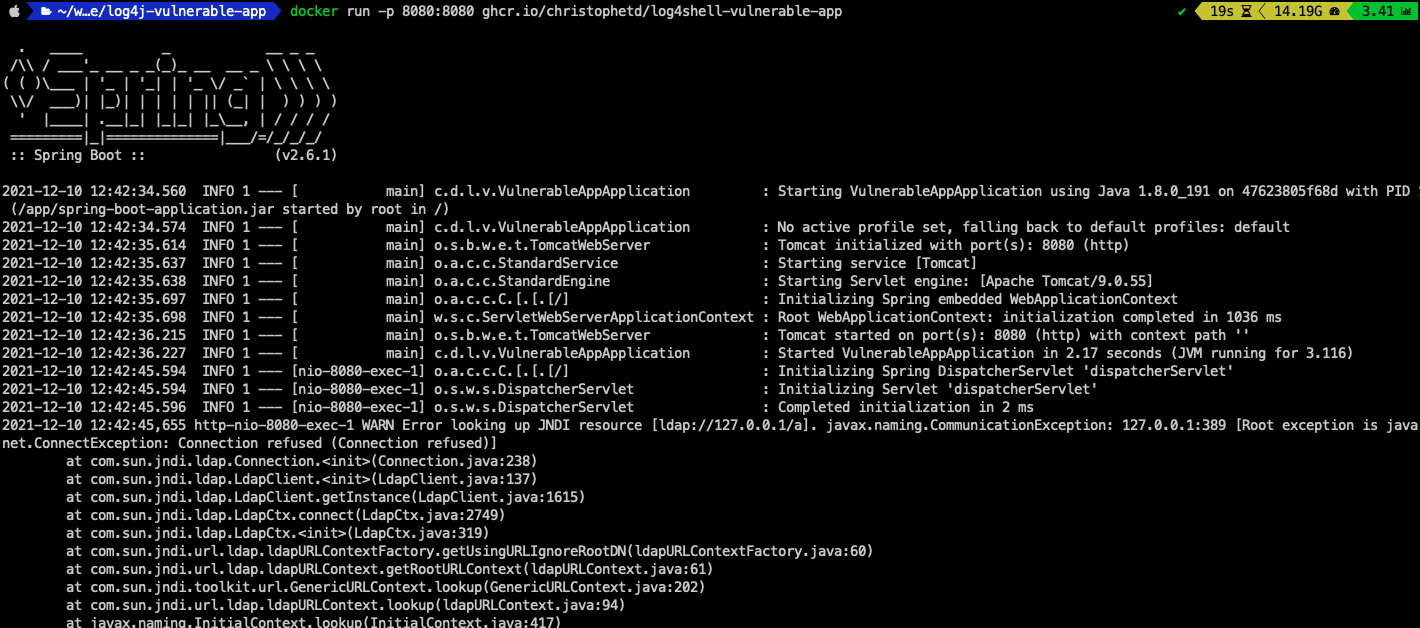 prmawyer/log4shell-vulnerable-app
Spring Boot web application vulnerable to Log4Shell (CVE-2021-44228).
 tr3m0x/cve-2021-41773
PoC and analysis of CVE-2021-41773