
not-going-anywhere
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
api-securitydatabase-securityeducation+3
178
trailofbits/not-going-anywhereIntentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
 trusted-ai/aif360
A comprehensive set of fairness metrics for datasets and machine learning models, explanations for these metrics, and algorithms to mitigate bias in…
 amnestytech/inside-pegasus
A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…
 dungsocool/cve-2025-7384
Exploit PoC and root-cause analysis for a critical unauthenticated PHP object injection in WordPress Database for Contact Form 7, leading to RCE via…
 allanlw/svg-cheatsheet
A cheatsheet for exploiting server-side SVG processors.
 owasp/odtm
OWASP Ontology-driven Threat Modelling framework
 denuvosoftwaresolutions/simba
Efficient Deobfuscation of Linear Mixed Boolean-Arithmetic Expressions
 trailofbits/gosentry
Security-oriented Go toolchain, focused on state-of-the-art fuzzing capabilities.
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 lorenzodegiorgi/setup-cve-2015-8562
Docker-compose to set up a test environment for exploiting CVE-2015-8562
 syntaxbearror/powershell-printnightmare
A collection of scripts to help set the appropriate registry keys for CVE-2021-34527
 grantzile/poc-cve-2024-33883
PoC of CVE-2024-33883, RCE vulnerability of ejs.
 martinclauss/exim-rce-cve-2018-6789
This repository provides a learning environment to understand how an Exim RCE exploit for CVE-2018-6789 works.
 localh0ste/cve-2025-4138
Tarfile module directory traversal vulnerability ( with overflow crossed Directory ) --> Lead to Privilege escalation
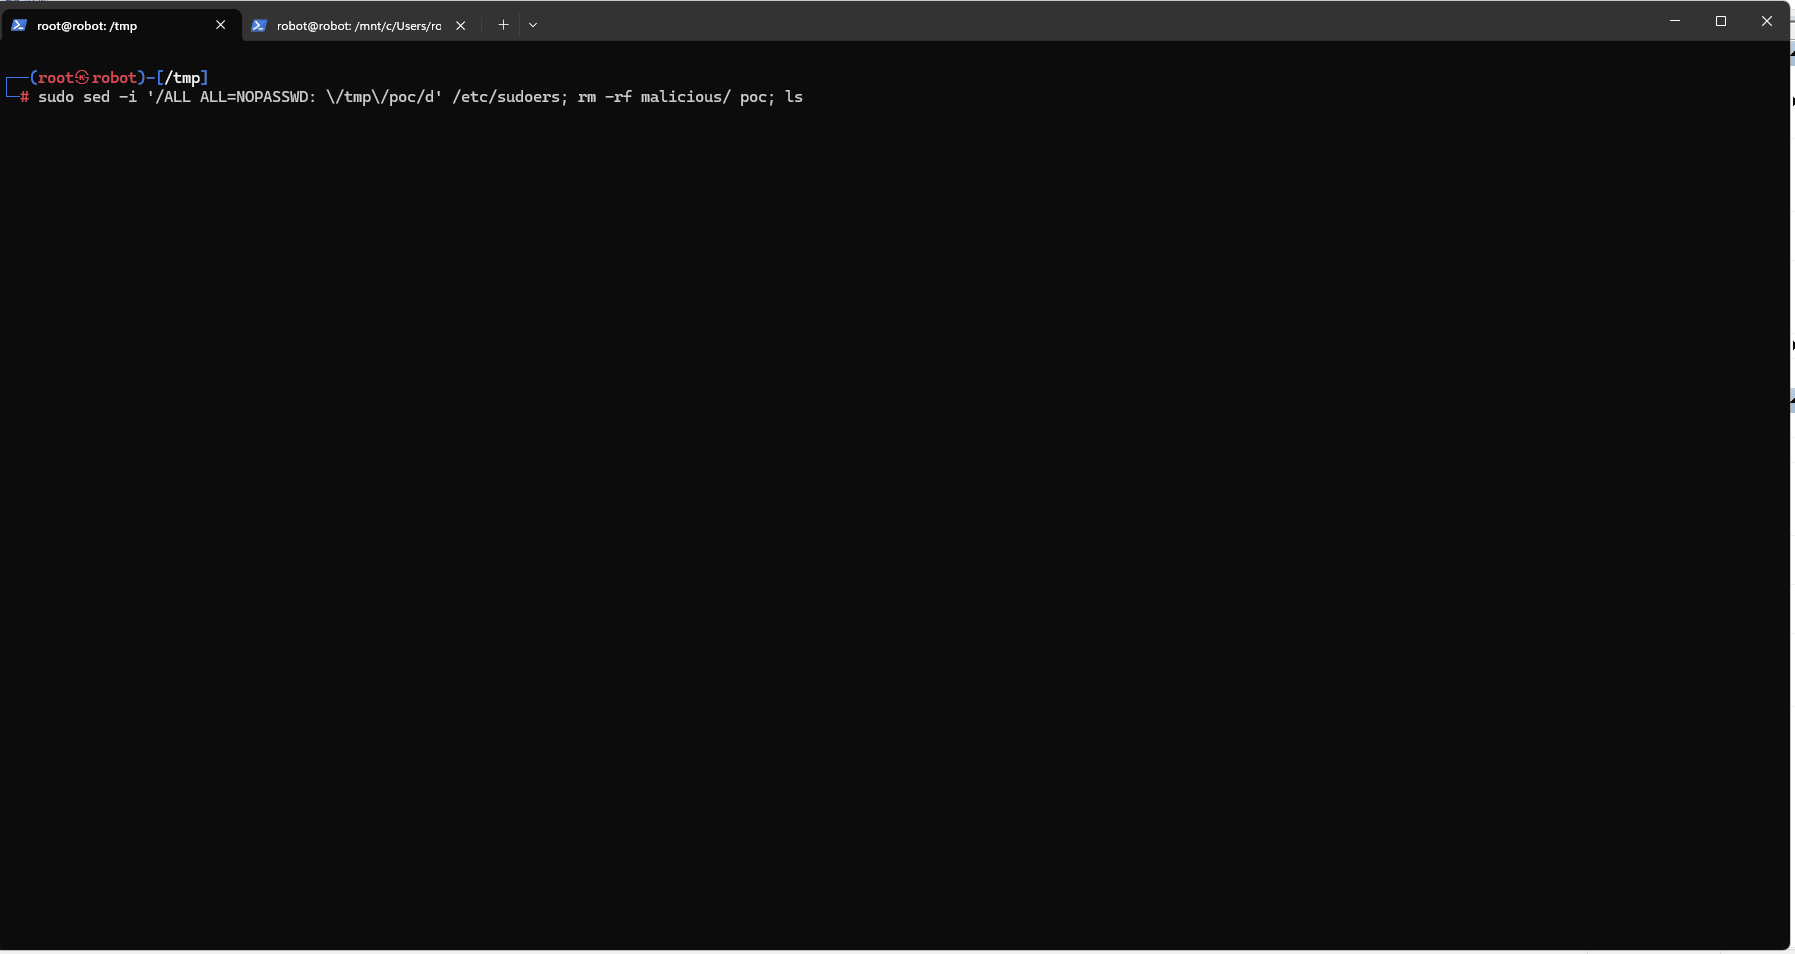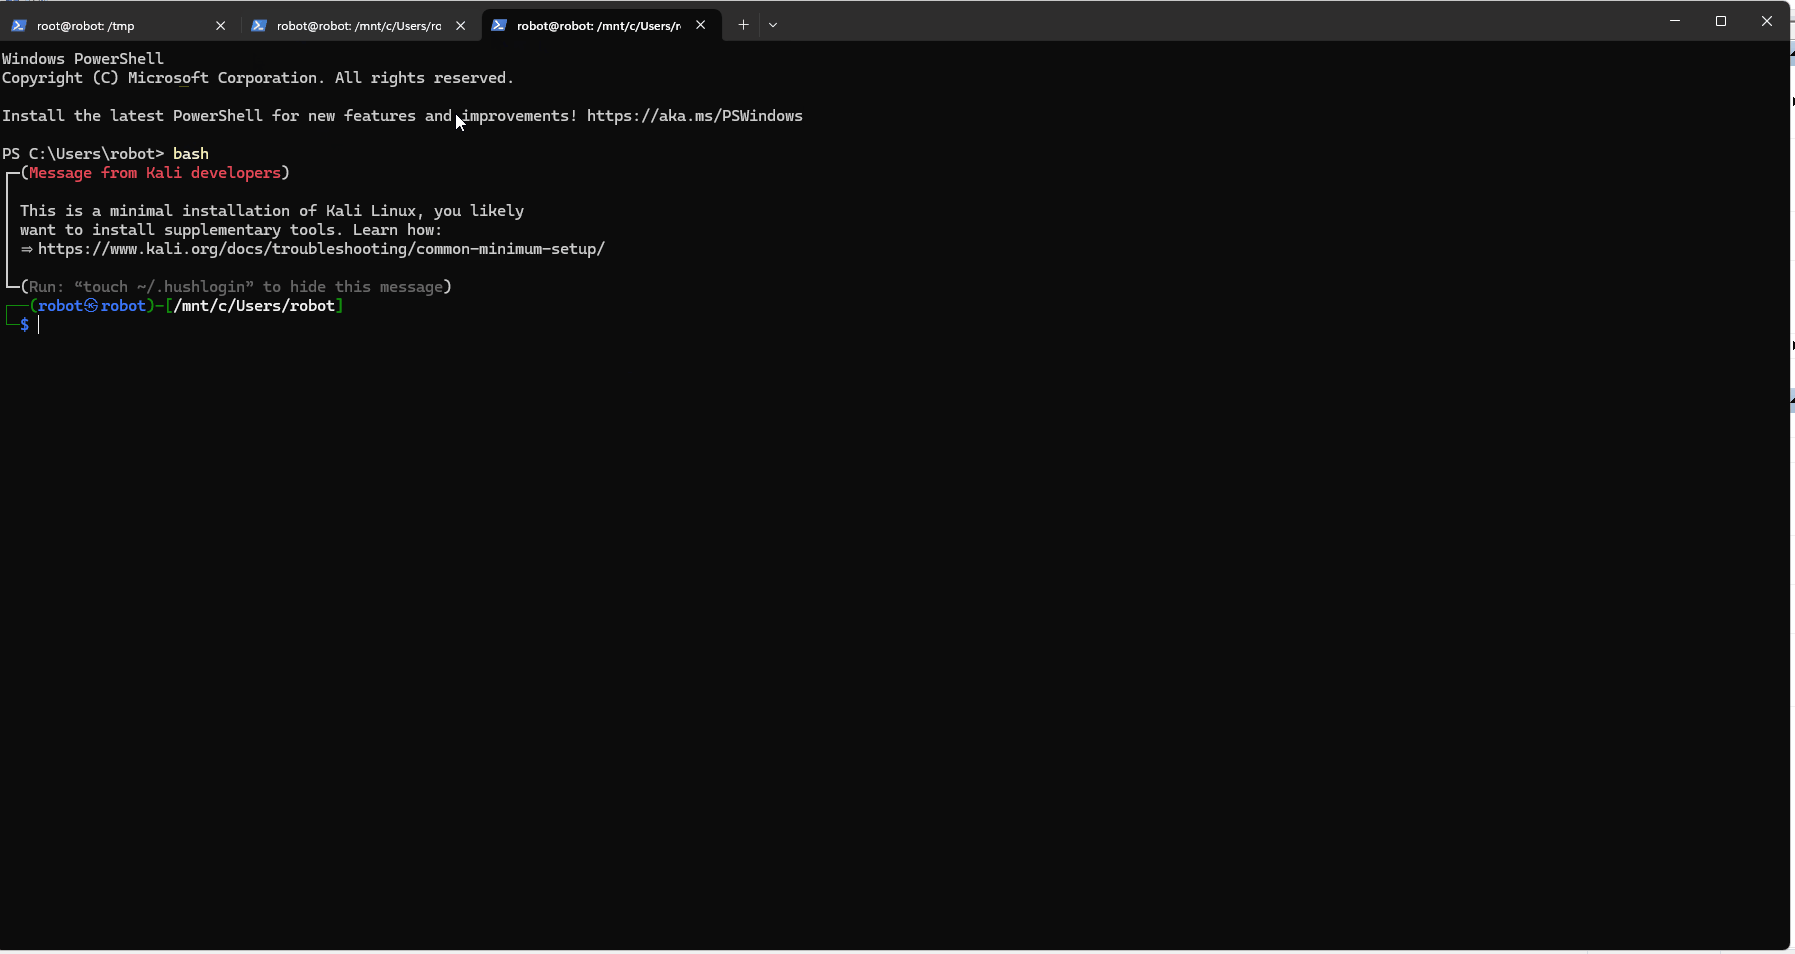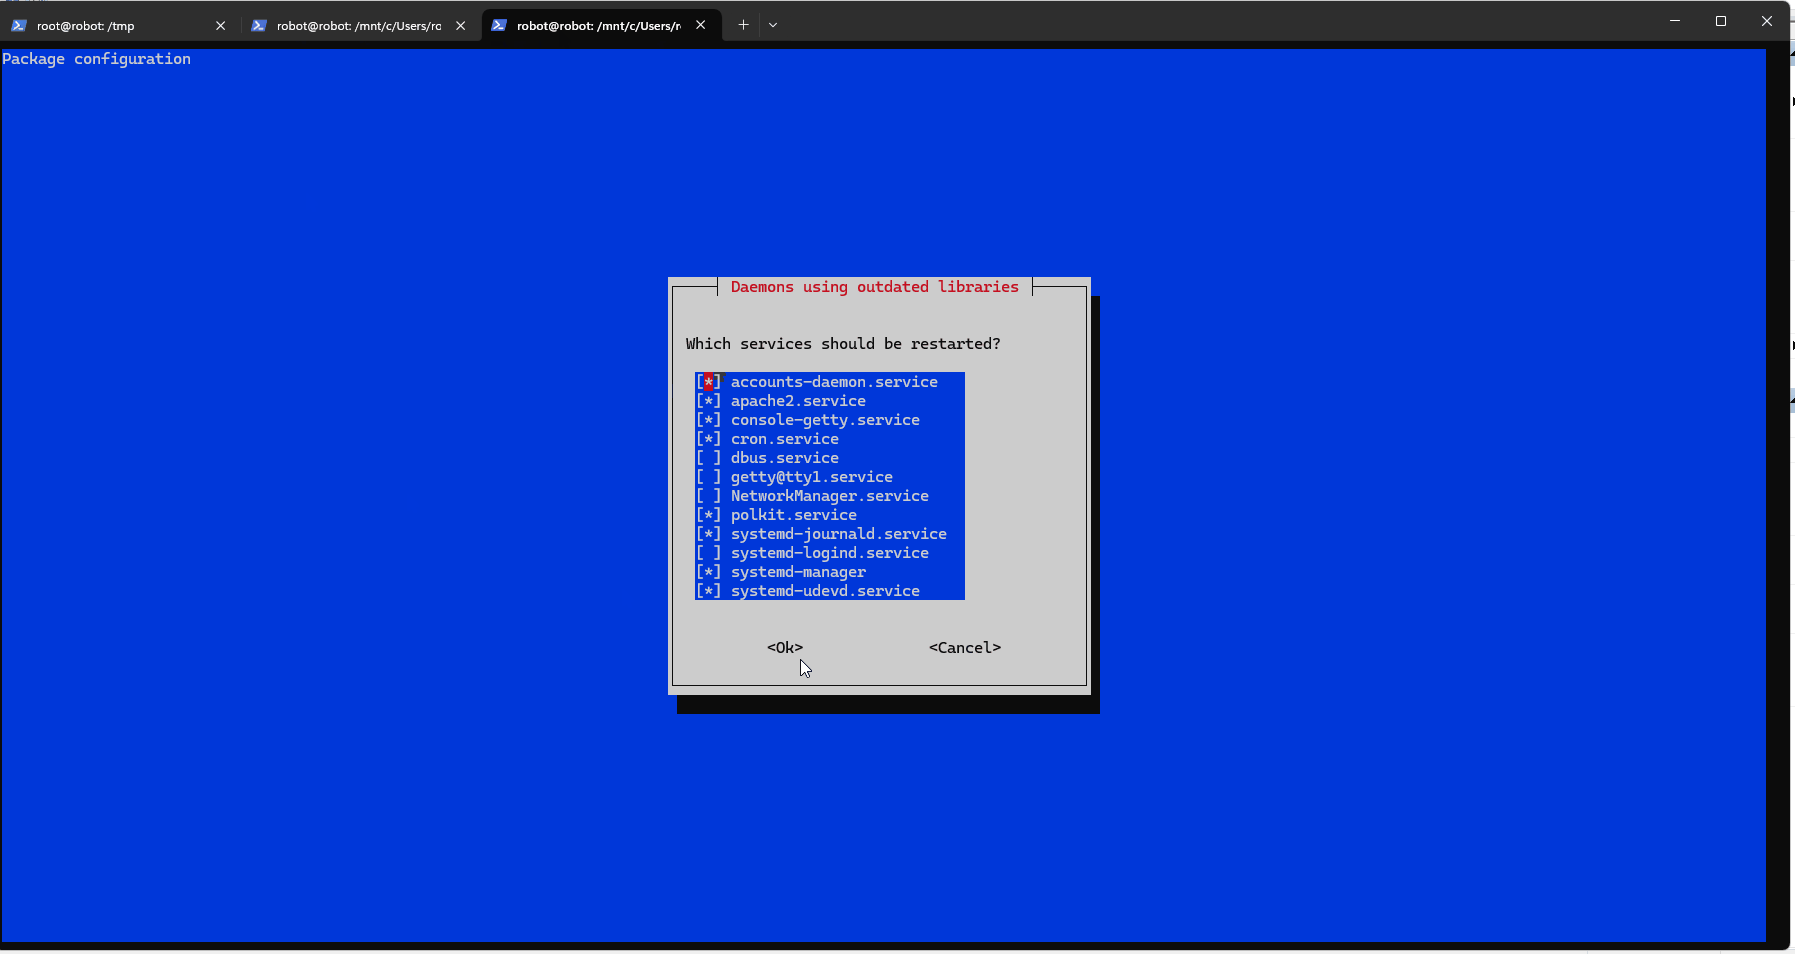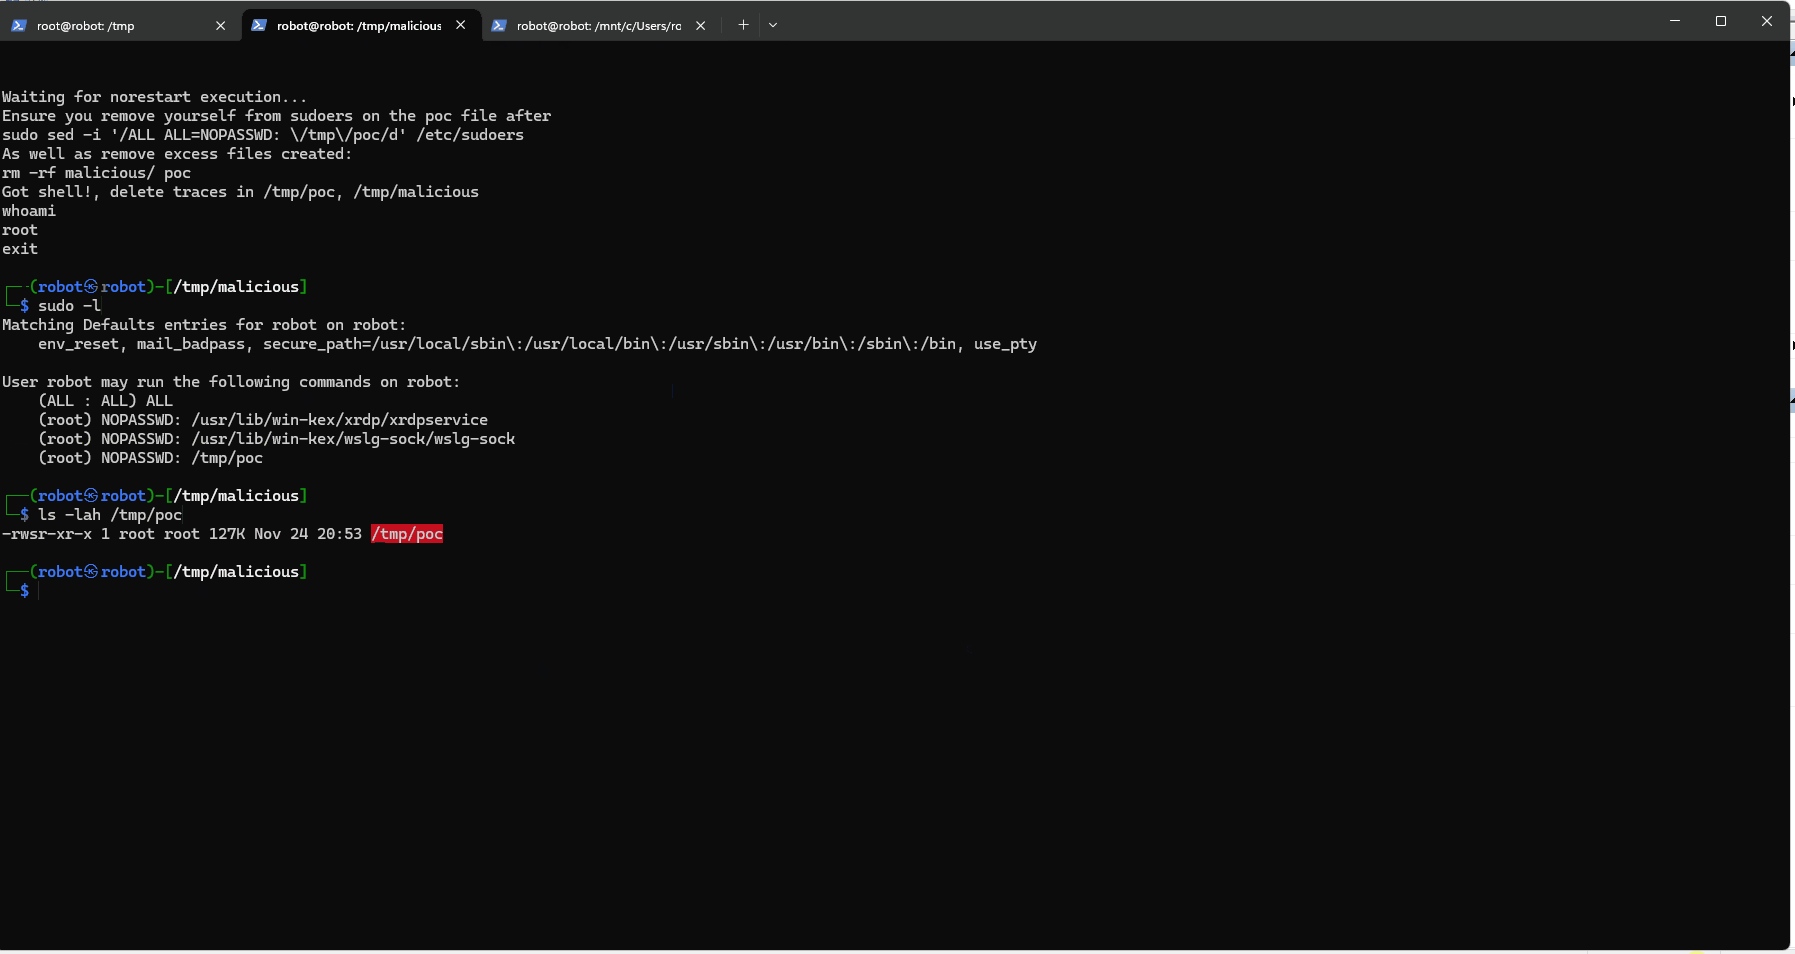 pentestfunctions/cve-2024-48990-poc-testing
Testing POC for use cases
 mistymntncop/cve-2023-4863
Proof-of-concept for CVE-2023-4863, a heap buffer overflow in WebP image decoding. Demonstrates the code_lengths trigger mechanism discovered by…
 rsalmond/cve-2021-34824
reproducing an old istio bug
 lixterclarixe/cve-2020-11019
In FreeRDP less than or equal to 2.0.0, when running with logger set to "WLOG_TRACE", a possible crash of application could occur due to a read of an…