prompt-injection-email-samples

Open .eml test set for evaluating how email security controls and AI mailbox assistants handle indirect prompt injection across disclosure,…

Open .eml test set for evaluating how email security controls and AI mailbox assistants handle indirect prompt injection across disclosure,…

A contextual security auditing system for research artifacts

Weak-RNG stream-sweep research (CVE-2026-71851 class): PRNG schemes x seeds -> BIP39 -> victim set membership

Proof-of-concept exploit for a pre-authentication buffer overflow in GNU InetUtils telnetd (CVE-2026-32746), including a Docker lab environment and…

Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…

A comprehensive set of fairness metrics for datasets and machine learning models, explanations for these metrics, and algorithms to mitigate bias in…

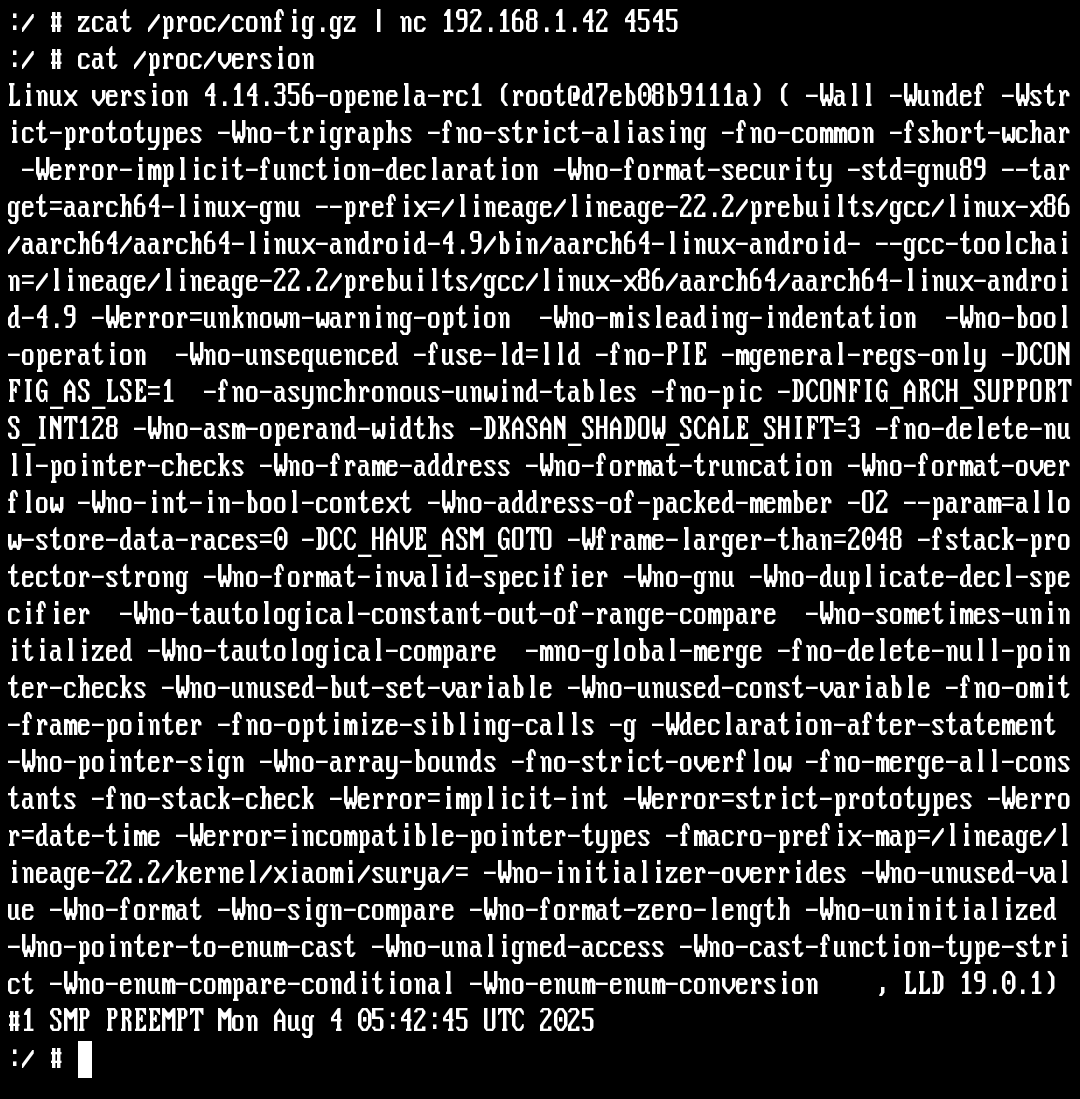
Step-by-step guide to building custom Kali NetHunter kernels for Android: source retrieval, toolchain selection, cross-compilation, and flashing.

How to set up 2 VirtualBox VM to debug kernel driver using windbg

Win32 and Kernel abusing techniques for pentesters

A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…

PoC for CVE-2026-22015: malicious event injects environment variables into serverless functions, overwriting secrets and enabling privilege…

Exploit PoC and root-cause analysis for a critical unauthenticated PHP object injection in WordPress Database for Contact Form 7, leading to RCE via…

SetCookie Analysis in Browser Research Results

A cheatsheet for exploiting server-side SVG processors.


Security Advisory: Unauthenticated NULL Pointer Dereference Crashes the Server (TinyWeb)

CVE-2026-32746 - GNU InetUtils telnetd LINEMODE SLC Buffer Overflow PoC (pre-auth RCE, CVSS 9.8)

OWASP Ontology-driven Threat Modelling framework