
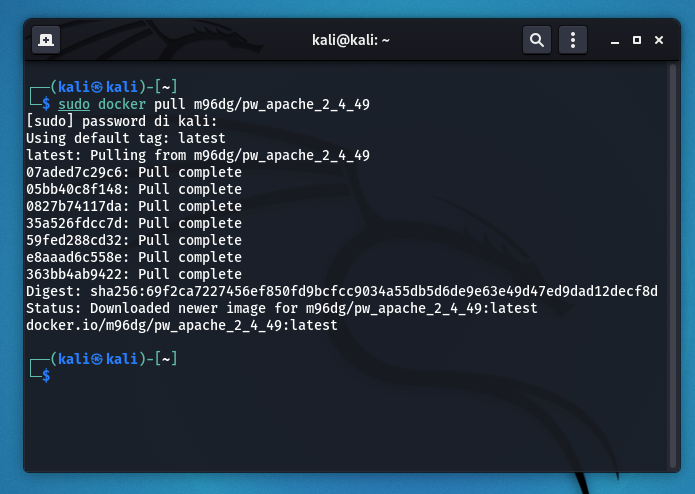
CVE-2021-41773-exercise
 m96dg/cve-2021-41773-exercise
Hands-on lab to exploit Apache 2.4.49 path traversal (CVE-2021-41773) using Docker, Nmap scanning, and curl to retrieve a flag.
educationexploitationlabs-practice+3
m96dg/cve-2021-41773-exerciseHands-on lab to exploit Apache 2.4.49 path traversal (CVE-2021-41773) using Docker, Nmap scanning, and curl to retrieve a flag.
 the-viper-one/pentest-everything
A collection of CTF write-ups, pentesting topics, guides and notes. Notes compiled from multiple sources and my own lab research. Topics also support…

 nxploited/cve-2025-4796
Eventin <= 4.0.34 - Authenticated (Contributor+) Privilege Escalation via User Email Change/Account Takeover
 gellin/teamviewer_permissions_hook_v1
A proof of concept injectable C++ dll, that uses naked inline hooking and direct memory modification to change your TeamViewer permissions.
 mightysai1997/cve-2021-41773
Exploit script for Apache HTTP Server 2.4.49/2.4.50 path traversal and remote code execution (CVE-2021-41773). Includes Docker-based reproduction…
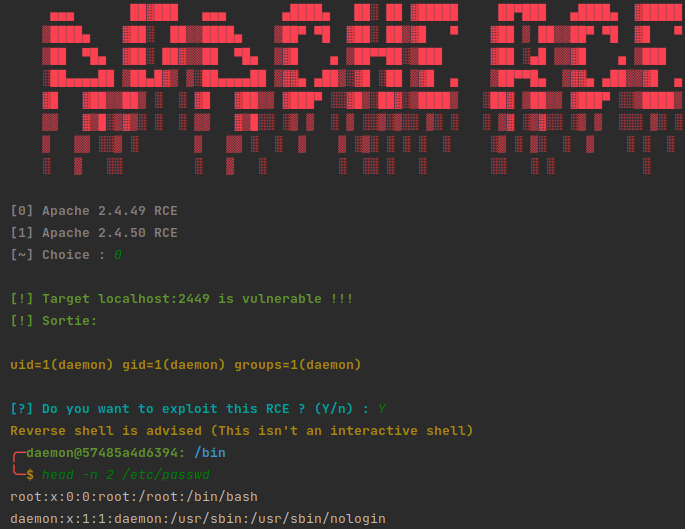 mightysai1997/cve-2021-41773-v-
Proof-of-concept exploit for Apache HTTP Server 2.4.49/2.4.50 path traversal vulnerability (CVE-2021-41773) enabling remote code execution via CGI…
 zakariamaaraki/dirty-cow-cve-2016-5195-
Exploit the dirtycow vulnerability to login as root
 wanmywan/cve-2026-48611-phpbb
Bypass Authentication
 samplev45/cve-2025-22963
Detailed disclosure of CVE-2025-22963, a CSRF vulnerability in Teedy <= v1.11 enabling account takeover via forced user information changes.
 nxploited/cve-2024-6244
pz-frontend-manager < 1.0.6 - CSRF Profile Picture Exploit
 mightysai1997/cve-2021-41773m
Proof-of-concept exploit for Apache HTTP Server 2.4.49 path traversal vulnerability (CVE-2021-41773) with remote code execution and reverse shell…
 mightysai1997/cve-2021-41773-i-
Proof-of-concept exploit for Apache HTTP Server 2.4.49 path traversal (CVE-2021-41773) with Docker-based lab environment and patch diff analysis.
 ludovicpatho/cve-2021-41773
The first vulnerability with the CVE identifier CVE-2021-41773 is a path traversal flaw that exists in Apache HTTP Server 2.4.49.
 wolf1892/confluence-rce-poc
Setting up POC for CVE-2021-26084
 itsecurityco/cve-2021-41773
Proof-of-concept exploit for Apache HTTP Server path traversal vulnerability CVE-2021-41773, with Docker setup and detailed vulnerability analysis.
 elsvital/cve-2022-33891-fix
Educational lab demonstrating CVE-2022-33891 exploitation and patch application for Apache Spark with ACL authentication, including PoC verification…
 armaansidana2003/cve-2025-25618
Proof-of-concept demonstrating incorrect access control in Unifiedtransform v2.0, allowing teachers to modify section details. Includes step-by-step…