
Simple Pentesting
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
educationinformation-gatheringnetwork-mapping+7
sakispat/simple-pentestingAn educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 t-beckett/h-osint
Local-first, keyboard-driven OSINT workbench for the terminal with 28 modules covering username, domain, IP, email, breach, and geolocation lookups…
 v-pun215/tourmaline
Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
 samirchapagain/metasploit-lab-report
Educational penetration testing lab report documenting exploitation of vsftpd 2.3.4 backdoor (CVE-2011-2523) on Metasploitable 2 using Metasploit,…
 ghostwolflab/apt-individual-combat-guide
Educational guide and code repository for understanding APT attack techniques, covering reconnaissance, web and service exploitation, trojans, C2,…
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
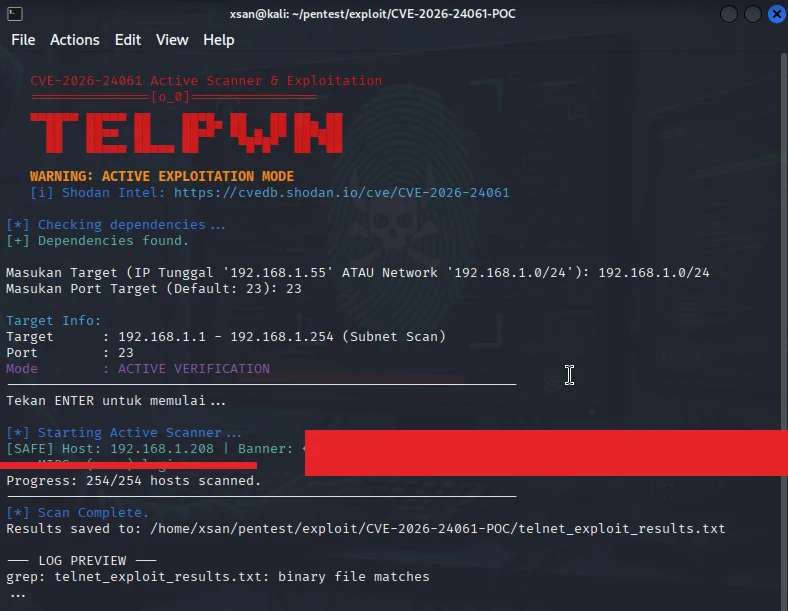 xsanflip/cve-2026-24061-scanner
Bash-based scanner for CVE-2026-24061 that performs subnet reconnaissance, banner grabbing, and active exploitation checks against GNU Inetutils…
 toxy4ny/bl00dym4ry
Educational trojan simulator for cybersecurity training, simulating phishing attacks with social engineering, system reconnaissance, anti-sandbox…
 shawnng078-ops/cve-2024-28000-exploit-lab
Hands-on reproduction of CVE-2024-28000 in LiteSpeed Cache using an isolated WordPress lab. Includes reconnaissance, vulnerable hash recovery,…
 rogerzeferino/cve-2019-17558-apache-solr-rce
CTF write-up documenting CVE-2019-17558 exploitation in Apache Solr, covering reconnaissance, Metasploit limitations, manual Velocity template…
 george0papasotiriou/cve-2026-11106-dns-zone-transfer-axfr-information-disclosure
Proof-of-concept for CVE-2026-11106 exploiting unrestricted DNS AXFR zone transfers to enumerate domain records, expose internal hosts, and leak…
 irsaattiquecyber/systemvulnerabilitychecklist_project4_decodelabs
System Vulnerability Checklist & Network Security Hardening project featuring reconnaissance, vsFTPd backdoor analysis (CVE-2011-2523), and active…
 jas502n/security_article
scrapy website Article and link ...
 d0n601/pwncity
Insecure TeamCity CI environment for hands-on penetration testing training: reconnaissance, credential theft, privilege escalation, and lateral…
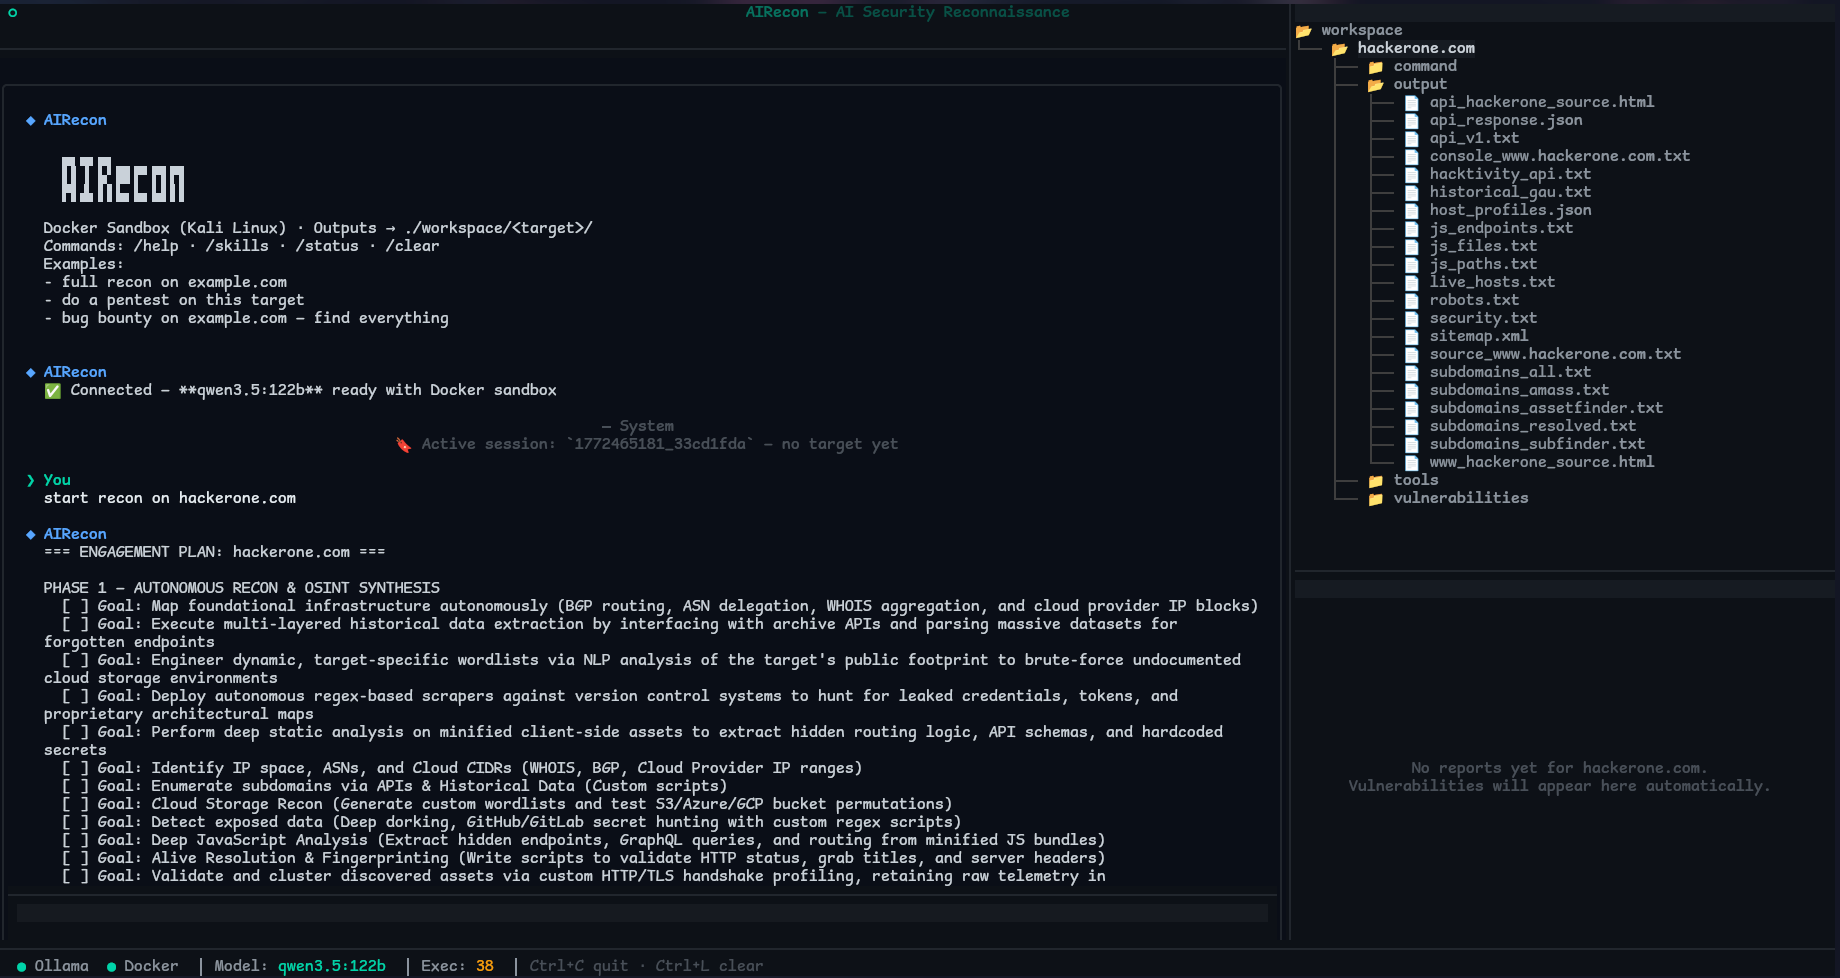 pikpikcu/airecon
AIRecon is an autonomous cybersecurity agent that combines a self-hosted Large Language Model (Ollama) with a Kali Linux Docker sandbox and a Textual…
 notrustedx/job-manager-disclosure
CVE-2015-6668, relacionada con el plugin WP Job Manager para WordPress (versiones ≤ 0.7.25).