

FIASSE
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
code-analysiscurated-resourcesdevsecops+7
145 days ago
owasp/fiasseA Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 first-roman/sprig-mvc-demo-patch
This demo application partially covers the vulnerability CVE-2024-38828
 luisdalmolin/recon-test-livewire
Test target: fresh Laravel 12 app with Livewire pinned to vulnerable 3.6.3 (CVE-2025-54068) for recon scanning
 seanpesce/cve-2024-22243
Example exploitable scenarios for CVE-2024-22243 affecting the Spring framework (open redirect & SSRF).
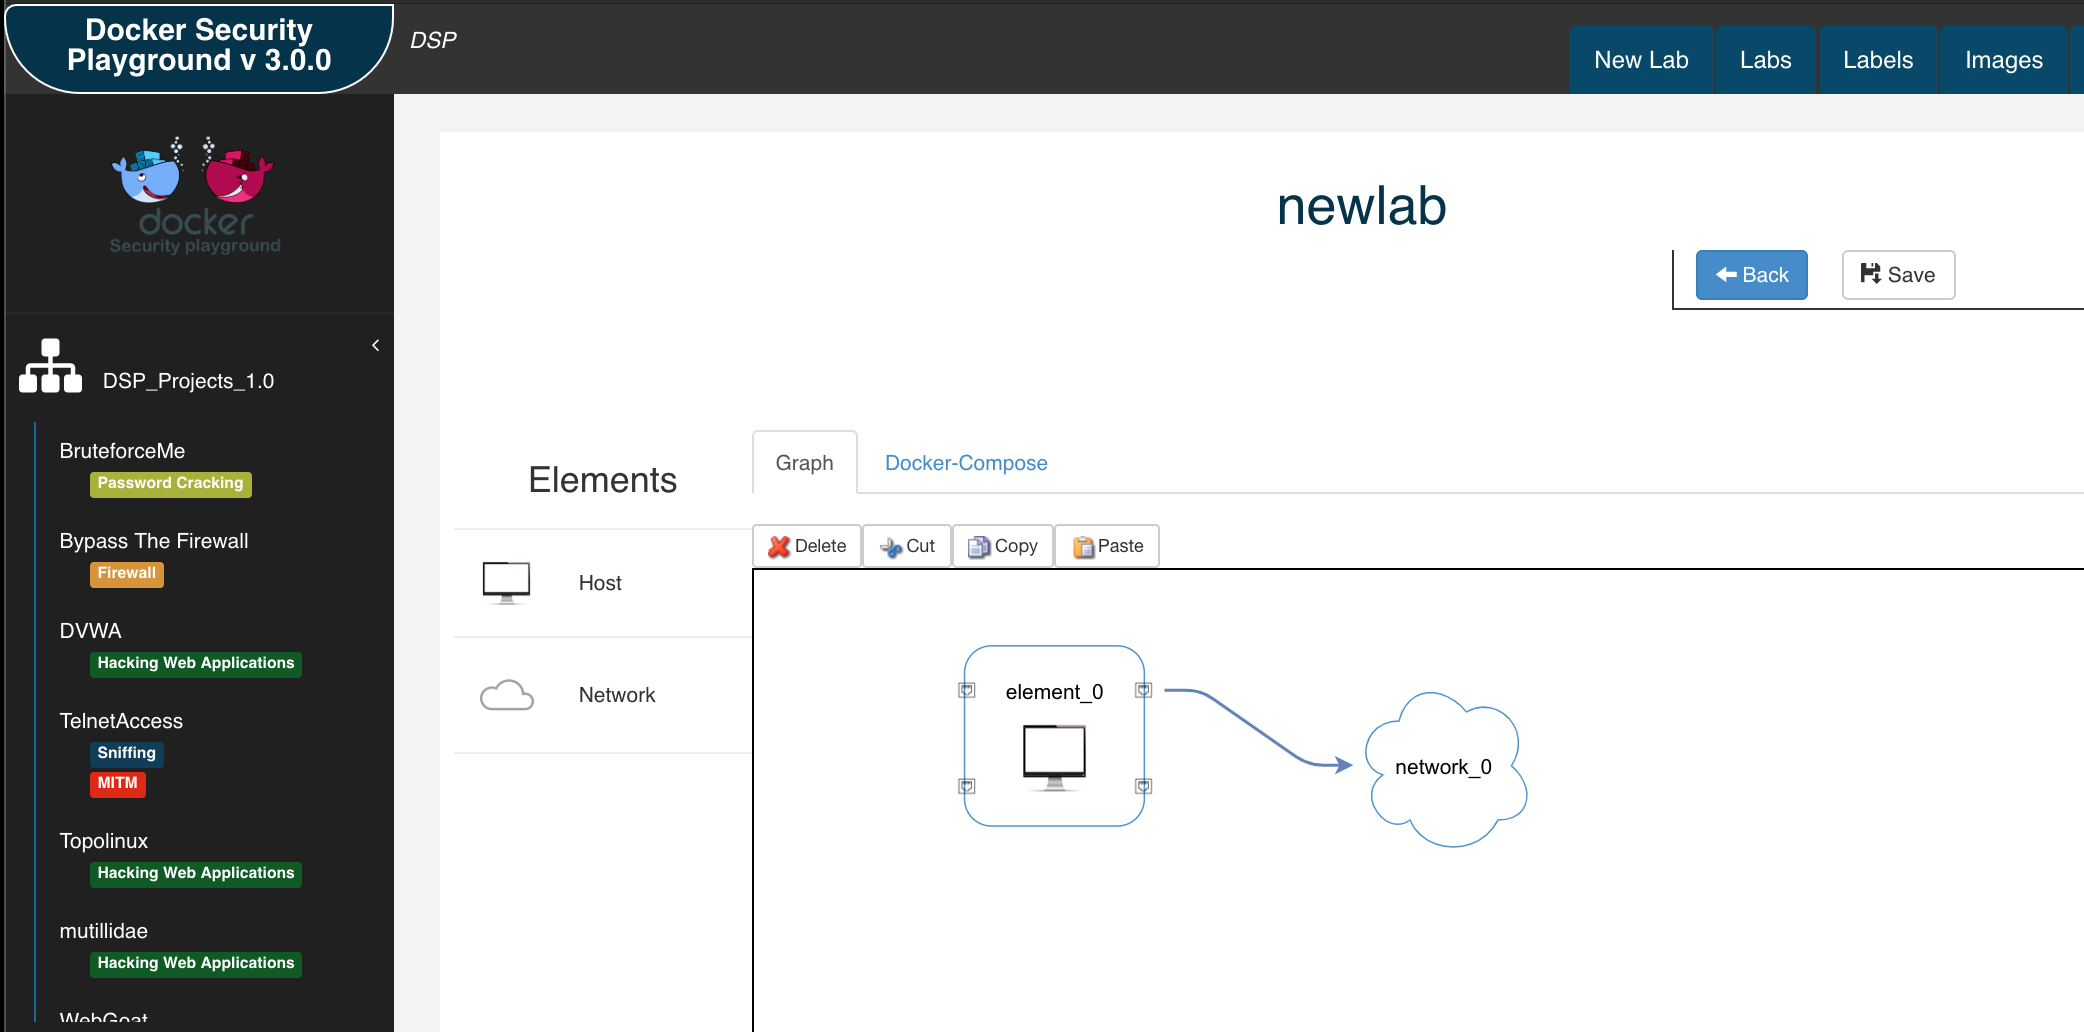 dockersecurityplayground/dsp
A Microservices-based framework for the study of Network Security and Penetration Test techniques
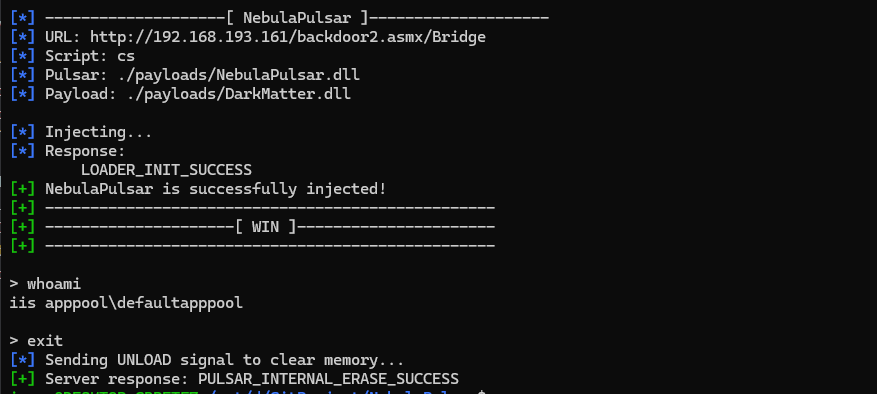 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…