
CVE-2026-39987
 alreadyclosed/cve-2026-39987
CVE-2026-39987 for marimo 0.20.4 PoC
ctfeducationexploitation+2
alreadyclosed/cve-2026-39987CVE-2026-39987 for marimo 0.20.4 PoC
 chpratik/nginx_2026_cve_bundle_cti_report
Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533
 oscerd/camel-pqc-tls
Post-Quantum Cryptography (PQC) TLS 1.3 examples with Apache Camel using X25519MLKEM768 hybrid key exchange on JDK 21 (BouncyCastle) and JDK 27…
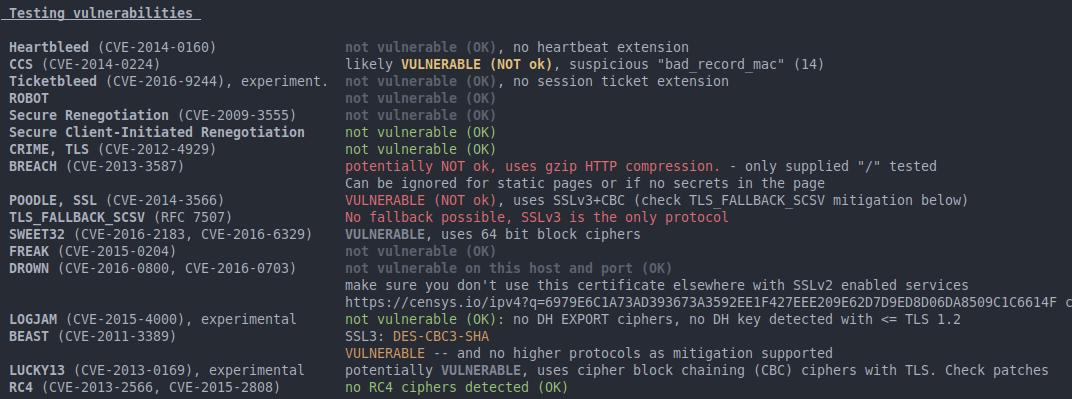 mpgn/poodle-poc
:poodle: Poodle (Padding Oracle On Downgraded Legacy Encryption) attack CVE-2014-3566 :poodle:
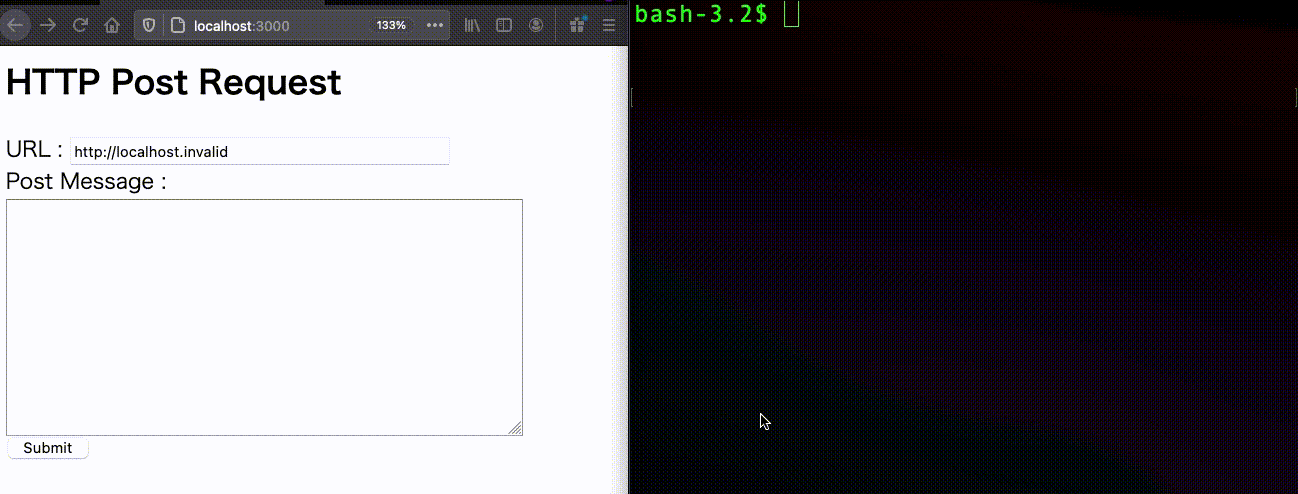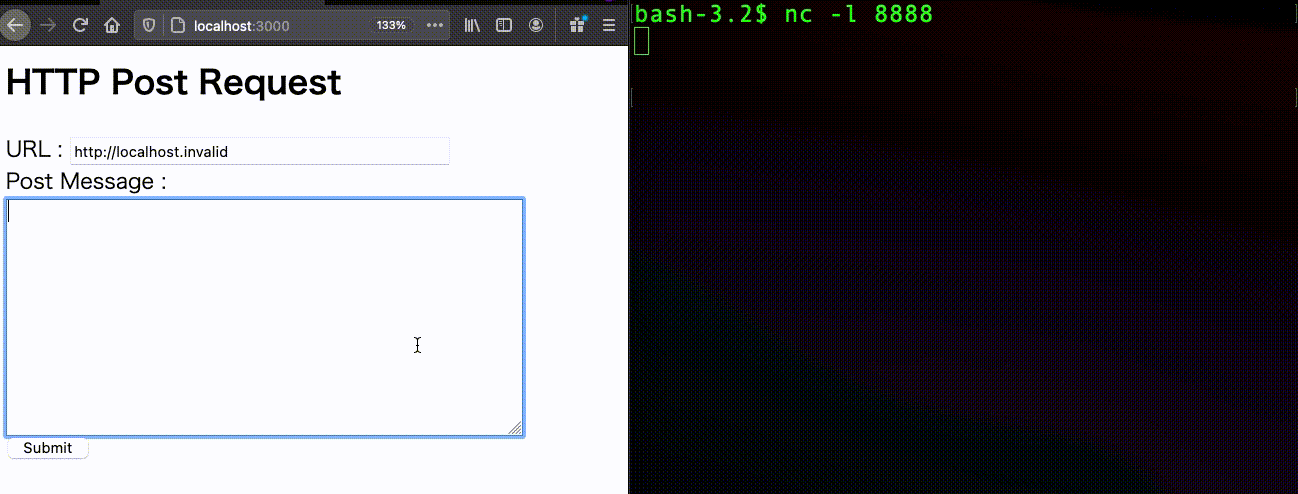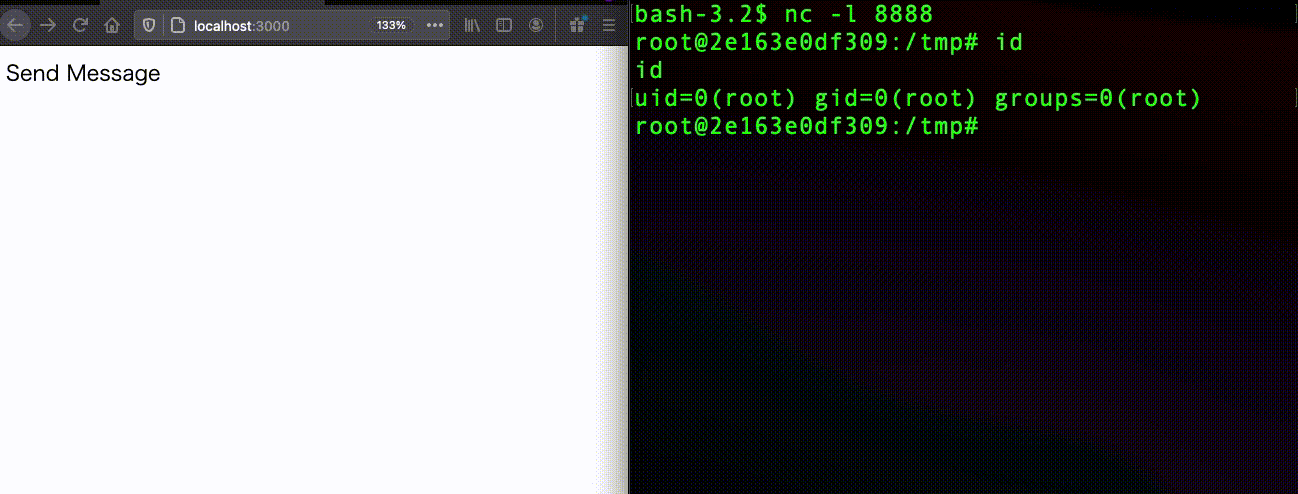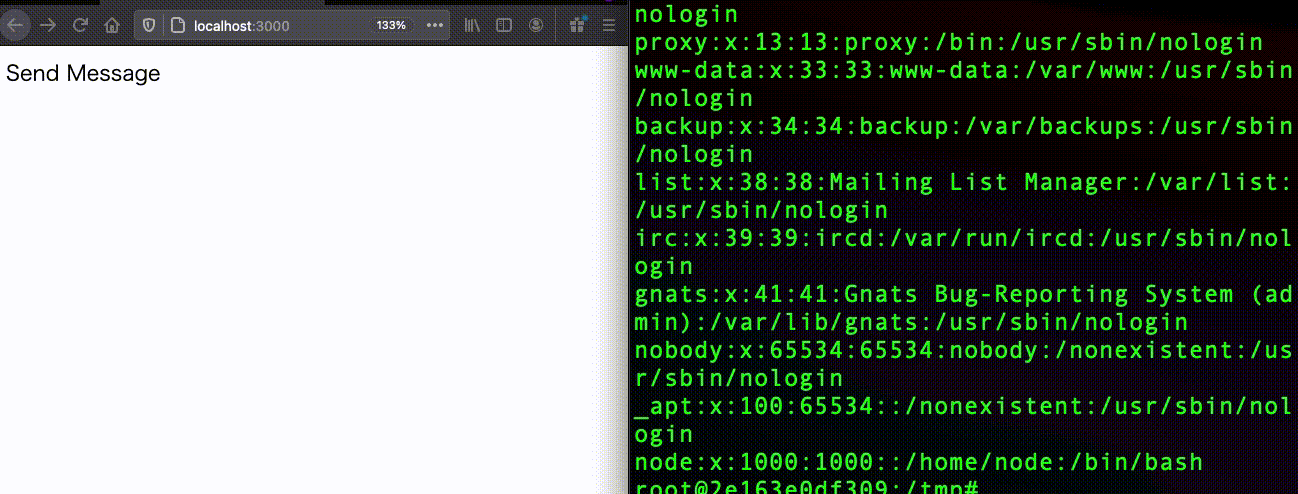 s-index/cve-2020-28502
CVE-2020-28502 node-XMLHttpRequest RCE
 landonf/testability-cve-2014-1266
Demonstrating that SSLVerifySignedServerKeyExchange() is trivially testable.
 magercode/list-cve-2025-2026
Daftar CVE 2025-2026 terupdate
 seed1337/cve-2024-24919-poc
Proof-of-concept exploit for CVE-2024-24919, an unauthenticated arbitrary file read vulnerability in Check Point SSL VPN appliances. Includes Nuclei…
 d1se0/cve-2024-10924-bypass-mfa-wordpress-lab
Lab environment and exploit script for CVE-2024-10924, demonstrating MFA bypass in WordPress via the Really Simple SSL plugin's skip_onboarding…
 sariamubeen/cve-2024-10924
Python exploit for CVE-2024-10924 that bypasses Two-Factor Authentication in the Really Simple SSL WordPress plugin, enabling unauthorized…
 node011/cve-2023-27997-poc
Fortigate SSL VPN buffer overflow exploit
 mikesplain/cve-2014-3566-poodle-cookbook
Chef cookbook that detects and fails runs on servers vulnerable to CVE-2014-3566 (POODLE) by scanning specified SSL ports, serving as both a security…
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
 h8su/wordpress-cve-2024-10924-exploit
A Proof-of-Concept (PoC) exploit for CVE-2024-10924, a vulnerability in the Really Simple SSL WordPress plugin that allows bypassing two-factor…
 gremwell/cve-2020-0601_poc
Proof-of-concept exploit for CVE-2020-0601 (Windows CryptoAPI spoofing) that generates rogue CA certificates to intercept HTTPS traffic, with…
 anilpatel199n/cve-2024-40898
This Python script checks for the presence of CVE-2024-40898, a critical vulnerability in Apache HTTP Server that may allow SSL/TLS certificate…
 ademto/wordpress-cve-2024-10924-pentest
Penetration testing report and exploit for CVE-2024-10924, a 2FA bypass in Really Simple SSL, including reconnaissance, exploitation, and remediation…