
Mastik
 0xade1a1de/mastik
C toolkit implementing micro-architectural side-channel attacks on Intel x86-64, including Prime+Probe, Flush+Reload, Flush+Flush, CacheBleed and…
binary-analysiscryptographyeducation+3
124
0xade1a1de/mastikC toolkit implementing micro-architectural side-channel attacks on Intel x86-64, including Prime+Probe, Flush+Reload, Flush+Flush, CacheBleed and…
 mrhackercharlie/netspecter
Real-time system monitoring tool for detecting process activity and network exposure!
 crypto-unict/ghostfacempc
Reference implementation of privacy-preserving face recognition using replicated secret sharing in MP-SPDZ, with quantized GhostFaceNet inference,…
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 aramosf/cve-2026-61500
Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.
 kongqbin/cve-2016-5195
Educational implementation of the Dirty COW (CVE-2016-5195) privilege escalation exploit, including race condition payload and SUID-based root shell…
 ciphercloak/cve-2026-41651
Provides technical details and mitigation guidance for the Pack2TheRoot privilege escalation vulnerability (CVE-2026-41651) affecting Linux systems.
 haomin-yu/cve-2024-13176-timing-analysis
Instrumented analysis and reproducibility materials for ECDSA timing leakage in OpenSSL CVE-2024-13176
 lucacav/steg-tools
A list of tools and material on steganography and information hiding
 ph4l4nx/ctf-s-tools
Repository to index useful tools for CTF's
 priyanshu-rawa/cybersecurity-handbook
Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.
 jigerjain/interview_tips
Summary of Cyber Security interview questions I have been through, hope this helps
 kkirsche/slae
SecurityTube Linux Assembly Expert x86 Exam
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
 nekr0ff/needrestart-sudo-escalate-cve-2024-4890
PoC exploit for CVE-2024-4890: Sudo privilege escalation via neecdrestart (>=3.8). Ethical lab-only. Scripts in Python and C.
 shoucheng3/jlangch__venice_cve-2022-36007_1-10-16
Sandboxed Lisp dialect for the JVM with immutable data structures, macros, and over 900 core functions. Ideal for safe scripting, automation, and…
 thomasarmel/rollback_car_attack_proverif
ProVerif proof of concept of the Rollback attack on car keyfob (CVE-2022-37418, CVE-2022-36945 and CVE-2022-37305)
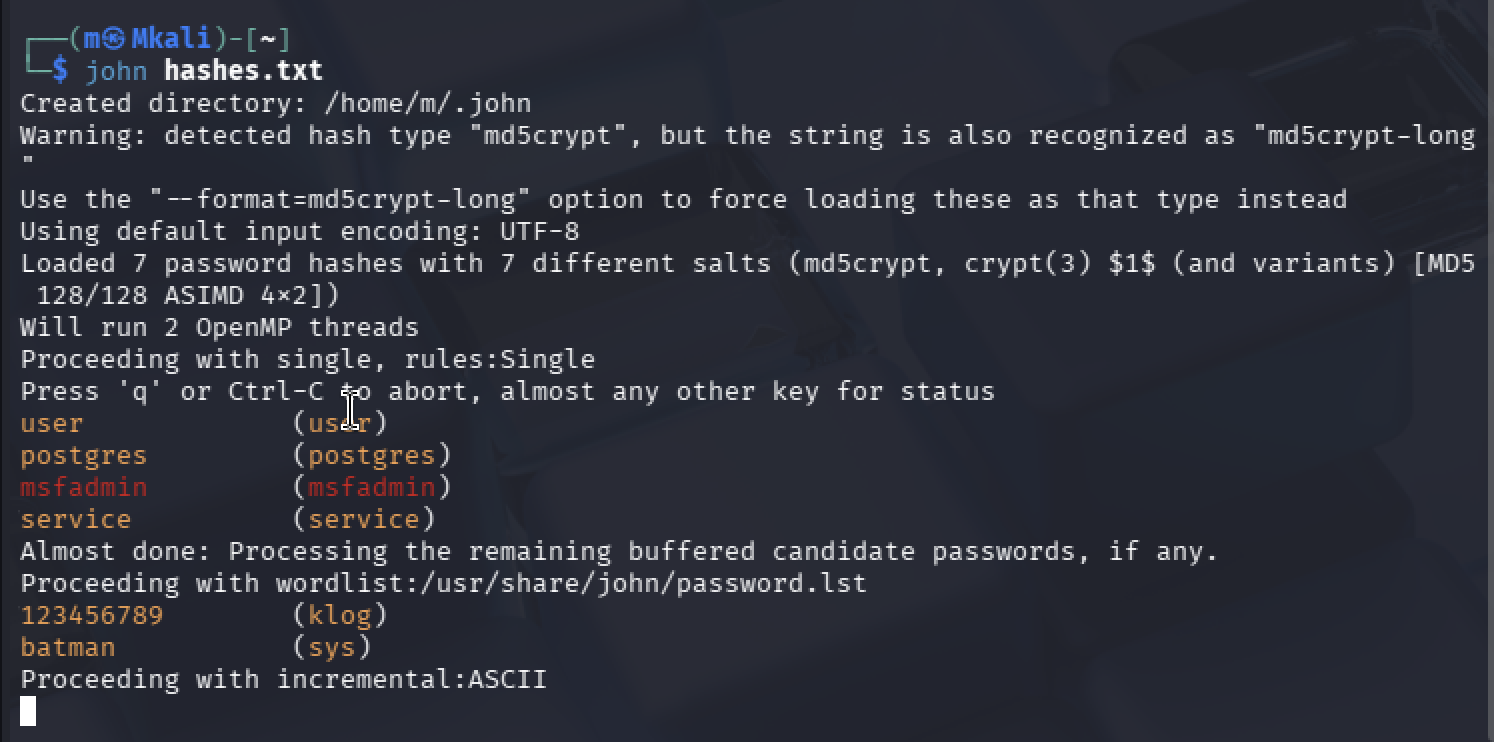 mirza-22144/vulnerability-assessment-exploitation-lab
Full-lifecycle penetration test of a legacy Linux environment (Metasploitable 2) emulated on Apple Silicon. Demonstrating network reconnaissance, RCE…