

SimpleVisor
 ionescu007/simplevisor
Minimal Intel VT-x hypervisor for Windows and UEFI that virtualizes a live host for introspection, supporting dynamic hyperjacking, unhyperjacking,…
binary-analysiseducationhardware-security+4
2.0k
ionescu007/simplevisorMinimal Intel VT-x hypervisor for Windows and UEFI that virtualizes a live host for introspection, supporting dynamic hyperjacking, unhyperjacking,…
 george0papasotiriou/cve-2026-23008-solidity-assembly-return-data-size-confusion
Educational PoC for Solidity assembly return-data size confusion; includes vulnerable contract, exploit simulation, and mitigation guidance for…
 0xdea/shellcode
A collection of my shellcode samples.
 quyt0/cve-2019-18935-exploit-study
In-depth study of CVE-2019-18935 affecting Telerik UI for ASP.NET AJAX. Covers .NET deserialization vulnerability, RadAsyncUpload handler, gadget…
 gallopsled/pwntools
CTF framework and exploit development library
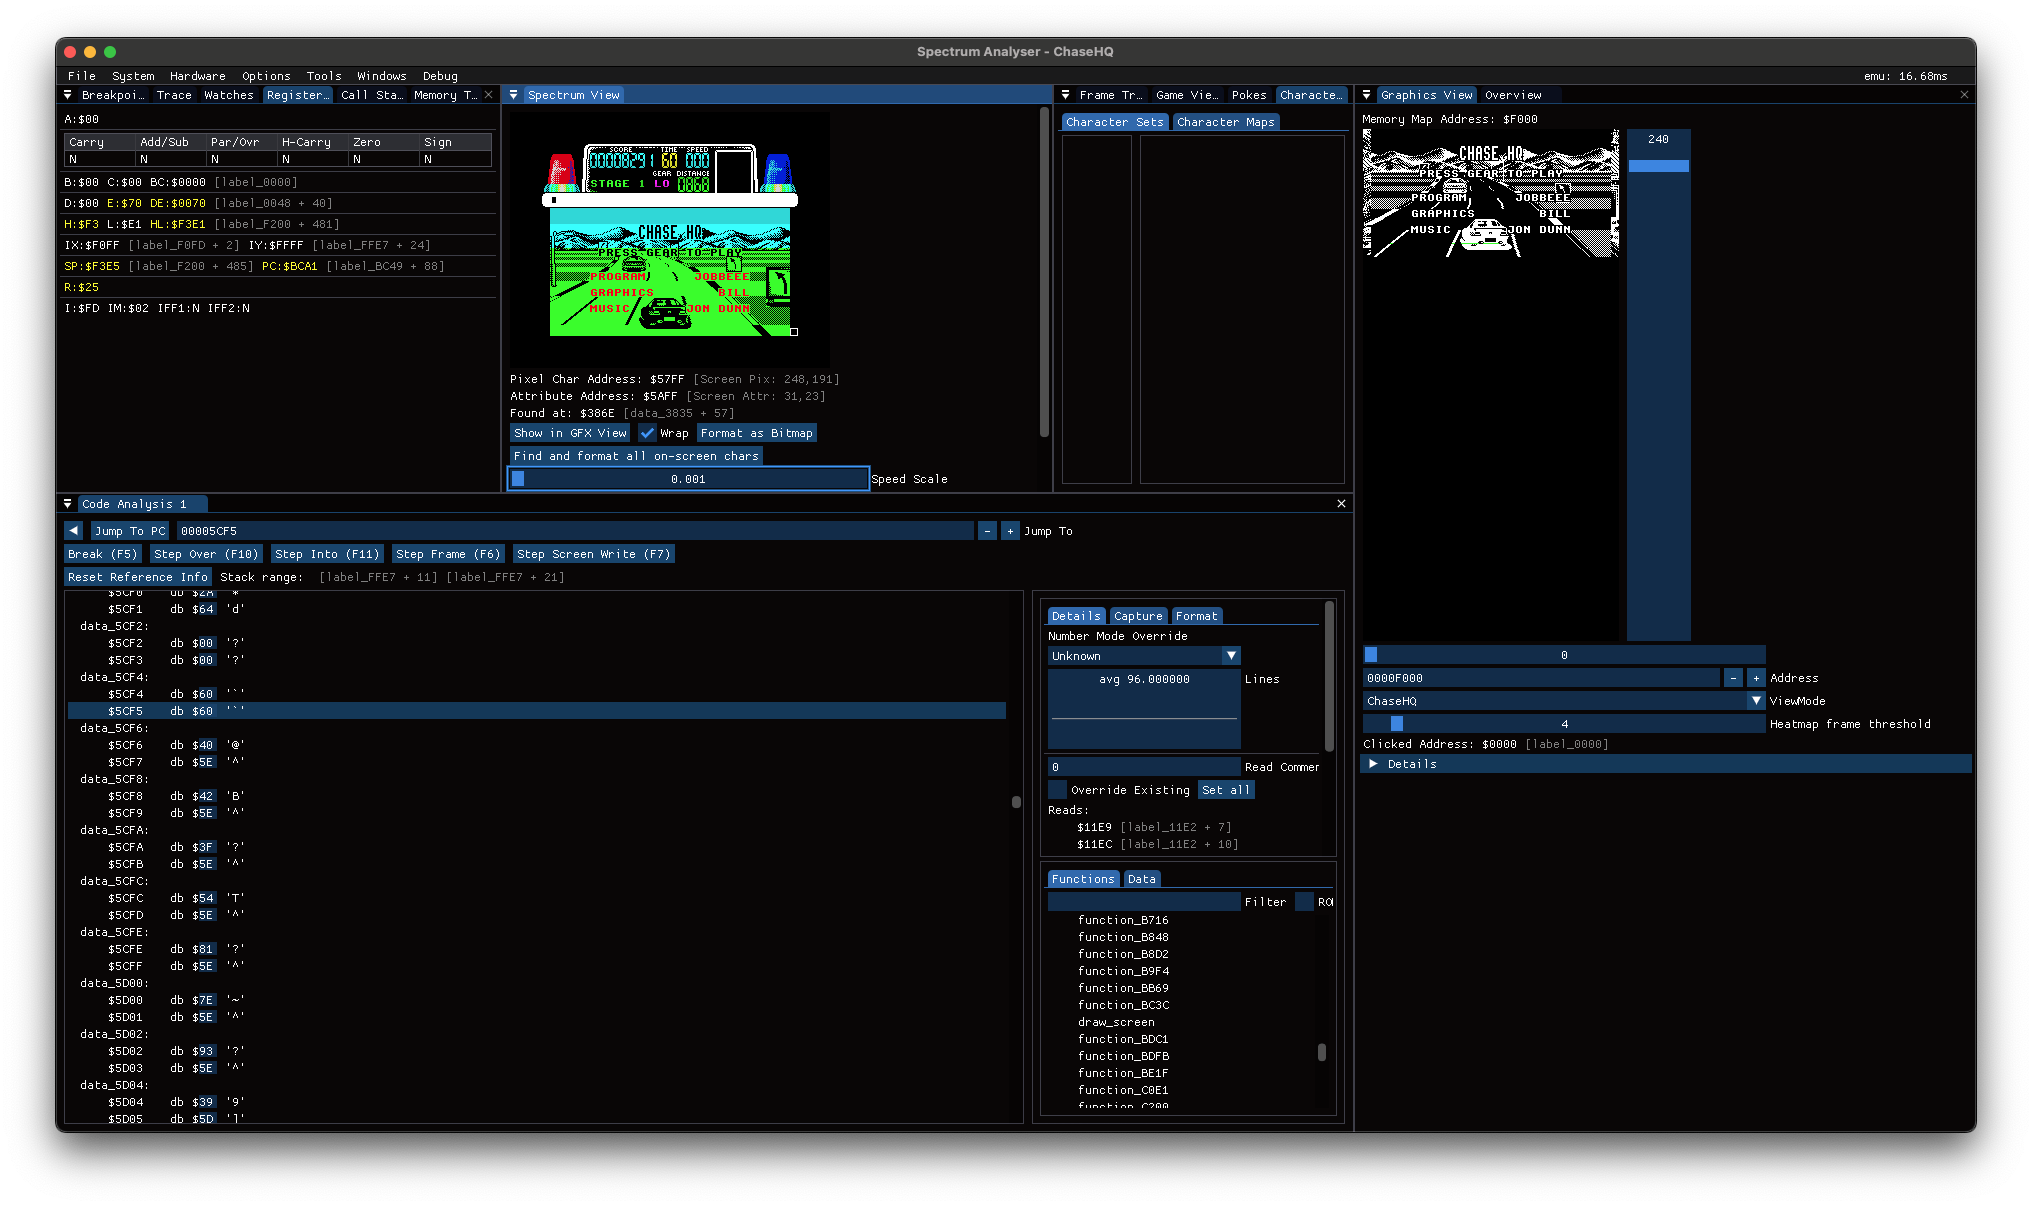 dpt/chasehq
Chase H.Q. for ZX Spectrum — reverse-engineered and reconstructed in portable C
 gbonacini/cve-2026-31431
Standalone C++/x86-64 assembly implementation of CVE-2026-31431 (Copyfail) for local privilege escalation. Compiles to a dependency-free binary that…
 qduarte-42/rainfall
Introduction to the exploitation of ELF binaries.
 harbor-framework/terminal-bench-2
Benchmark for evaluating AI agents on real-world tasks including vulnerability resolution, code debugging, and protein assembly in containerized…
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
 pithase/asm-copyfail
CVE-2026-31431 (Copy Fail) — Análisis y desarrollo en Ensamblador x86-64 | Analysis and development in x86-64 Assembly
 jimmyader/cheatsheethost
A locally hosted page for cheat sheets. Currently being used for reverse engineering and hosted in labs so I can limit or forgo (lock down firewall)…
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
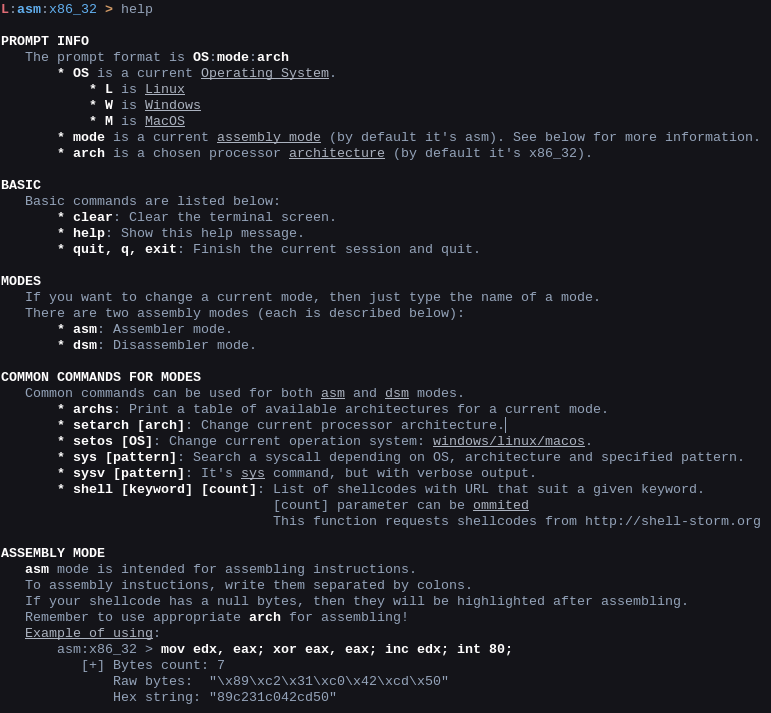 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
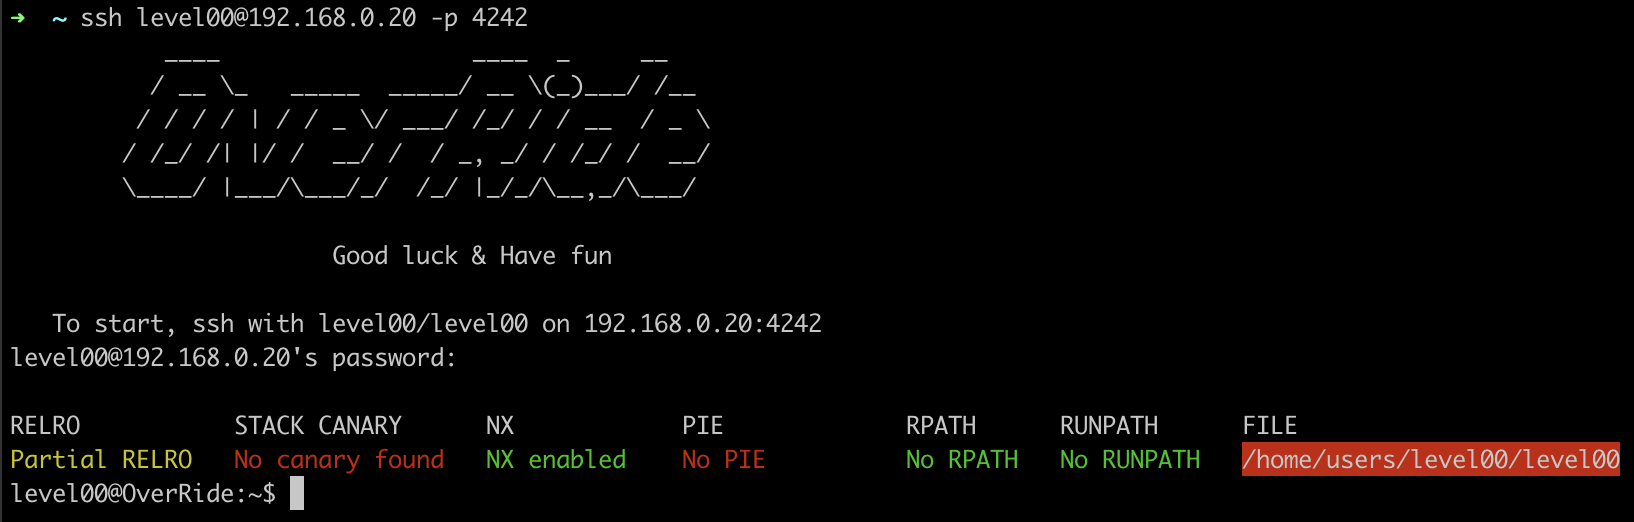 anyaschukin/override
Binary Exploitation and Reverse-Engineering (from assembly into C)