
rat-shell
 stphivos/rat-shell
Windows Remote Access Trojan (RAT)
command-and-controleducationpayload-development+3
stphivos/rat-shellWindows Remote Access Trojan (RAT)
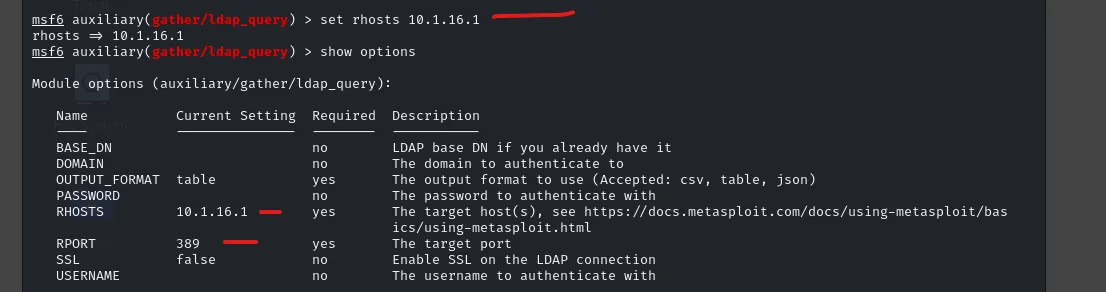 nyambiblaise/domain-controller-dc-exploitation-with-metasploit-impacket
End-to-end Domain Controller exploitation using Metasploit and Impacket: discovered DC10, exploited Zerologon (CVE-2020-1472), extracted NTLM hashes,…