
DOMPurify
 cure53/dompurify
DOMPurify - a DOM-only, super-fast, uber-tolerant XSS sanitizer for HTML, MathML and SVG. DOMPurify works with a secure default, but offers a lot of…
api-securitycode-analysisdefensive-tools+3
17.5k
cure53/dompurifyDOMPurify - a DOM-only, super-fast, uber-tolerant XSS sanitizer for HTML, MathML and SVG. DOMPurify works with a secure default, but offers a lot of…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
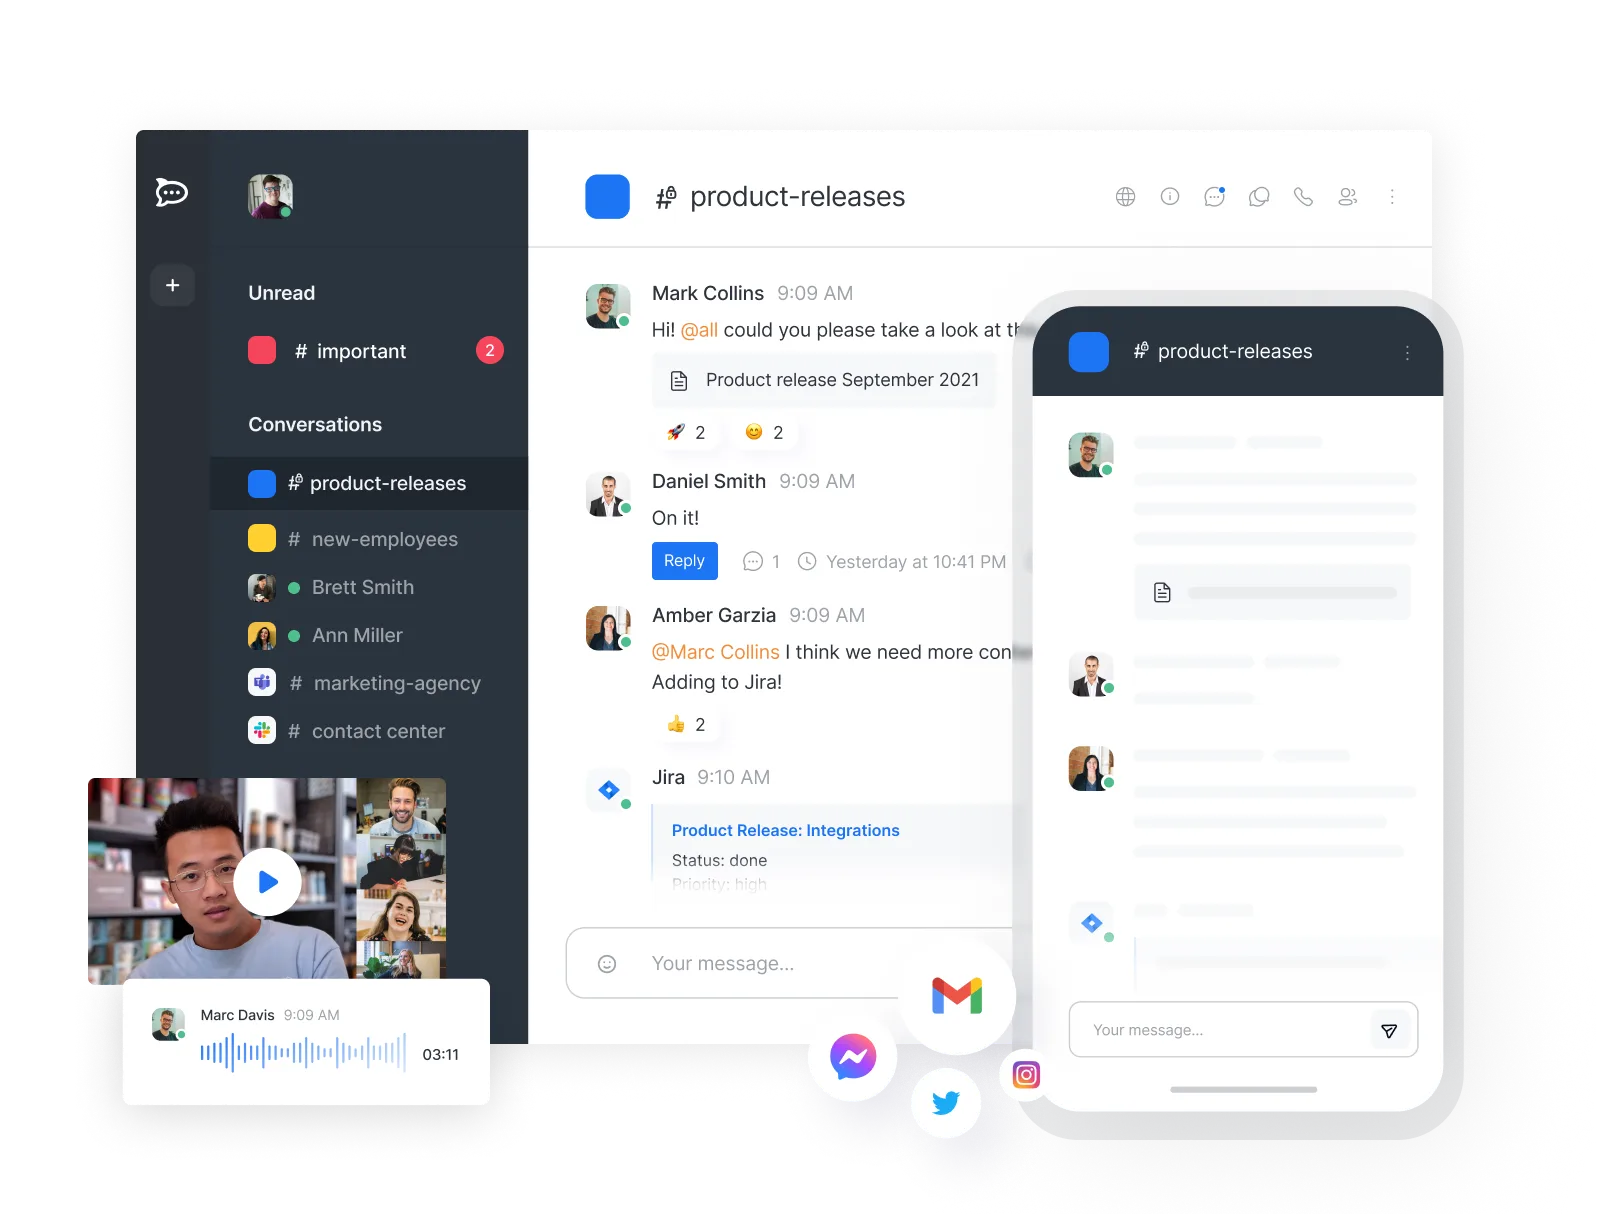 rocketchat/rocket.chat
The Secure CommsOS™ for mission-critical operations
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
 saied25/fix-react2shell-next
🔧 Fix vulnerable versions in Next.js and React RSC apps with one command to secure against CVE-2025-66478. Improve your app's safety effortlessly.
 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
 menevarad007/cve-2026-37750
Reflected XSS proof-of-concept for School Management System 1.0, demonstrating unauthenticated JavaScript execution via the type parameter in…
 ch4120n/cve-2026-58138
CVE-2026-58138 — Conductor (3.21.21..<3.30.2) unauthenticated RCE via INLINE GraalVM evaluator (HostAccess.ALL). Lab + PoC, verified e2e (root).
 alex-w-developer/getblocked
Lightweight, local-only MV3 Chrome extension for reducing common third-party web tracking.
 otakuliu/expression-sandbox-escape-simulation-lab
Educational lab demonstrating JavaScript expression sandbox escape techniques and patch evolution through multiple vulnerable sandbox versions, with…
 saku0512/cve-2026-9086-poc
CVE-2026-9086 proof-of-concept for Keycloak client URI validation bypass using mixed-case javascript: and data: XSS payloads, with Docker-based…
 badkeys/keypairvuln
Private keys generated with vulnerable keypair versions (CVE-2021-41117)
 pwntoday/cve-2025-6554
Proof-of-concept exploit for a V8 JavaScript engine vulnerability (CVE-2025-6554) demonstrating a TDZ bypass that leaks 'The Hole' sentinel, enabling…
 borahll/cve-2021-21220
Educational presentation detailing the exploitation of CVE-2021-21220, a V8 JIT type confusion leading to OOB access and RCE via WebAssembly, with…
 john-jung/cve-2026-26903-poc
A PoC for demonstrating CVE-2026-26903
 molnarg/cve-2014-0521
JavaScript-based exploit for Adobe Reader CVE-2014-0521 with proof-of-concept PDFs demonstrating file reading and data exfiltration via WebDAV.
 theethat-thamwasin/cve-2025-63307
An authenticated Stored Cross-site Scripting (XSS) vulnerability in laravel-file-manager v3.3.1 and below allows attackers with access to the file…
 shenal01/cve-2025-60880
Proof-of-concept for a stored XSS vulnerability in Bagisto admin panel, demonstrating SVG upload with malicious JavaScript and providing mitigation…