
CVE-2026-63030-Wp2Shell
 ghostinexile/cve-2026-63030-wp2shell
WordPress REST API SQLi to RCE PoC (CVE-2026-63030 & CVE-2026-60137)
code-analysiseducationexploitation+3
4
ghostinexile/cve-2026-63030-wp2shellWordPress REST API SQLi to RCE PoC (CVE-2026-63030 & CVE-2026-60137)
 686f6c61/poc-aiowpm-cve-2026-19949
Reproducible Docker-based proof-of-concept for CVE-2026-19949, a second-order SQL injection in All-in-One WP Migration <= 7.109 that leaks the…
 xshadow-here/cve-2026-8732
WP Maps Pro <= 6.1.0 - Unauthenticated Privilege Escalation via Administrator Account Creation
 incommatose/cve-2023-6063-poc
A Proof on Concept for CVE-2023-6063, a time-based blind SQL injection vulnerability in WP Fastest Cache ≤1.2.2.
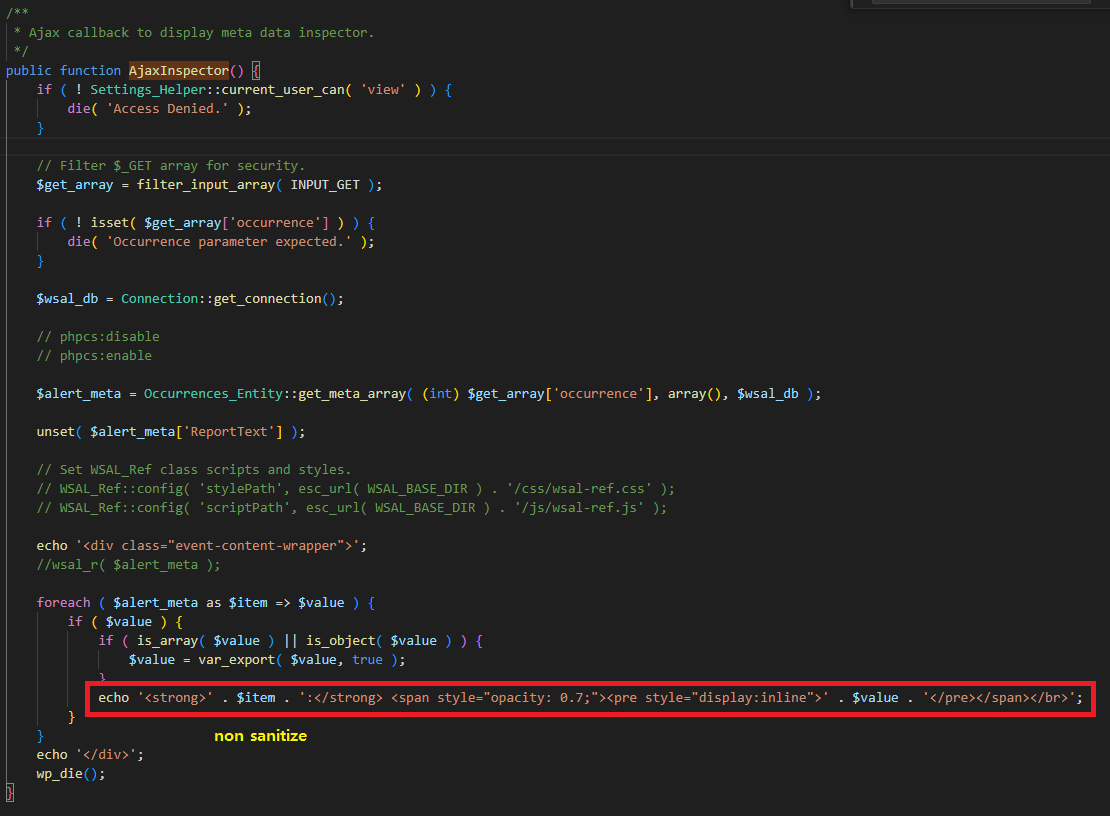 skrkcb2/cve-2025-0924-different
Technical analysis of CVE-2025-0924, a Stored XSS vulnerability in WP Activity Log plugin for WordPress. Includes root cause analysis, exploitation…
 0xsha/wp2shell
CVE-2026-63030 + CVE-2026-60137 - “wp2shell”: unauthenticated RCE in WordPress core
 dinosn/cve-2026-87902-wordpress-lfi-lab
Reproduction lab + URL-list scanner + PoC for CVE-2026-87902 / GHSA-7hp8-65ch-5whp — WordPress get_page_template() unauthenticated LFI to conditional…
 shinthink/cve-2026-9290
Pre-auth Local File Inclusion in WP User Manager <= 2.9.17 via path traversal in tab parameter (CVSS 7.5)
 squamity/cve-2026-8181-poc
Python PoC for CVE-2026-8181, a critical authentication bypass in Burst Statistics WordPress plugin. Includes exploit automation, bulk scanning, and…
 joshuavanderpoll/cve-2026-54806
Proof-of-concept exploit for CVE-2026-54806: unauthenticated PHP object injection in WP Activity Log plugin enabling blind RCE via User-Agent header.…
 codeb0ssx/ultimate-wp2shell
wp2shell — Pre-authentication RCE in WordPress Core (CVE-2026-60137 + CVE-2026-63030). Chains an SQL injection in author__not_in with batch-route…
 sudo-wp/sudowp-hooks-visualizer
A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…
 reneoliveirajr/wp_cve-2020-35489_checker
WordPress Sites Vulnerability Checker for CVE-2020-35489 - "Educational Use Only"
 dinosn/cve-2026-6379
Docker-based lab kit for CVE-2026-6379, an unauthenticated SQL injection in WP Photo Album Plus. Includes time-based blind PoC, root-cause analysis,…
 aj2108/cve-2026-9848
CVE-2026-9848 is an Unauthenticated SQL Injection (SQLi) vulnerability affecting the WP Ticket (Customer Support Ticket System & Helpdesk) plugin for…
 jenderal92/cve-2026-8181
CVE-2026-8181: Burst Statistics Auth Bypass → REST API takeover & admin creation. Python 2.7. Educational use only.
 notrustedx/job-manager-disclosure
CVE-2015-6668, relacionada con el plugin WP Job Manager para WordPress (versiones ≤ 0.7.25).
 ghoxtbyte/cve-2026-16265
Technical advisory and research notes for CVE-2026-16265, a Subscriber+ denial-of-service flaw in the WP Maps WordPress plugin fixed in version 4.9.7.