CVE-2025-49113-Roundcube_1.6.10

Authenticated remote code execution exploit for Roundcube 1.6.10 (CVE-2025-49113). Delivers a reverse shell via a crafted PHP payload through the…

Authenticated remote code execution exploit for Roundcube 1.6.10 (CVE-2025-49113). Delivers a reverse shell via a crafted PHP payload through the…

Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…

Exploit for VariaType HTB machine leveraging XML injection in fontTools to achieve RCE via PHP reverse shell payload in .designspace metadata.

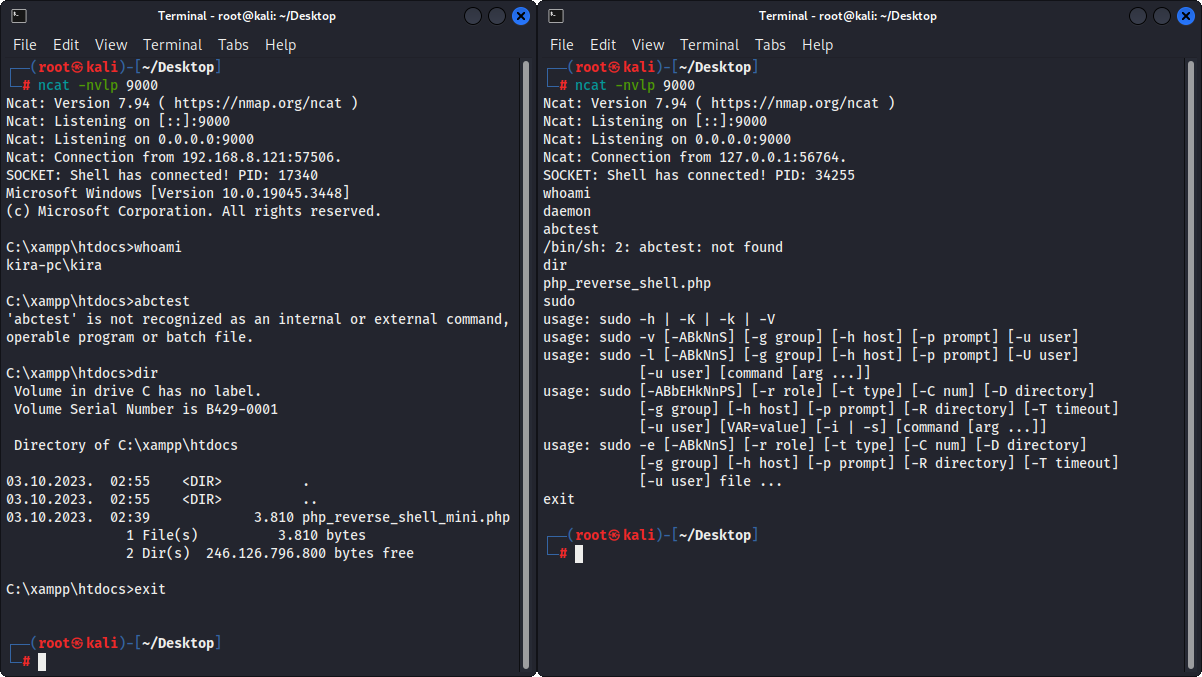
This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…

PHP shells that work on Linux OS, macOS, and Windows OS.

Proof-of-concept exploit for CVE-2026-54806: unauthenticated PHP object injection in WP Activity Log plugin enabling blind RCE via User-Agent header.…

CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…

Proof-of-concept exploit for CVE-2026-29782, chaining SQL injection and PHP object injection to achieve remote code execution in OpenSTAManager.…

Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…

Controlled NGINX HTTP/2 frame injection lab for CVE-2026-42926 patch validation and defensive research

Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…

CVE-2026-56290 - Mass Exploit for Joomla Com_pagebuilderck component (Unrestricted File Upload → RCE). Multi-threaded, automatic CSRF bypass, PHP…

Proof-of-concept exploit for PHP CGI argument injection (CVE-2024-4577) enabling remote code execution on vulnerable Windows servers with scanning…

PoC exploit for Wolf CMS <= 0.8.3.1: authenticates to Admin, writes an arbitrary PHP file to /public via FileManagerController, and executes commands…

CVE-2023-30253 — Dolibarr ERP/CRM 17.0.0 RCE via PHP code injection (exploit educativo)

Automated exploit for CVE-2024-25641 targeting Cacti 1.2.26. Achieves remote code execution via authenticated arbitrary file write in the Package…

CVE-2024-27348 Exploitation Toolkit: Complete RCE exploit for Apache Huge-Graph-Server vulnerability.

Exploit for CVE-2024-40110, an unauthenticated file upload RCE in Poultry Farm Management System v1.0. Uploads a PHP shell to execute arbitrary…