
pygoat
 adeyosemanputra/pygoat
intentionally vuln web Application Security in django
educationlabs-practicepenetration-testing+2
343
adeyosemanputra/pygoatintentionally vuln web Application Security in django
 vulnex/bytesrevealer
Online Reverse Enginerring viewer
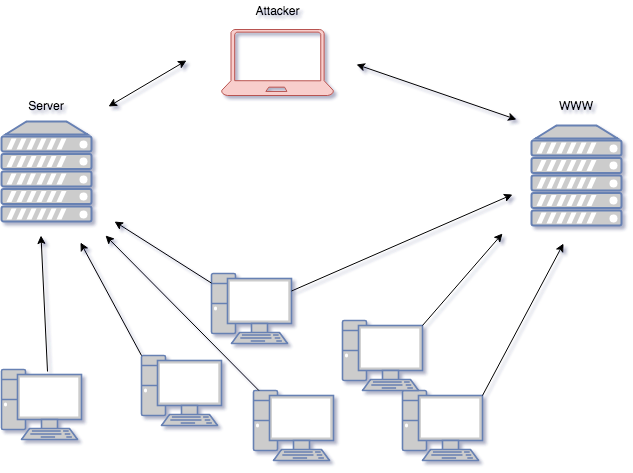 m507/m-botnet
A C2 project that controls a self-propagating MS17-010 worm.
 boredhackerblog/winrar_cve-2023-38831_lazy_poc
lazy way to create CVE-2023-38831 winrar file for testing
 byinarie/cve-2024-3094-info
Information for CVE-2024-3094
 anomalousvectors/cve-2022-24785-poc-lab
Moment.js vuln lab
 parbatzone/reconvault
🔍 Recon notes organizer for bug bounty hunters and CTF players — subdomains, ports, endpoints, vulns, all in one place.
 ns-projects-unina/ctf_cve_dsp_1
Una CTF, in formato DSP-compliant, basata sulla CVE-2025-29927 di nextjs.
 13m0n4de/pngcheck-vulns
A repository of proof-of-concept files demonstrating disclosed and patched vulnerabilities in pngcheck (2.4.0 - 3.0.1), including CVE-2020-27818,…
 meterianhq/log4j-vuln-coverage-check
A simple project to check coverage of Log4J vuln CVE-2021-44228 (and related)
 sallocinavalcante/lab-smb-responder-cve-2024-21413
Laboratorio criado para PenTest da Vuln CVE 2024-214113(MONIKER LINK).
 gromhacks/payload-and-polyglot-lists
GromHacks Labs -- The payload lists they don't want you to have. 1,324 injection probes beamed down from the mothership to detect what's injectable…
 madstap/bouncy-castle-generative-test-poc
A generative test that would've caught CVE-2020-28052
 flame-11/cve-2024-3408-dtale
Vuln lab for CVE-2024-3408 - D-Tale Authentication Bypass & RCE
 dannyendortest/java-vulnerable
EXPOSURE demo target: Tomcat (CVE-2016-0714) + Apache Rave (CVE-2013-1814) + Java filter-padding deps
 kali-mx/cve-2023-38408
PoC for the recent critical vuln affecting OpenSSH versions < 9.3p2
 bshyuunn/bandiview-7.05-vuln-poc
bandiview (7.05) vuln PoC | CVE-2024-45870, CVE-2024-45871, CVE-2024-45872
