Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
241 results
agent-governance-toolkit preview

agent-governance-toolkit

GitHubmicrosoft/agent-governance-toolkit

Policy enforcement, zero-trust identity, execution sandboxing, and audit logging for autonomous AI agents. Covers 10/10 OWASP Agentic Top 10 with…

ai-securitycurated-resourcesdevsecops+2
6.3k
2h 4m ago
wstg preview

wstg

GitHubowasp/wstg

The Web Security Testing Guide is a comprehensive Open Source guide to testing the security of web applications and web services.

educationlearning-paths-coursespenetration-testing+2
9.8k8h 5m ago
kubernetes-goat preview

kubernetes-goat

GitHubmadhuakula/kubernetes-goat

Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…

cloud-securitycontainer-escapecontainer-security+4
5.8k5 months ago
owasp-cstg preview

owasp-cstg

GitHubowasp/owasp-cstg

Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…

cloud-securitycurated-resourceseducation+8
353 months ago
training-security-awareness preview

training-security-awareness

GitHubransomleak/training-security-awareness

Open-source interactive security awareness training library with 130+ SCORM exercises covering phishing, vishing, BEC, MFA fatigue, and OWASP AI/LLM…

ai-securityeducationemail-security+5
1917 days ago
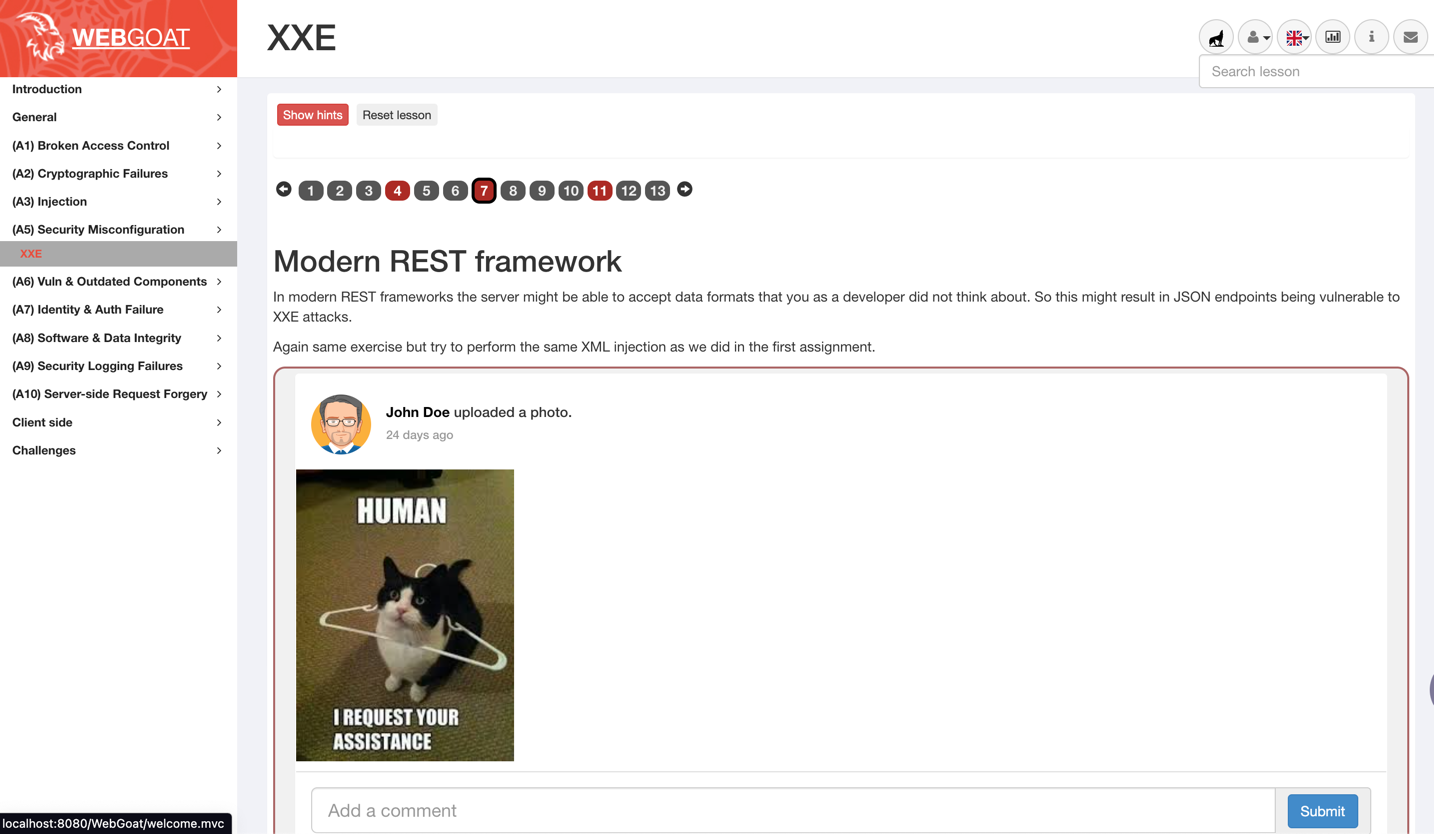
WebGoat preview

WebGoat

GitHubwebgoat/webgoat

Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…

ctfeducationlabs-practice+4
9.3k3 days ago
CyberStrike preview

CyberStrike

GitHubcyberstrikeus/cyberstrike

Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…

ai-securitycloud-securityeducation+9
2.8k1 day ago
CheatSheetSeries preview

CheatSheetSeries

GitHubowasp/cheatsheetseries

The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.

api-securityauthenticationcloud-security+6
33.2k2 days ago
OWASP-Top-10-AI-Infrastructure-Security-Risks preview

OWASP-Top-10-AI-Infrastructure-Security-Risks

GitHubowasp/owasp-top-10-ai-infrastructure-security-risks

A practical framework identifying and prioritizing the top security risks in AI datacenter infrastructure, covering hardware, networking, management…

ai-securitycloud-infrastructure-securitycurated-resources+5
22 days ago
aiiroverlay preview

aiiroverlay

GitHubjacobideji/aiiroverlay

AI IR Overlay™ — practical incident response framework for AI agents in production. Built on NIST SP 800-61 r3, mapped to NIST AI RMF, NIST CSF 2.0,…

ai-securitycloud-securitycurated-resources+4
32 months ago
wrongsecrets preview

wrongsecrets

GitHubowasp/wrongsecrets

Vulnerable app with examples showing how to not use secrets

cloud-securitycontainer-securityctf+5
1.5k1 day ago
atomicvulns preview

atomicvulns

GitHubdoretox/atomicvulns

Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.

ctfeducationlabs-practice+5
85 days ago
SBOM-VEX-Taint-Analysis preview

SBOM-VEX-Taint-Analysis

GitHubowasp/sbom-vex-taint-analysis

Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…

ai-securitycurated-resourceseducation+3
41 month ago
juice-shop preview

juice-shop

GitHubjuice-shop/juice-shop

Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…

ctfeducationlabs-practice+3
13.9k1 month ago
AI_Security_Top preview

AI_Security_Top

GitHubghostwolflab/ai_security_top

A structured knowledge base covering AI security fundamentals, threat modeling, red team offensive techniques, and blue team defenses, including LLM…

adversarial-attackai-securitycurated-resources+5
1476 months ago
training-application-security preview

training-application-security

GitHubransomleak/training-application-security

Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…

api-securitydevsecopseducation+7
187 days ago
llm-agent-testbed preview

llm-agent-testbed

GitHubpie-script/llm-agent-testbed

An empirical security testbed evaluating prompt injection, confused-deputy vulnerabilities, and tool-calling defenses in LLM agents.

ai-securityapi-securityeducation+4
143 days ago
MASTG-Hacking-Playground preview

MASTG-Hacking-Playground

GitHubowasp/mastg-hacking-playground

Collection of intentionally insecure iOS and Android apps for learning mobile security testing, reverse engineering, and vulnerability analysis,…

android-securityeducationios-security+5
6953 years ago
Previous12…14Next