
CVE-2026-77771
 pervinzahidli/cve-2026-77771
Advisory for CVE-2026-77771, a 2FA bypass in the miniOrange WordPress plugin via session-scoped OTP lockout, with impact analysis and remediation…
authenticationdefensive-toolseducation+2
pervinzahidli/cve-2026-77771Advisory for CVE-2026-77771, a 2FA bypass in the miniOrange WordPress plugin via session-scoped OTP lockout, with impact analysis and remediation…
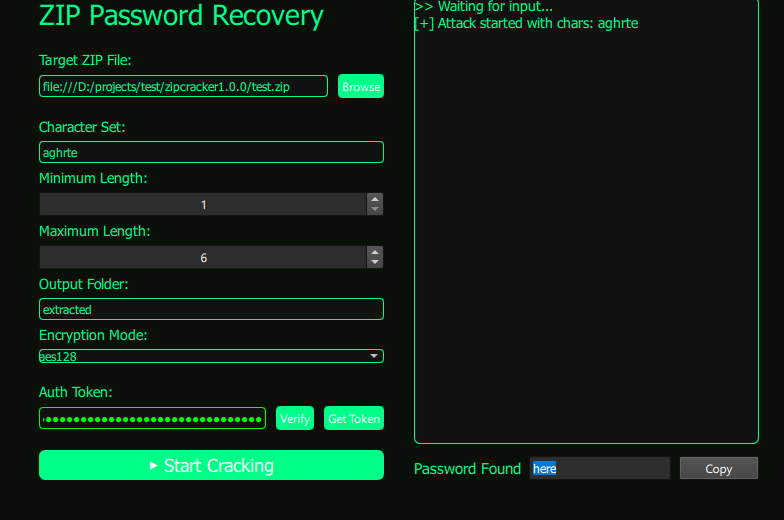 the-hollowclan/zipcracker
A 100% free standalone ZIP password recovery tool
 pedrofbrm/apache-web-log-analysis-lab
Blue Team lab focused on analyzing Apache web access logs to detect directory brute forcing and web scanning activity.
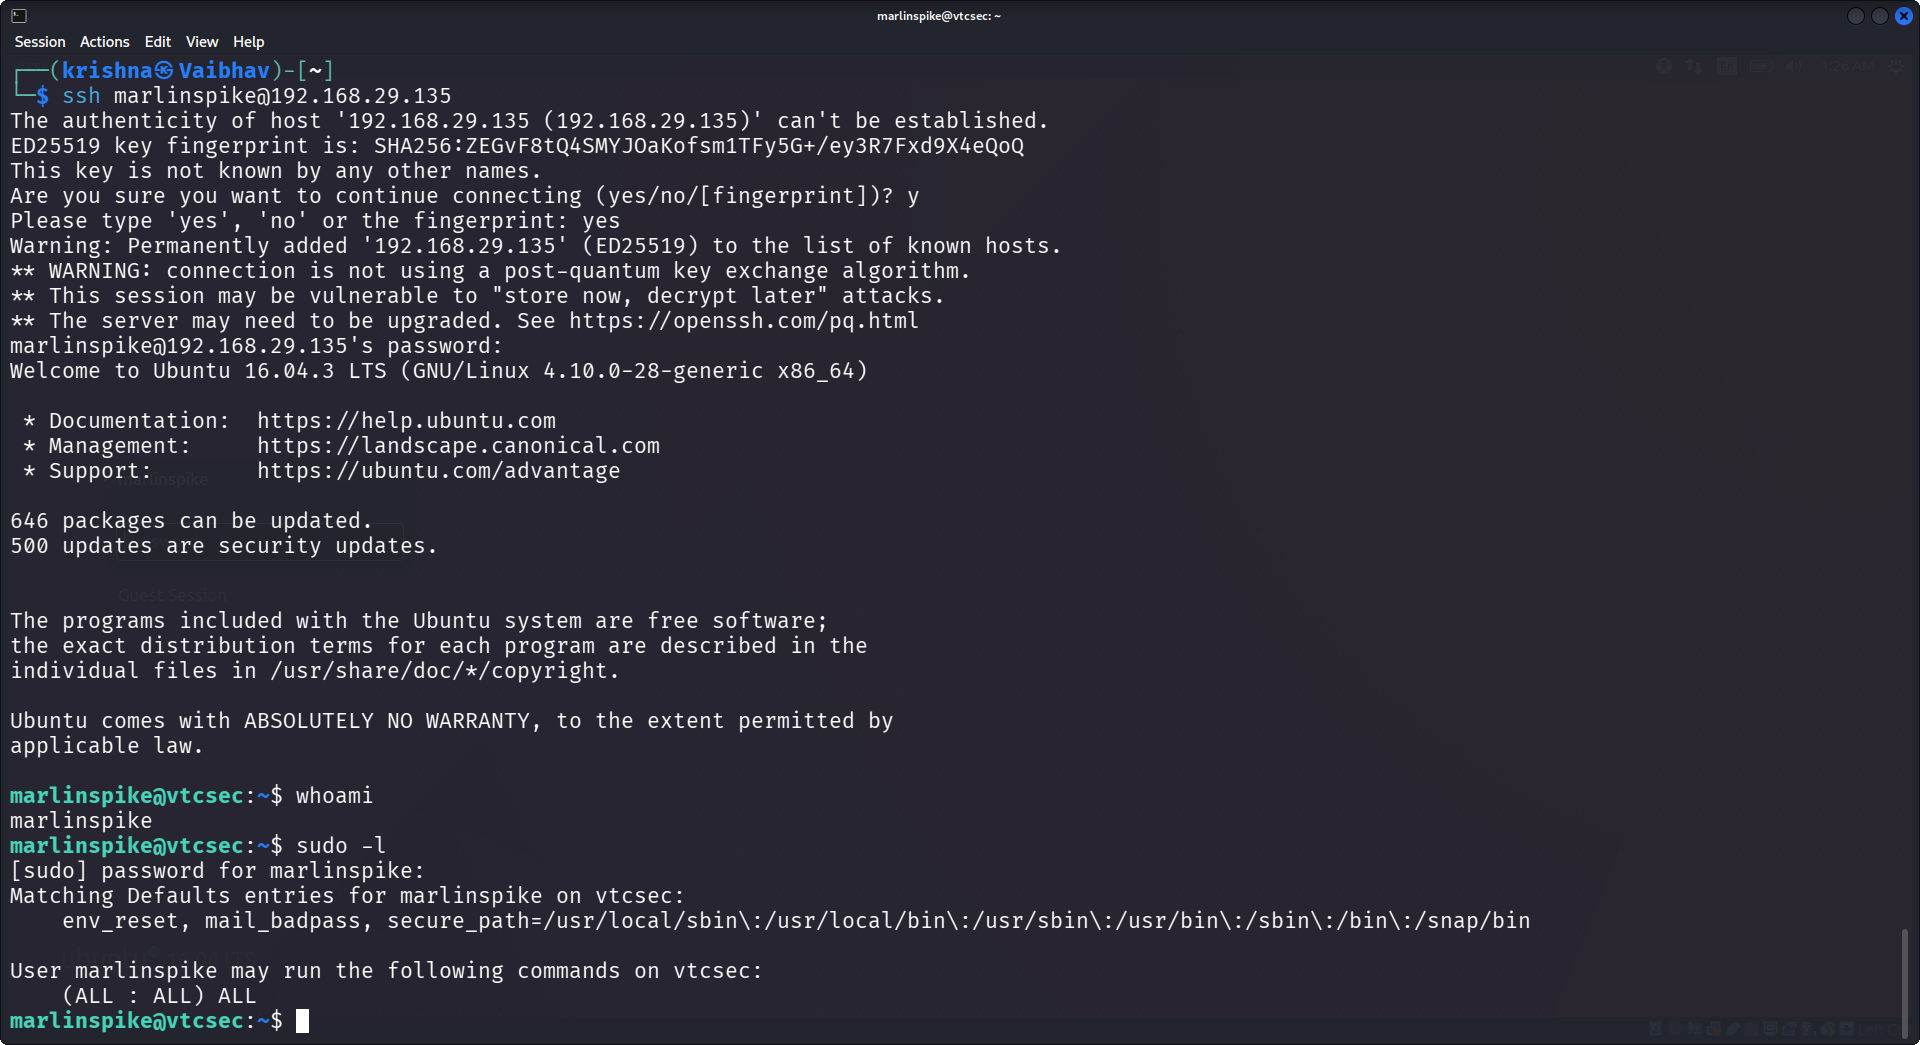 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
 itzmetanjim/cve-2026-8697
Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…
 taisa456/network-security-snort
Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…
 anonymous121029034720384234234/py-network-scanner
Advanced network penetration testing toolkit with SSH vulnerability assessment, CVE-2018-15473 exploitation, stealth brute force capabilities, and…
 otterhacker/labs4u2self
Deployable AWS-hosted Active Directory pentest lab with domain controller and vulnerable MSSQL; practice S4U2Self abuse, SQL brute force, and RCE.
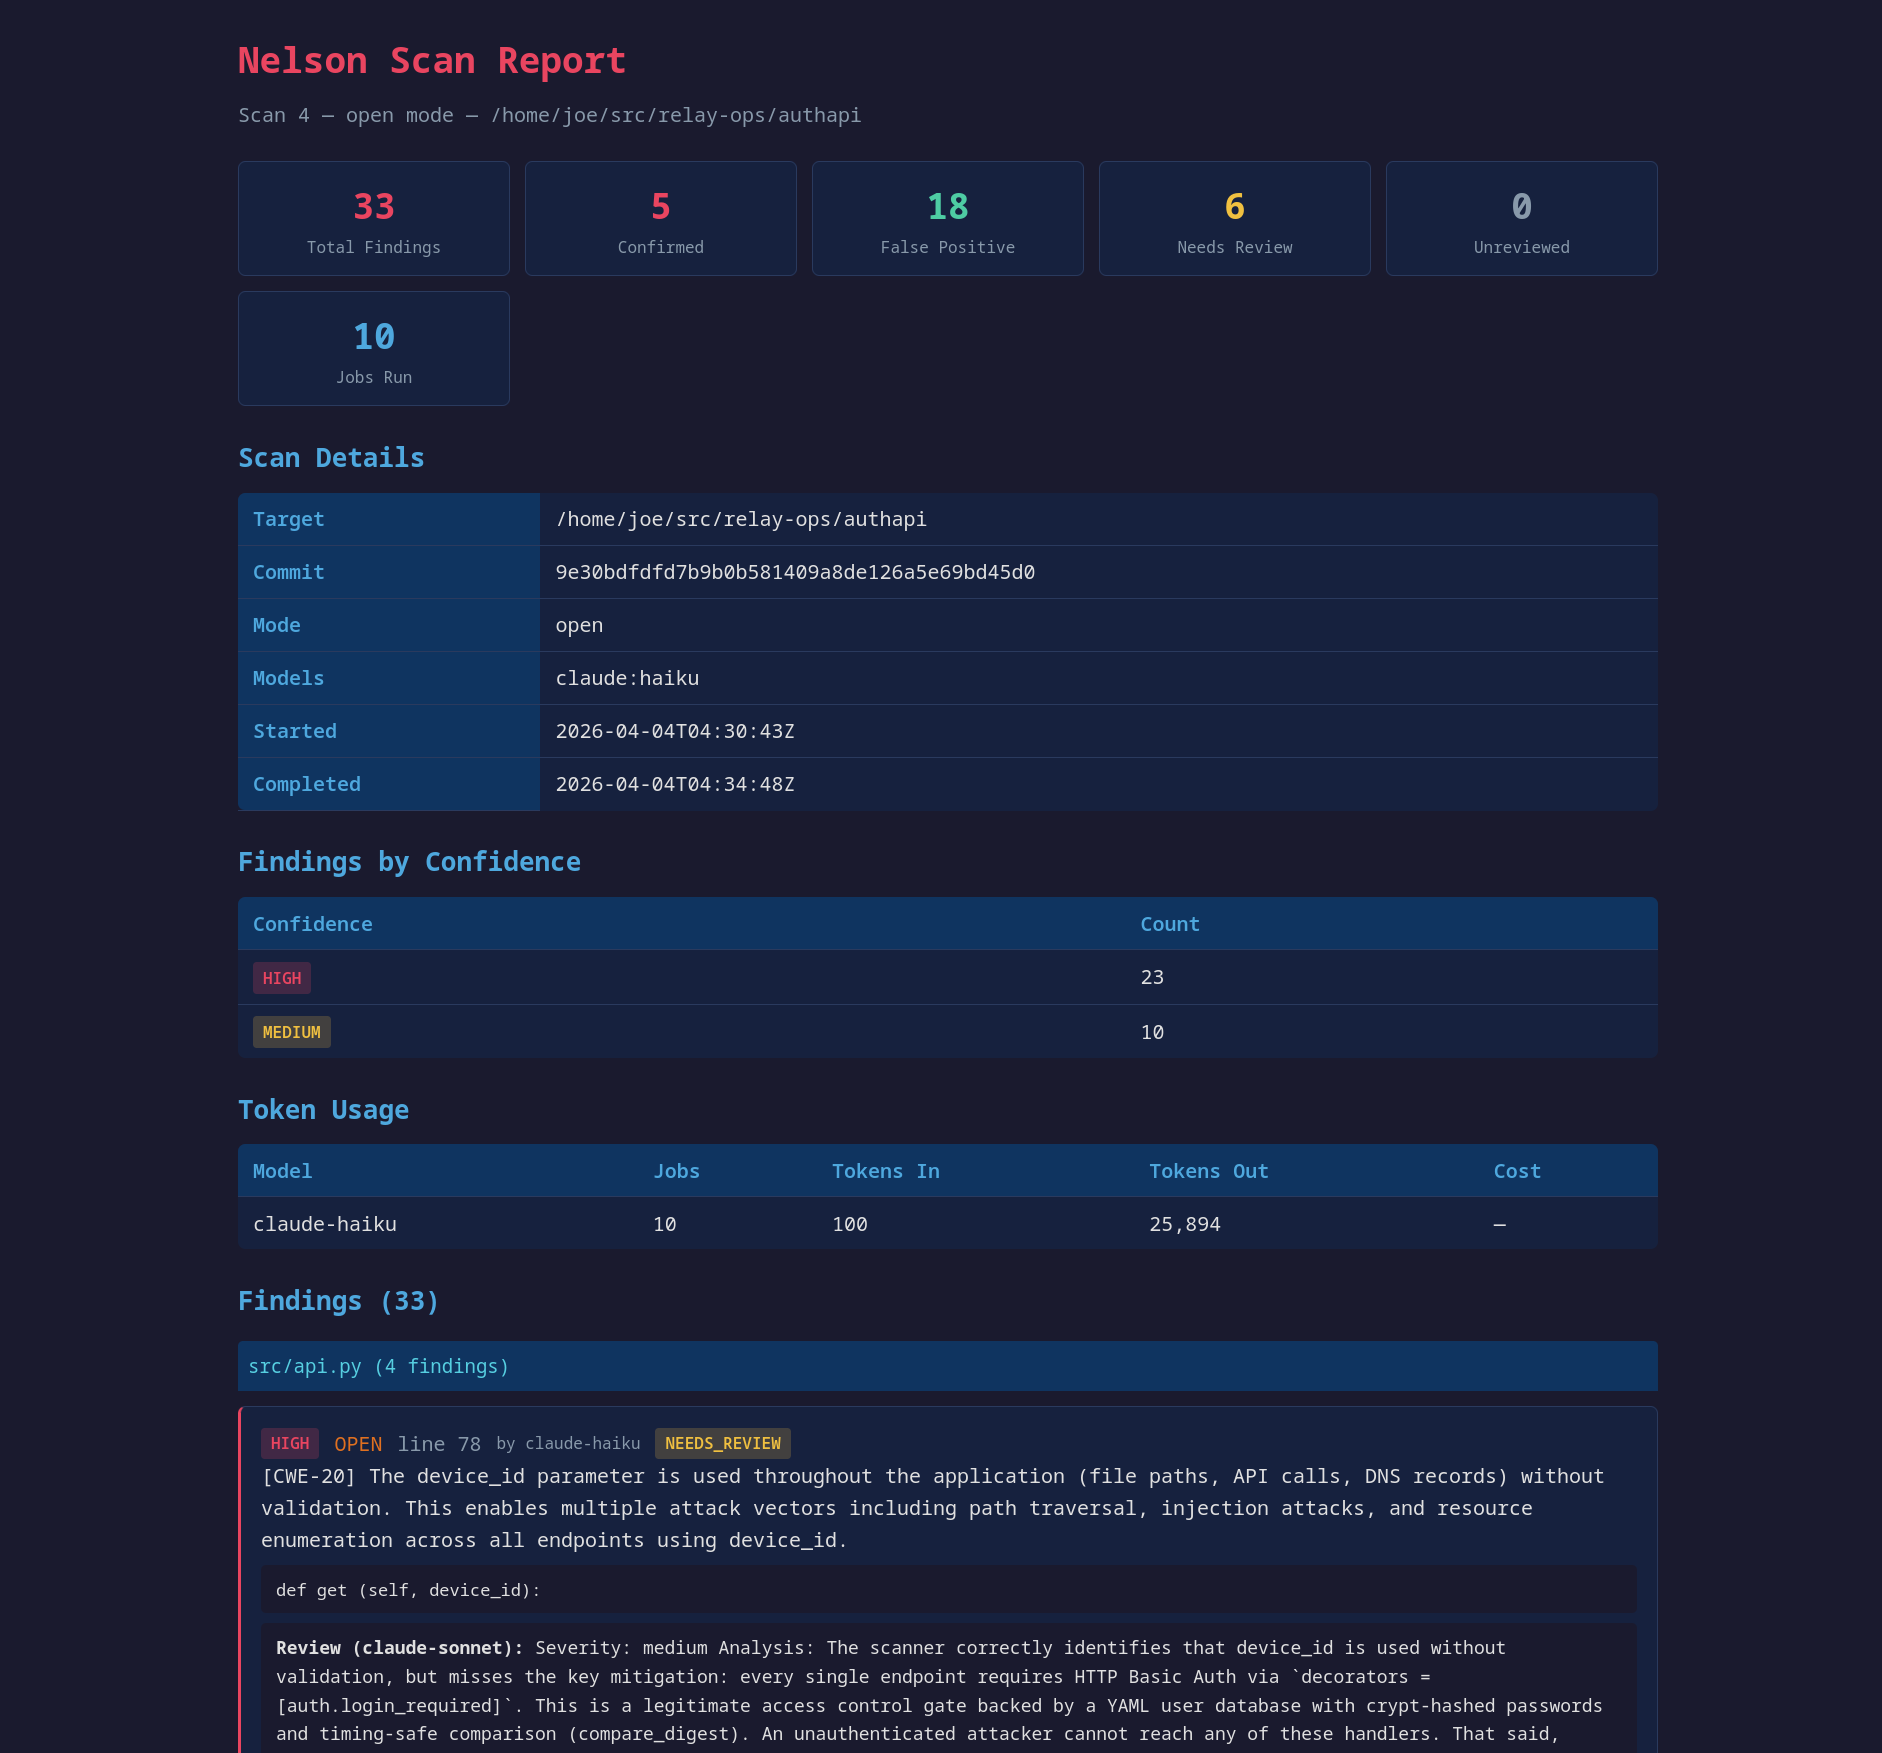 swelljoe/nelson
Finding vulnerabilities through dumb brute force
 m0d0ri205/wargame-turkey_in_2
CTF wargame platform featuring Unicode bypass exploitation (CVE-2015-9238), flag file segmentation, brute force delay, and password hashing for…
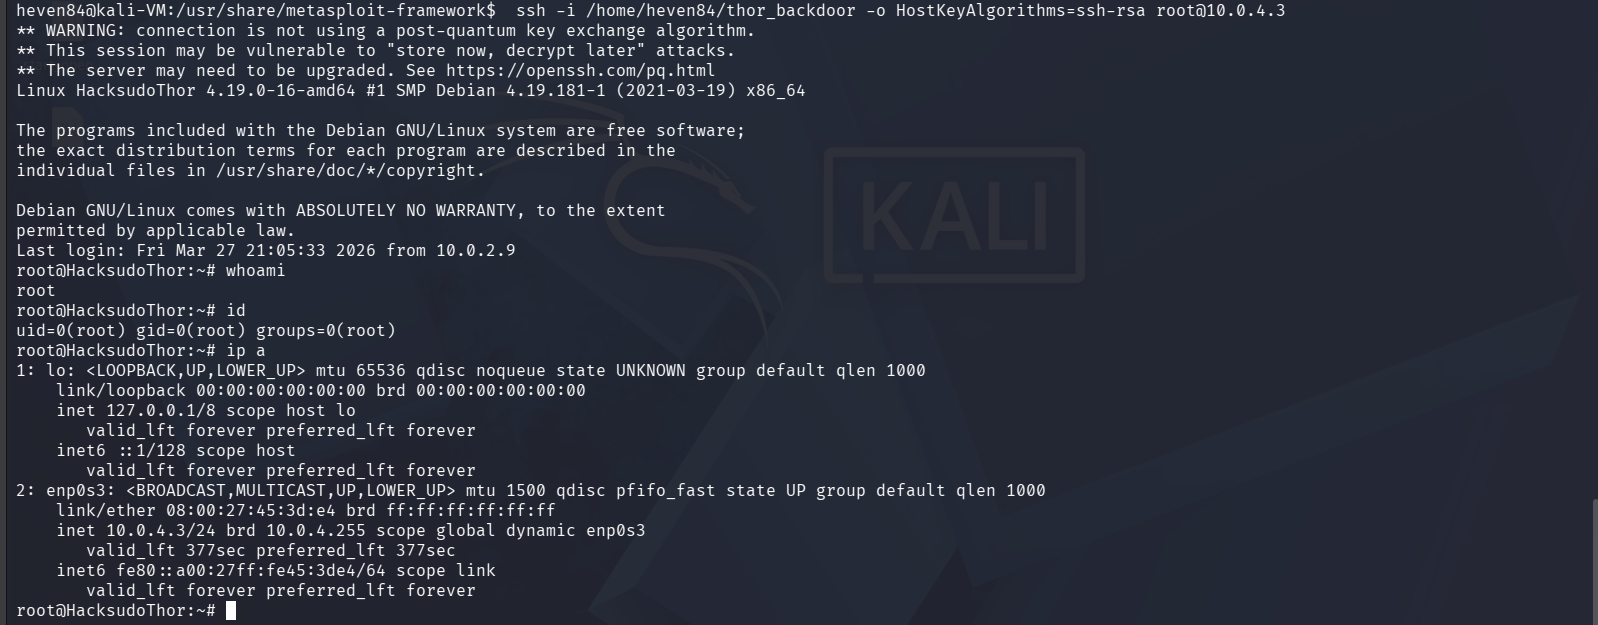 heventafese/penetration-testing-walkthrough-hacksudo-thor
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…
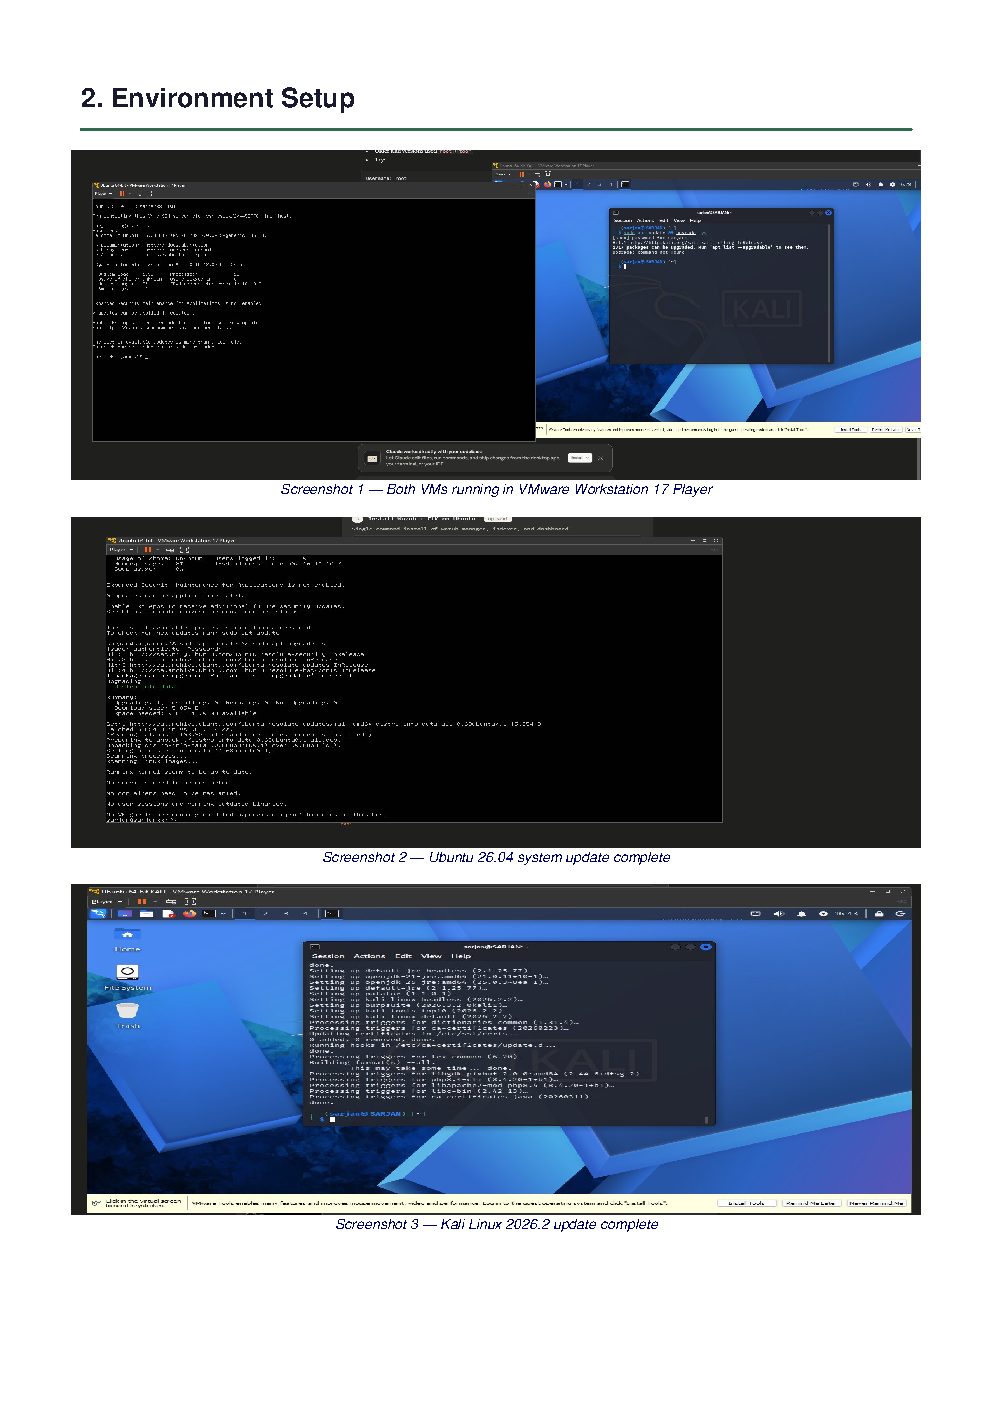 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
 coldfusionx/cve-2019-17240_bludit-bf-bypass
Bludit <= 3.9.2 - Authentication Bruteforce Mitigation Bypass Exploit/PoC
 besioo/hackerone
Brute-force scraper for HackerOne disclosed reports via their public API, collecting report IDs, links, titles, and states for security research and…
 lhiebert01/network-attack-simulator
Streamlit educational dashboard that simulates port scanning, DoS, brute force and data exfiltration attacks, with visualizations, attack logs and…