CVE-2024-28000
 alihzsec/cve-2024-28000
Hands-on exploit lab for CVE-2024-28000 — unauthenticated privilege escalation in LiteSpeed Cache (WordPress plugin, <=6.3.0.1). Spins up a…
educationexploitationlabs-practice+5
alihzsec/cve-2024-28000Hands-on exploit lab for CVE-2024-28000 — unauthenticated privilege escalation in LiteSpeed Cache (WordPress plugin, <=6.3.0.1). Spins up a…
 cveproject/cvelistv5
CVE cache of the official CVE List in CVE JSON 5 format
 incommatose/cve-2023-6063-poc
A Proof on Concept for CVE-2023-6063, a time-based blind SQL injection vulnerability in WP Fastest Cache ≤1.2.2.
 fortbridge-uk/cve-2026-75604
Reproduction lab and exploit tooling for CVE-2026-75604, a path traversal in Next.js incremental cache leading to unauthenticated RCE on Windows.…
 luotian2/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.
 adilkurtulmus/linux-copy-fail-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431 (Copy-Fail), a Linux kernel AF_ALG and splice() flaw enabling page cache poisoning and local privilege…
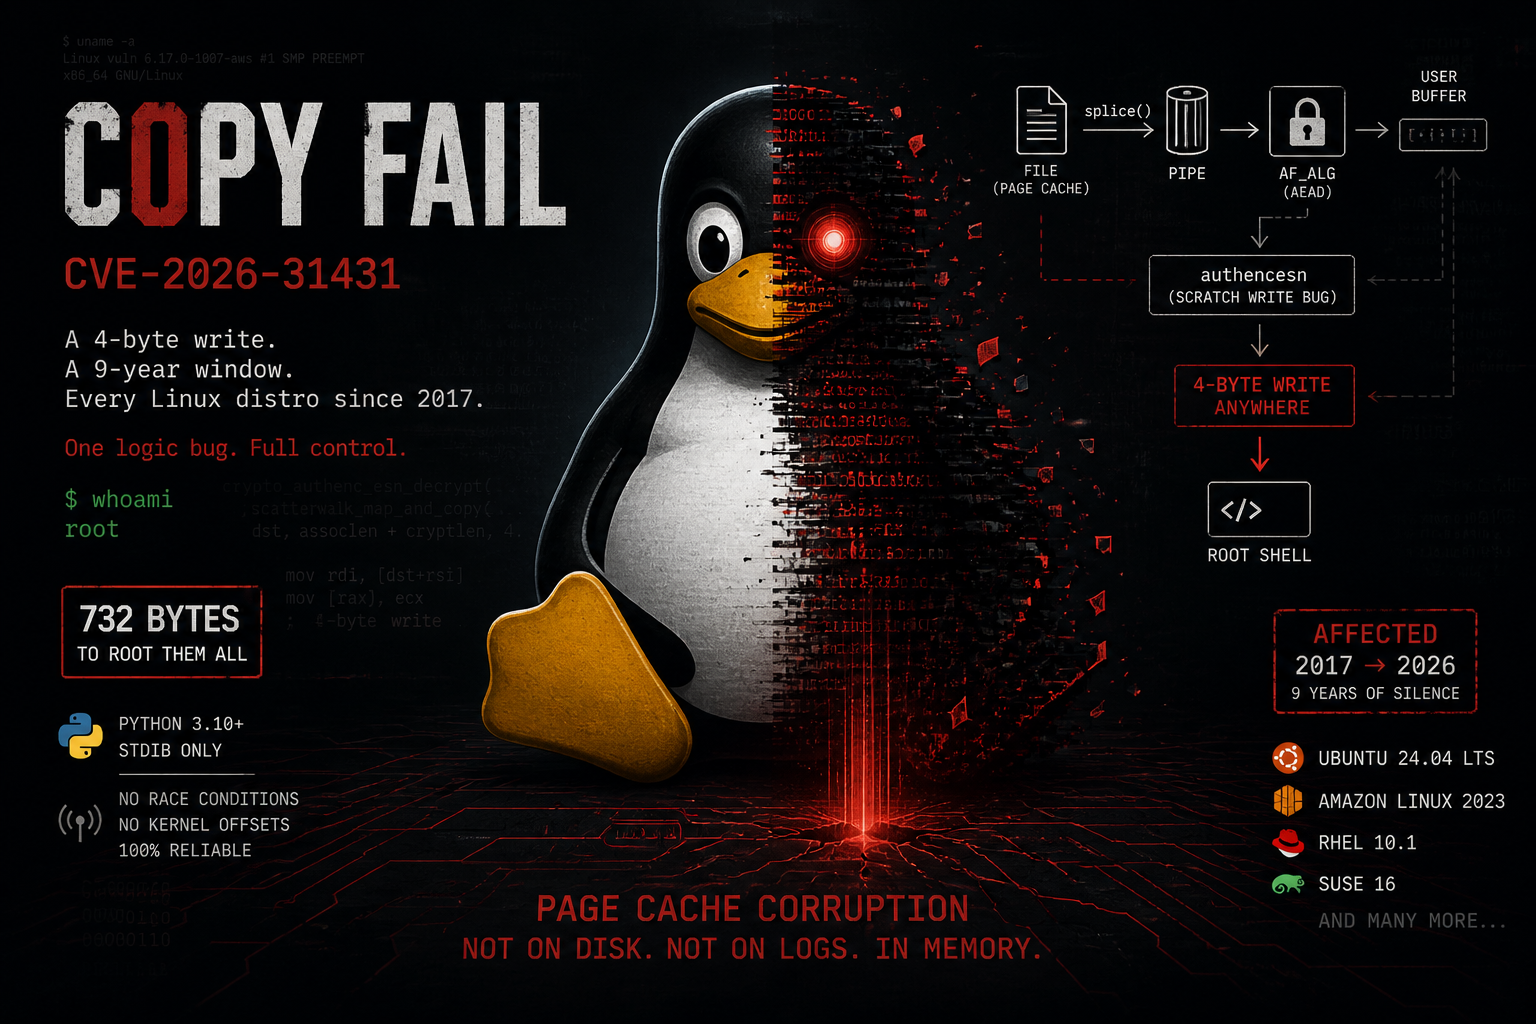 themalwareguardian/cve-2026-31431
A structured explanation of CVE-2026-31431 (Copy Fail), connecting the three kernel changes that introduced the vulnerability and enabled its…
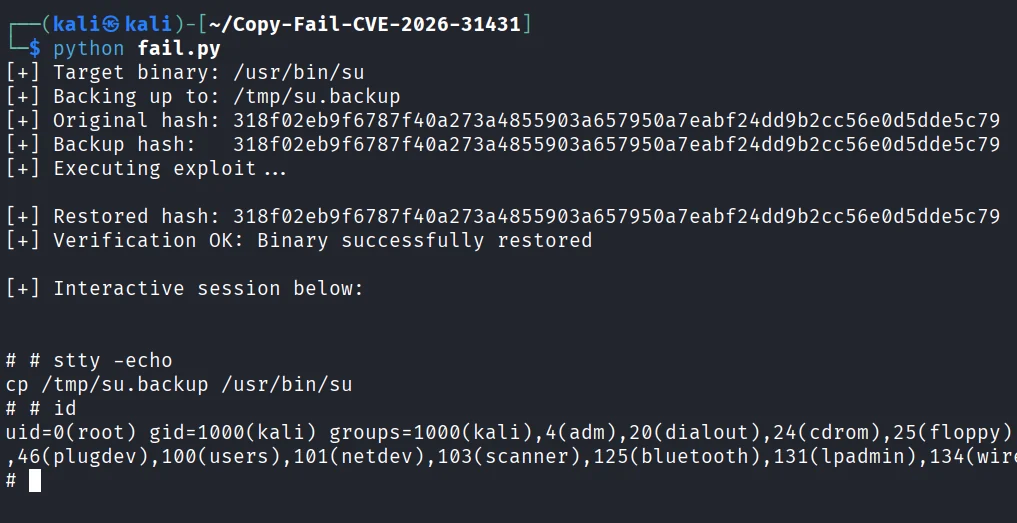 mohamedkarrab/copy-fail-cve-2026-31431
Proof-of-concept exploit for Linux kernel CVE-2026-31431 (Copy Fail) that abuses AF_ALG to corrupt setuid-root binaries in page cache, achieving…
 nicholasc03/dns-poisoning-triage-lab
Forensic triage of DNS cache poisoning in legacy hardware. Includes PCAP analysis of 839-byte unsolicited record injections, CVE-2025-40778 mapping,…
 rootdirective-sec/cve-2026-3844-lab
Local Docker lab for reproducing CVE-2026-3844, an unauthenticated arbitrary file upload to RCE in the WordPress Breeze Cache plugin. Compares…

 rat5ak/cve-2026-3805-curl-smb-uaf
CVE-2026-3805: Use-After-Free in curl SMB connection reuse - heap info disclosure
 dhananjayasj/cve-2026-3844-breeze-cache-wordpress-plugin-remote-code-execution
Docker lab and manual exploitation guide for CVE-2026-3844, a critical unauthenticated arbitrary file upload vulnerability in the Breeze Cache…
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 0xfuffm3/cve-2026-31635-dirtydecrypt
Linux kernel local privilege escalation exploit for CVE-2026-31635 that corrupts page cache via RxRPC in-place decryption, overwrites read-only…
 nehkark/cve-2025-40778
Proof-of-concept demonstrating DNS cache poisoning via additional record injection in BIND 9, with tools to validate and exploit CVE-2025-40778 for…
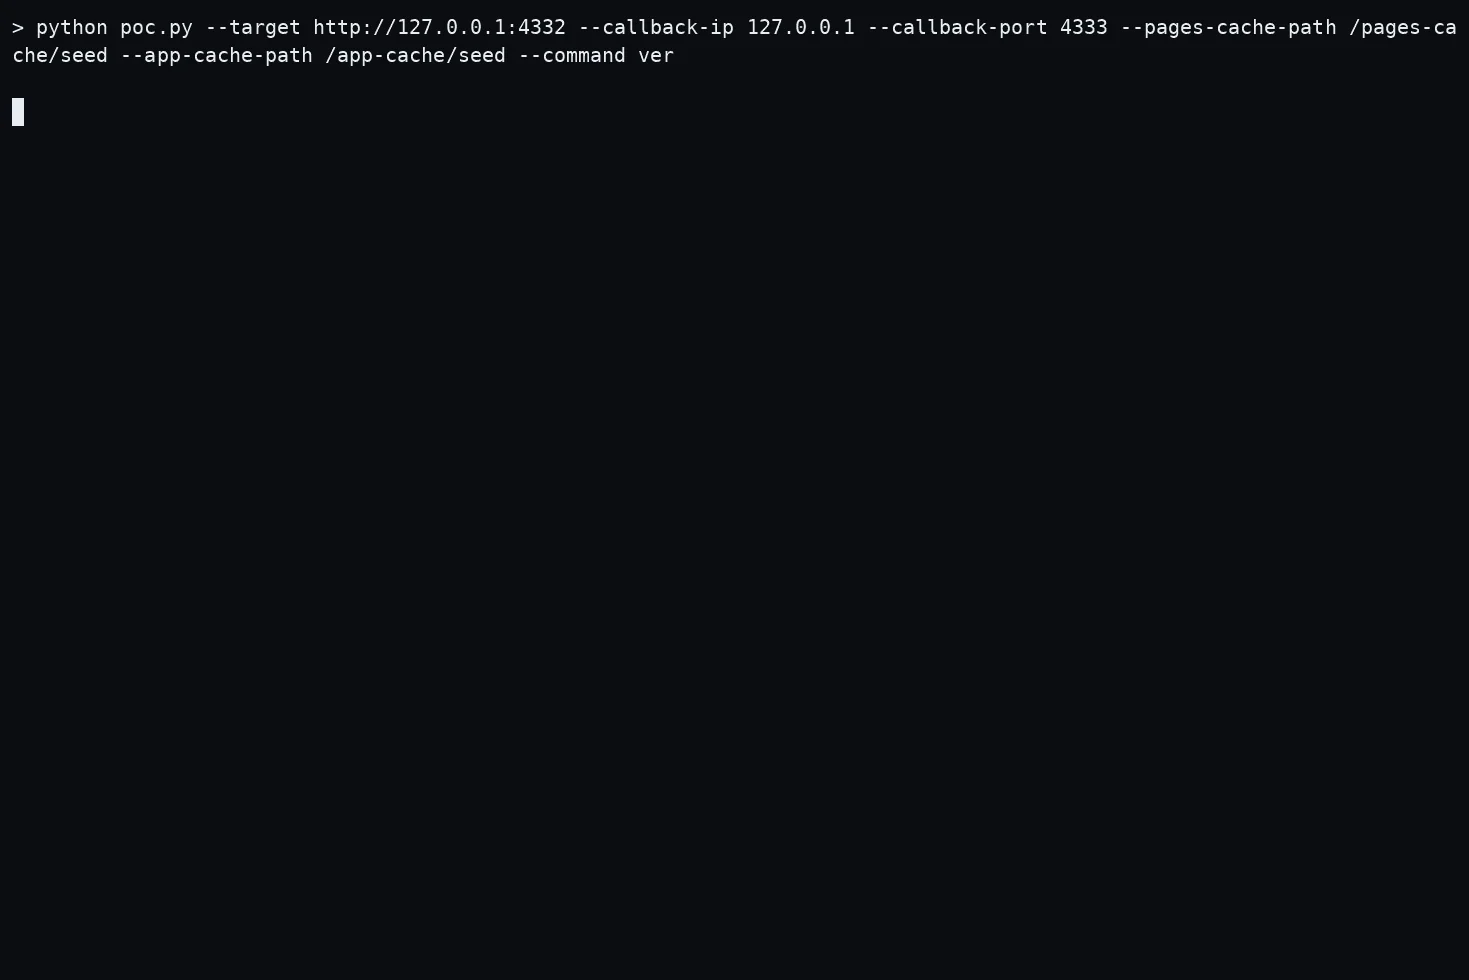 hackspeak/cve-2026-75604
Proof-of-concept exploit for CVE-2026-75604, an unauthenticated RCE in Windows-hosted Next.js via cache path traversal and forged Server Action, for…