
heartbleed
 cheese-hub/heartbleed
Educational Docker-based lab demonstrating the Heartbleed bug (CVE-2014-0160) with hacker, victim, and server containers for hands-on exploitation…
container-securityctfeducation+4
2
cheese-hub/heartbleedEducational Docker-based lab demonstrating the Heartbleed bug (CVE-2014-0160) with hacker, victim, and server containers for hands-on exploitation…
 kn0x0x/cve-2025-32756-poc
Proof of Concept for CVE-2025-32756 - A critical stack-based buffer overflow vulnerability affecting multiple Fortinet products.
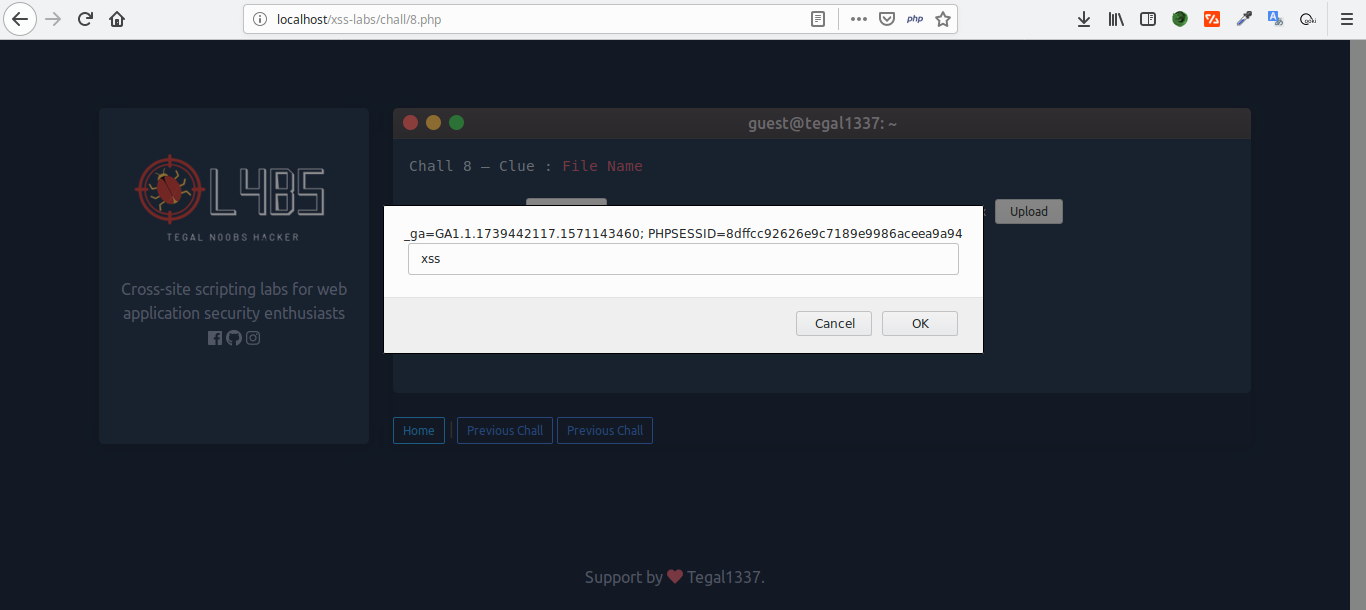 tegal1337/0l4bs
Cross-site scripting labs for web application security enthusiasts
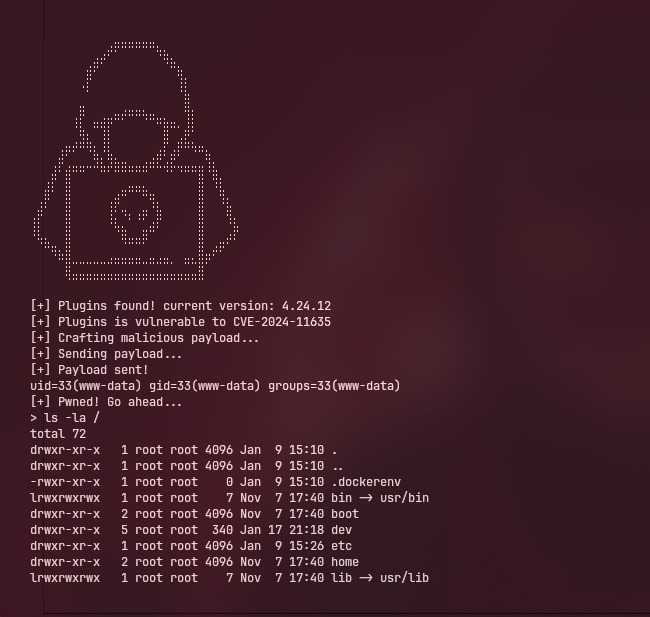 vigilante-1337/cve-2024-11635
The WordPress File Upload plugin for WordPress is vulnerable to Remote Code Execution in all versions up to, and including, 4.24.12 via the…
 tnot123/cve-2017-9822
In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…
 cavi-au/consent-o-matic
Browser extension that automatically fills out cookie popups based on your preferences
 vighneshnair7/cve-2024-51031
Proof-of-concept for CVE-2024-51031: Stored Cross-Site Scripting (XSS) in Sourcecodester Cab Management System 1.0 via manage_account.php fields.…
 junghyeonkum/cve-2022-24706
Proof-of-concept exploit for CVE-2022-24706 targeting Apache CouchDB 3.2.1 and below. Demonstrates remote command execution via Erlang Distribution…
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
 nccgroup/setcookieanalysisinbrowsers
SetCookie Analysis in Browser Research Results
 dani33339/tough-cookie-v2.5.0-patched
Patched tough-cookie v2.5.0 fixing CVE-2023-26136 prototype pollution vulnerability with Object.create(null) in MemoryCookieStore, including exploit…
 charanmv08/cve-2022-29117-assessment
CVE-2022-29117 (.NET Cookie-Handling DoS) Assessment, Understanding & Questions Framework
 cucumberanorsncompany/sealsecurityassignment
Researching on the vulnrability CVE-2023-26136
 maanvader/cve-2023-27524-poc
A POC for the all new CVE-2023-27524 which allows for authentication bypass and gaining access to the admin dashboard.
 uriyahav/tough-cookie-2.5.0-cve-2023-26136-fix
ecurity patch for CVE-2023-26136 in tough-cookie 2.5.0 - Prototype pollution vulnerability fix with backward compatibility
 fuyuooumi1027/cve-2023-45857-demo
Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…
 eliot-code/cve-2026-52924
Technical analysis of CVE-2026-52924, a critical use-after-free in Linux kernel SCTP stale cookie handling, including root cause, attack flow, fix,…
 ghostpels/cve-2026-75865
Unauthenticated arbitrary file upload -> RCE in WPLP Cookie Consent (gdpr-cookie-consent) <= 4.4.1 - technical write-up and PoC