
jenkins-cve-2016-0792
 jpiechowka/jenkins-cve-2016-0792
Exploit for Jenkins serialization vulnerability - CVE-2016-0792
code-analysisdynamic-code-analysisexploitation+3
47
jpiechowka/jenkins-cve-2016-0792Exploit for Jenkins serialization vulnerability - CVE-2016-0792
 open-flaw/cve-2026-56848
Exploit PoC for CVE-2026-56848, a Node.js HTTP/2 heap-use-after-free that allows remote unauthenticated DoS. Includes raw-socket trigger, ASan build…
 raka200juta/28458
Python exploit script for CVE-2020-28458, a prototype pollution vulnerability in DataTables. It sends crafted payloads to target URLs, supports proxy…
 shoucheng3/x-stream__xstream_cve-2021-21345_1-4-15
Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.
 hunt-benito/one-multiply-too-many-cve-2026-70638-llama-cpp-android-jni-integer-overflow
Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 jaeles-project/jaeles
The Swiss Army knife for automated Web Application Testing
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
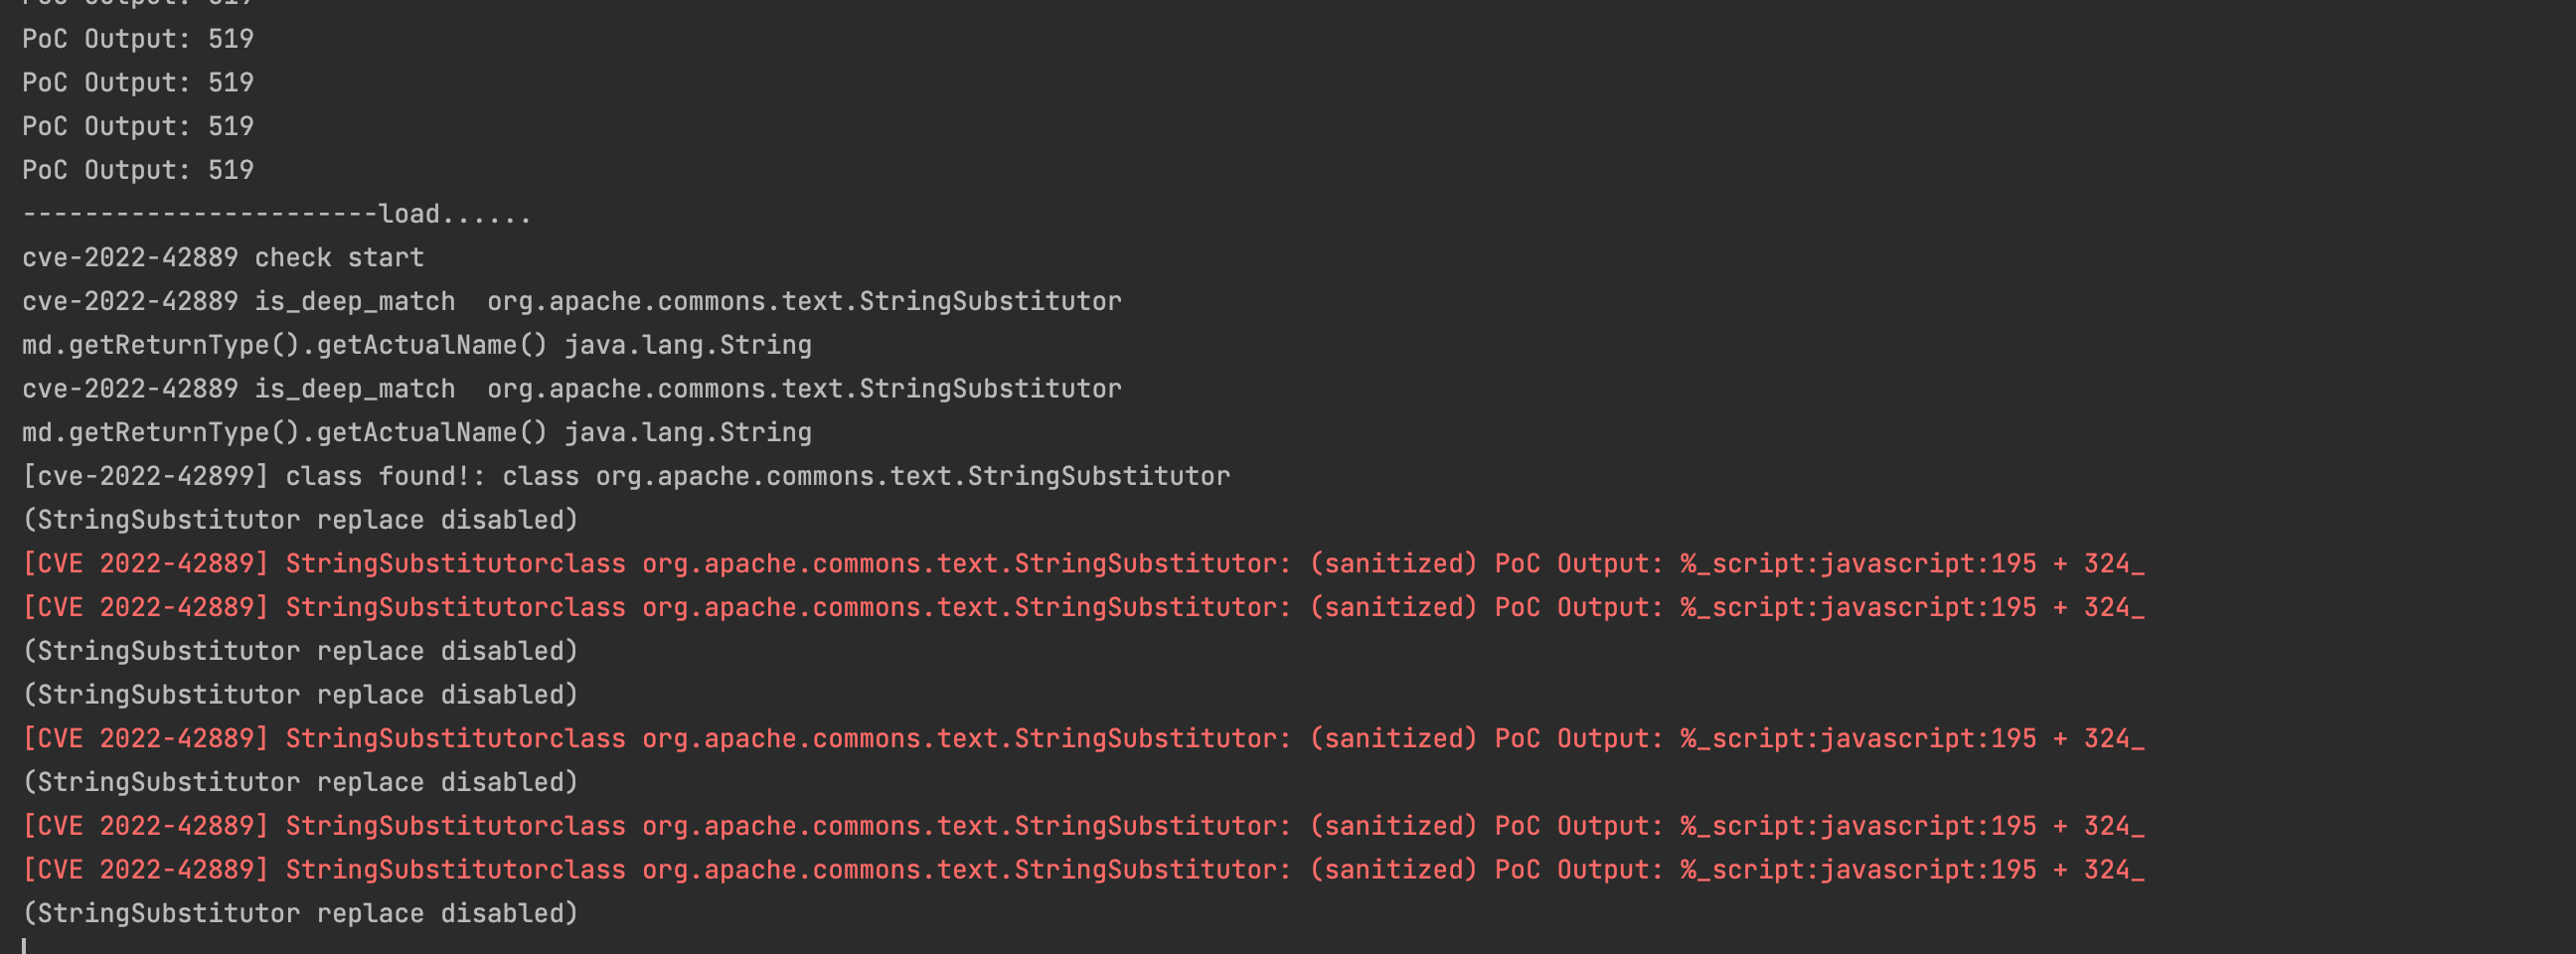 uk0/cve-2022-42889-intercept
通过 jvm 启动参数 以及 jps pid进行拦截非法参数
 abubakar-shahid/cve-2024-36886
Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…
 hupe1980/cve-2021-3129
Laravel debug mode - Remote Code Execution (RCE)
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…