

ReverseKit
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
binary-analysisdynamic-code-analysismalware-analysis+1
7923 years ago
zer0condition/reversekitx64 Dynamic Reverse Engineering Toolkit
 hunt-benito/one-multiply-too-many-cve-2026-70638-llama-cpp-android-jni-integer-overflow
Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
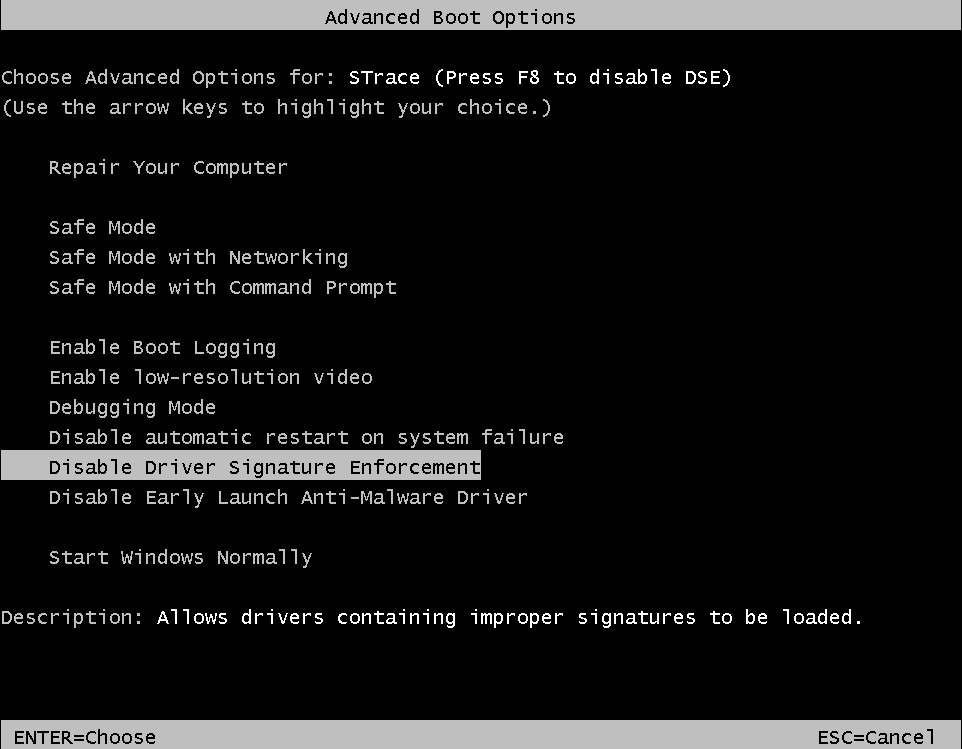 mandiant/strace
A DTrace on Windows Reimplementation