
recaptcha
 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
anti-botcaptcha-bypassdynamic-code-analysis+3
elyelysiox/recaptchaDocumentation and reverse engineering of reCAPTCHA
 shoucheng3/esapi__esapi-java-legacy_cve-2022-23457_2-2-3-1
Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…
 eset/malware-research
Code written as part of our various malware investigations
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
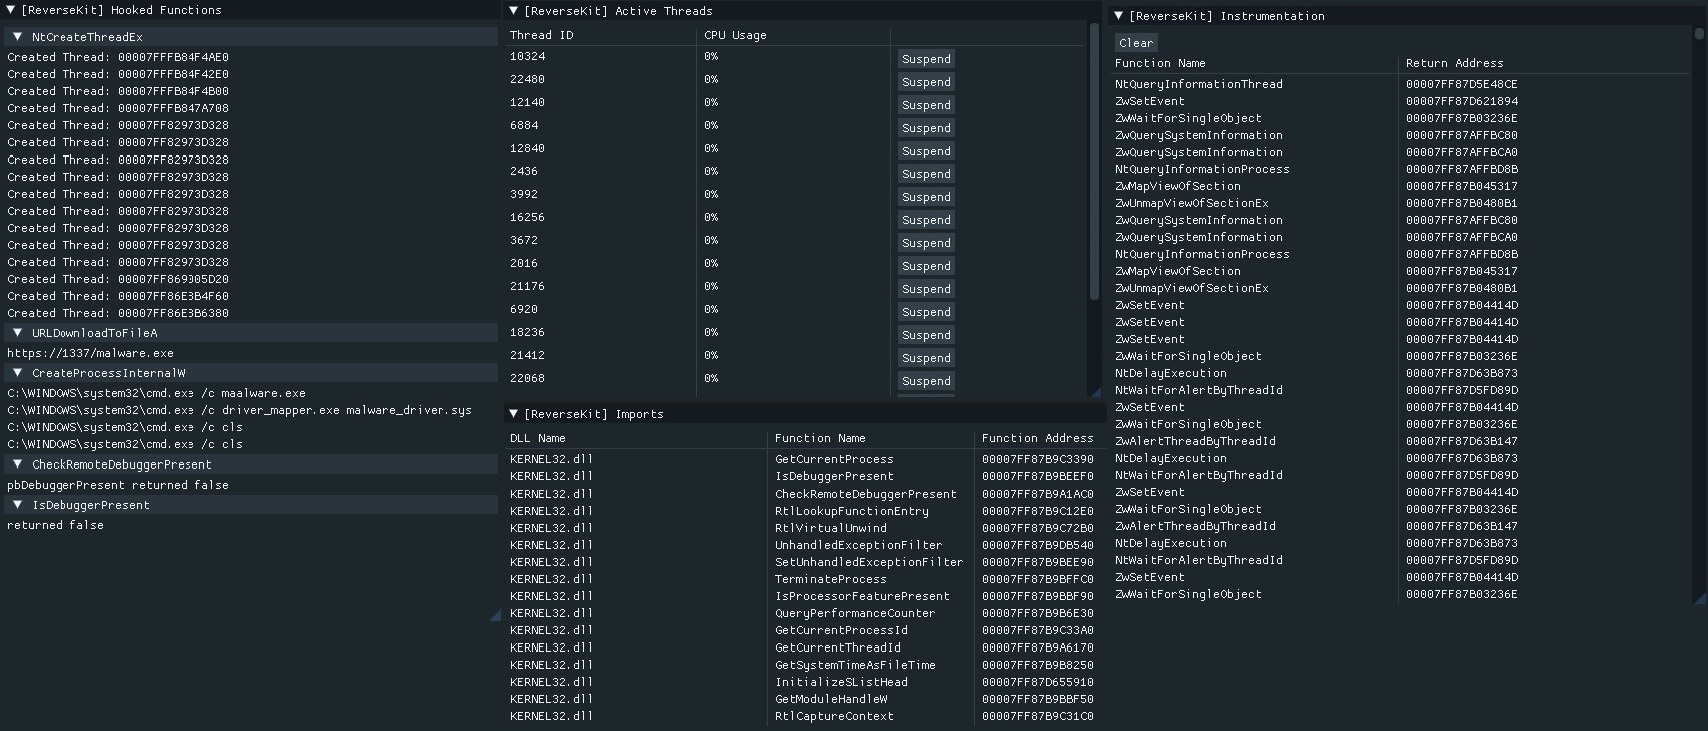 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 cloudflare/security-audit-skill
A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
 chichou/vscode-frida
Unofficial frida extension for VSCode
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
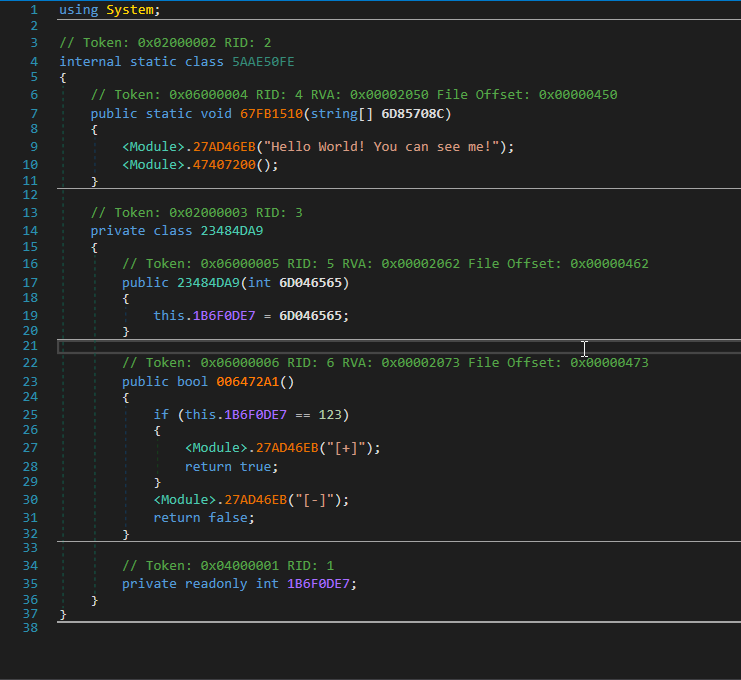 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.