

 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 theshinigami/mafrida
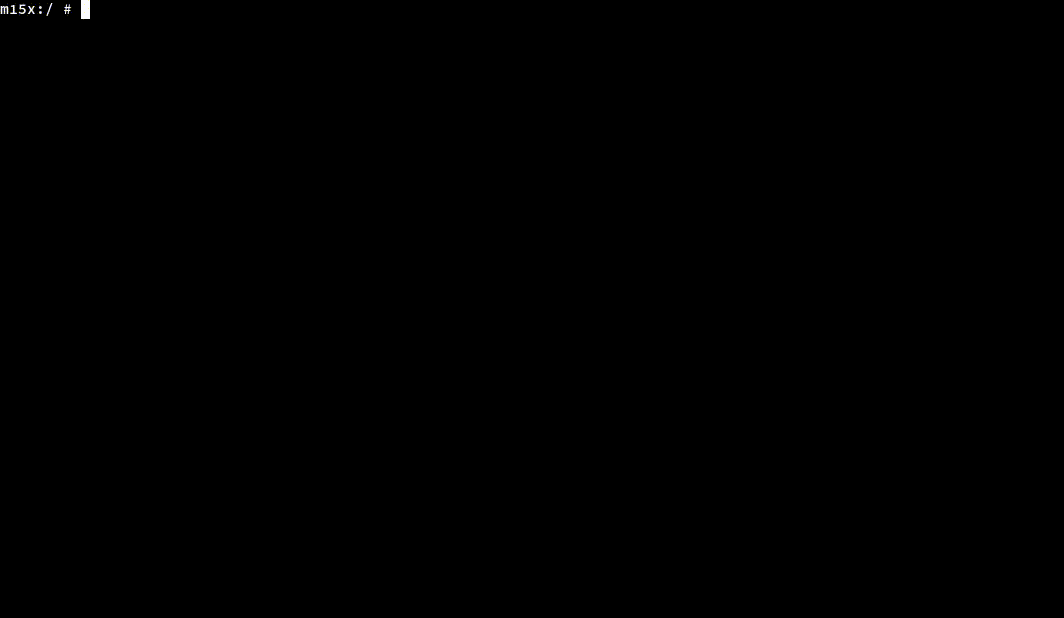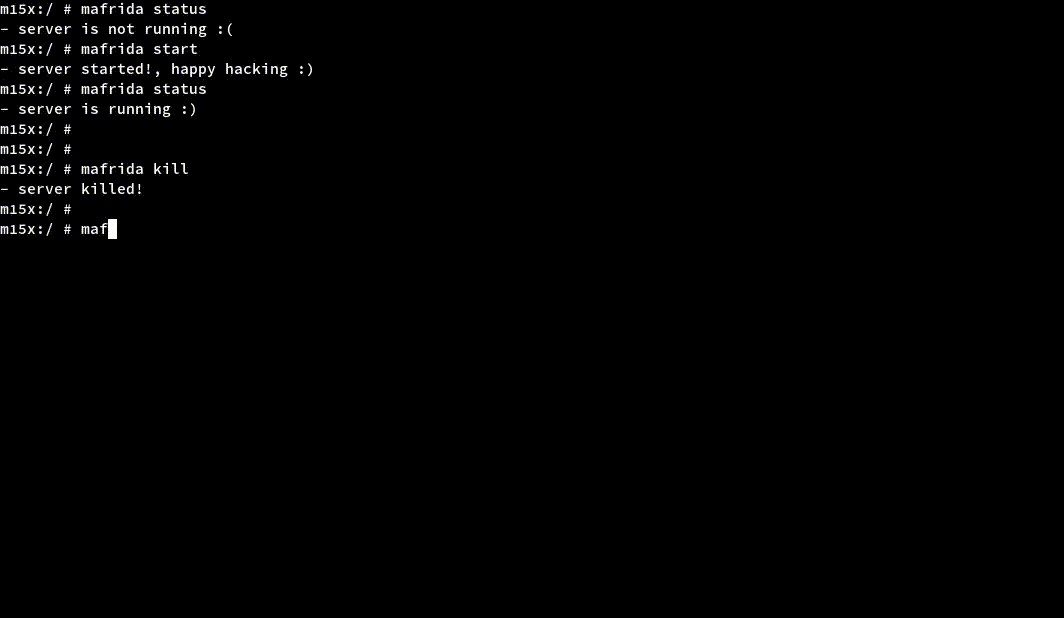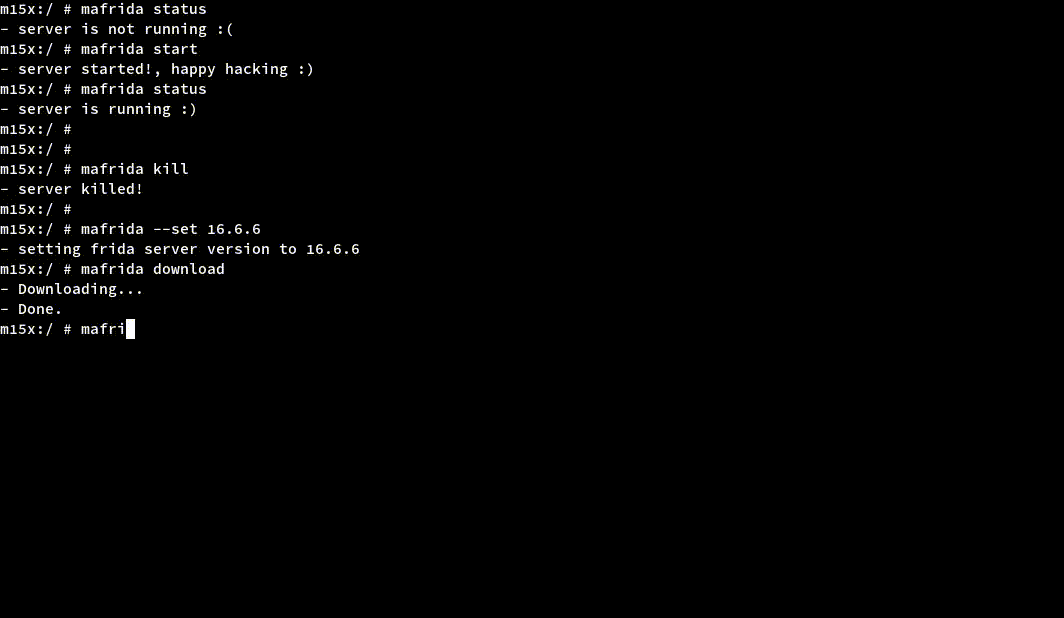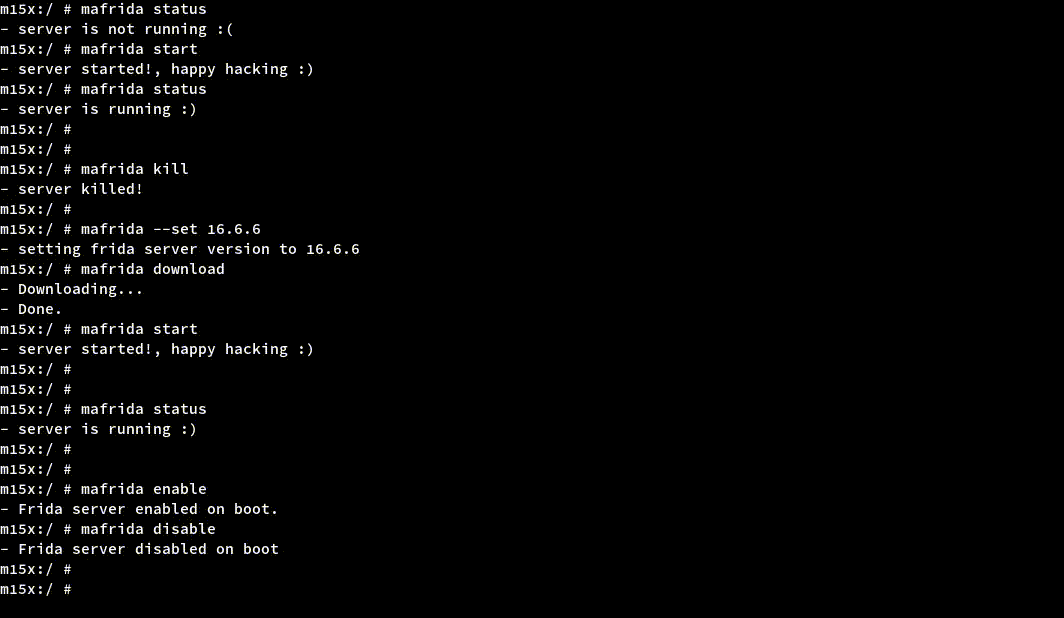
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 mandiant/strace
A DTrace on Windows Reimplementation
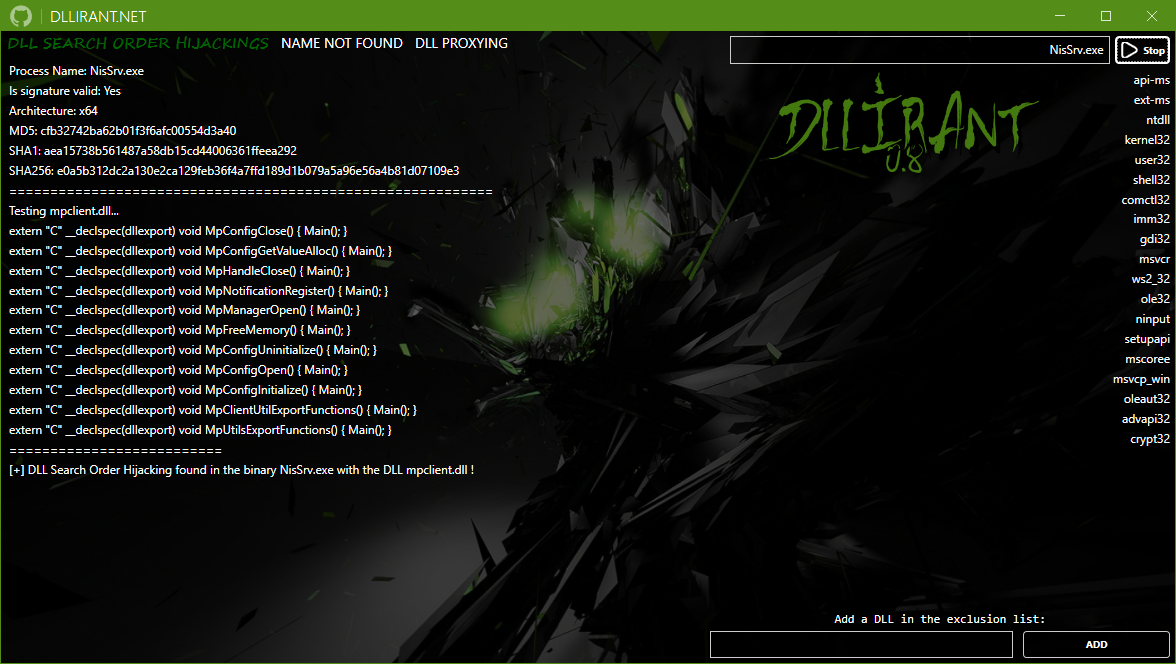 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
 therealdreg/ida_bochs_windows
Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 shoucheng3/x-stream__xstream_cve-2021-21345_1-4-15
Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.
 abubakar-shahid/cve-2024-36886
Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…
 chichou/vscode-frida
Unofficial frida extension for VSCode
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 pizlonator/fil-c
Fil-C: completely compatible memory safety for C and C++
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
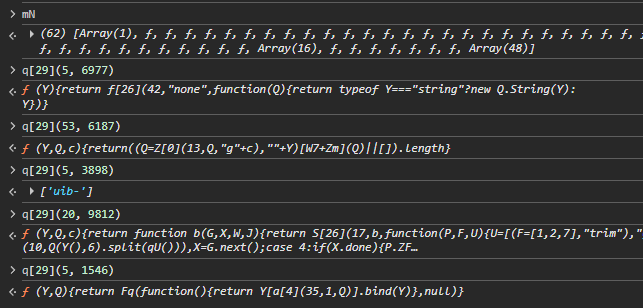 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA