pesieve-go
 hasherezade/pesieve-go
Golang bindings for PE-sieve
binary-analysisdynamic-code-analysismalware-analysis+1
43
hasherezade/pesieve-goGolang bindings for PE-sieve
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
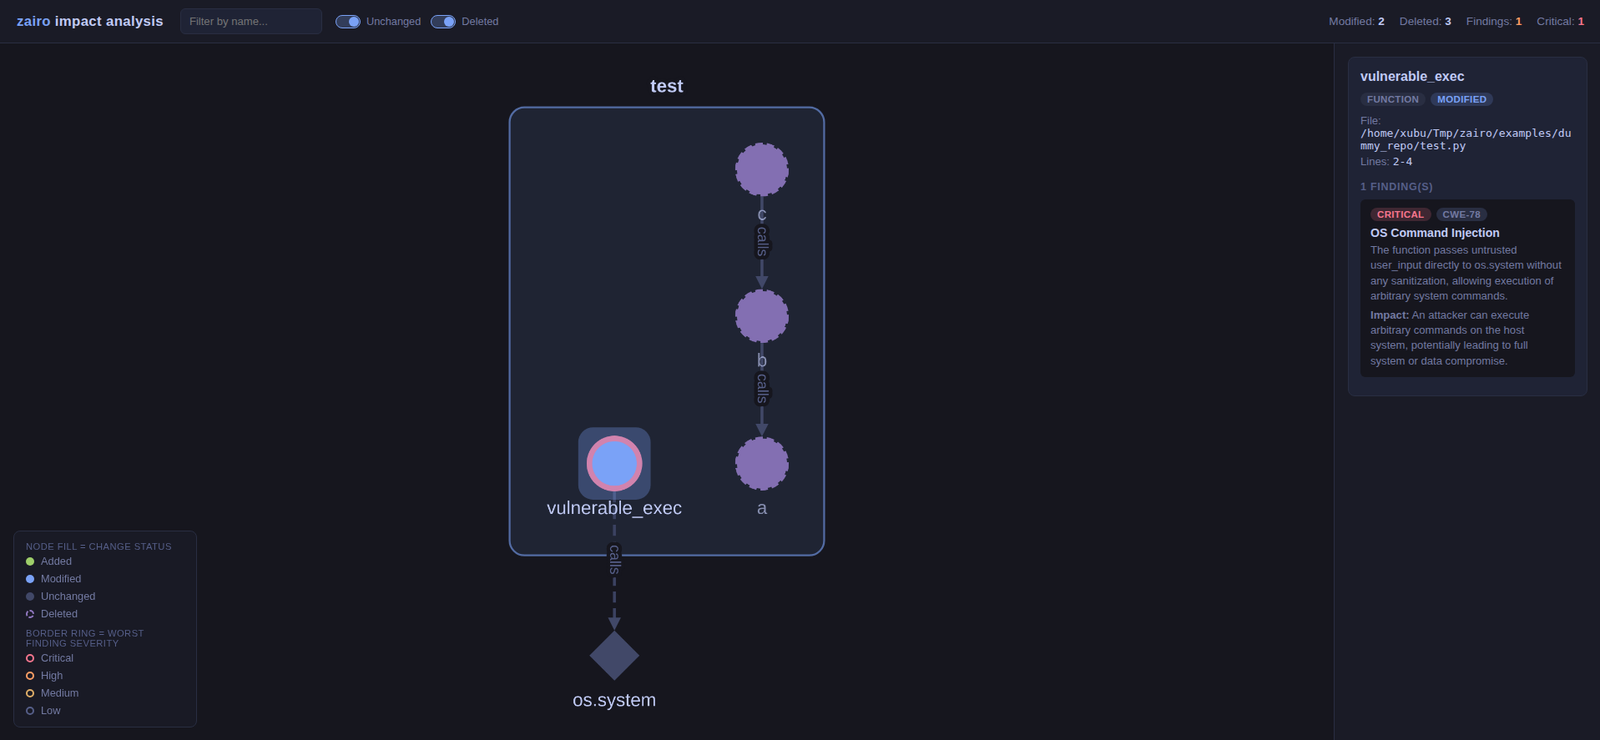 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
 hunt-benito/one-multiply-too-many-cve-2026-70638-llama-cpp-android-jni-integer-overflow
Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…
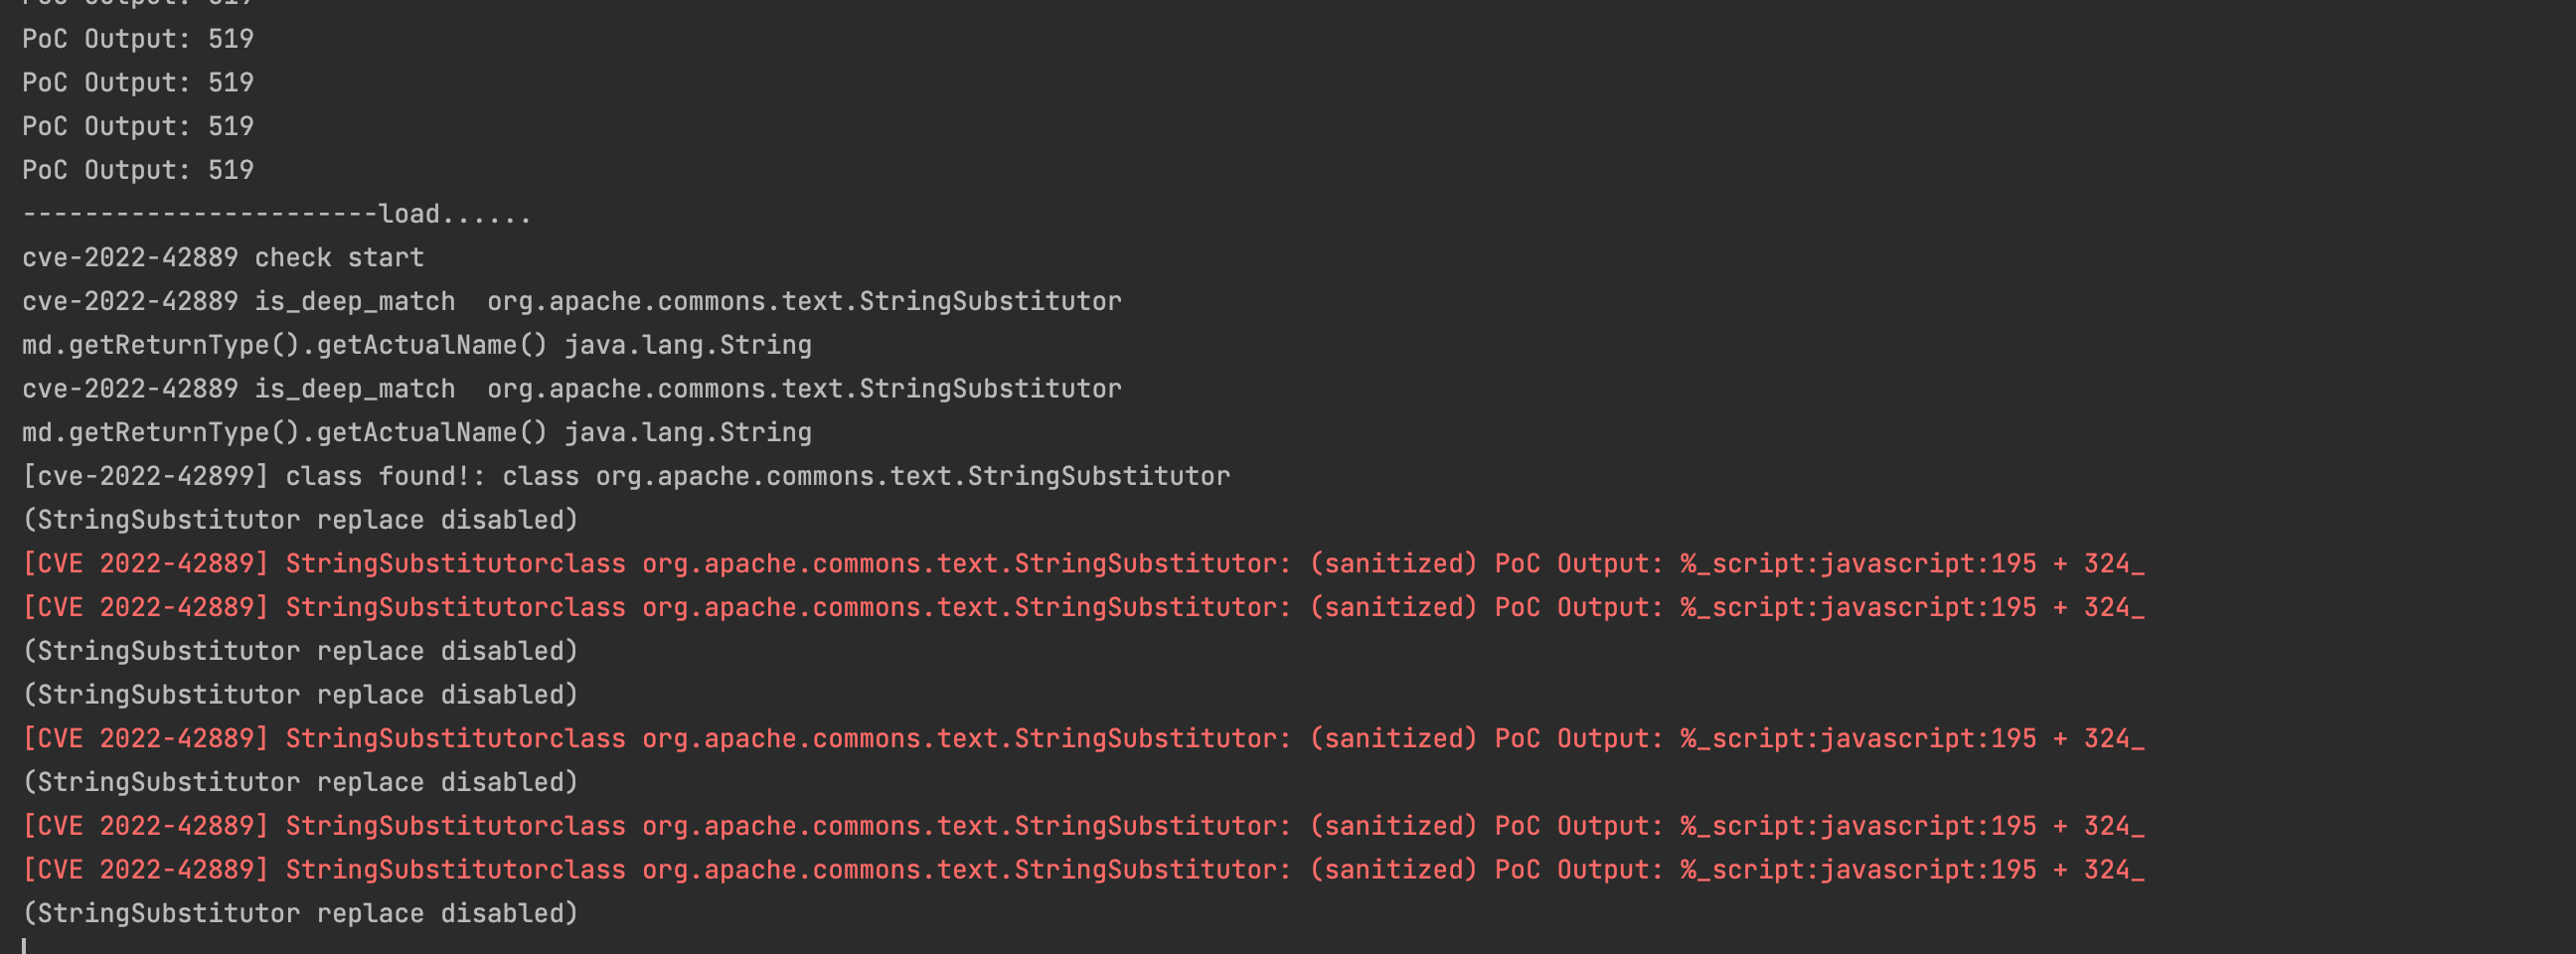 uk0/cve-2022-42889-intercept
通过 jvm 启动参数 以及 jps pid进行拦截非法参数
 whatswrongandwhy/ptrace
Linux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.
 tinopreter/docviewerexploitapp
This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…
 abubakar-shahid/cve-2024-36886
Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…
 hupe1980/cve-2021-3129
Laravel debug mode - Remote Code Execution (RCE)
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 de4dot/de4dot
.NET deobfuscator and unpacker.
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
 trailofbits/umberto
Library and CLI for mutating structured data (JSON, XML, X.509) to support grammar-based fuzzing, with multiple mutation strategies and integration…
 google/kernel-sanitizers
Linux Kernel Sanitizers, fast bug-detectors for the Linux kernel
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…