
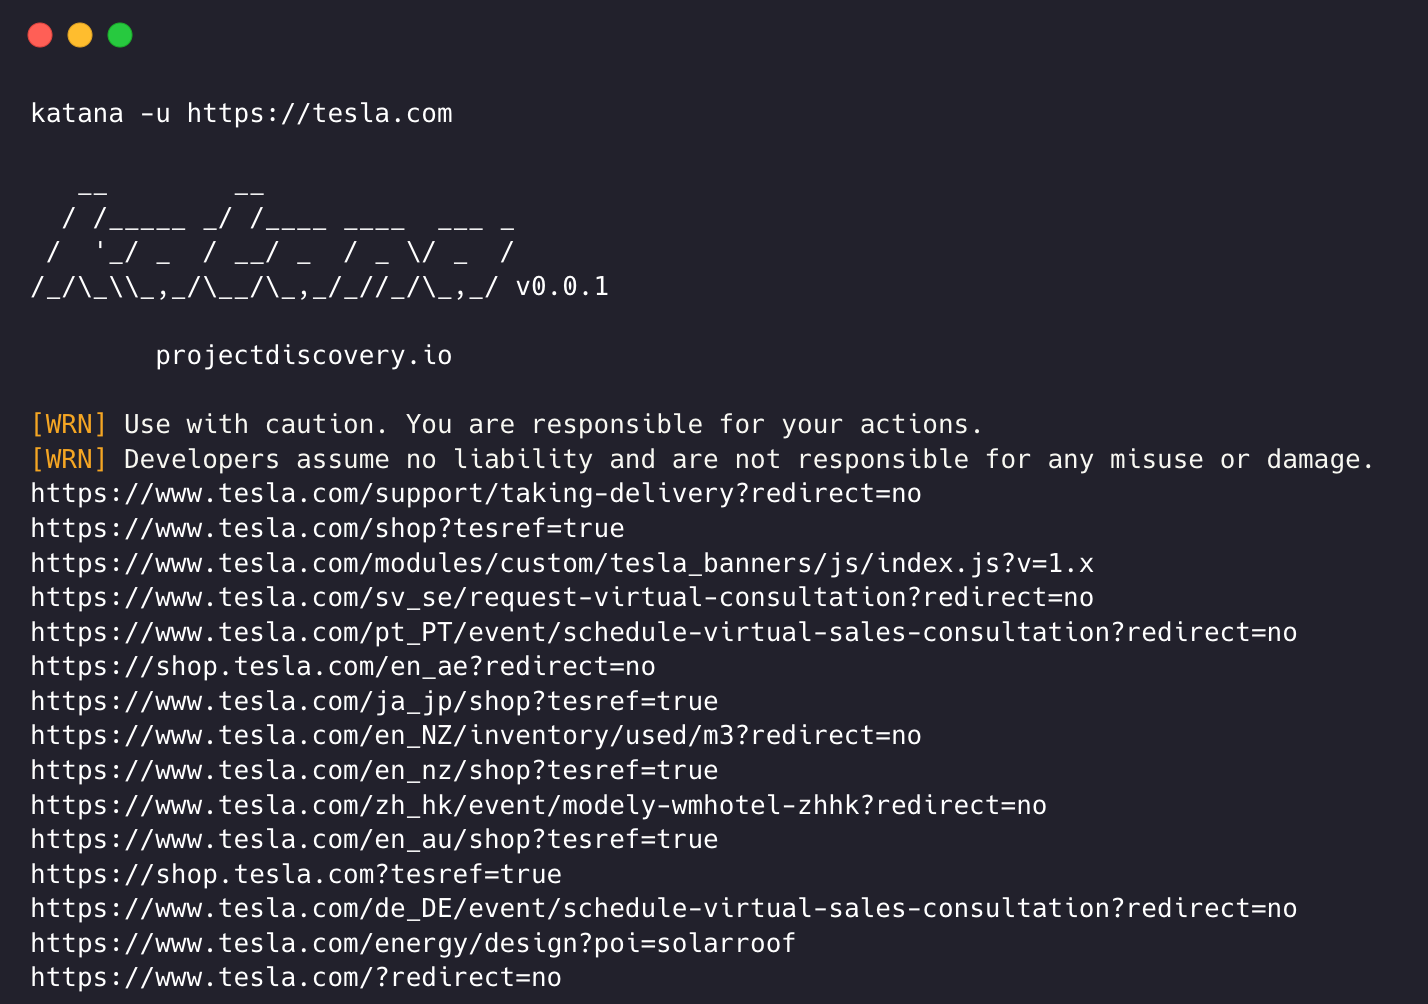
katana
 projectdiscovery/katana
A next-generation crawling and spidering framework.
api-securityapi-security-testingcrawler+7
projectdiscovery/katanaA next-generation crawling and spidering framework.
 assetnote/kiterunner
High-speed API and web content discovery tool that bruteforces routes using compiled Swagger datasets, supporting depth scanning, custom wordlists,…
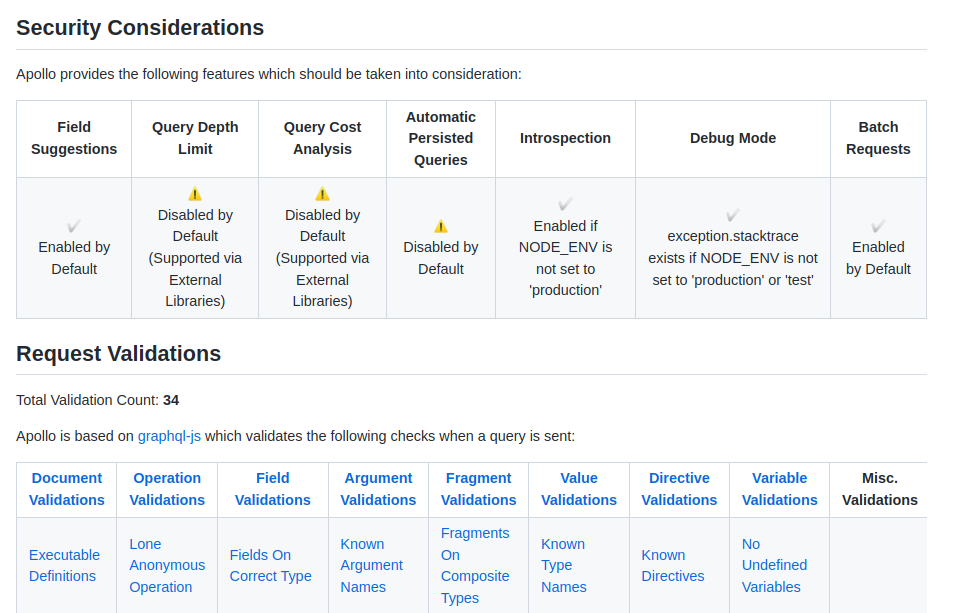 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
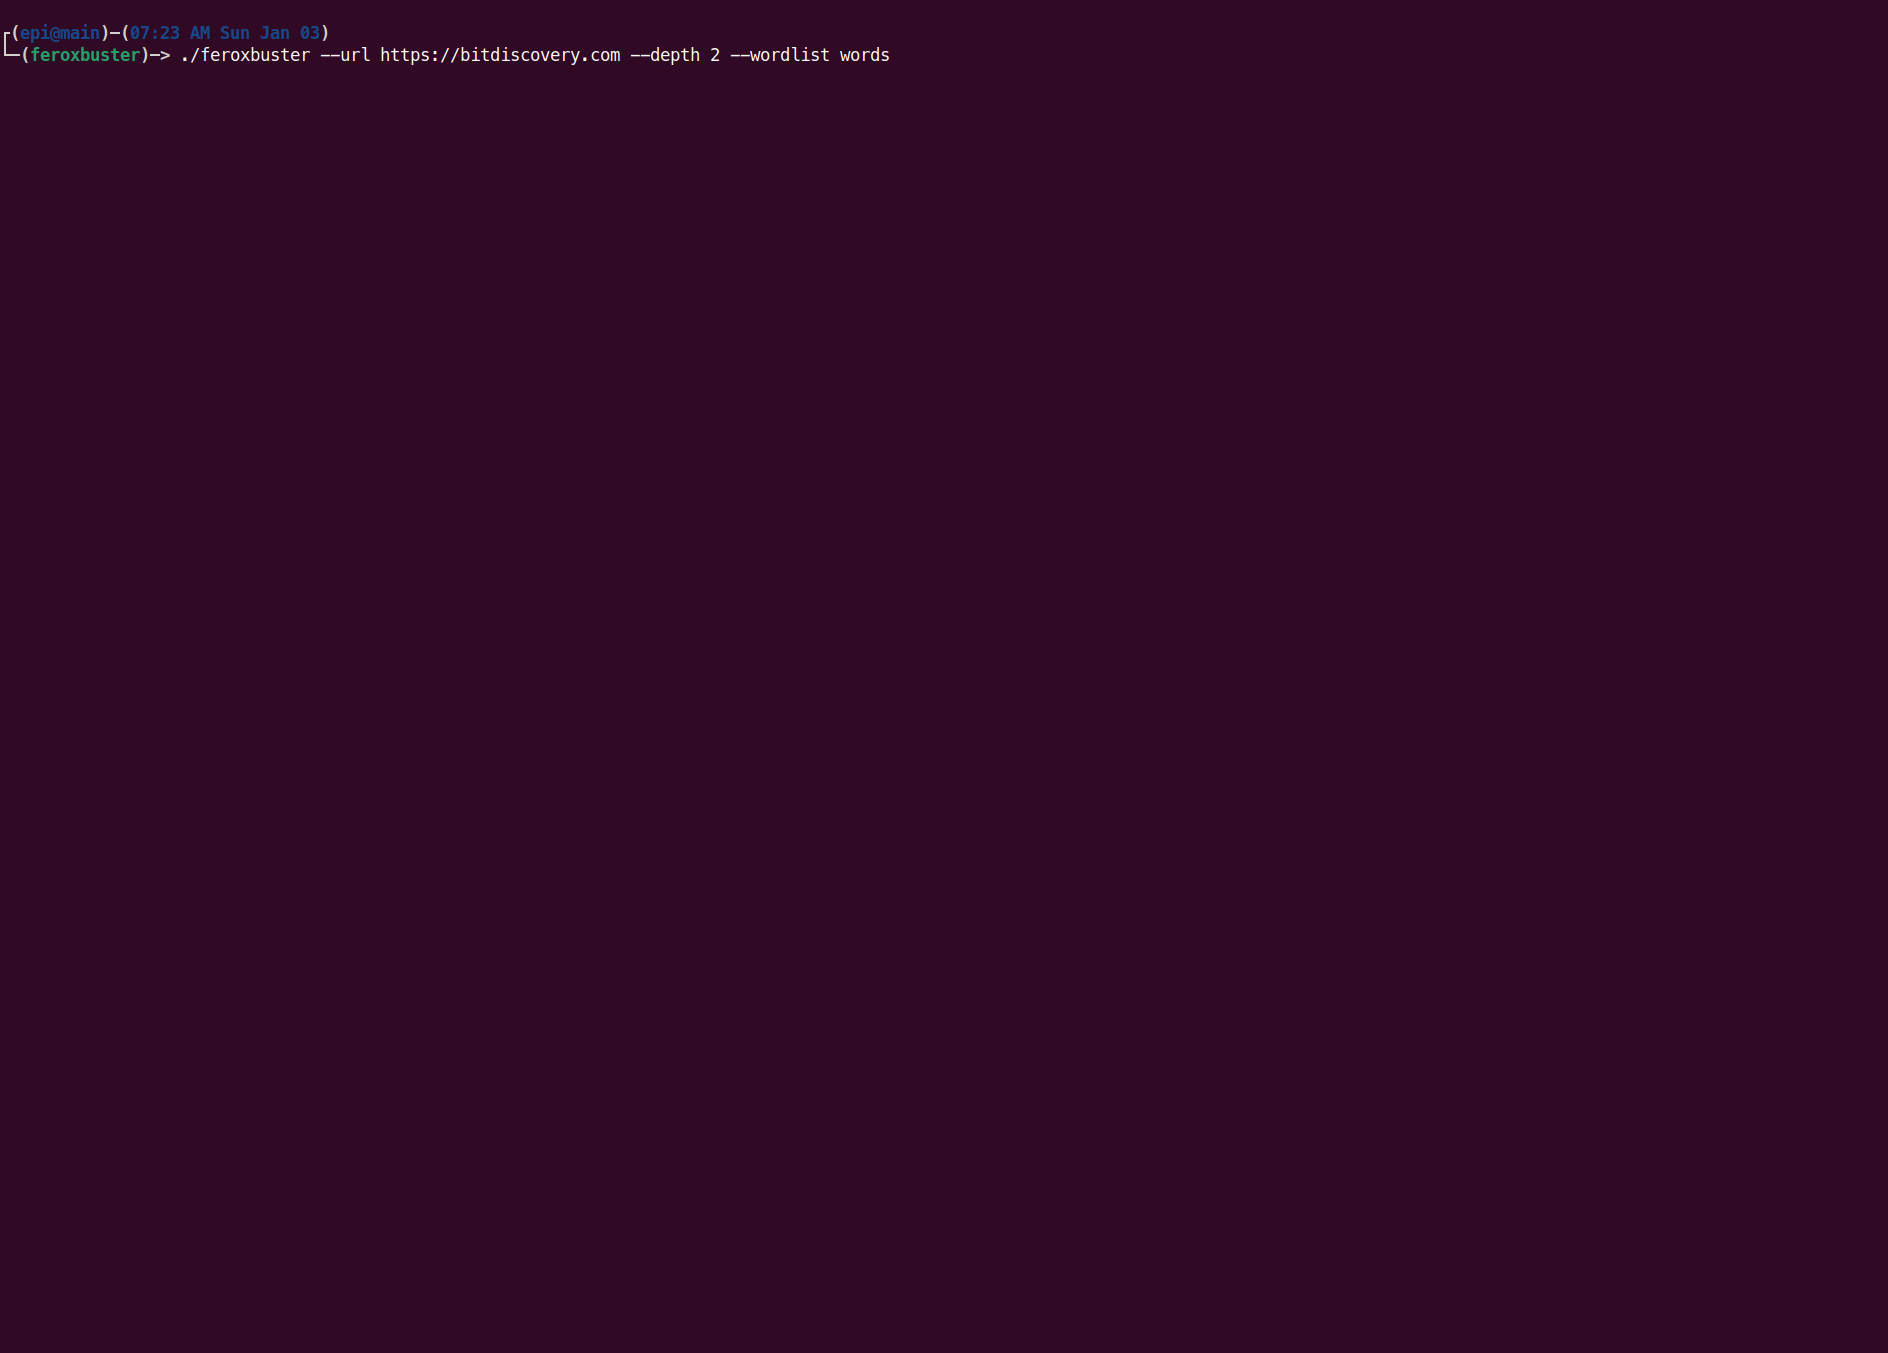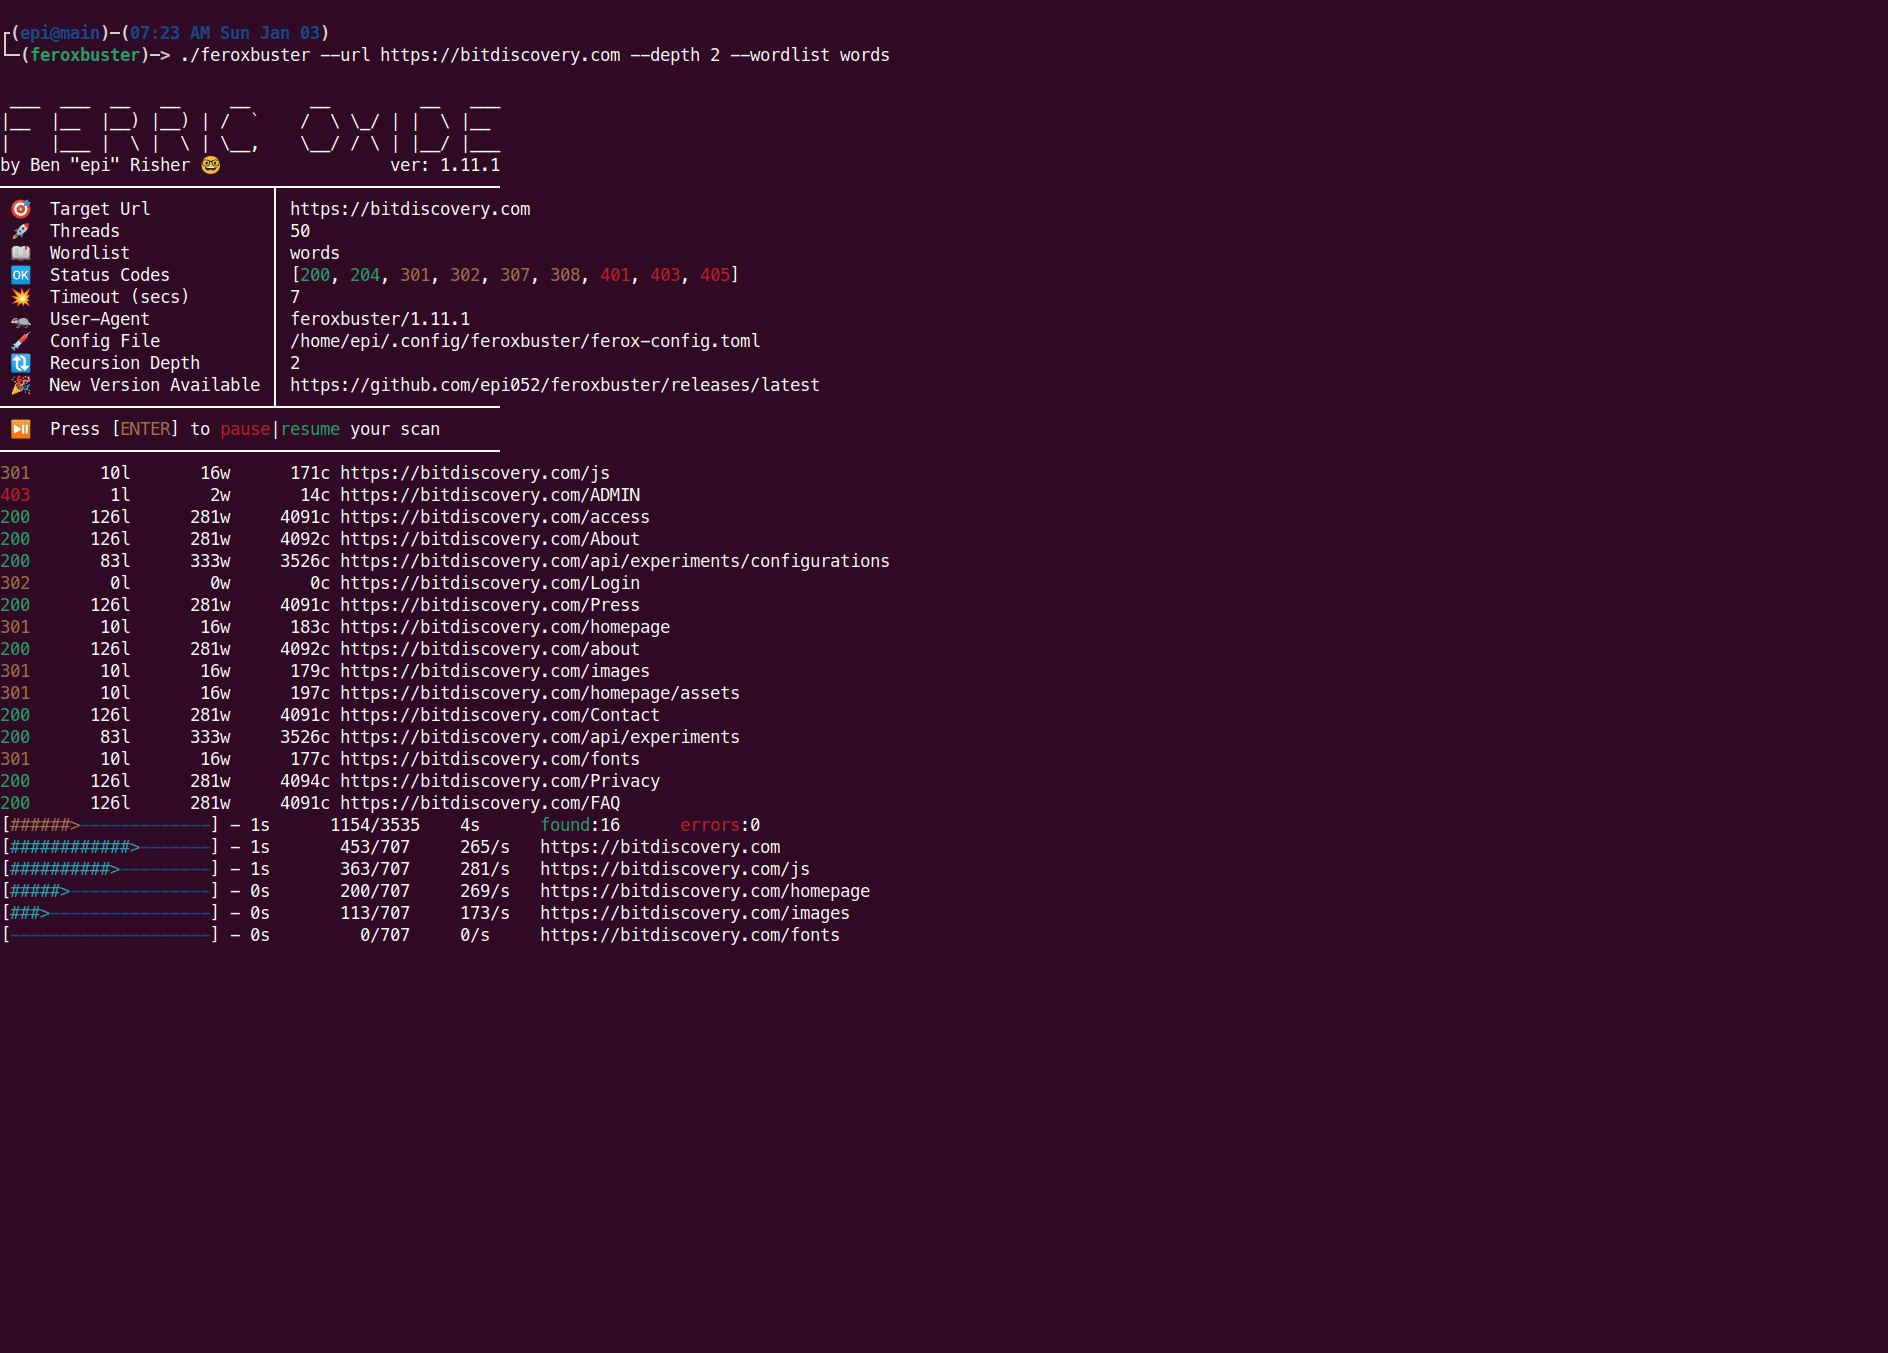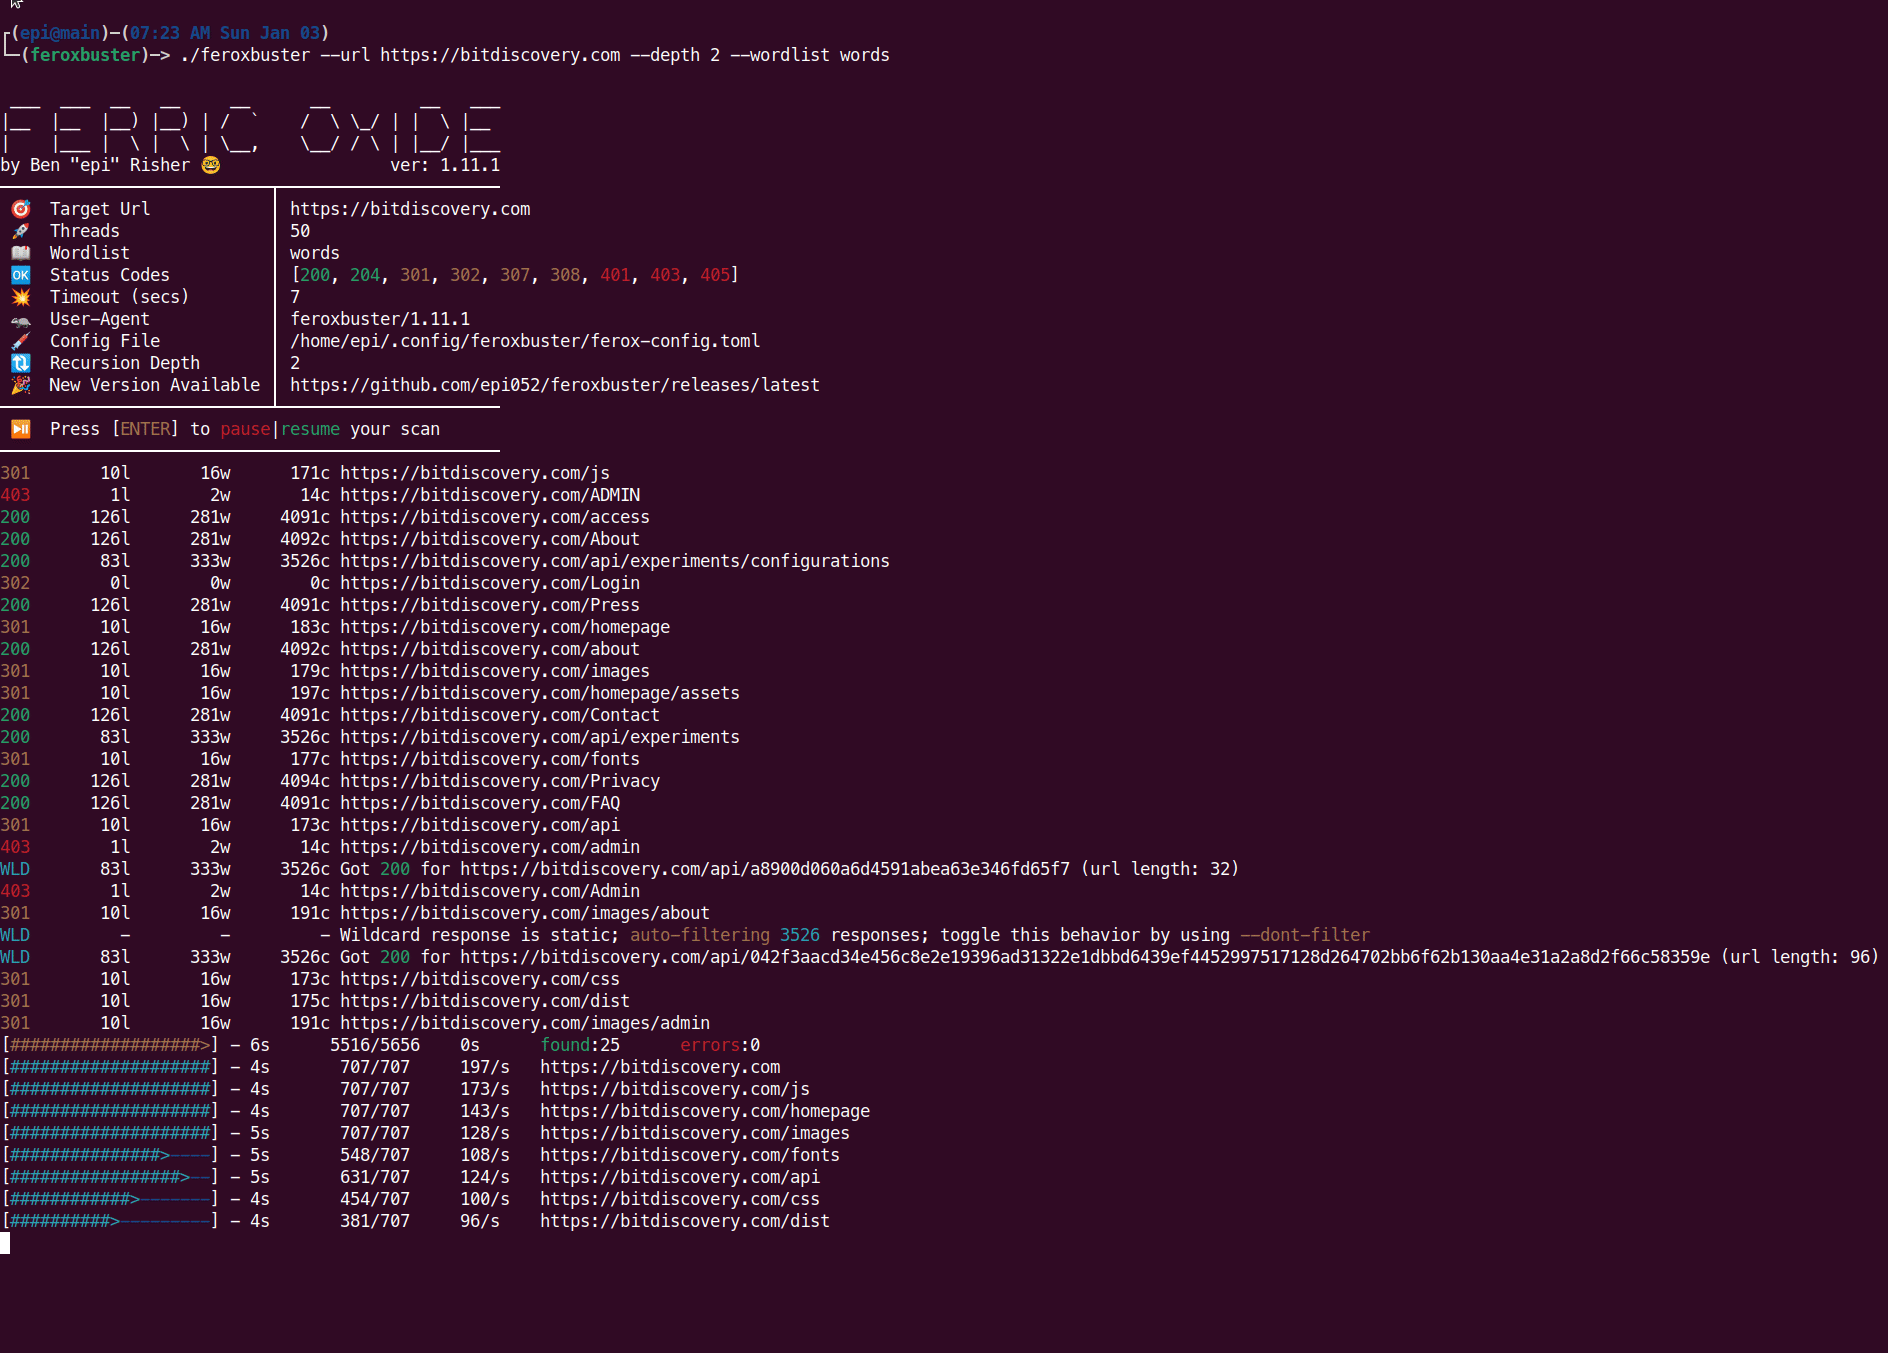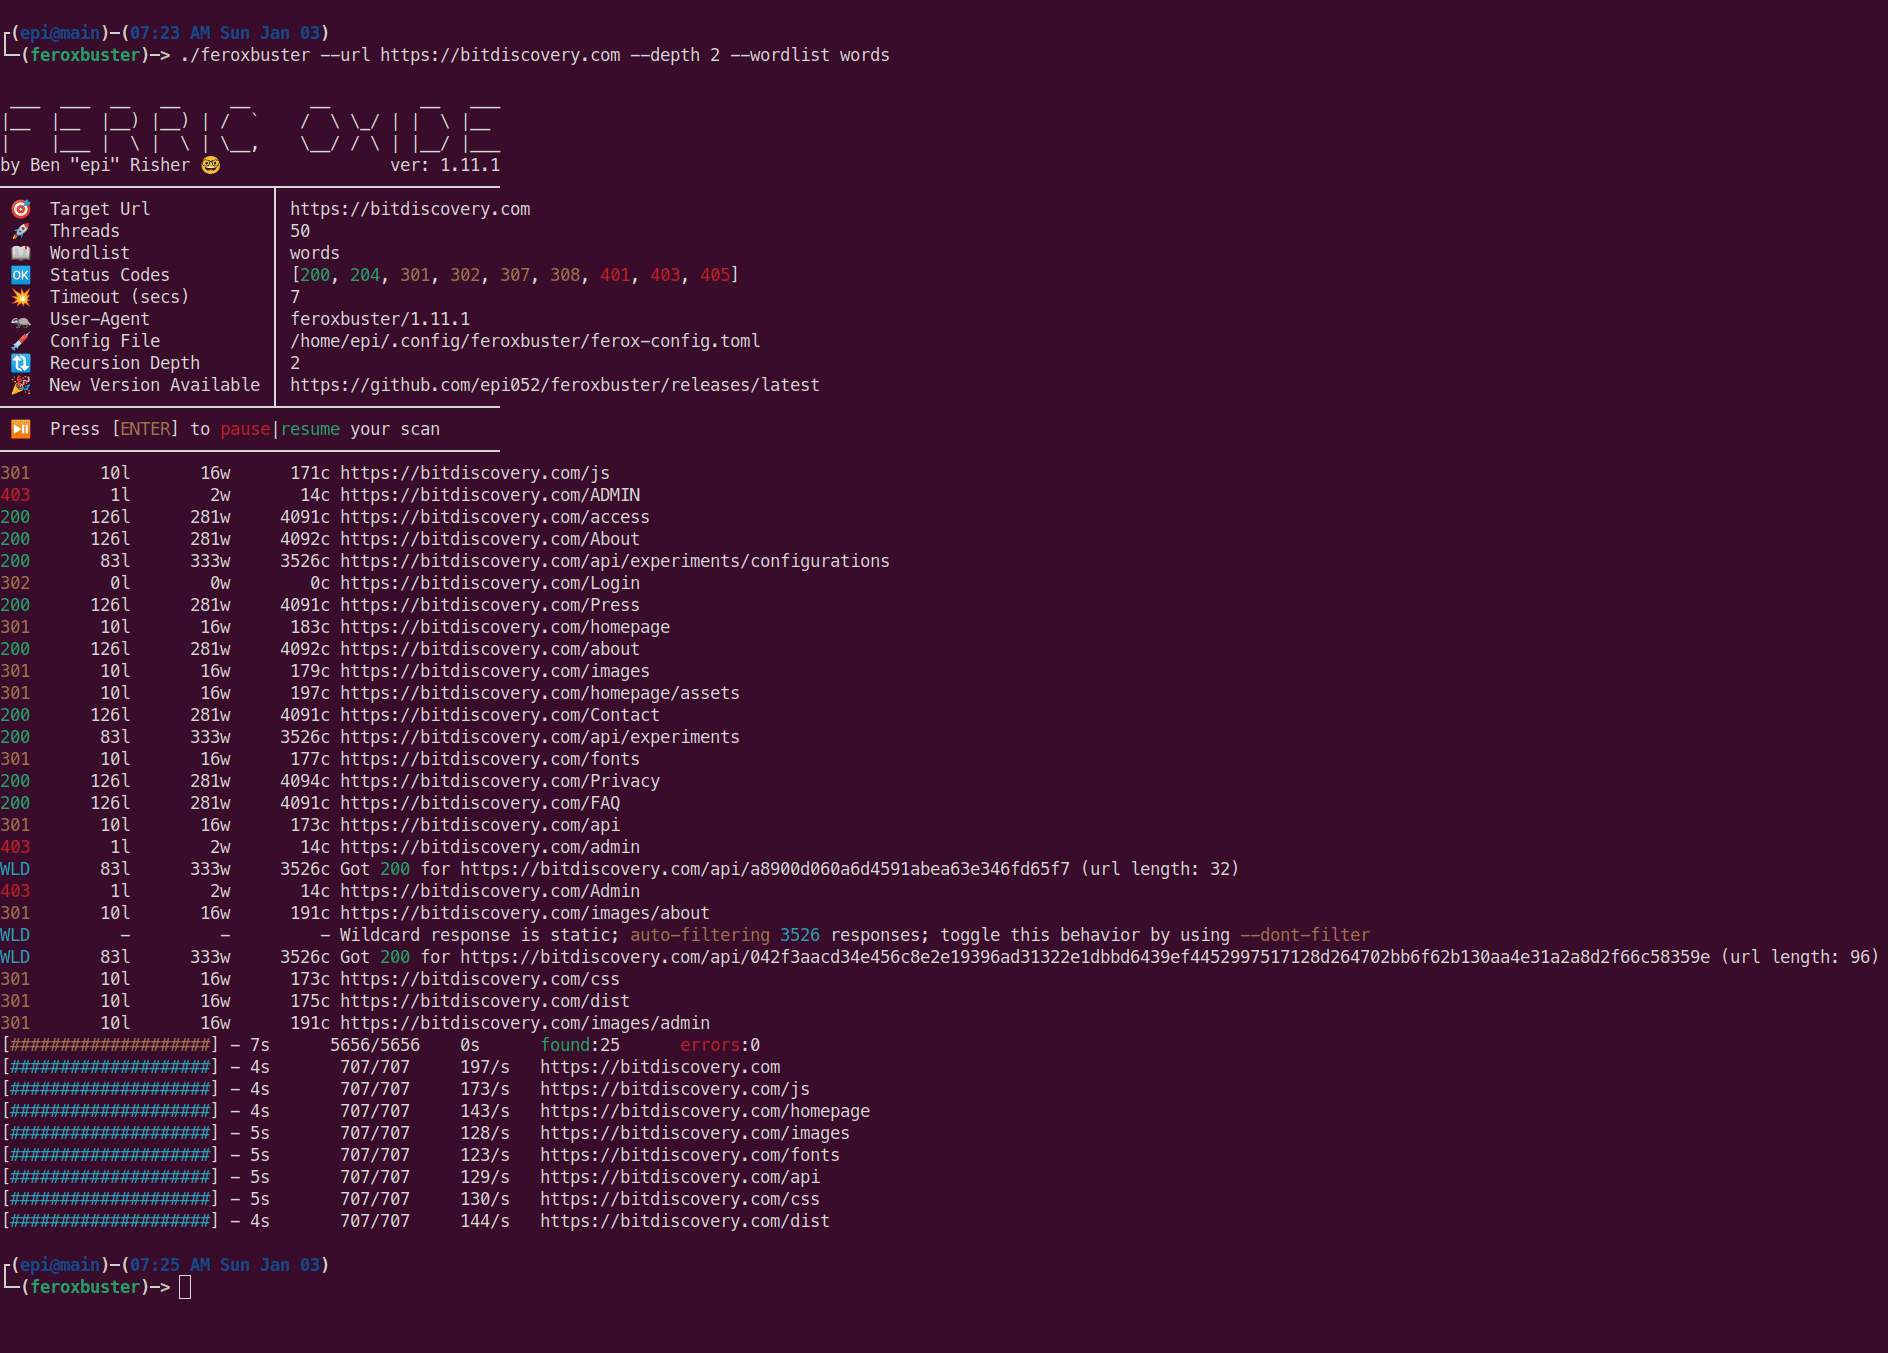 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 dragonjar/burpia
Extensión de Burp Suite que incorpora detección pasiva de vulnerabilidades mediante inteligencia artificial.
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 angorafuzzer/angora
Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 open-flaw/cve-2026-56848
Exploit PoC for CVE-2026-56848, a Node.js HTTP/2 heap-use-after-free that allows remote unauthenticated DoS. Includes raw-socket trigger, ASan build…
 raka200juta/28458
Python exploit script for CVE-2020-28458, a prototype pollution vulnerability in DataTables. It sends crafted payloads to target URLs, supports proxy…
 jaeles-project/jaeles
The Swiss Army knife for automated Web Application Testing
 narfindustries/http-garden
Differential testing framework for HTTP implementations