Archived
umberto
 trailofbits/umberto
Library and CLI for mutating structured data (JSON, XML, X.509) to support grammar-based fuzzing, with multiple mutation strategies and integration…
dynamic-code-analysisfuzzinggeneral-purpose-utilities+1
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
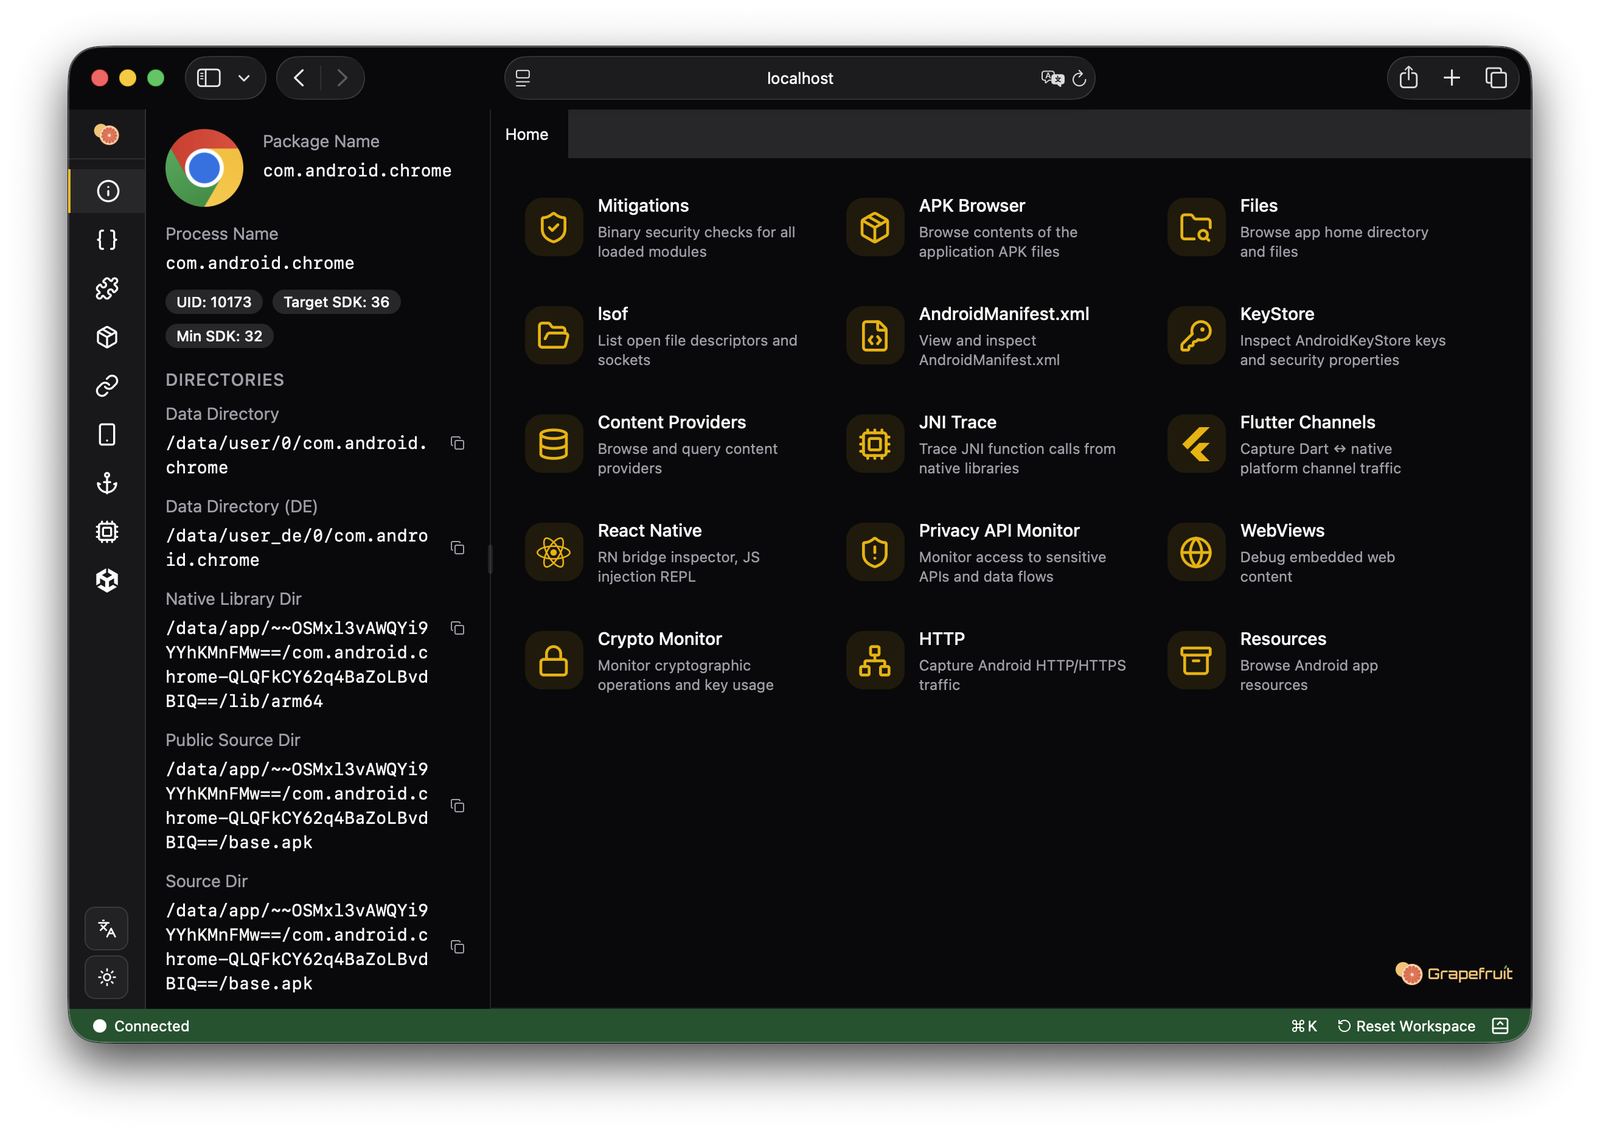 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
 chichou/vscode-frida
Unofficial frida extension for VSCode
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 hunt-benito/one-multiply-too-many-cve-2026-70638-llama-cpp-android-jni-integer-overflow
Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
 google/kernel-sanitizers
Linux Kernel Sanitizers, fast bug-detectors for the Linux kernel