
wpscan
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
crawlerdynamic-code-analysisinformation-gathering+7
9.8k
wpscanteam/wpscanWordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 pizlonator/fil-c
Fil-C: completely compatible memory safety for C and C++
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 jaeles-project/jaeles
The Swiss Army knife for automated Web Application Testing
 rust-fuzz/cargo-fuzz
Cargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
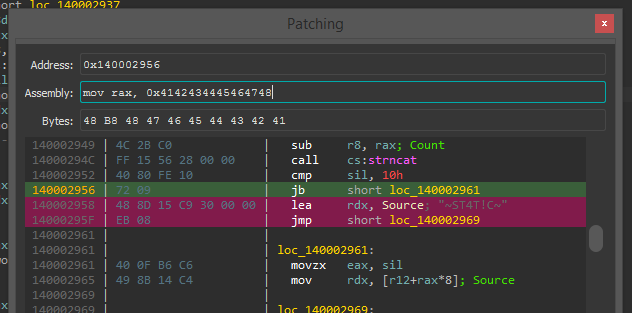 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 splx-ai/agentic-radar
A security scanner for your LLM agentic workflows
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
 angorafuzzer/angora
Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.