

dalfox
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
devsecopsdynamic-code-analysispenetration-testing+5
5.3k
hahwul/dalfoxFast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 go-delve/delve
Source-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…

 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 eset/malware-research
Code written as part of our various malware investigations
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
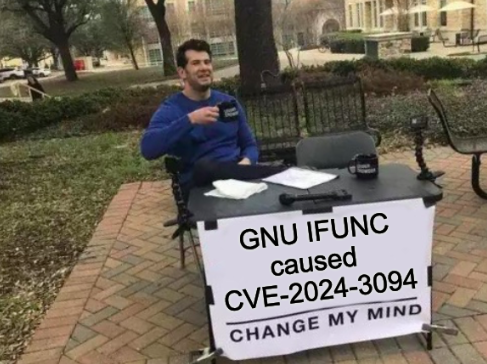 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)